How DNS Filtering Works and Why It Blocks Sites
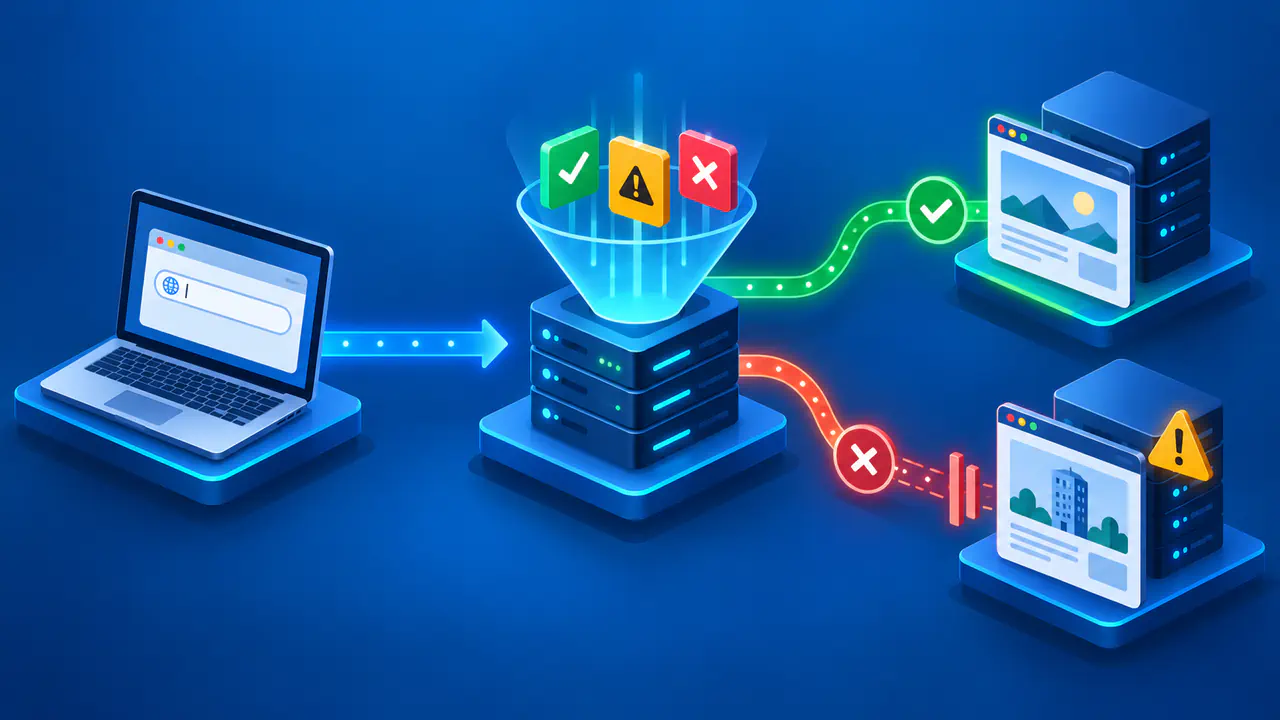
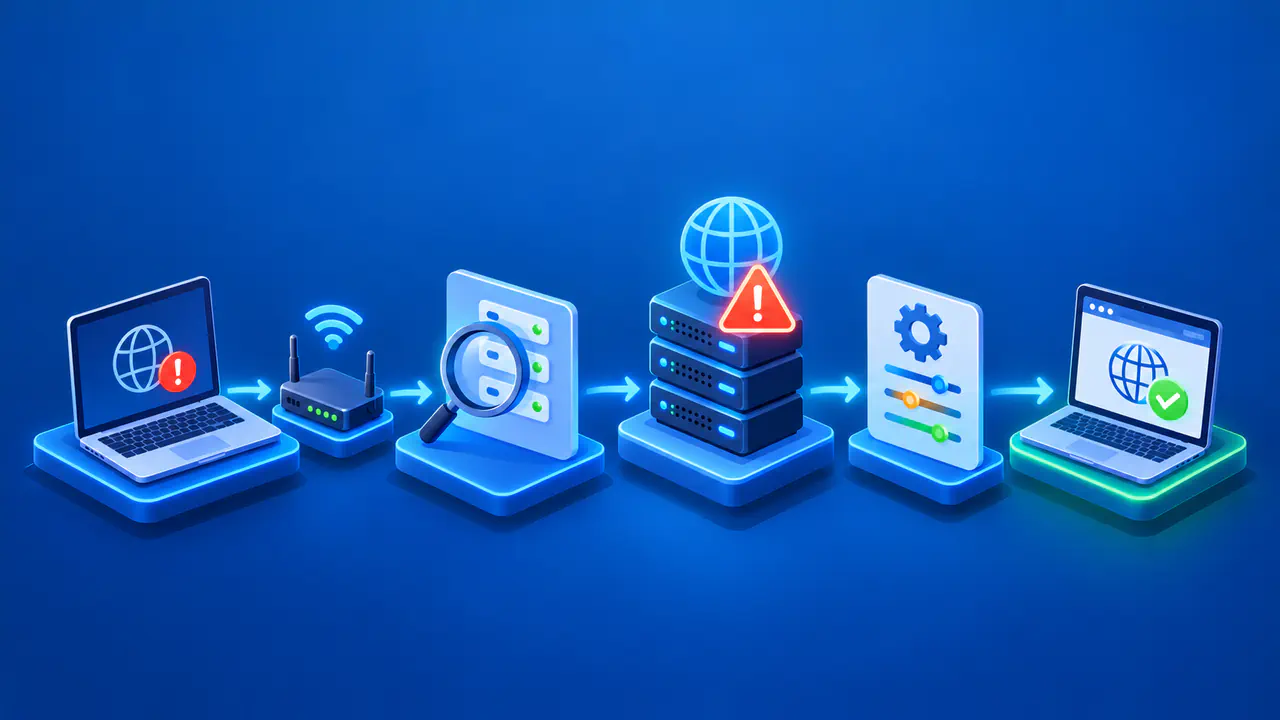
DNS filtering applies access rules while a device looks up a domain name. The resolver that answers the query can withhold the normal result or replace it with a policy response. The browser may then report that the site cannot be reached, even though the web server itself is healthy.
The key question is which name was blocked and by which policy. A page can depend on many names besides the address shown in its URL. A filter may permit the main site while blocking a name used for login, images, payments, or another embedded service. Identify the failing name before assuming that the whole site is down.
How Resolvers Apply Domain Policies
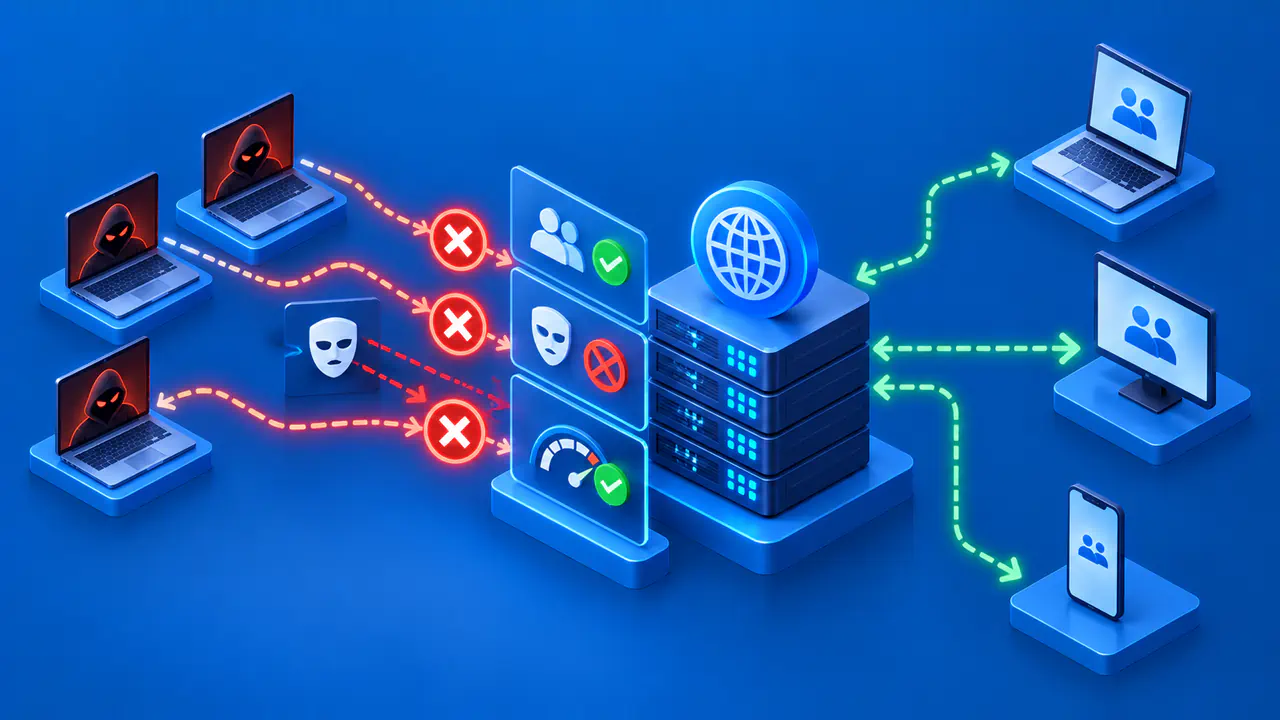
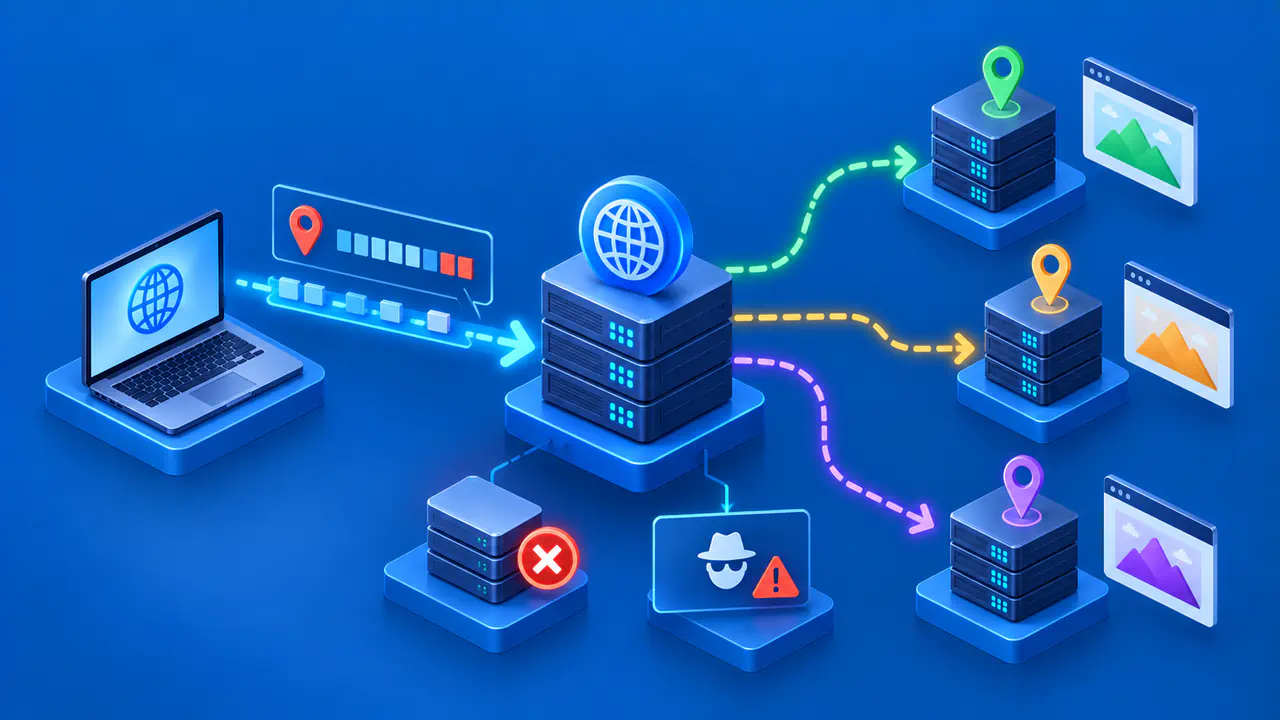
Most DNS filters apply rules to domain names, not to individual web pages. An administrator might add an exact name to a denylist, subscribe to a categorized list, or write a rule that matches a wider family of names. A service can use different policies for different client groups. The resolver checks its active rules for the client and either provides the ordinary DNS result or applies the matching policy.
Security policies may block names associated with malware or phishing sites that try to steal credentials. Other lists target advertising, tracking or content categories restricted by the network owner. A policy block therefore does not always mean that the destination is malicious; the category and the owner's rules determine why access was restricted.
Pi-hole supports exact domain entries, regular expressions that match patterns in names, and subscribed lists maintained externally. Group settings determine which rules and lists apply to each client, so two devices using the same Pi-hole installation can receive different answers. Check whether the relevant rule is enabled and applies to the affected client's group.
What a Blocked DNS Reply Looks Like
The response varies by implementation and configuration. Pi-hole's NULL blocking mode returns 0.0.0.0 for an A query asking for an IPv4 address or :: for an AAAA query asking for an IPv6 address, withholding the site's normal address. Other modes can return a negative answer or the Pi-hole's own address. These are alternative behaviors, so a block does not always produce the same browser message.
NXDOMAIN tells the client that the queried name does not exist. NODATA means there is no record of the requested type; the DNS response code is NOERROR, with no relevant answer records. A filter can deliberately produce either result, so neither response by itself proves what the domain's public DNS actually contains. Pi-hole can also attach Extended DNS Error information to explain a block.
A browser message alone rarely identifies which rule produced the answer. The resolver's query log, the returned DNS data and the matching policy entry provide more specific evidence. A timeout is different from a negative reply: it means no response arrived within the waiting period, and it can have causes unrelated to filtering.
What Response Policy Zones Do
BIND 9 can apply Response Policy Zones (RPZ) inside a recursive resolver, which looks up DNS data for its clients. Policy triggers can use the queried name, addresses in answers, or client and nameserver information. Depending on the rule, BIND can return a negative answer, substitute data or discard the response.
These local rules do not alter the records published by the domain's authoritative nameservers. A pass-through action leaves the response unchanged by RPZ. When several active policy rules match, an earlier zone in the response-policy configuration takes precedence, and BIND also ranks the trigger types within each zone. An exception in a later zone may therefore lose to an earlier block.
Why a Legitimate Site Can Be Blocked
Blocklists are judgments about names at a particular time. A domain may have changed ownership, been added to a list in error, or be shared by both a wanted feature and an unwanted service. A broad pattern may catch a harmless subdomain because its spelling resembles a tracking or risky domain. A site may also fail indirectly because one of its supporting domains is blocked while its primary name resolves normally.
First confirm that the affected device is actually using the expected filtering resolver. Then look for the failed name and timestamp in the resolver's query log. If a policy match appears, identify the responsible rule or subscribed list and the client or group it applies to. Compare the result for the same name and record type under a controlled, authorized resolver configuration, keeping the client scope and test time in the record.
For example, a login page's hostname might resolve correctly while a separate authentication name is denied. Allowing the page's main domain again would not address that specific failure. The useful evidence is the denied dependency and its matched rule, followed by an authorized test of the login feature.
Do not infer a false positive solely because you can open the site on another network. The two networks may use different policies, and a site can change between tests. If no block event is recorded, also check ordinary DNS failures, application errors and connectivity before editing a filter. An unreachable page alone is not evidence that a blocking rule is wrong.
What Name Filtering Cannot Inspect
DNS queries contain names, not the full paths of HTTPS pages. A name-only filter cannot permit one page and reject another page under the same hostname based on their paths. It also cannot reliably remove every advertisement, especially when wanted content and advertisements share a name. Those decisions require information beyond the DNS lookup.
The filter only acts on queries that reach it. A browser, VPN or application can use a resolver different from the one expected by the network administrator. That possibility belongs in the diagnosis, but an approved network policy still governs which service a managed device should use. Changing to an unapproved resolver is not a substitute for reviewing a mistaken rule.
Make a Narrow Authorized Exception
When a legitimate dependency is demonstrably blocked, the network owner can make a targeted exception. Prefer the exact necessary domain over a parent-domain wildcard or disabling the whole blocklist. In Pi-hole, an enabled exact allowlist entry takes precedence over matching deny entries for the relevant client group. In BIND RPZ, use a pass-through rule with the appropriate zone priority.
Record the name, rule source, affected client group and reason for approval before making the change. Retest the feature that failed and confirm that unrelated blocked names remain blocked. If the approved exception restores access, retain the observed result and schedule a review if the dependency is temporary. If the feature still fails, examine the next observed failure rather than expanding the exception to an entire parent domain without evidence.