What Is Reverse DNS?
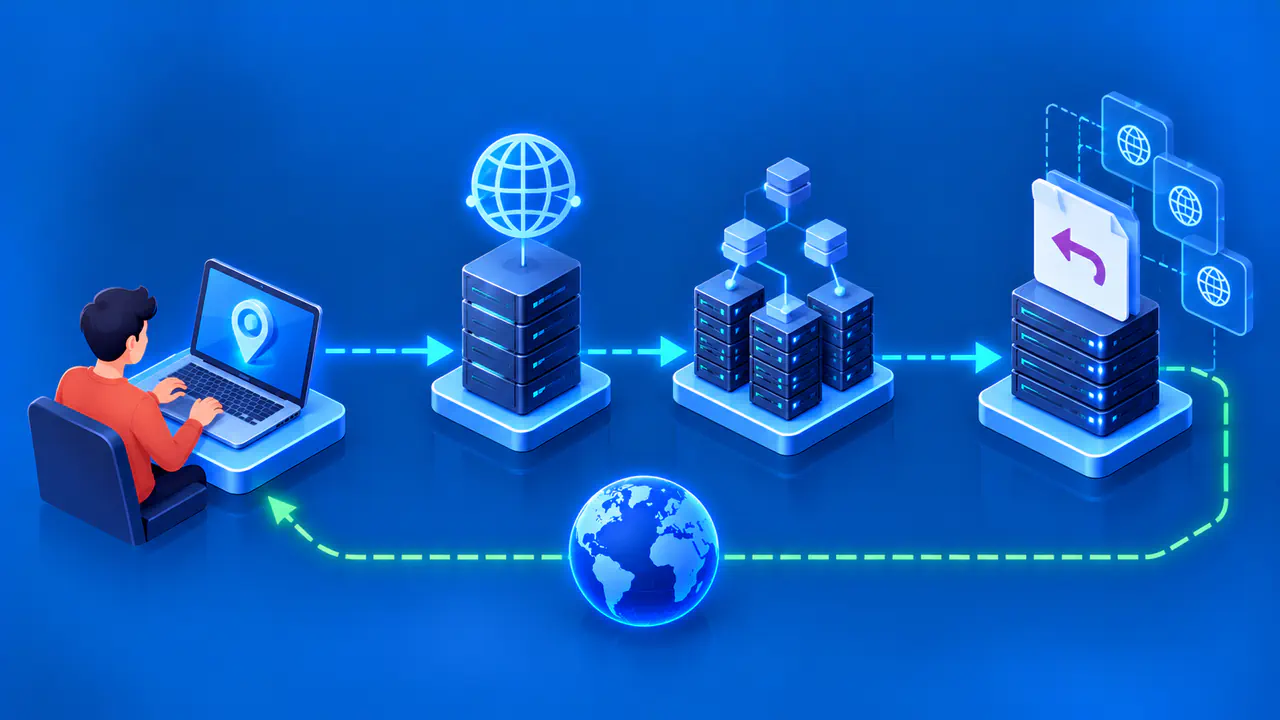
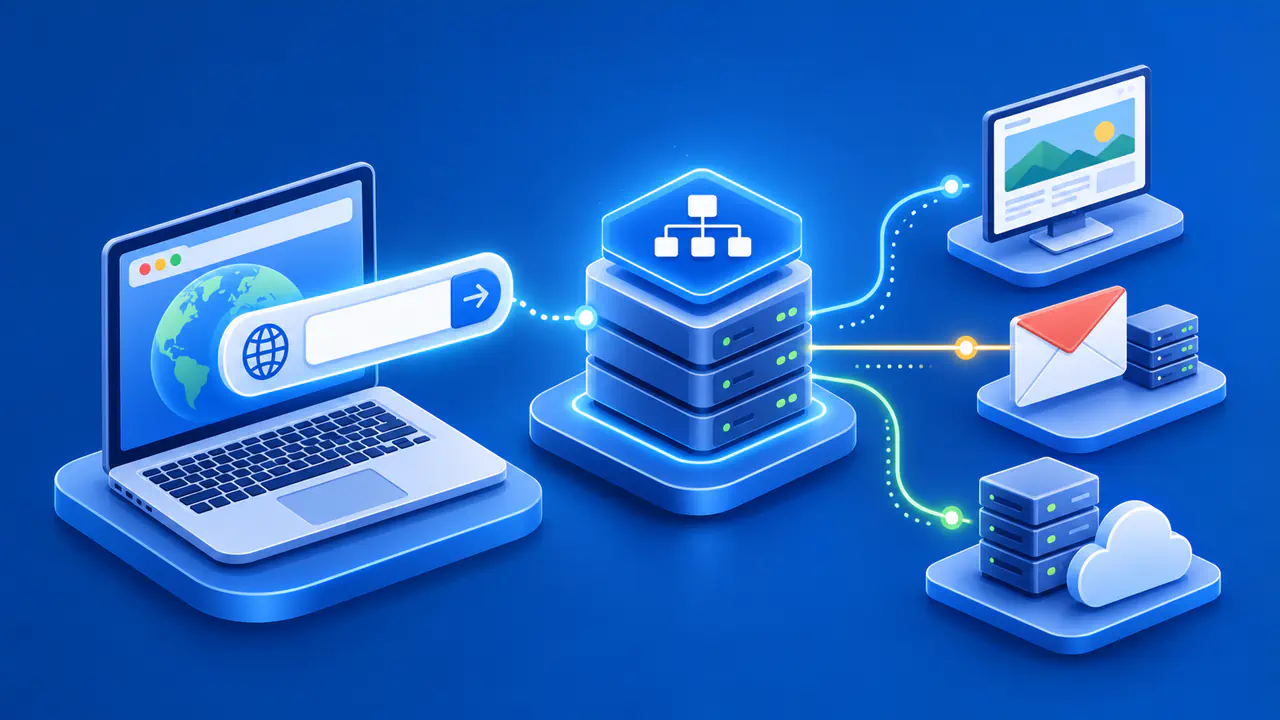
Reverse DNS starts with an IP address and asks for a domain name associated with it. The answer comes from a pointer record, usually called a PTR record, in the Domain Name System. A forward address lookup goes in the other direction, starting with a name and returning an IPv4 or IPv6 address. A PTR result supplies a network label; it does not identify the person using the address or list every website using that IP.
For example, an administrator might give a server address a descriptive PTR name. A lookup can return that name if the reverse DNS zone has been configured. If no PTR record is present, the lack of a name does not mean the address is unused or invalid. The record is published DNS data, rather than a name discovered by inspecting the device.
How a PTR Lookup Works
In forward DNS, an A record associates a name with an IPv4 address, while an AAAA record associates a name with an IPv6 address. A reverse lookup instead asks for PTR data at a DNS name derived from the IP address. The lookup software usually constructs that query name for you. The query name and the domain name returned in the PTR record have different roles.
For an IPv4 example, the documentation address 192.0.2.18 becomes the query name 18.2.0.192.in-addr.arpa. The four address numbers are reversed, then followed by in-addr.arpa. A hypothetical PTR answer might name server.example.com. The reversed address selects the DNS entry to query, while server.example.com is the value returned from that entry. This illustrates the format, rather than an actual lookup of a live server.
IPv6 reverse queries use ip6.arpa. The address is represented by all 32 hexadecimal digits, with the digits in reverse order and dots between them. The final digit of the expanded address appears first in the query name. This differs from reversing the four decimal numbers of an IPv4 address, although both queries request the same PTR record type.
Some applications follow a PTR answer with a forward lookup of the returned name. For IPv4 they check the name's A records; for IPv6 they check its AAAA records. If those records include the original address, the forward and reverse results agree for that check. An A or AAAA record does not automatically create a PTR, and a PTR does not automatically create a corresponding address record.
Who Controls the Reverse DNS Zone?
The address provider or a network operator with delegated control manages the reverse DNS zone. A zone is a part of the DNS namespace used to manage records for an address range. Delegation directs queries for that part of the namespace to designated authoritative name servers, which publish the zone's records.
Owning a website domain does not automatically give you control over the reverse zone for the website's public IP address. The forward records for a domain and the reverse records for an address are managed separately. A hosting customer may need the address provider to publish or change a PTR name. The precise arrangement depends on who manages the reverse zone, rather than who registered the website's domain.
A provider may publish a generic name that describes its infrastructure. That name can differ from the website's domain or the commercial brand used by a customer. A descriptive label may help an operator recognize a router or server, but the wording reflects a naming choice. An abbreviation that resembles a city name is not a reliable measurement of the device's location.
Why a PTR Record May Be Missing
Reverse DNS is not guaranteed for every public IP address. The responsible operator may not have added a PTR record, or the reverse zone may not be delegated or configured correctly. Dynamic addresses can have generic names or no published name. A connection can still work even when its address has no PTR record.
Check the actual DNS response before treating a blank result as missing data. NXDOMAIN indicates that a DNS name needed for the lookup does not exist. For a PTR query, NODATA indicates that the name exists but has no PTR data. SERVFAIL means the server could not complete the query, while a timeout means no reply arrived within the waiting period. SERVFAIL and timeouts do not establish that no PTR record exists.
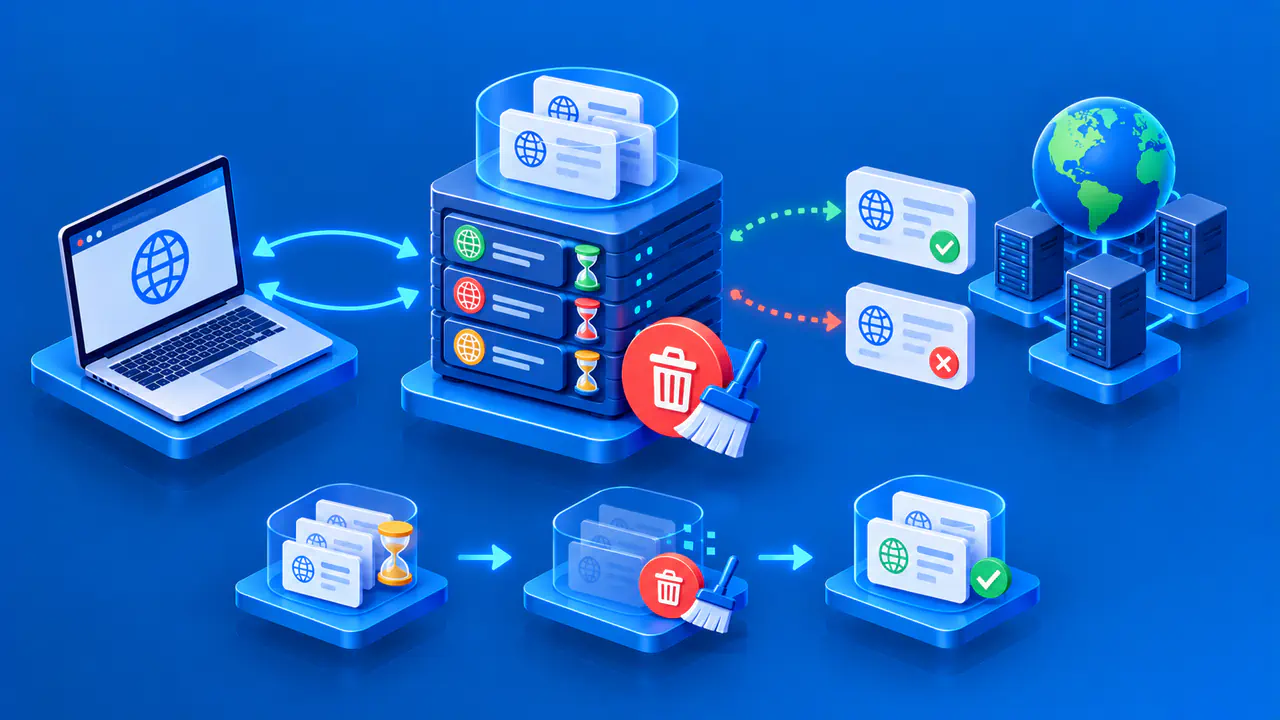
DNS answers can also be cached. After an operator changes a PTR, one resolver may still hold the old answer while another has refreshed its copy. TTL normally limits how long a resolver reuses cached data, and negative answers can be cached too. A newly added record may therefore not appear immediately through every resolver. Compare the queried address, response status, and resolver when investigating a difference.
Private addresses may have different names inside different networks. Many homes and businesses reuse addresses such as 192.168.1.1, so a public reverse lookup cannot uniquely identify the network using one. An organization can maintain internal reverse DNS for its own addresses. A public resolver may return no name even when an internal resolver has a useful local record.
Interpreting the Returned Name
A PTR name can be descriptive, stale, generic, or misleading. The name alone does not prove that the organization it mentions owns the IP address block. The regional internet registry's records can identify the organization registered for the address range. Routing information describes how the range is announced or carried. A DNS name does not replace either kind of evidence.
Reverse DNS also cannot enumerate every website hosted at an address. Several domains can have forward records pointing to the same IP without appearing in its PTR data. A hosting platform may use one infrastructure name for an address shared by many customers. Reading that name as the complete list of sites would miss the separate domain configurations.
In logs and diagnostic results, keep the original IP address and event time alongside any reverse name. Also record when the DNS lookup was made, since a lookup performed today may return a different name from one published when an older event occurred. If a lookup fails, retain the response status or timeout instead of replacing the address with an assumed hostname. That preserves the observation you can actually support.