How to Verify a Domain with a DNS TXT Record
Many services ask you to add a DNS TXT record before you can use a domain with your account. The service supplies a record name and a verification token, then queries that name for the matching TXT value. Publishing the token demonstrates control over the DNS records for that name. It does not, by itself, establish legal ownership of the domain or configure email delivery.
To complete verification, copy the token issued for your account, add it at the active DNS provider, check the published value, and return to the service to confirm the result. Saving a record in an inactive DNS dashboard does not publish it for the domain. A record at the wrong name will also be missed when the service queries the requested name.
Get the Exact Token from Your Service
Sign in to the service account that will use the domain and start domain verification. Copy the requested record type, host or name, value, and any displayed instructions. Use the value shown for your account and domain. Do not use a sample value from a tutorial or a token from another organization. Keep the verification page open so you can compare its instructions with the DNS entry.
Record names vary. A service may request a TXT value at example.com itself, shown as @ in some DNS panels, or at a name such as _verify.example.com. A panel might expect only _verify because it appends the domain automatically. Check the full name shown by the panel before saving. Entering _verify.example.com where the panel expects only the label can produce _verify.example.com.example.com.
Find the Authoritative DNS Provider
The registrar that sold the domain is not always the provider serving its DNS. Look up the domain's delegated name servers and identify the account or provider that manages the corresponding zone. Make the change in that active zone. An inactive copy of a zone at the registrar will have no effect while the domain is delegated elsewhere.
With BIND's dig utility, an NS lookup such as dig example.com NS can help identify the domain's name servers. Querying a specific authoritative server with dig @ns1.example.net example.com TXT checks what that server is currently serving. Replace all sample names with the actual domain and server before using a command. If the returned servers differ from those listed in the DNS dashboard you are using, check the domain's current delegation before editing records there. For a subdomain delegated to separate name servers, use the DNS zone responsible for that subdomain.
Add a TXT Record without Replacing Other Records
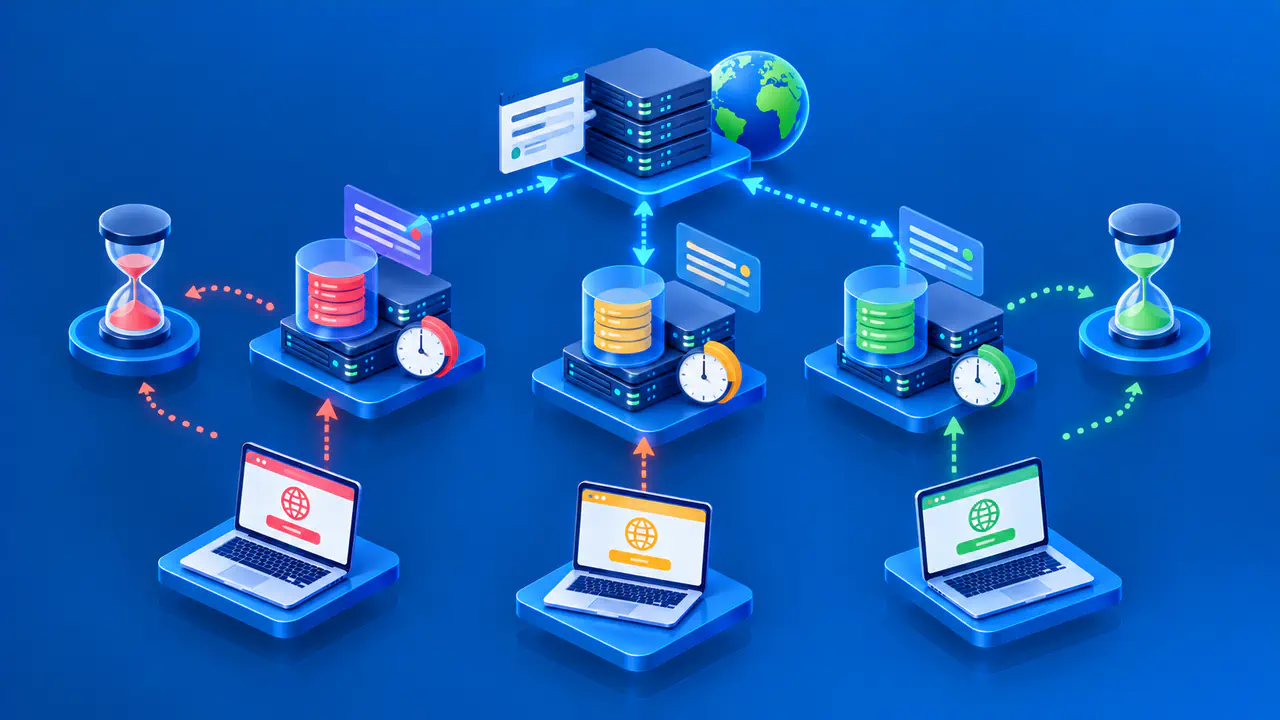
In the authoritative DNS panel, create a new TXT record at the name specified by the service and paste its value exactly. Follow the DNS provider's instructions for its host field and any automatic quoting of text. Avoid introducing a leading or trailing space into the token. Use the DNS provider's default TTL unless the service specifies a different value. TTL controls how long a DNS answer may be cached; changing it does not correct a wrong name or token.
A DNS name may have several TXT records. Keep existing TXT values, including any SPF policy used for email authentication, unless the person responsible for those records has planned a change. Add the new verification value as a separate record rather than overwriting another TXT entry. The DNS provider may display these records as separate rows or as multiple values in one record set. Keep the verification token separate from the SPF policy and from other services' tokens.
Review the saved record's fully qualified name and exact token. Take care with any automated wizard that proposes additional DNS changes. For example, Microsoft 365 separates domain verification from subsequent service DNS setup, where an MX change can move mail delivery. If you only intend to verify the domain, leave unrelated mail settings unchanged.
Query the Published Value
After saving, query the requested name and TXT type. For example, dig example.com TXT asks for TXT records at example.com; replace example.com with the full requested name if verification is at a subdomain. A query to an authoritative server shows whether that server has published the record. A recursive resolver looks up DNS records on behalf of clients and can cache the answers. Its response may therefore differ from a recently updated authoritative answer.
Find the verification record in the response and compare its complete value with the service token. Other TXT records at the same name do not establish that your token is present. DNS tools often put quotation marks around text as part of the output format; follow the DNS provider's instructions for entering the value rather than assuming those display marks belong in the token.
A single TXT record can contain multiple text strings. Those strings belong to that one record and are different from separate TXT records for other services. If the token is long, check how the provider stores it and how the verifying service expects it to be represented. Do not join unrelated TXT records into one value.
If no matching record appears, check the full record name, active DNS provider, and saved entry. Query the domain's authoritative servers individually if their responses disagree; the record may not yet be available on every server. If the authoritative responses match but a recursive resolver still returns an older answer, allow that cached answer to expire before retrying.
Complete Verification in the Service
Once DNS returns the expected value, return to the service and select its verification button or follow its completion instructions. Some services retry automatically; others require a button press. If verification still fails, compare the record name and token shown in the current service session with DNS again. The token may have changed if you switched accounts or restarted setup, and the service may not check DNS immediately.
Confirm that the service now shows the domain as verified, then note which account and service the record belongs to. A verification token published in public DNS can be read by anyone who queries that name, so it should not be treated as a secret. Never put a password or API credential in the TXT value.
Keep or remove the verification record according to the service's instructions. Some services, including Google Search Console, check the record again after initial verification and require it to remain available. Keep those required records when moving DNS to another provider so that the service can still confirm your access.