Punycode, IDNs, and Lookalike Domain Names
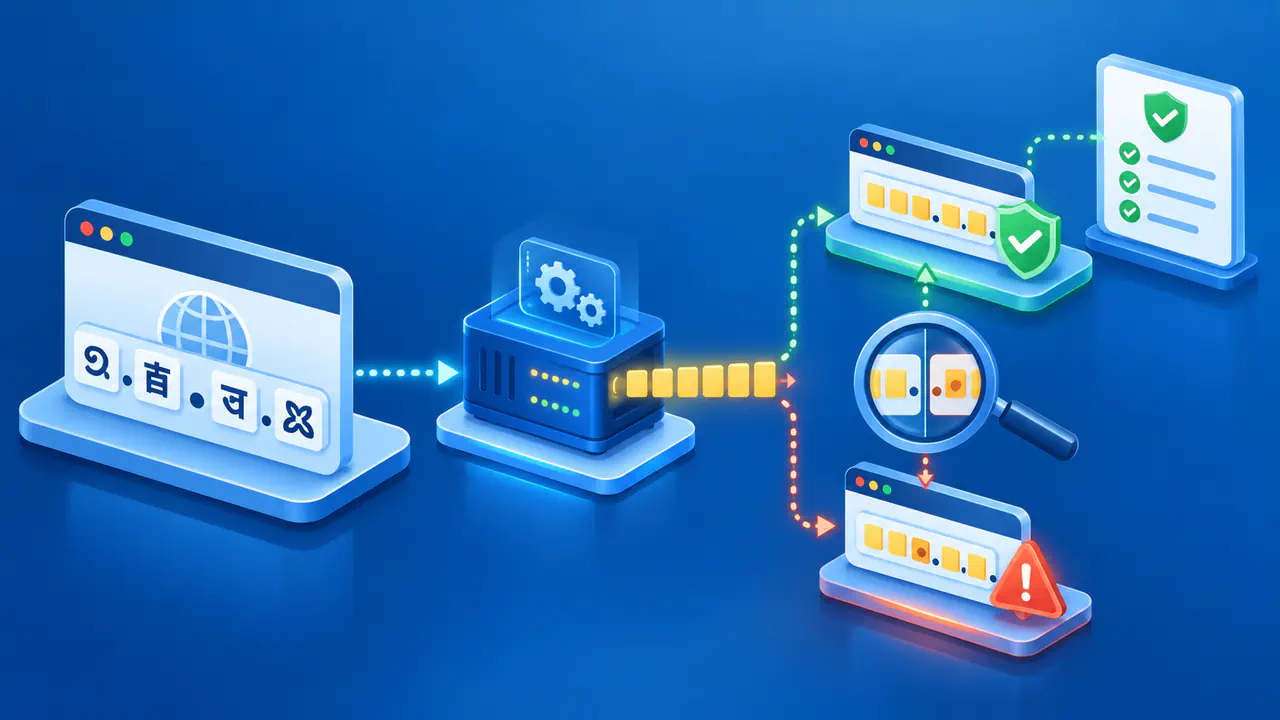
An internationalized domain name, or IDN, can include non-ASCII characters, allowing names to be written in many languages. Applications convert its internationalized labels to an ASCII form for DNS lookups. These encoded labels begin with xn-- and use Punycode. The prefix identifies an encoding format; it does not establish whether a site is trustworthy.
Two domain names can look almost identical while containing different characters and leading to different sites. The Unicode and ASCII forms of one valid IDN, however, identify the same name. When checking a link, distinguish two spellings of the same domain from two different domains that only look alike.
Understand U-Labels and A-Labels
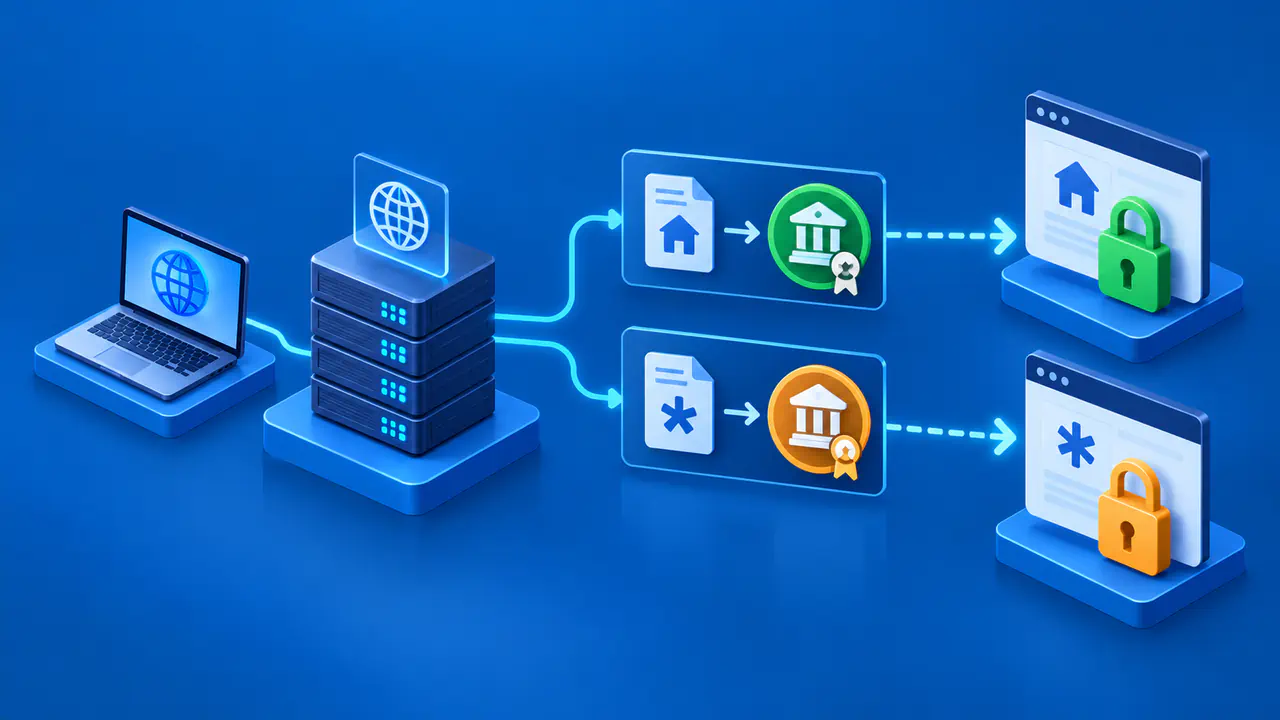
A U-label is the valid Unicode form of an internationalized domain label. The corresponding ASCII-compatible form is an A-label. An A-label starts with xn-- and contains the Punycode encoding of that U-label. Internationalized Domain Names in Applications (IDNA) defines the rules that make these labels valid. Each label is one component between dots, such as www, example, or com in www.example.com. Applications convert each internationalized label separately.
For example, the German label bücher has the A-label form xn--bcher-kva. An IDNA-aware application treats these as two representations of the same label. The letters have been encoded, not translated into another language. An ordinary ASCII label such as example stays as it is and does not acquire the xn-- prefix.
Punycode performs the encoding, while IDNA also restricts which characters and combinations can form a valid label. Adding xn-- to arbitrary text does not make a valid A-label. A tool that only decodes Punycode may return text that fails IDNA validation. Use a tool that checks the label's validity as well as converting it between Unicode and ASCII.
Read the Full Hostname, Not Just Its Appearance
A lookalike attack uses a name that appears close to a familiar one. A character from another script may resemble a Latin letter, and a slight spelling change or misleading subdomain can be just as deceptive without any IDN. Visual resemblance alone cannot establish whether two hostnames are equal. Compare the domain you expect with the complete hostname, including its suffix and subdomains. For example, accounts.example.com.login.example.net belongs under example.net, even though example.com appears near the start. The extra labels do not make it a subdomain of example.com.
The registrable domain is the part registered beneath a public suffix. With a suffix such as .com, that is typically a name such as example.com; other suffixes, such as co.uk, contain more than one label. Counting the last two labels is therefore not a reliable rule for every hostname.
For a service where you sign in or enter sensitive information, use a trusted bookmark or an address obtained through a known channel. Do not rely on the visible text of a link in an unexpected message. Copy the link address without opening it, then inspect the hostname as text. If you have already opened the page, check the browser's address bar before entering information.
A familiar logo does not authenticate the hostname. HTTPS also does not establish that a lookalike domain belongs to the organization you intended to visit: a different domain can have its own valid TLS certificate. Compare the actual name with the known address even when the connection is encrypted.
Why Browsers May Display Different Forms
Browsers may show an IDN label as Unicode or as its ASCII xn-- form depending on their display policies and the characters involved. Chrome checks for potentially confusing character combinations and may also warn about lookalike addresses. The behavior can change with browser versions and may differ between applications. A copied URL, a DNS tool, and a browser address bar can therefore show different forms of the same underlying label.
Do not treat the absence of a browser warning as confirmation that you reached the right domain. Display checks do not cover every deceptive spelling, and a valid IDN can be used by either a legitimate site or an impersonator.
Verify the Intended Hostname
Start with a known address obtained independently of the message or page you are checking. Use a trusted URL parser to identify the hostname separately from the path, query, port, and other URL components. A familiar name elsewhere in the URL does not identify the destination server.
For example, in https://accounts.example.com@other.example.net/sign-in, the hostname is other.example.net. The text before the @ sign is user information, not the destination hostname. This is a structural example, not an address to open.
For each internationalized label, use an IDNA-aware tool to obtain the Unicode and ASCII forms. Compare the validated ASCII hostname with the trusted reference after applying the same processing to both. DNS name comparison ignores ASCII letter case, but different letters, digits, dots, or hyphens can change the name. Converting a valid A-label to Unicode and back should reproduce that A-label, allowing for ASCII letter case; that check establishes encoding equivalence, not the site operator's identity.
Do not paste a sensitive URL into an unknown online converter. Use a trusted local tool for private links, which may contain access tokens in the path or query. If you have already followed a link, check the final hostname after any redirects as well. If the name differs from the trusted reference, contact the service through an established channel before entering credentials.
Report a Suspicious Domain Accurately
When reporting a suspicious domain, preserve the exact hostname and its A-label form if conversion succeeds, along with the browser or application that displayed the name. Include the address you expected and explain how you received the link. If conversion fails, record the error rather than changing characters to make the name pass validation. If redirects were already observed, note the starting and final hostnames without reopening the link just to collect more details.
A screenshot can show what looked misleading, but it does not preserve the exact character sequence for comparison. Include the hostname as text too. Remove passwords, access tokens, and other private data from any URL you share; these values are not needed to compare the domain names.