How to Control Referrer Data in HTTP Requests
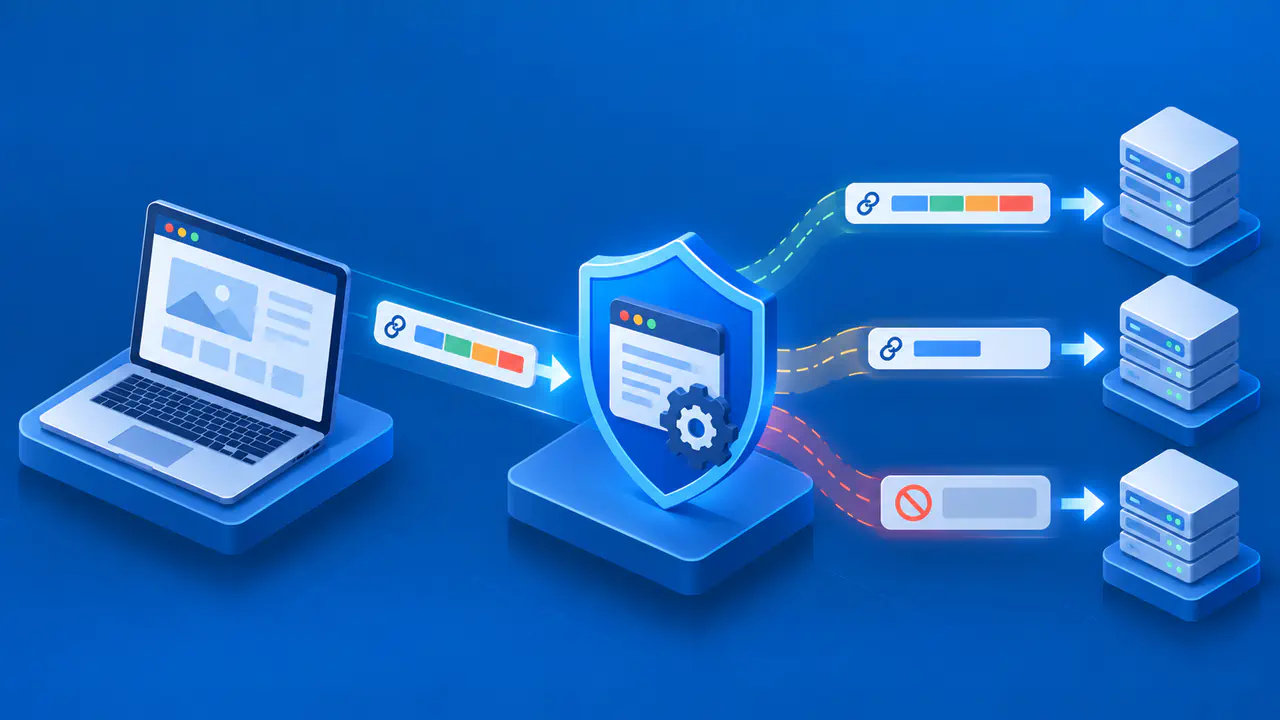
When a browser follows a link or loads a resource, it may include a Referer request header telling the destination which page or resource led to the request. Referer is a historical misspelling; the response header that controls this information is Referrer-Policy. Depending on the policy and destination, the browser may include the source URL with its path and query, send only its origin, or omit the referrer.
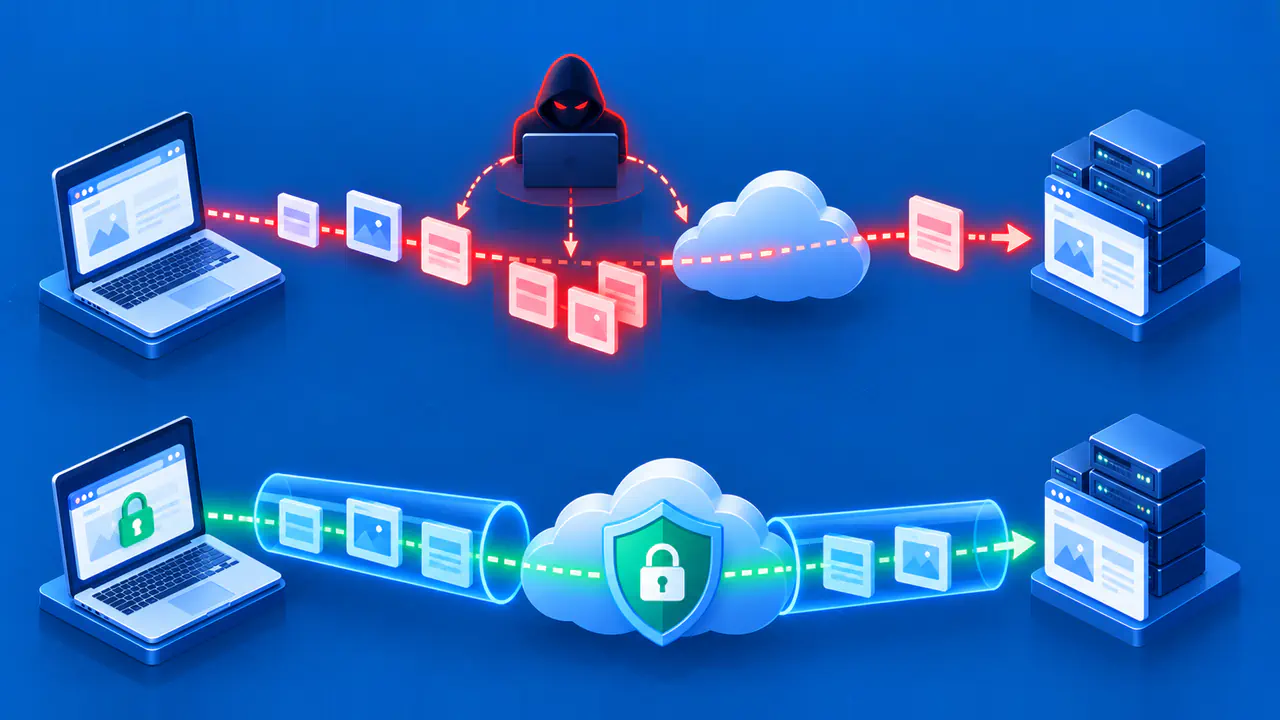
A path or query string may contain information that should not reach another site. Some site functions and analytics, however, depend on knowing the source page. Decide how much of that address each destination needs, then inspect browser requests to check what is actually sent. Referrer data is not a complete browsing history, and changing the policy does not hide a client's network IP address.
Decide What Data Each Destination Needs
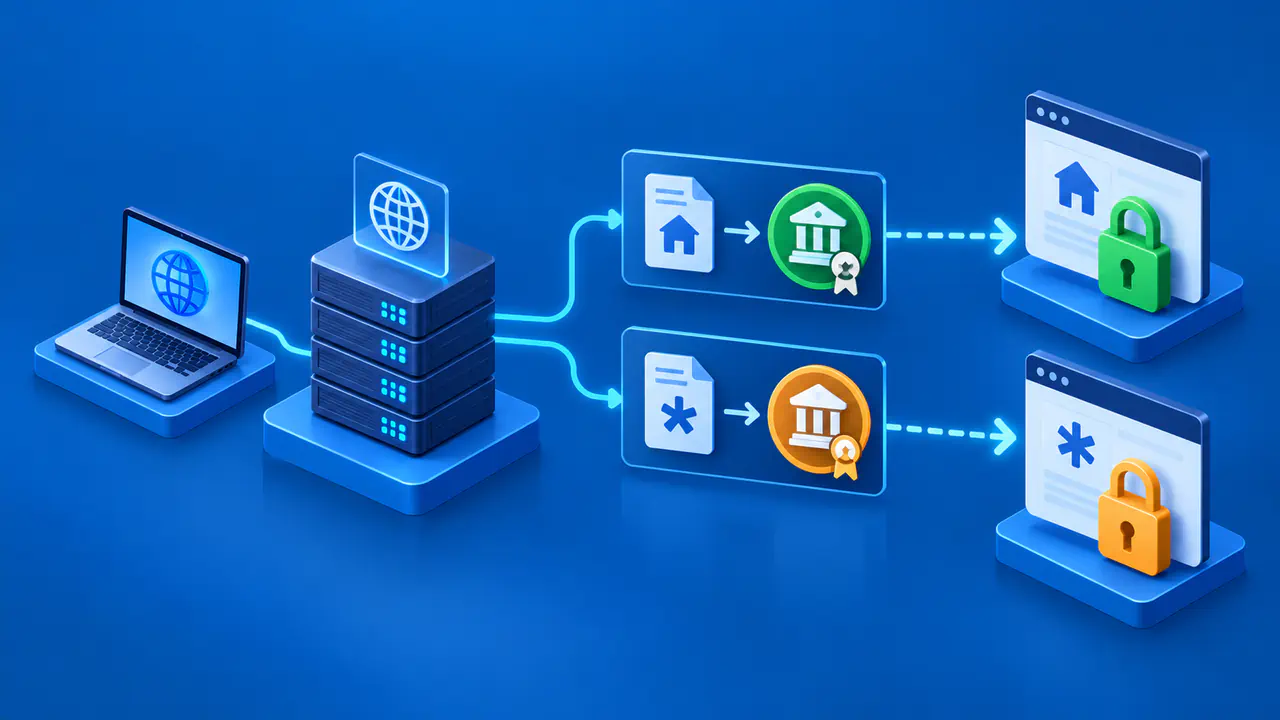
Begin with a source page such as https://example.com/account?view=recent. An origin consists of the scheme, hostname, and port; an origin-only Referer value for this example is https://example.com/. The path and query identify more than the site itself. Even when a policy allows those details, the browser removes any URL username, password, and fragment, meaning the part after a # character.
A request is same-origin only when its scheme, hostname, and port match the source. Another hostname or port is cross-origin even if the same organization operates both destinations. A third party may need no more than the origin, or no referrer at all. Consider requests from HTTPS to plain HTTP separately because an unencrypted connection can expose the transmitted information.
Check the links, images, scripts, frames, redirects, forms, and scripted requests on pages containing sensitive information. Look for account identifiers or tokens in their URLs, and keep sensitive values out of URLs wherever possible. Referrer policy should not be the only protection for those values. Ask whether external partners need to identify the source site or the specific page before choosing how much information to share.
Choose a Policy for Same-Origin and Cross-Origin Requests
Modern browsers normally use strict-origin-when-cross-origin when no valid policy is set. Under this policy, same-origin requests can include the path and query, while cross-origin requests receive only the origin unless the connection downgrades from HTTPS to unencrypted HTTP. On a downgrade to an ordinary HTTP site, the browser omits the referrer. Local development URLs such as http://localhost can be an exception because browsers may treat them as trustworthy. Setting an explicit policy makes the site's choice clear and allows tighter restrictions where needed.
Choose a stricter or more permissive value only after comparing the information each option permits:
no-referreromits the Referer header entirely, including on same-origin requests.same-originpermits the path and query for same-origin destinations and omits the referrer for other origins.strict-originpermits only the origin and suppresses the referrer on a security downgrade.originpermits the origin even when the request downgrades to HTTP.unsafe-urlpermits the path and query for external destinations, including HTTP destinations, so it can disclose more than an analytics service needs.
For an account page, consider no-referrer if no destination needs source information, or same-origin if only the site itself needs the page address. A public page may allow external sites to receive its origin. Compare the expected outgoing values with the information needed by each site function; the same choice need not suit every page.
Apply Header and Element-Level Controls
Send the chosen policy in the response that delivers the document, for example Referrer-Policy: strict-origin-when-cross-origin. A content delivery network (CDN) or application may replace a value set on the origin server, so inspect the response that reaches the browser. Check representative pages served through each relevant template and delivery system.
HTML can also set the document policy with a meta element in the head, such as <meta name="referrer" content="no-referrer">. For one supported element, add a setting such as referrerpolicy="no-referrer"; links, images, scripts, and frames support this attribute. A link can instead use rel="noreferrer" to omit the referrer for that navigation.
Check element attributes when individual requests differ from the page policy. External stylesheets can use a policy sent with their own responses for resources they load; without one, the browser applies its default policy. Inline styles use the document's policy. Browser privacy settings can further restrict referrer information, so test the browsers and settings used by the intended audience.
Referer and Origin are different request headers. Origin identifies an origin without a path, and its inclusion follows separate rules. A referrer policy can make Origin contain null for some requests, such as a form POST under no-referrer, but it does not remove Origin from every request. Referrer policy does not replace cross-origin resource sharing (CORS) rules or server-side request authorization.
Observe Outgoing Requests and Redirects
Use browser developer tools or a controlled receiving endpoint to inspect the actual outgoing request. Compare three cases: a same-origin HTTPS request, a cross-origin HTTPS request, and an HTTPS-to-HTTP request if that downgrade is relevant and permitted in a safe test environment. Check whether Referer is present, which value it contains, and which policy applies to that request. Do not place real tokens or personal data in test URLs.
Test redirect chains rather than only the final destination. A redirect changes the destination URL, and its response can set a referrer policy for the next request. Inspect each hop to see what was sent to each destination. A final request with no referrer does not prove the earlier redirect endpoint saw none. Likewise, a policy on the final page cannot retroactively change a request already made to reach it.
Repeat these checks after changing a CDN rule, HTML template, element attribute, or the browsers the site supports. A new policy cannot erase server logs or headers already sent. Before deploying a more restrictive policy, check whether services that use referral data still work when they receive only the origin or no referrer. Record the expected loss of detail so that reduced referral data is not mistaken for a logging fault.