HTTP vs HTTPS: What Is the Difference?
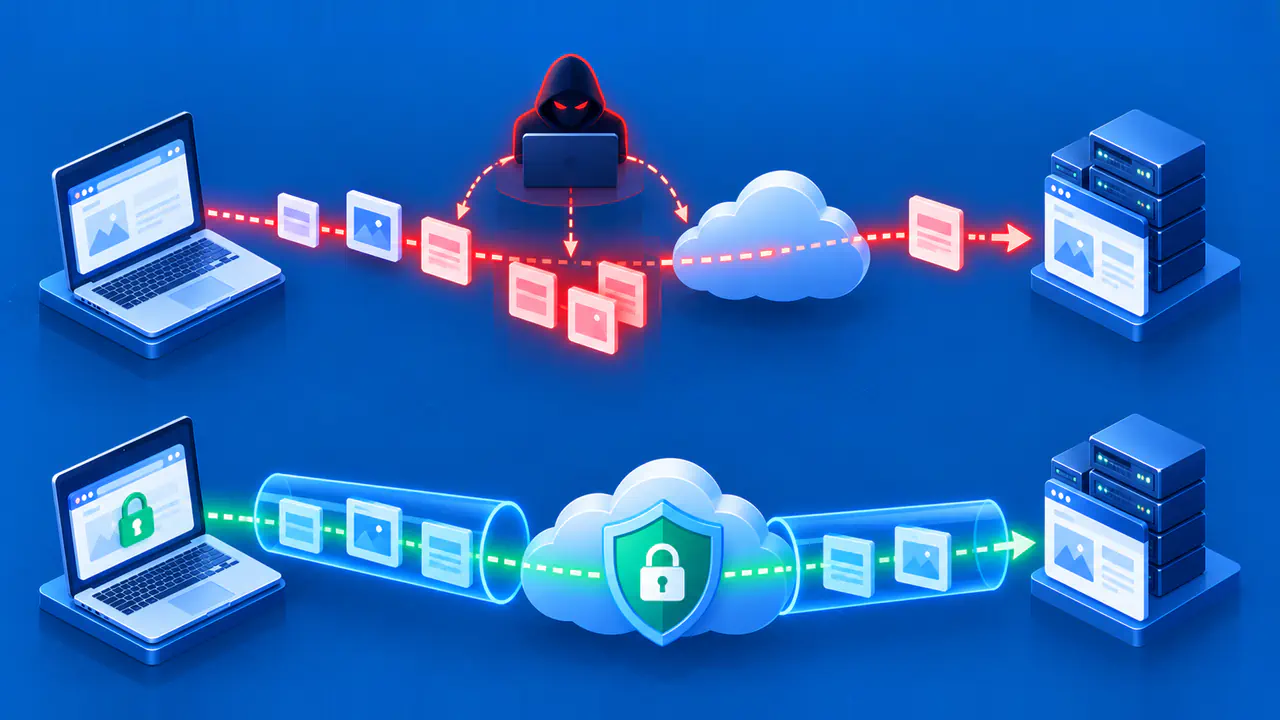
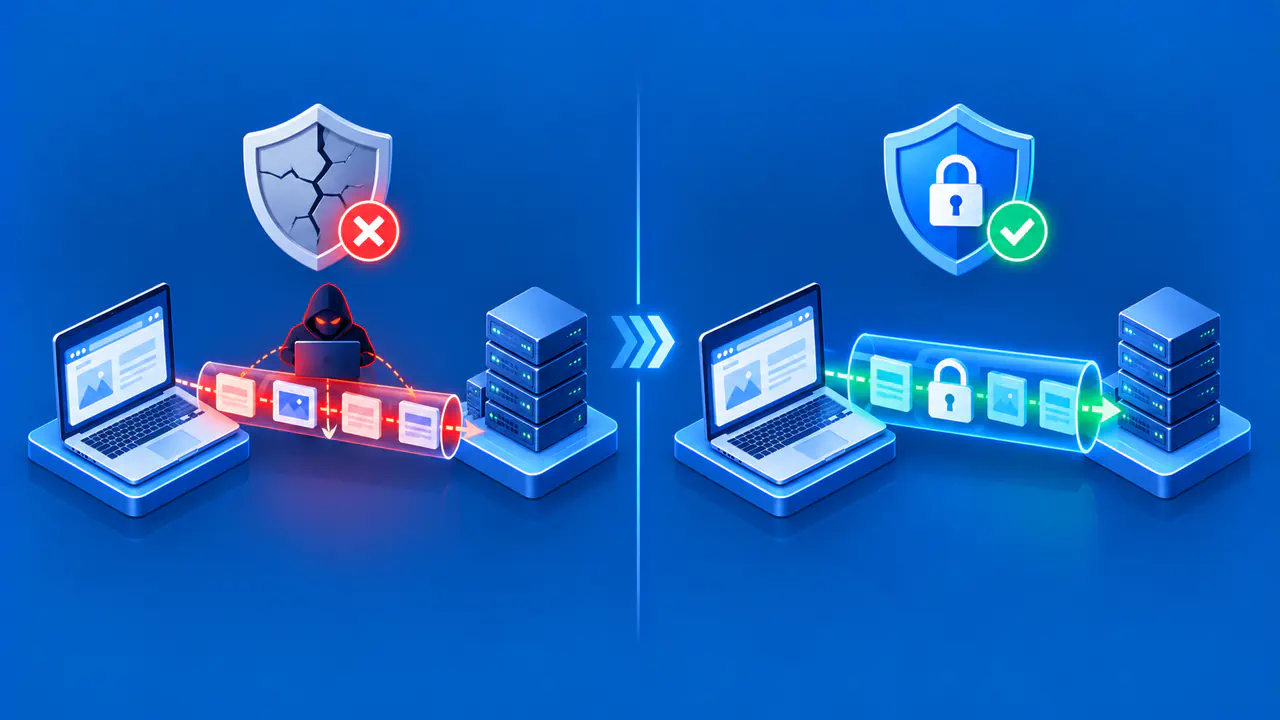
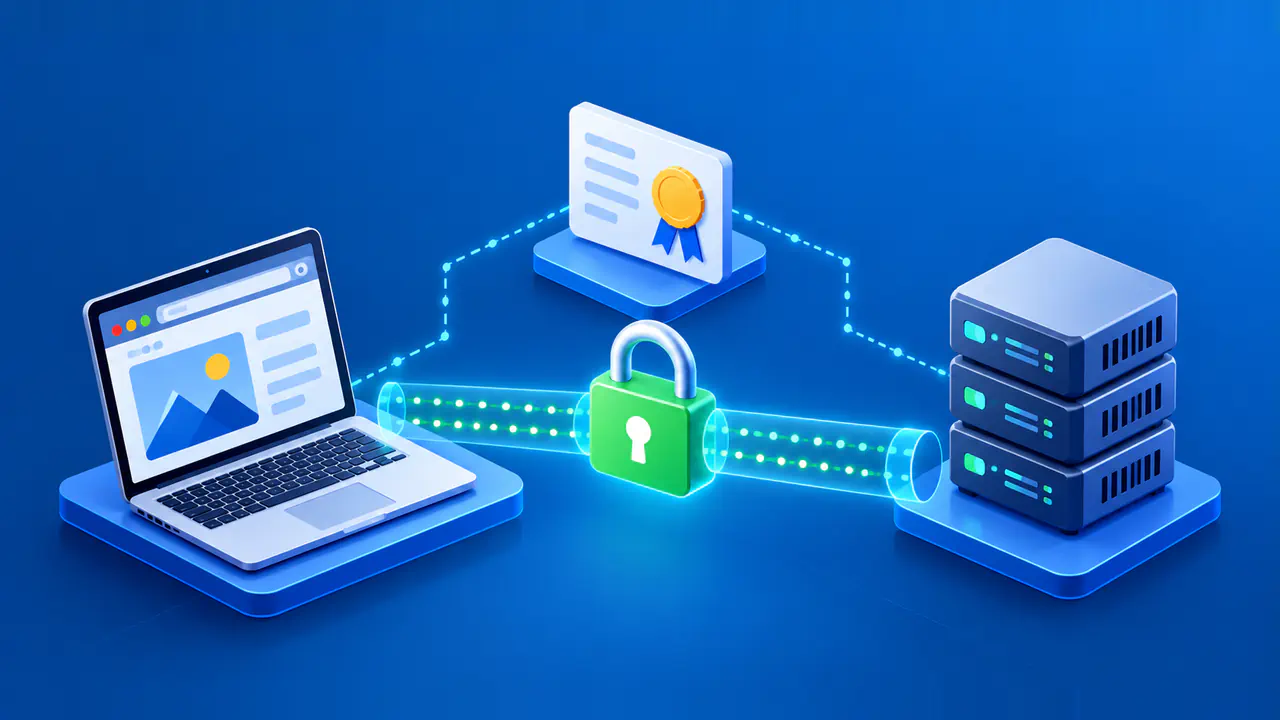
HTTP and HTTPS carry the same kinds of web requests and responses, but HTTPS protects the connection with Transport Layer Security (TLS). Ordinary HTTP sends those messages without transport encryption. With HTTPS, the browser checks the identity of the server it connects to and encrypts the exchange with that server.
The difference matters whenever a page loads content or sends information across a network. HTTPS protects the connection, not the honesty of the website or every place data may go after the connection ends.
How HTTP and HTTPS Carry a Web Request
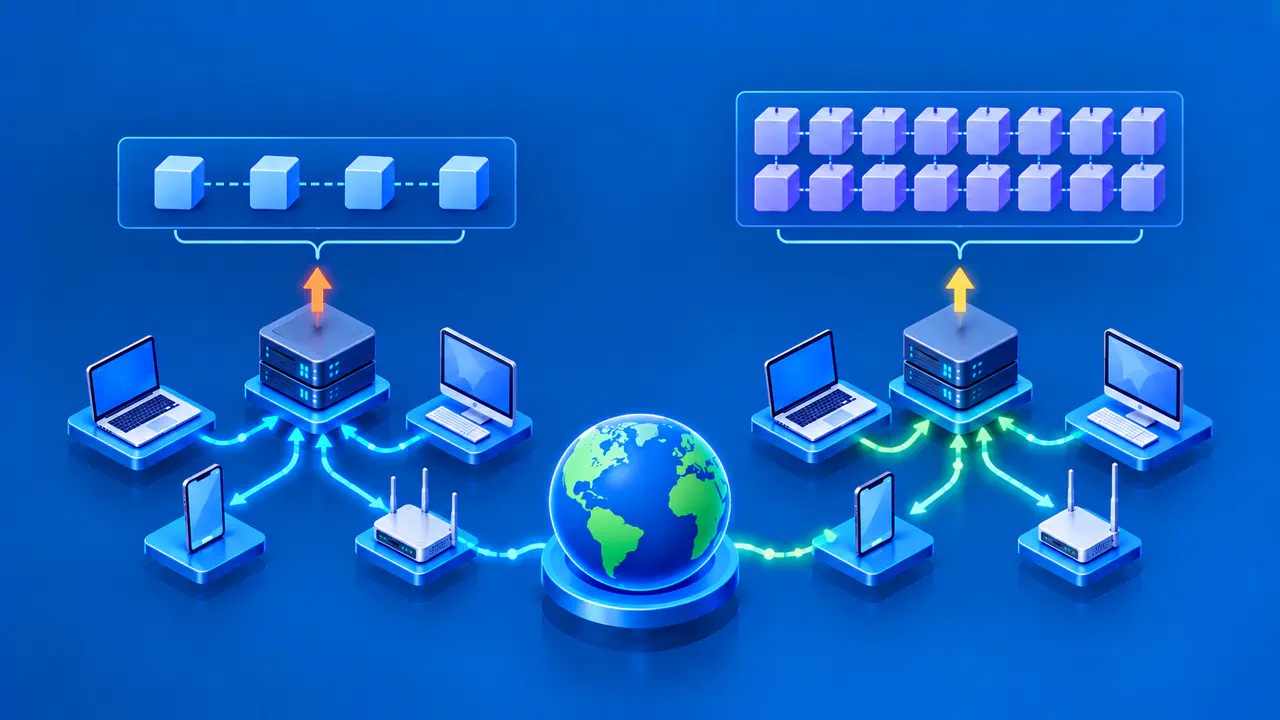
A browser requests a page by sending an HTTP message that identifies the resource it wants. The response can contain a page, an image, an error, or other data. On a plain HTTP connection, someone able to observe or interfere with that connection can read the messages and may alter them in transit. A password submitted over HTTP travels unencrypted on that connection, regardless of how the form looks.
The https:// prefix in a web address tells the browser to use TLS when communicating with the site. The http:// prefix identifies ordinary HTTP. The name before the colon, http or https, is called the URL scheme.
HTTP stands for Hypertext Transfer Protocol and defines how web requests and responses work. A browser can send the same kind of GET request to retrieve a page or a POST request to submit form data under either scheme. A response can still carry a 404 status under HTTPS. The status says what happened to the resource request; the scheme says how that exchange was transported.
What Happens to Submitted Data
Consider a request containing a search term in its path or query. On ordinary HTTP, that information and the response travel without TLS protection across that connection. On HTTPS, the path, query, headers, and response content are inside the protected HTTP exchange. An observer on the network may still see where the connection goes, but does not ordinarily see the precise search term from those HTTP messages after a valid TLS connection is established.
Cookies illustrate the same boundary. A cookie carried in a plain HTTP request can be exposed on that connection. HTTPS protects it in transit to the server handling that connection, but the service still decides what the cookie represents, when it expires, and how it is stored. On a public website, the Secure cookie attribute tells the browser to send that cookie only over HTTPS. A sensitive cookie needs this restriction even if the website normally uses HTTPS.
What TLS Adds to HTTPS
When a browser first establishes a typical HTTPS connection, the server presents a certificate. The browser checks whether the certificate is valid for the requested name and trusted under its certificate rules. This helps prevent an unrelated server on the network from silently claiming to be the requested site.
Later connections may resume an earlier TLS session without sending a new certificate. This uses authentication information from the earlier connection; it does not mean that HTTPS has stopped checking the server's identity.
Once a properly verified TLS connection is established, TLS provides confidentiality and integrity for its HTTP messages. Confidentiality keeps their contents unreadable to someone observing the network. Integrity makes unauthorized changes to those messages detectable. This matters even for a public page that collects no private data: an altered link could send a visitor to a different download.
Why the Whole Page Needs HTTPS
A page can load images, scripts, and other resources from several hostnames. Each connection needs appropriate protection. When an HTTPS page requests an insecure HTTP resource, browsers generally upgrade the request to HTTPS or block it, depending on the resource and browser rules. An old HTTP image address may therefore be upgraded, while an insecure script can be blocked. A site needs HTTPS for its required resources as well as its main page.
Where HTTPS Protection Ends
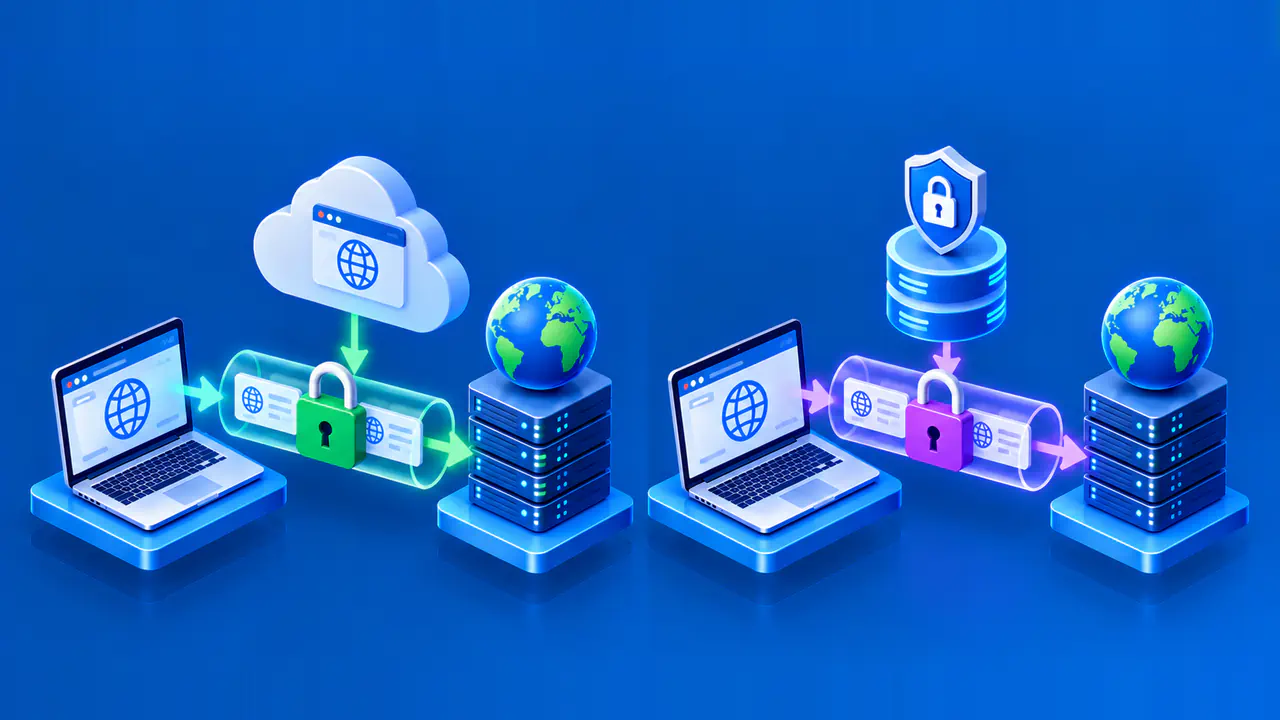
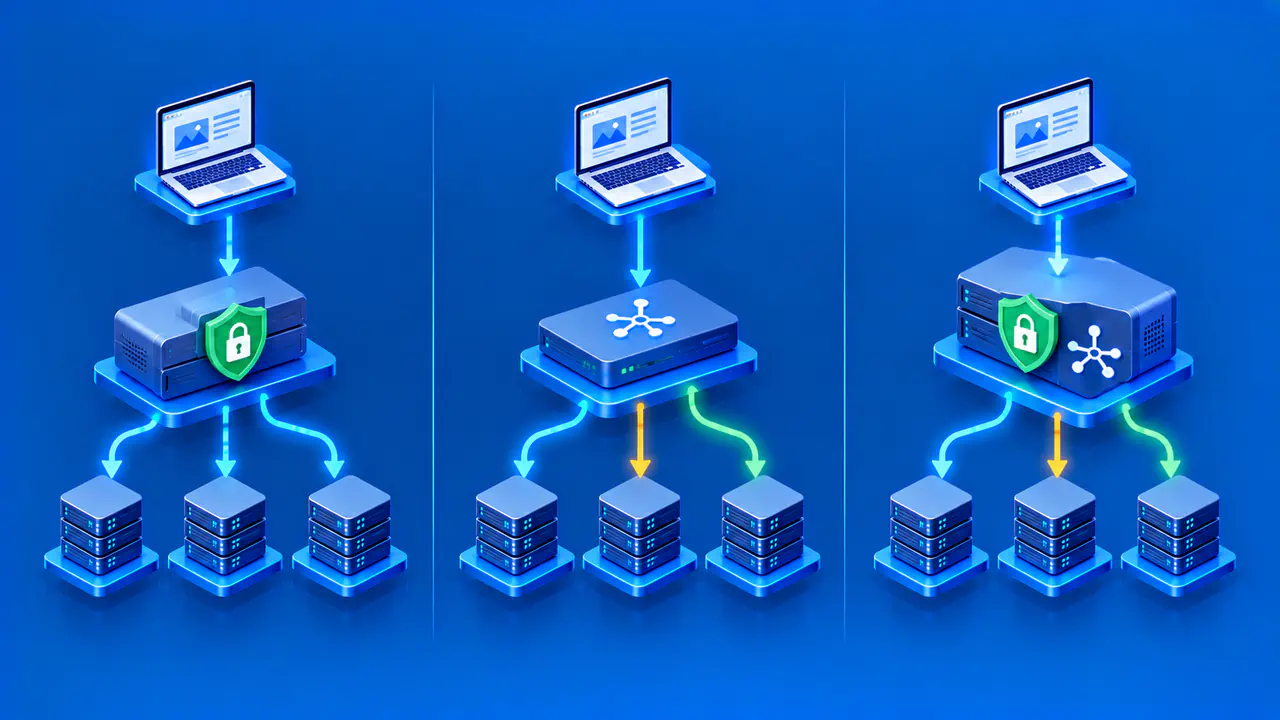
The server where a browser's HTTPS connection ends is the TLS endpoint. That server may be an intermediary, such as a content delivery network, rather than the origin server that hosts the website. The intermediary can read the HTTP message, apply routing or caching rules, and make a separate connection to the origin. The browser's HTTPS indicator does not show how that separate connection is protected. The site operator must configure protection between the intermediary and the origin as well.
The receiving service can read the request's path, query, headers, and submitted data. It may keep records according to its settings and policies. HTTPS does not erase information after it reaches the service or prevent the service from using it. Consider what information a website asks for and why before you send it.
Software on the device, including a browser extension with access to page data, may be able to read information before encryption or after decryption. HTTPS does not control what that software can access.
What a Network Observer May Still Learn
HTTPS does not make a connection invisible. A network operator can generally see the destination IP address, connection timing, and the amount of data transferred. Depending on the browser, network, and deployed privacy features, DNS queries or the TLS server name may also reveal the requested hostname.
This distinction is why HTTPS is different from a VPN. HTTPS protects one connection to a website's TLS endpoint. It does not automatically hide the device's other traffic or make the entire browsing session anonymous. A VPN has a different network scope and introduces its own endpoint.
Why an HTTPS Website Can Still Be Unsafe
A valid HTTPS connection shows that the browser established a protected connection to the named endpoint. It does not establish that the site's claims are true, that a download is harmless, or that an account request is legitimate. A deceptive site can obtain a valid certificate for a domain it controls and serve harmful content over HTTPS.
Read the actual hostname before entering sensitive information. A familiar design, a lock icon, or an https:// prefix cannot make a different hostname into the site you intended to visit. If the browser reports a certificate problem, treat it as an unresolved connection issue instead of clicking through on the assumption that the content is trustworthy.
Using HTTPS for a Website
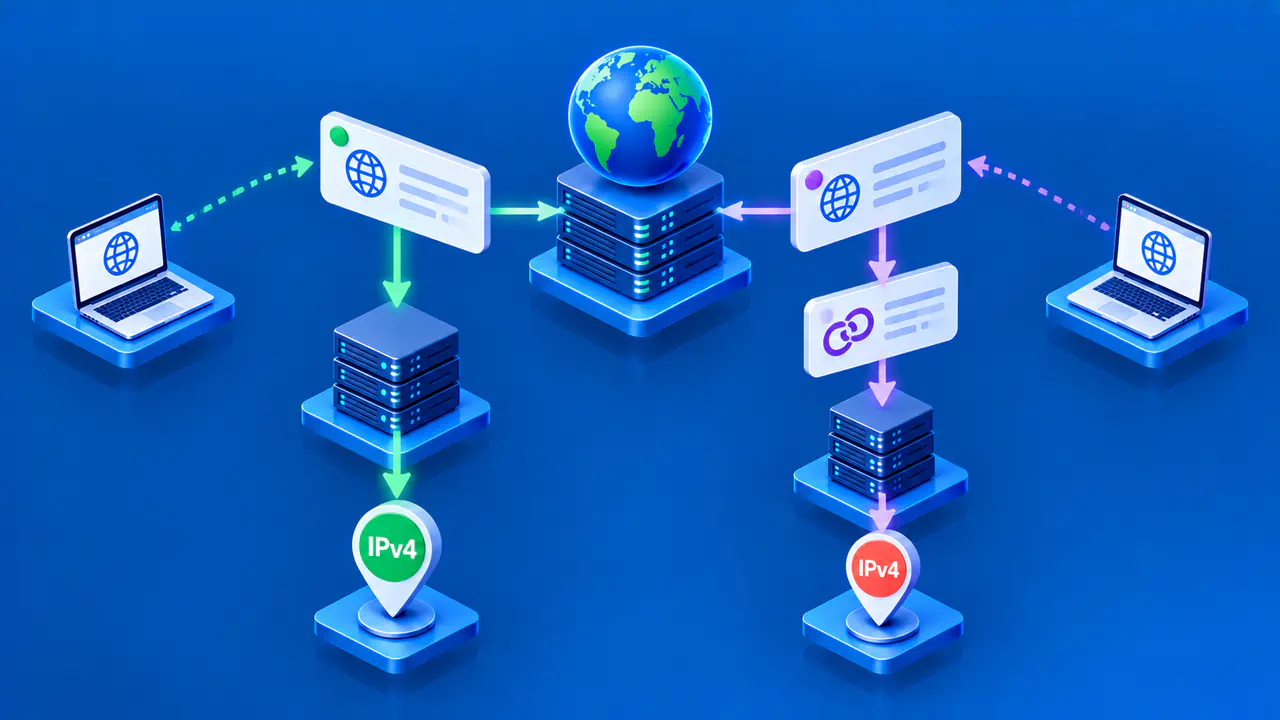
Changing http:// to https:// does not guarantee that the address will work. The server must support HTTPS for that hostname, and the HTTP and HTTPS addresses can serve different content. Browsers treat the two schemes as different origins, so permissions and some stored site data can also differ. A site must deliberately provide its intended pages over HTTPS instead of relying on the visitor to change the address.
To enable HTTPS, configure TLS for the site's hostname and serve its pages and resources over HTTPS. A certificate file or an HTTPS setting in a hosting panel does not confirm that visitors can load those pages securely. Check the site in a browser after deployment, and fix certificate or blocked-resource errors before asking visitors to submit information.