How to Create a CSR with OpenSSL
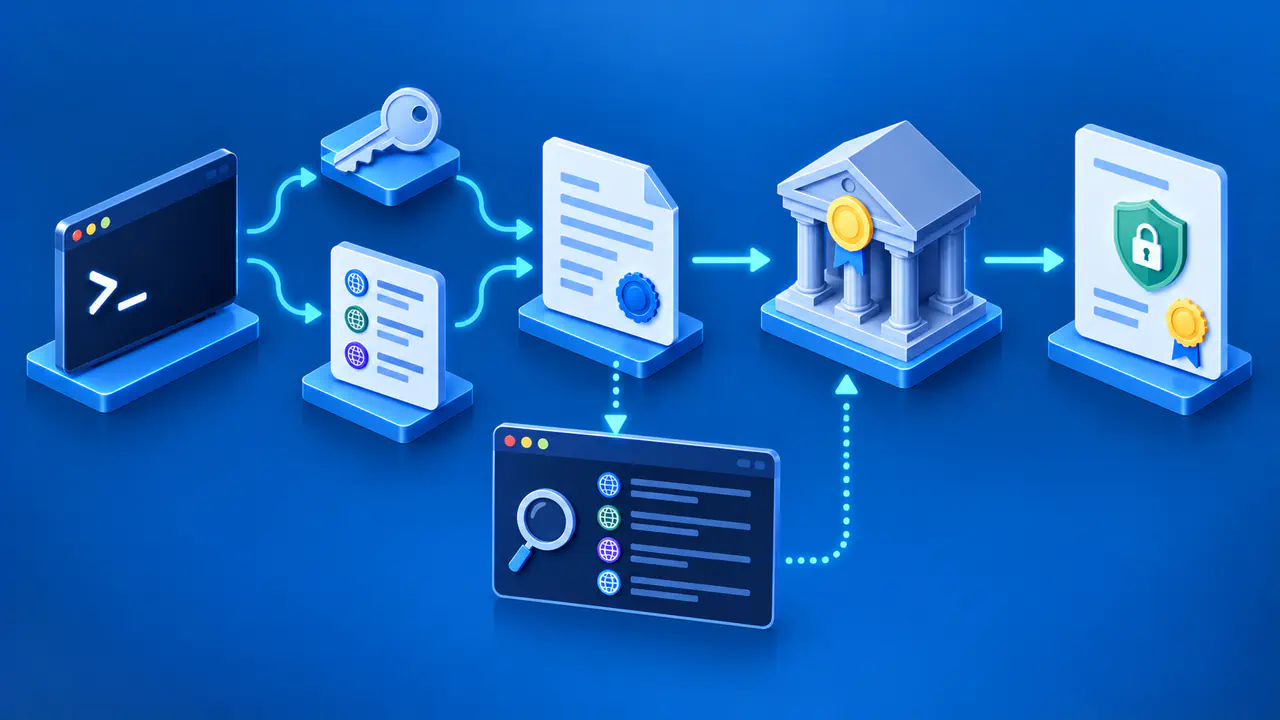
A certificate signing request, or CSR, is a signed request for a certificate. It contains a public key and requested identity information, including the hostnames you want in the certificate. OpenSSL can create a new private key and CSR, or create a CSR from an existing key. The CSR is sent to a certificate authority, or CA, while the private key stays under the operator's control.
Plan the names before running a command. A CSR is not an issued certificate, and a CA may reject a request or issue a certificate with different permitted information after its own checks. Inspect the names and public key in the request before submission.
Plan the SAN Names
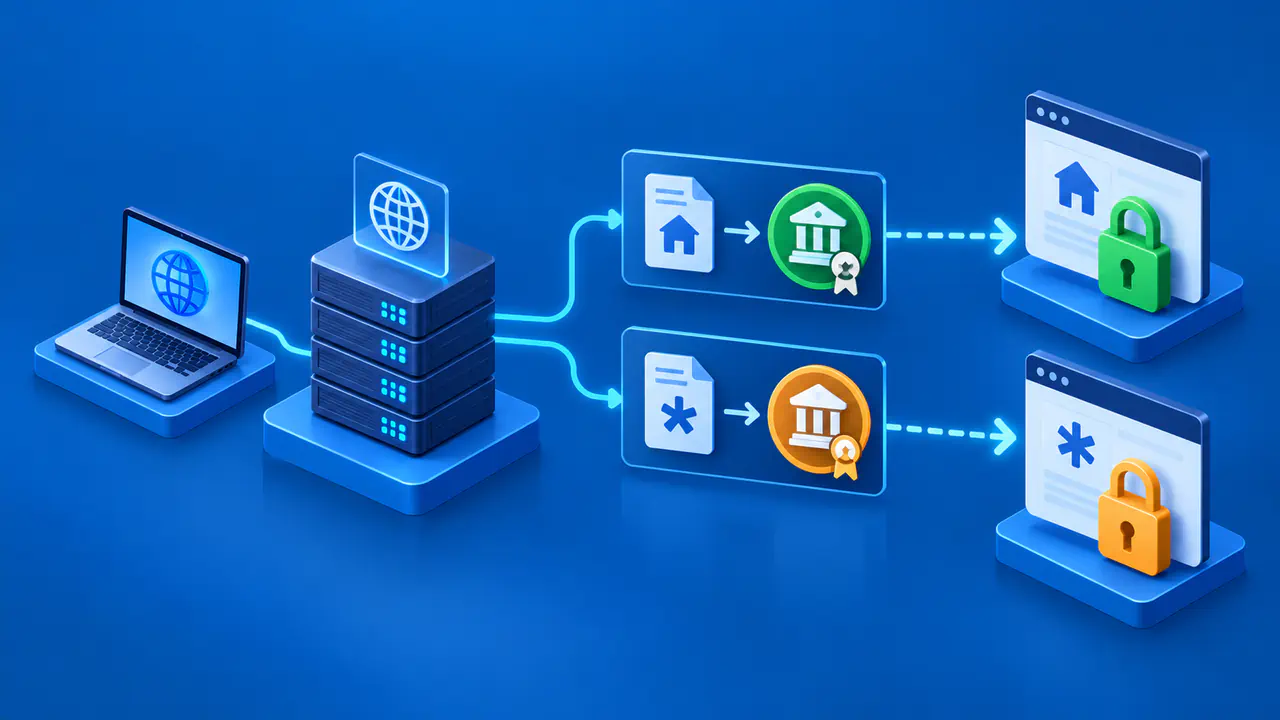
Write down every exact DNS hostname the service must authenticate. For example, example.com and www.example.com are separate identities. A wildcard such as *.example.com has limited matching rules and does not include the parent name. Add only names you are authorized to use and can validate through the chosen CA.
Current TLS clients check DNS identities in the issued certificate's Subject Alternative Name, or SAN, extension, so request that extension in the CSR. The Common Name in a subject is not a replacement for a missing SAN entry. If the intended URL uses a literal IP address, request an IP identity rather than a DNS entry that merely contains the address. Check the CA's policy and the application's requirements for every identifier type.
Decide whether to create a new key or use a protected existing key. A separate key prevents the new service from sharing the same secret with existing services. Reusing a key has operational implications: compromise of that key affects every certificate using it. Choose a key algorithm and size supported by the CA and clients. The examples below use OpenSSL 3.5; confirm the options on the version installed in your own controlled environment.
Generate a Key and Request
For a new key, use a private working directory with access restricted to the operator, and choose output filenames that do not already exist. Check the request configuration before proceeding: encrypt_key = no disables encryption even without a command-line option to do so. This OpenSSL 3.5 command generates a 3072-bit RSA key and a PKCS#10 CSR for example.com and www.example.com:
openssl req -newkey rsa:3072 -keyout site.key -out site.csr -subj "/CN=example.com" -addext "subjectAltName=DNS:example.com,DNS:www.example.com"The -newkey option generates the key, -keyout names the key file, and -out names the CSR file. The -addext value requests the SAN identities. The -subj value supplies the request subject, with example.com as its Common Name in this example.
When encryption is enabled and no output passphrase source is supplied, OpenSSL prompts for a passphrase. Plan how the service will access the key and, if it is encrypted, its passphrase before deployment. Avoid disabling encryption just to suppress a prompt. Unattended key use still needs appropriate file permissions and secret management.
If you are using a protected existing key instead, skip the key-generation command and supply the key with -key. This alternative creates a new CSR without replacing the input key file:
openssl req -new -key site.key -out site.csr -subj "/CN=example.com" -addext "subjectAltName=DNS:example.com,DNS:www.example.com"Use the command that matches your key choice, with the actual service's filenames and SAN names. Supply an existing key's passphrase through a protected method if OpenSSL asks for it. Never paste the private key into a web form, support ticket, chat, or certificate request field.
Inspect the CSR
Before submission, inspect and verify the request using the OpenSSL request command:
openssl req -in site.csr -noout -text -verifyThe text view should show the subject, public-key details, and requested extensions, including every intended SAN entry. The -verify option checks the request's self-signature. It does not mean the CA has validated domain control or issued a trusted certificate. If the request lacks a name or contains an unexpected identity, correct the input and generate a fresh CSR before proceeding.
For the RSA example, compare the public key in the CSR with the public key derived from the protected key:
openssl req -in site.csr -pubkey -noout
openssl pkey -in site.key -pubout
The PUBLIC KEY blocks should match. These commands print only public key data and leave the private-key file unchanged. If the blocks differ, check which key and request you selected before proceeding.
Store the request, key location, creation date, algorithm, and intended hostnames in an internal operations record. This helps avoid installing a certificate with an unrelated key later. Do not copy the private key into the record.
Submit Only the CSR
Give the CSR to the chosen CA through its approved process. The CA may require proof of domain control, organizational information, or another validation step depending on the certificate type. Creating a CSR does not perform those checks. The CA may also impose rules on acceptable SANs, algorithms, or key sizes.
Read the issuer's instructions for the exact product. Some automated certificate clients generate keys and requests internally, so a manually created CSR may not be the expected input. If the CA requires a different request format or additional fields, revise the request to meet those requirements before submitting it.
After issuance, inspect the actual certificate separately. Confirm that its SAN entries cover the intended hostnames, its validity dates are appropriate, and its trust chain can be presented by the service. A CSR containing a requested name is not proof the CA placed that name in the final certificate. Test the certificate at the endpoint that visitors actually reach.
Protect the Private Key
The matching private key is required for the service to authenticate with the issued certificate. Keep it accessible only to the service and administrators who need it. Apply appropriate file permissions and backup protection for the operating system, and avoid storing it in a public web directory or source repository. If the key is encrypted, protect its passphrase separately and plan service restart procedures.
Do not email the key to the CA. If a hosting provider needs to terminate TLS on your behalf, use its documented secure key-management process and understand which systems will have access to the key before transferring it. Where possible, let the provider create and protect its own key rather than exporting yours.
If a key is exposed, report the compromise to the issuer, request revocation where supported, and replace the affected certificates using a new key. Some short-lived certificates do not support revocation. Generating a new CSR cannot make the exposed key safe. Preserve the internal record needed to identify the services that use that key.
If you lose access to a private key, recover it only from a trusted, protected backup or obtain a replacement certificate for a new key. A CSR cannot restore the private key.