DV vs OV vs EV Certificates Explained
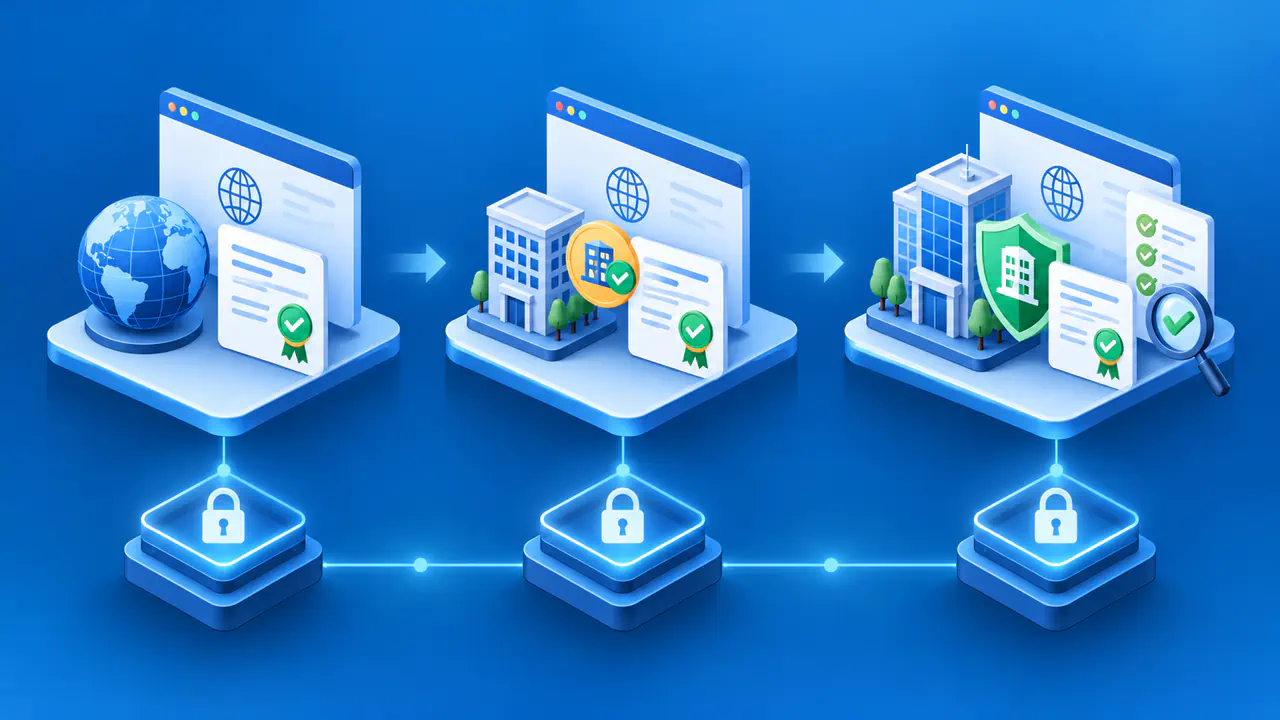
DV, OV, and EV describe different checks a certificate authority (CA) performs before issuing a publicly trusted TLS certificate. Domain Validation, or DV, establishes control of a domain name. Organization Validation, or OV, adds checks of the organization named in the certificate. Extended Validation, or EV, applies a more detailed organizational vetting process under its own guidelines.
These labels describe issuance and identity information, not a universal hierarchy of encryption strength. A browser and server negotiate TLS protocol and cryptographic settings separately from whether the certificate is DV, OV, or EV. The certificate type alone does not prove a website is honest or that a transaction is safe.
What Domain Validation Checks
For a DV certificate, the applicant demonstrates control of the domain or hostname to the issuing CA through an approved validation method. The CA also follows the applicable certificate requirements for issuance. The central point is that DV does not assert that a particular legal organization has been vetted as the operator of the site.
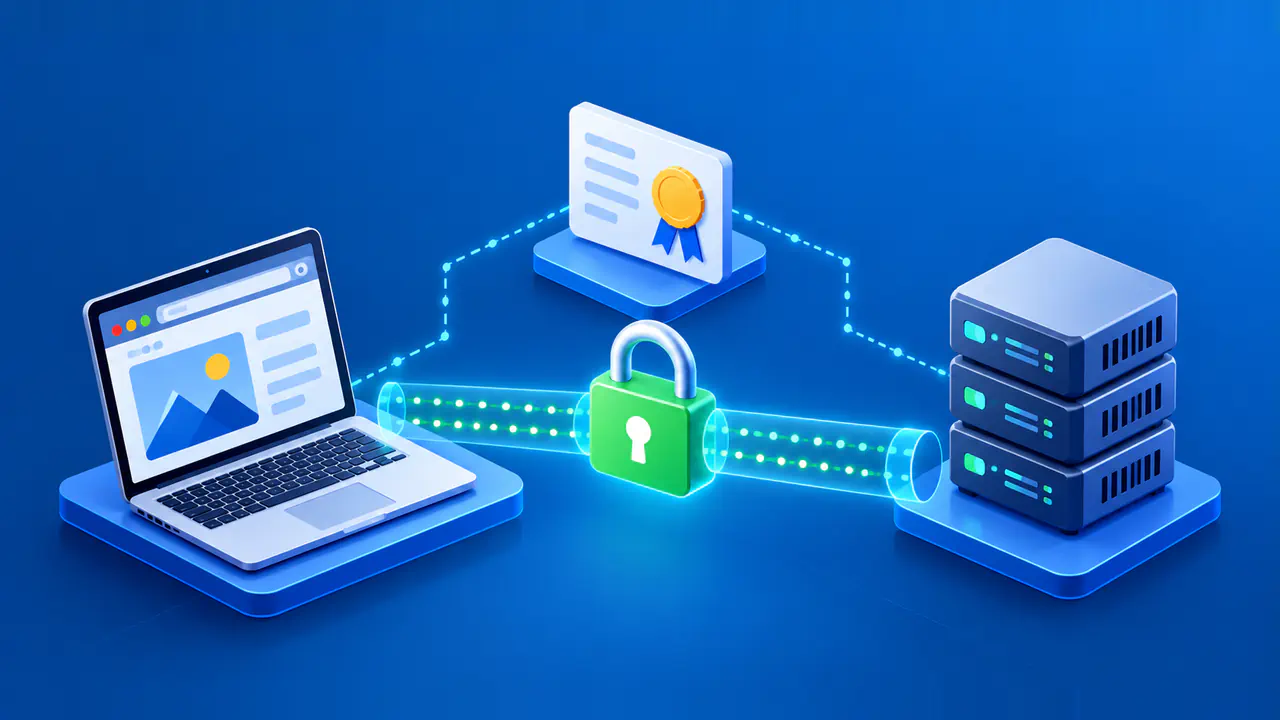
A DV certificate can still be valid and useful for HTTPS. It binds a public key to the validated name, allowing a client to check the name and certificate chain during a secure connection. It supports encrypted transport when TLS is configured correctly. A legitimate personal site, documentation service, or business site can use DV; the absence of organization details is not evidence that the site is malicious.
Domain control is narrower than trustworthiness. A party can control a confusingly similar name or create a site that presents misleading content. DV validation does not evaluate a site's products, refund practices, or claims. Visitors should consider the exact URL and other context when deciding whether to trust a service.
What Organization Validation Adds
An OV certificate adds a verified organization identity to the domain-control check. The CA checks the organization's name and address and confirms that the address is where the applicant exists or operates. Evidence can include government records, a reliable database, a site visit, or supported attestation documents. A physical visit is one possible method, not a requirement for every OV application. The CA also authenticates the certificate request from the organization's representative.
This can help an administrator or investigator link a certificate to a named organization. The information is recorded in the certificate's subject fields, so it can be checked separately from the website's own description of the business. An organization name in a server certificate does not grant its staff access to the server or application, and it is not a list of the people authorized to manage the site.
OV may be useful when an organization has a reason to place its validated name in the certificate for administrative, contractual, or policy purposes. It is not a prerequisite for ordinary TLS encryption. Before choosing OV, a site operator should weigh the need for verified organization details against the work involved in obtaining and renewing the certificate.
What Extended Validation Adds
EV requires more detailed evidence about organizational identity. The CA verifies legal existence and identity, physical address, and operational existence, as well as control of the requested domain names. It also checks the names, roles, and authority of those signing the subscriber agreement and approving the request. For a registered company, that includes checking its registration and whether it is currently recognized as active under the relevant rules.
EV does not mean that a website uses stronger encryption than a DV site. During a TLS 1.3 connection, the server selects a supported cipher suite from the client's offered list, and the connection uses symmetric keys to protect application data. The certificate's public key serves authentication rather than selecting that cipher suite. A DV site and an EV site can therefore negotiate the same encryption algorithm. The validation label alone does not change the server's TLS configuration or turn a weak configuration into a secure one.
An EV certificate also does not substitute for application security. The site still needs safe code, access control, updates, and incident response. A certificate can be technically valid while a vulnerable site exposes data through its application.
What Browsers Show
Browser interface details change over time and differ by product and device. A secure connection indicator primarily describes the connection state. It may not display an organization's name in the address bar even when an OV or EV certificate contains organization details. Some clients make those fields available in a certificate or site information view.
Firefox, for example, moved EV organization information out of its main URL bar into a site information panel in Firefox 70. Older screenshots may therefore show identity information that the current browser no longer displays in the address bar. Check the current browser's certificate details if organizational identity matters, and verify that the name shown matches the entity you intended to check.
Limits of Certificate Identity
All three certificate types depend on a valid trust path, current validity dates, appropriate name coverage, and possession of the corresponding private key by the service. Browser trust decisions also depend on current platform policy. The validation label does not override an expired certificate, wrong hostname, or broken chain.
Issuance checks happen at a point in time. Organizations can change, domains can move, and keys can be compromised. Renewal and certificate lifecycle practices matter regardless of DV, OV, or EV. An organization with contractual identity requirements should check the CA's current policies and confirm that the certificate includes the required identity details.