What Is an SSL Certificate?
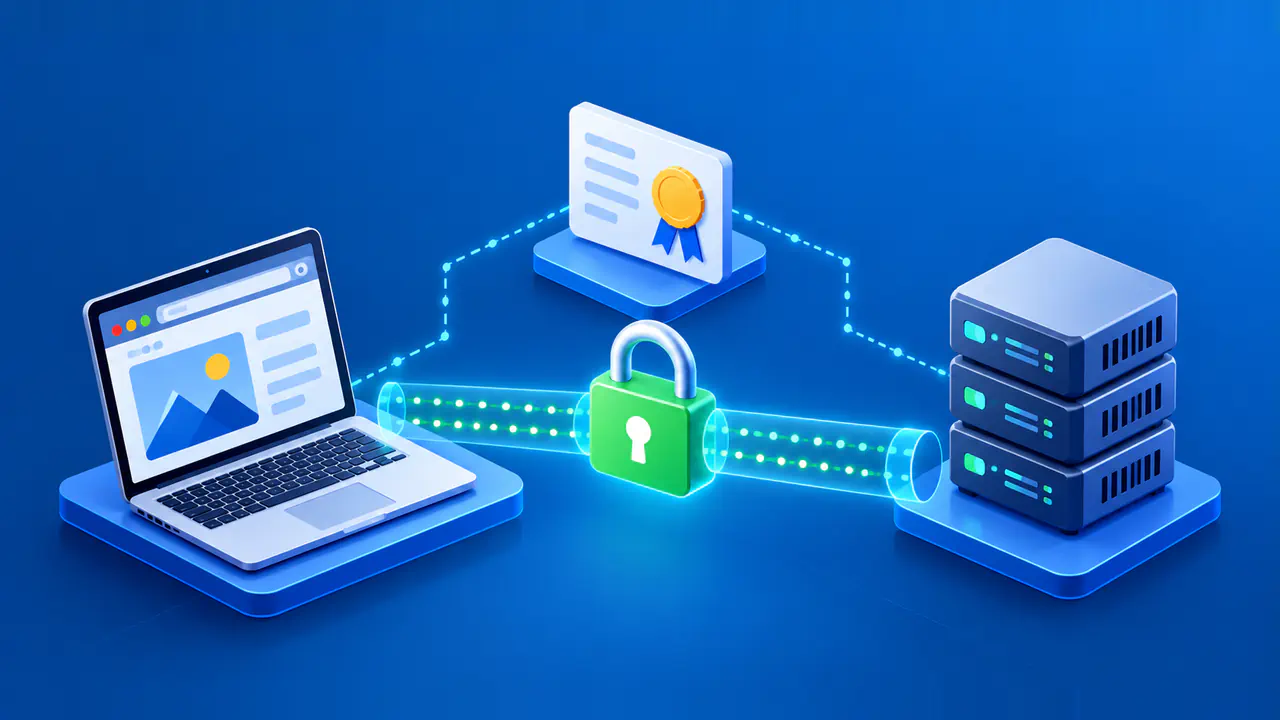
An SSL certificate is a digital certificate that associates a public key with an identity, commonly a website hostname. Despite the familiar name, modern HTTPS uses Transport Layer Security, or TLS, rather than the obsolete SSL protocol. The certificate helps a browser authenticate the server for the hostname it requested.
A website owner usually obtains this certificate from a certificate authority, an organization that issues signed certificates after checking the request. Hosting services may manage issuance and installation for the owner. The browser's acceptance still depends on the certificate presented and its own trust settings.
What the Certificate Identifies
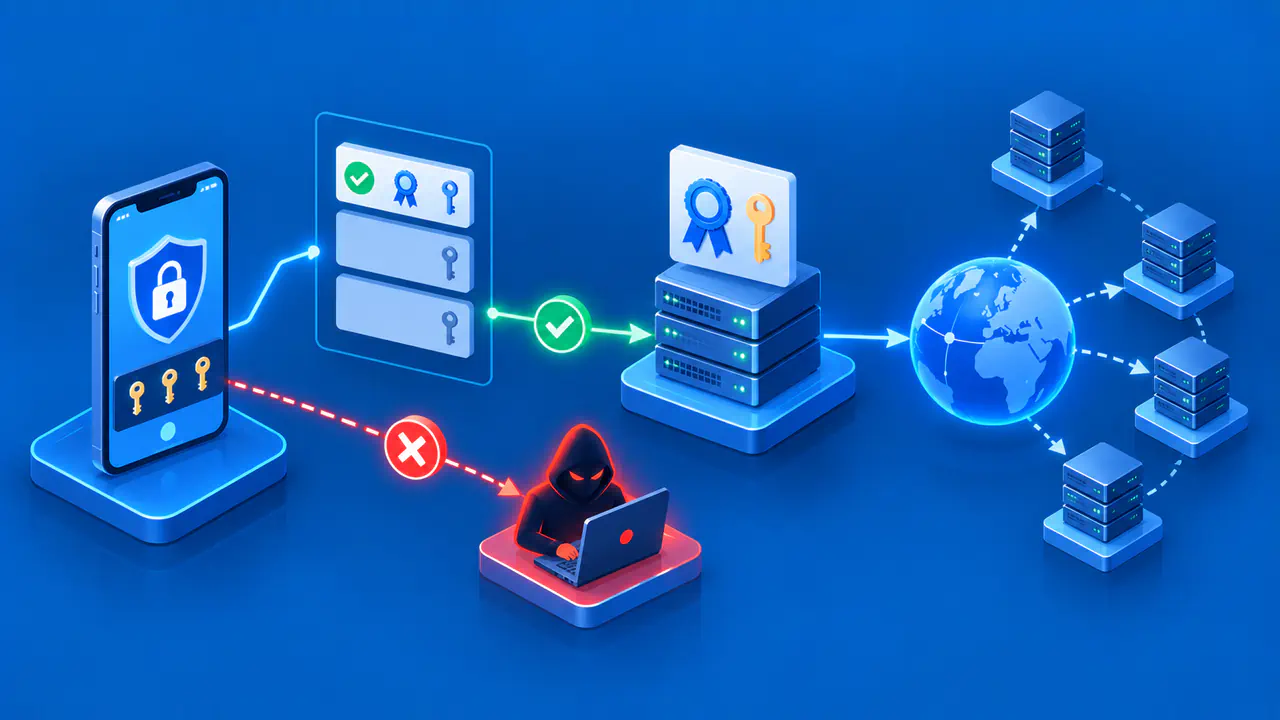
A website certificate includes a public key, one or more names it covers, validity dates, issuer information, and the issuer's digital signature. The matching private key is held separately by the server or service operating the site. The browser can receive the public certificate; the private key must remain protected.
If a browser requests shop.example.com, the certificate must be valid for that hostname under the applicable matching rules. A certificate for a different name does not authenticate the requested site simply because it belongs to the same company. Certificates can list several names in their Subject Alternative Name field, so the requested hostname must match an entry there.
The certificate does not normally list the web pages a site serves or identify every person who runs it. A common domain-validated certificate demonstrates that the requester met the certificate authority's domain-control checks. For example, the requester may prove control by placing a specified record in the domain's DNS or a file at a designated website path.
How the Public Key Supports HTTPS
In a full certificate-based TLS handshake, the server presents its certificate and proves that it controls the matching private key. In TLS 1.3, it signs data from the handshake, and the browser verifies that signature using the public key in the certificate. Copying a site's public certificate alone therefore does not let another server authenticate as that site.
The browser and server also agree on cryptographic settings and establish the keys used to protect the session. Modern TLS does not simply encrypt every page byte directly with the certificate's public key; it uses the authenticated handshake to establish efficient symmetric encryption for the actual traffic. The issuer's signature on the certificate and the server's proof during the handshake serve different purposes: the first certifies the name-to-key association, while the second demonstrates possession of the matching private key.
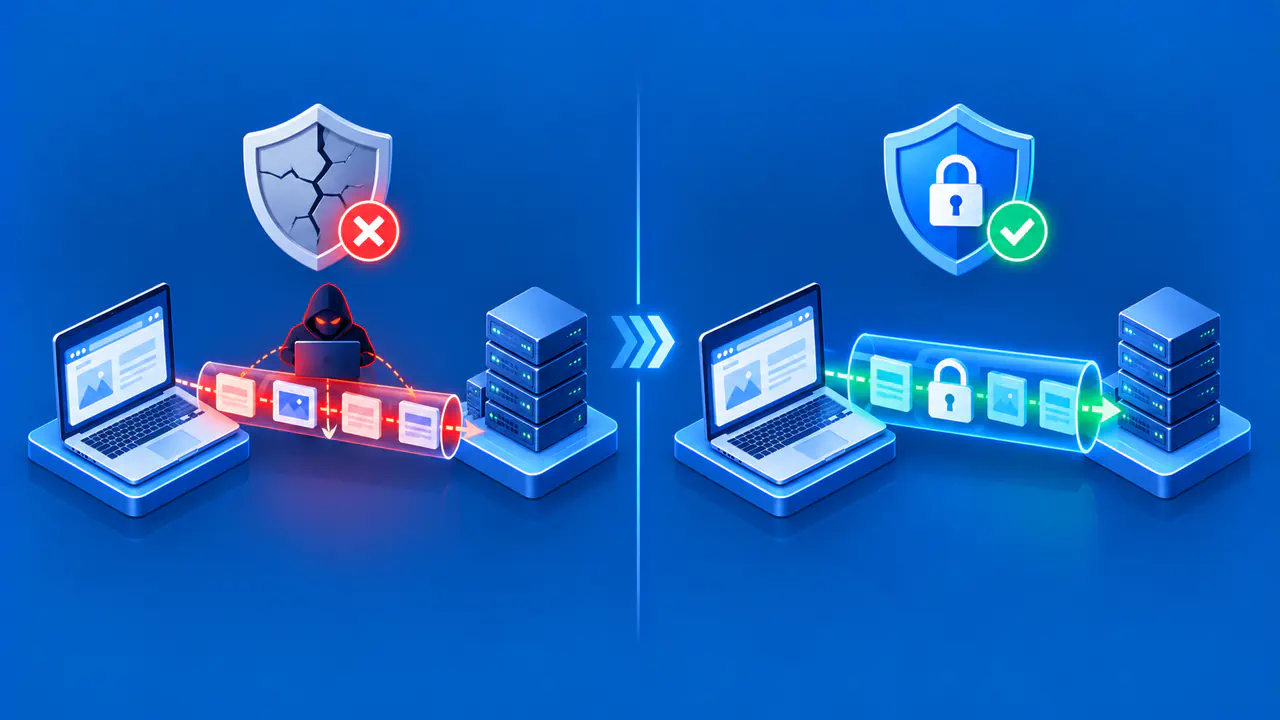
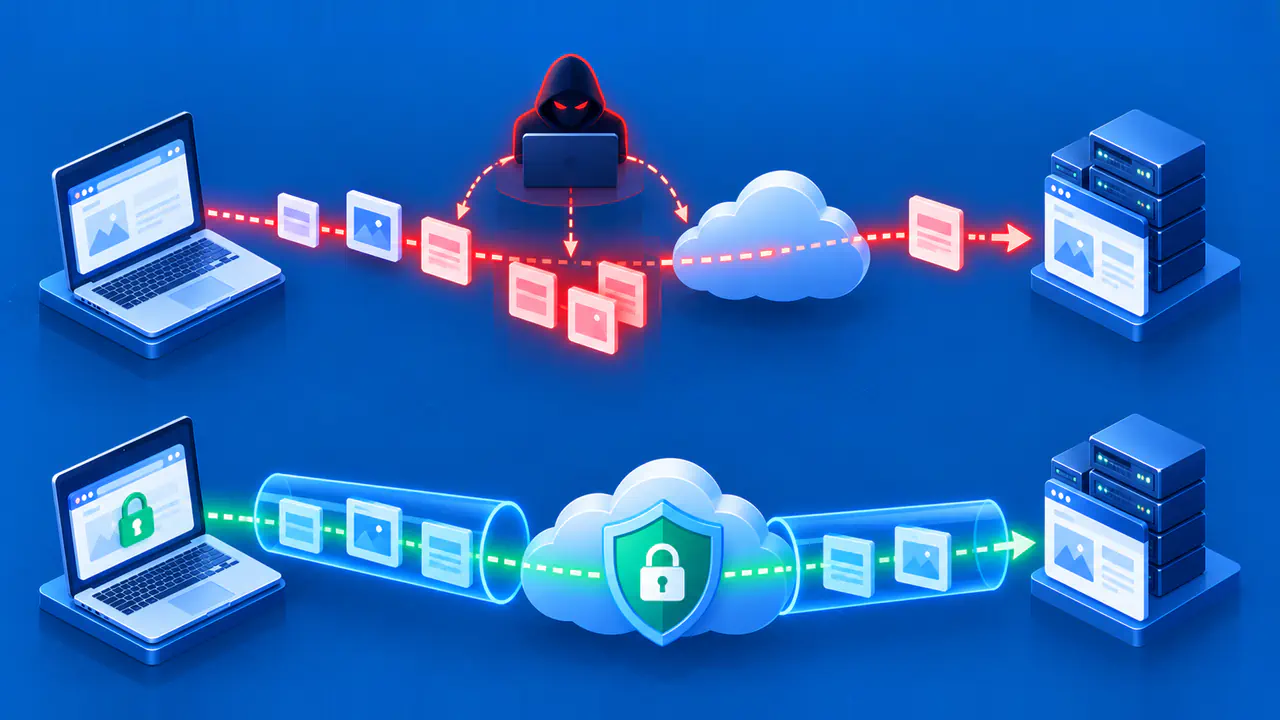
That protected connection gives confidentiality and integrity in transit: other parties on the network should not be able to read or silently alter the exchanged content when TLS is working as intended. It does not encrypt files already stored on the server. The protection applies to the traffic between the endpoints participating in that TLS connection.
How the Trust Chain Works
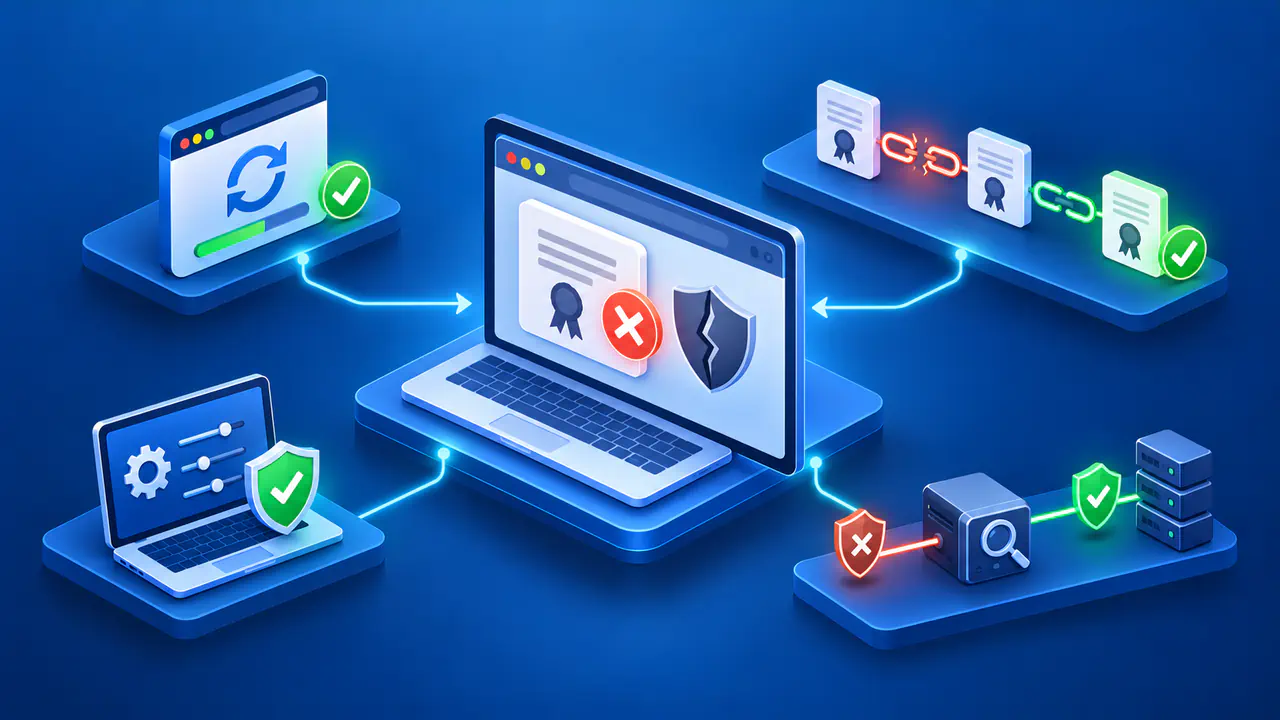
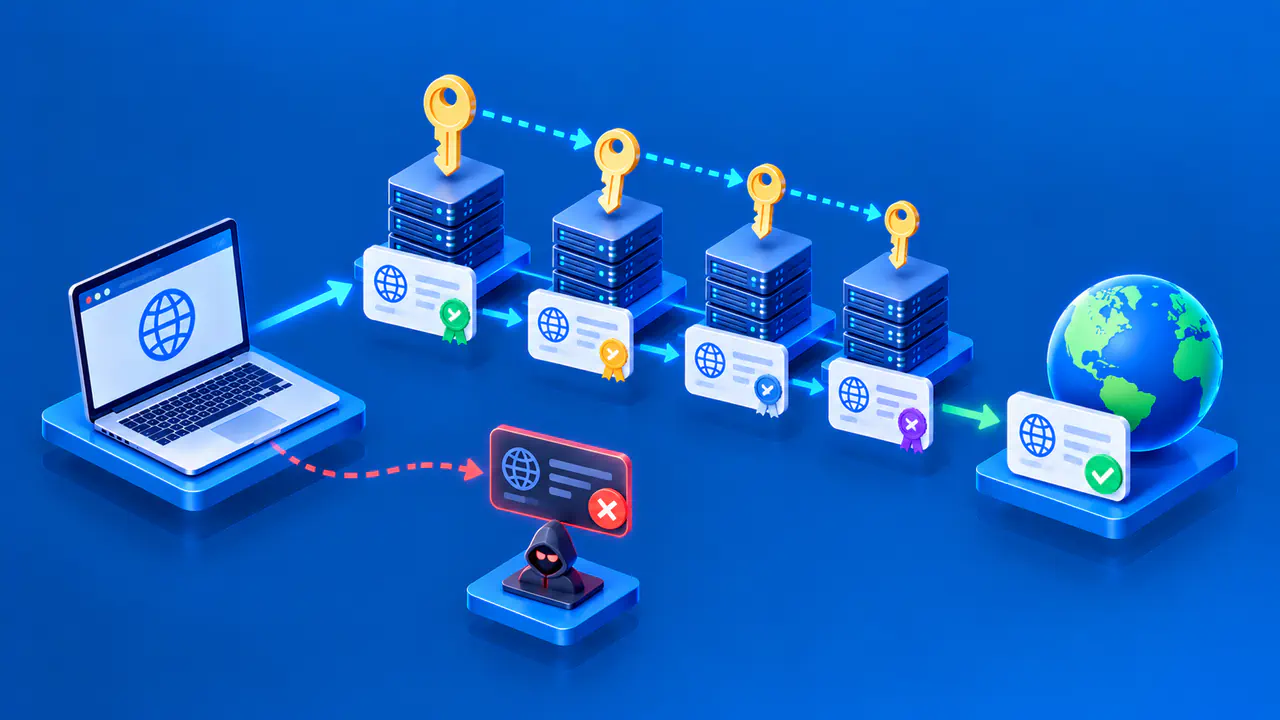
Most browsers and operating systems have a set of trusted root certificate authorities. A website's certificate is commonly signed by an intermediate authority, which is in turn linked to a trusted root. The browser builds and validates this chain, checks the requested hostname and the certificate's validity period, and applies its security policy. If the needed chain is incomplete or no acceptable trusted root is found, the browser may reject the connection or show a warning.
The root authority does not need to issue every website certificate directly. Intermediate authorities sign website certificates with their own private keys, allowing the root's private key to stay offline. A server typically presents its own certificate and the needed intermediate certificates. Trusted roots come from the browser's trust settings or the operating system's trust store; a root does not become trusted merely because the server sends it.
A self-signed certificate has a signature made with its own matching private key rather than a separate issuer's key. It can support an encrypted TLS session, but browsers do not normally trust a website's self-signed certificate by default. A controlled internal service can use one when its clients are explicitly configured to trust it. That local trust does not make the certificate publicly trusted.
Why the Name “SSL Certificate” Remains
SSL, short for Secure Sockets Layer, was an earlier protocol for protected connections. TLS replaced it and is the protocol used for modern HTTPS. The phrase “SSL certificate” remains common in hosting dashboards and everyday writing, but the certificate used by a current HTTPS site is more accurately called a TLS certificate or server certificate. Buying or enabling a product labeled SSL should not be taken as an instruction to enable obsolete SSL protocol versions.
Proxy and Origin Certificates
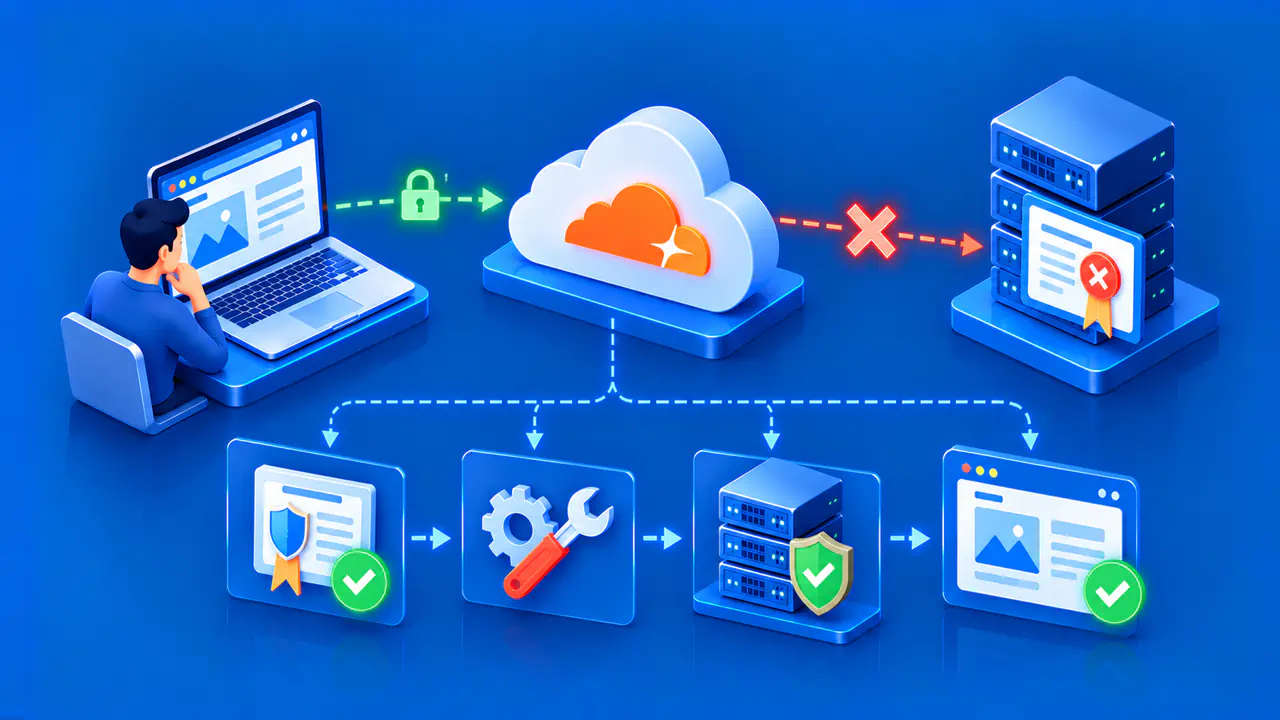
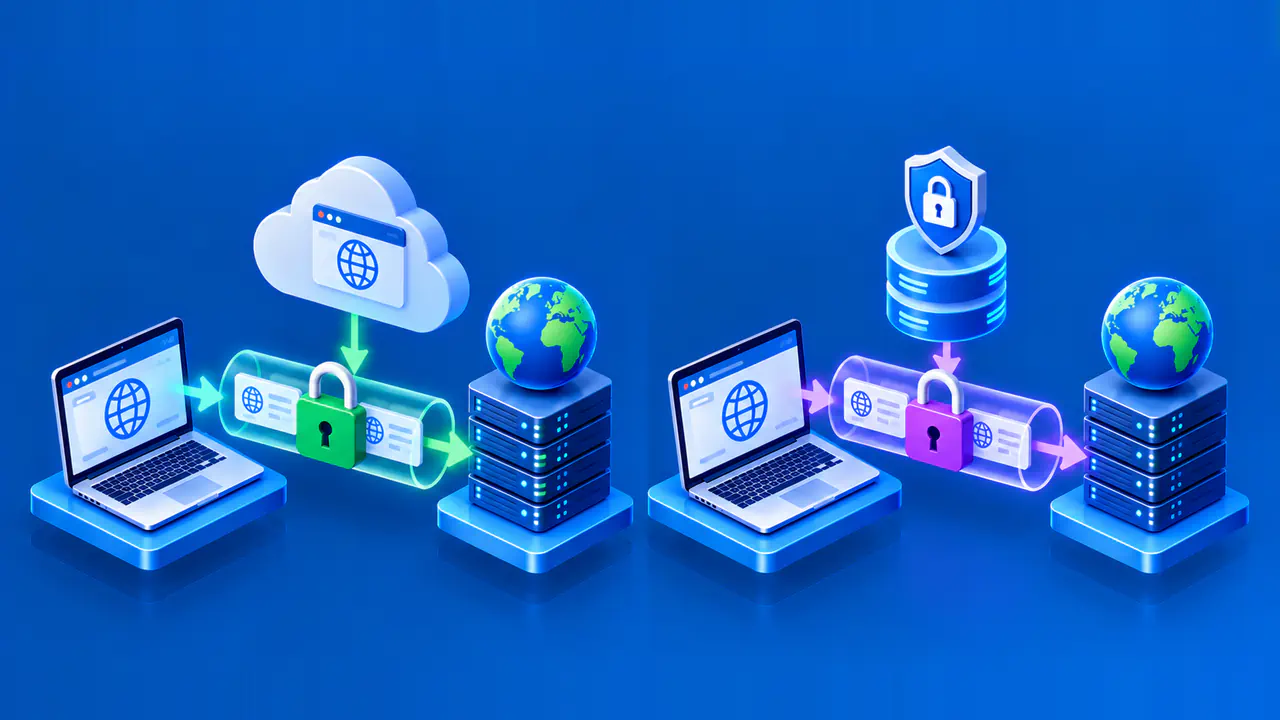
If a content delivery network or reverse proxy handles HTTPS for a website, the browser connects to that service instead of directly to the origin server. The origin may present a different certificate when the proxy connects to it over HTTPS. The browser validates the certificate presented by the proxy; that check does not establish whether the proxy's connection to the origin is secure.
What a Valid Certificate Does Not Prove
A browser accepting a certificate does not establish that the website operator is honest, the content is accurate, or downloaded files are harmless. If someone is tricked into visiting a lookalike hostname, a certificate for that name can still pass validation. Check the actual hostname before entering account details, even when the browser reports a secure connection.
The website operator must also protect the private key, configure TLS appropriately, maintain the application, and control access to stored information. A page can arrive intact over HTTPS while an application flaw exposes data after the server receives it. Certificate validation does not check those application permissions or how the operator handles submitted information.