How Server Name Indication Works
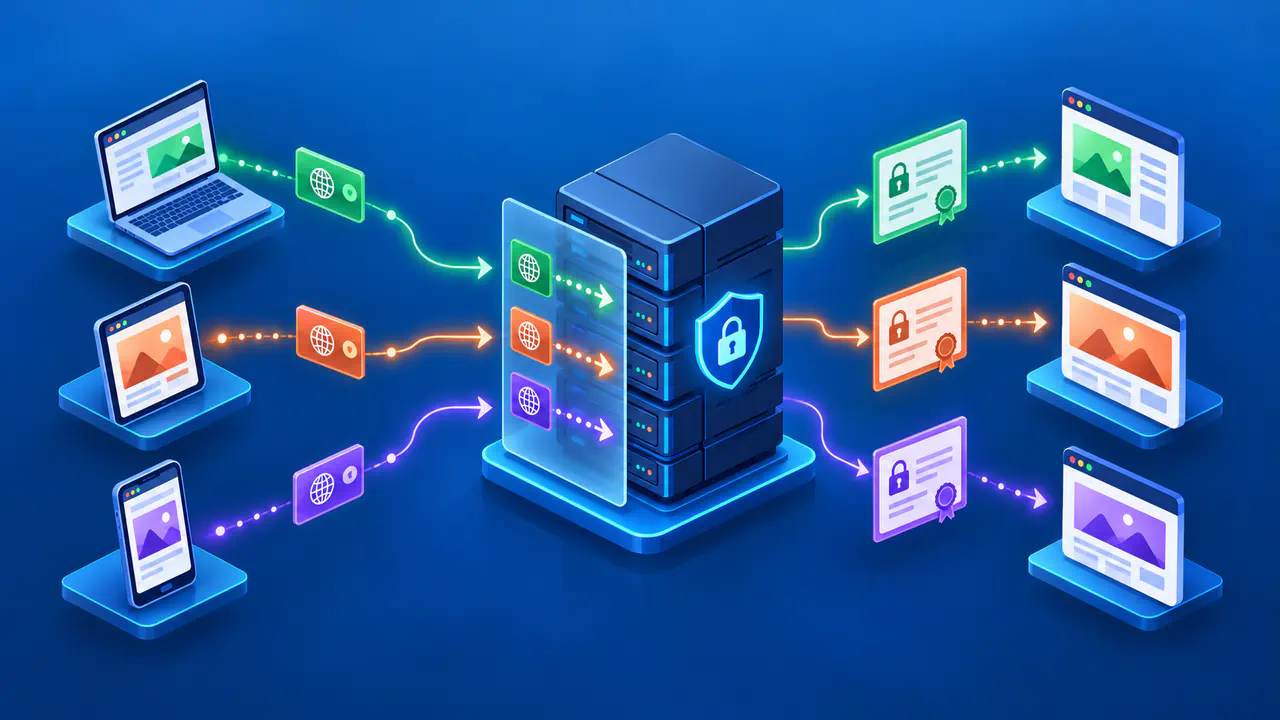
Server Name Indication, or SNI, is a TLS extension that lets a client state which DNS hostname it wants to reach during connection setup. A server hosting several HTTPS names on one network address can use that early name to choose a suitable certificate. This happens before the ordinary HTTP request is processed.
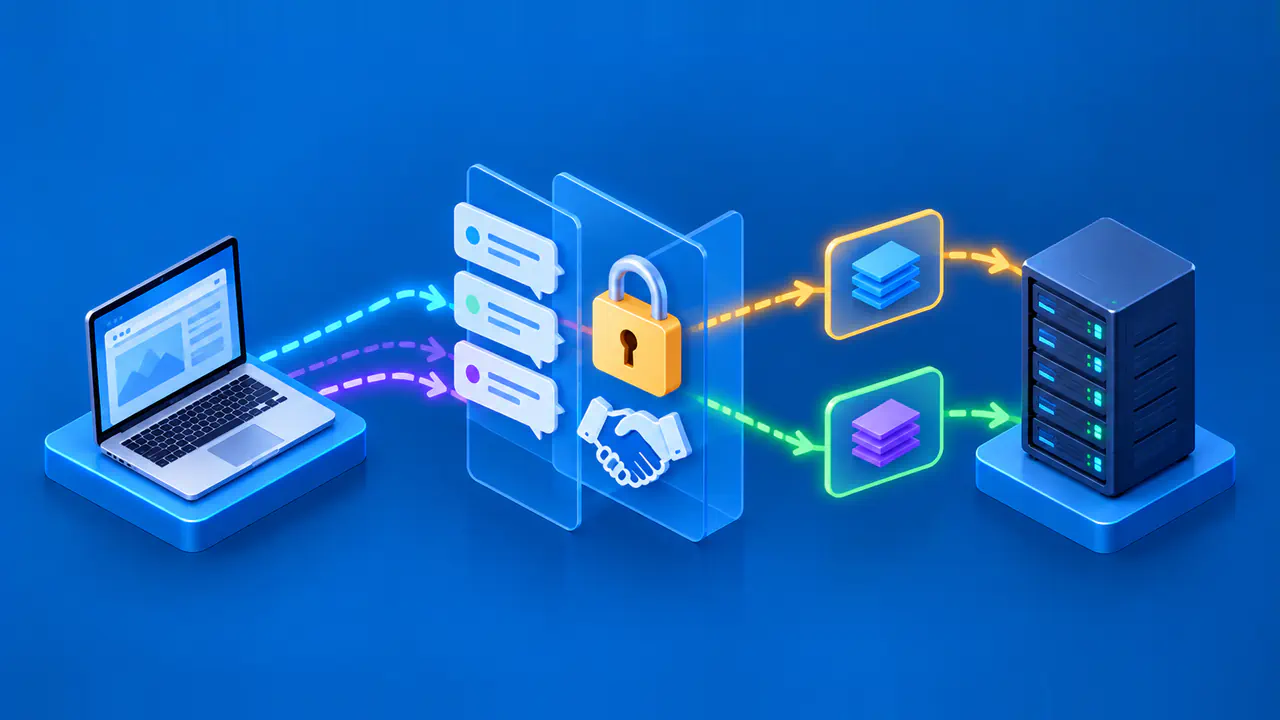
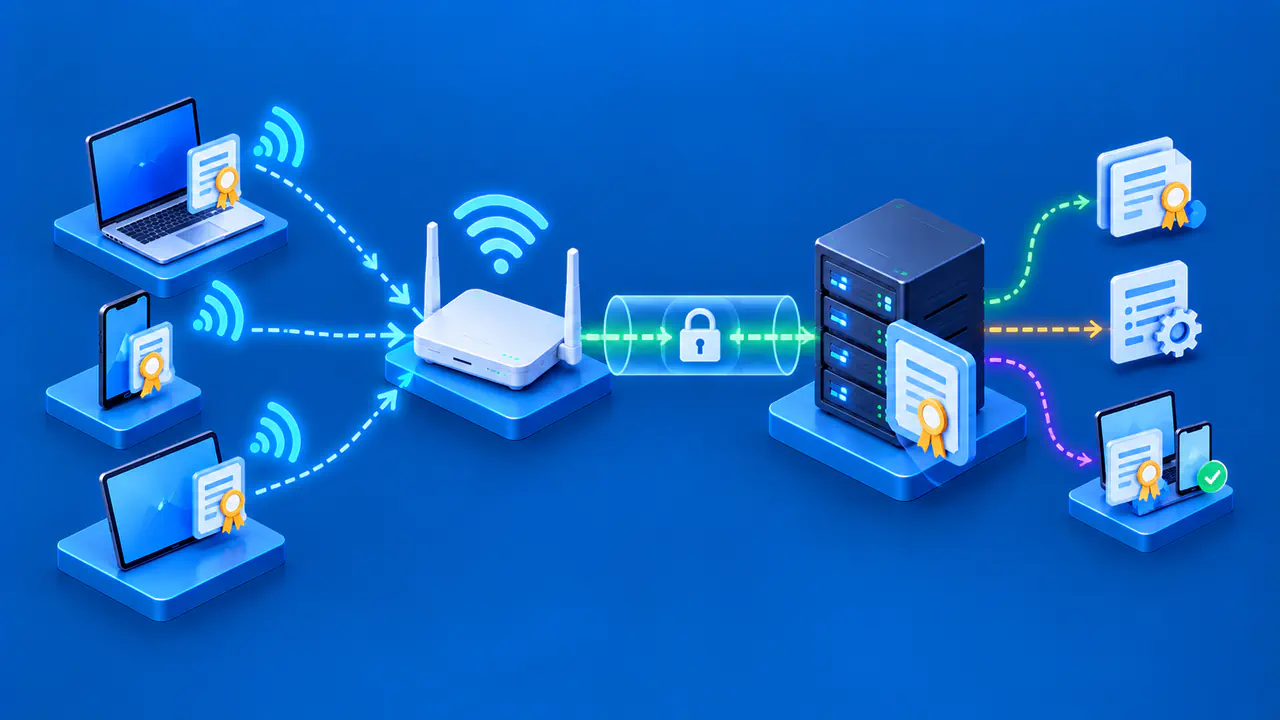
On a new HTTPS connection authenticated with a certificate, the server presents that certificate during the TLS handshake, before it receives the ordinary HTTP request. SNI supplies the hostname at this earlier stage. It is separate from the HTTP Host header and does not, by itself, make a certificate valid for a name.
One Address, Several HTTPS Names
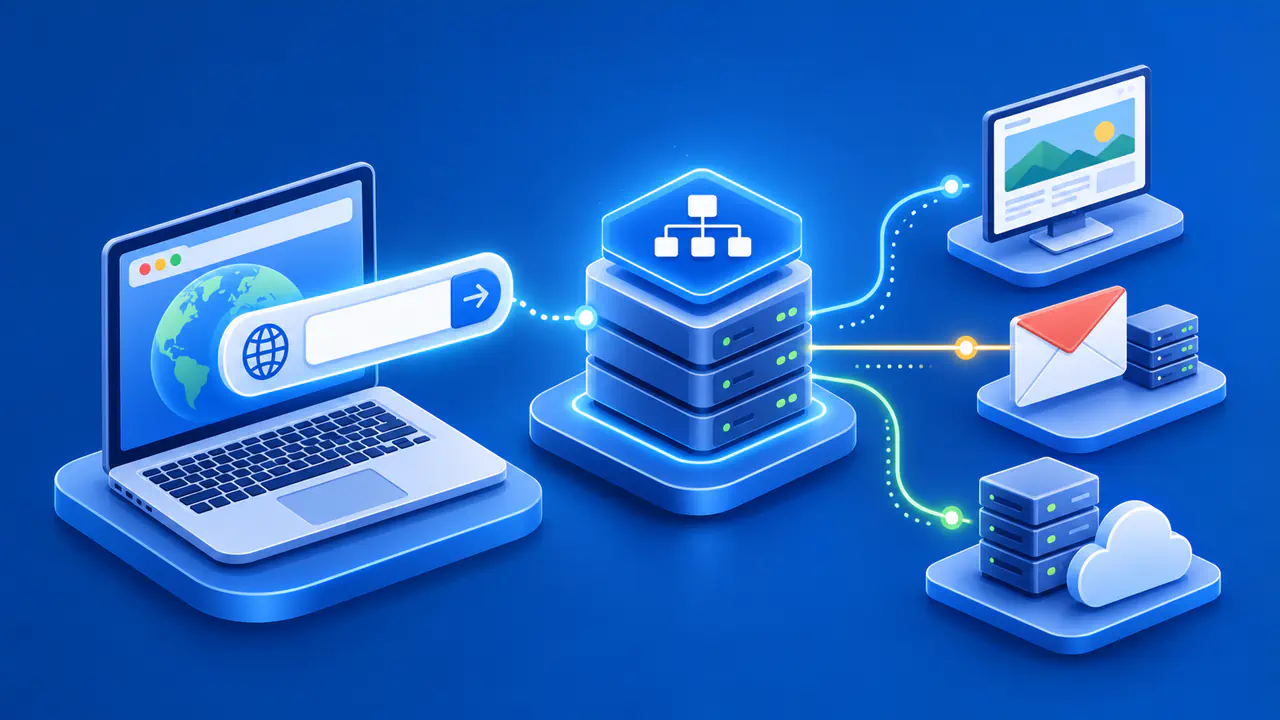
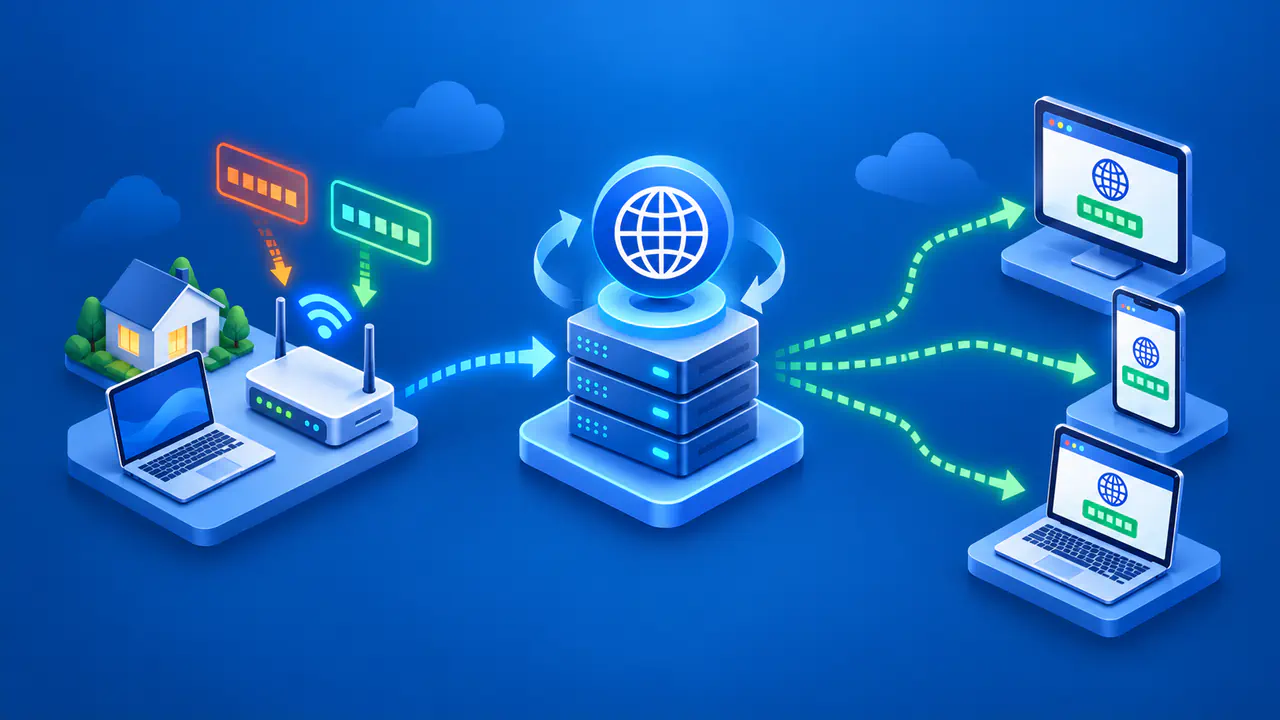
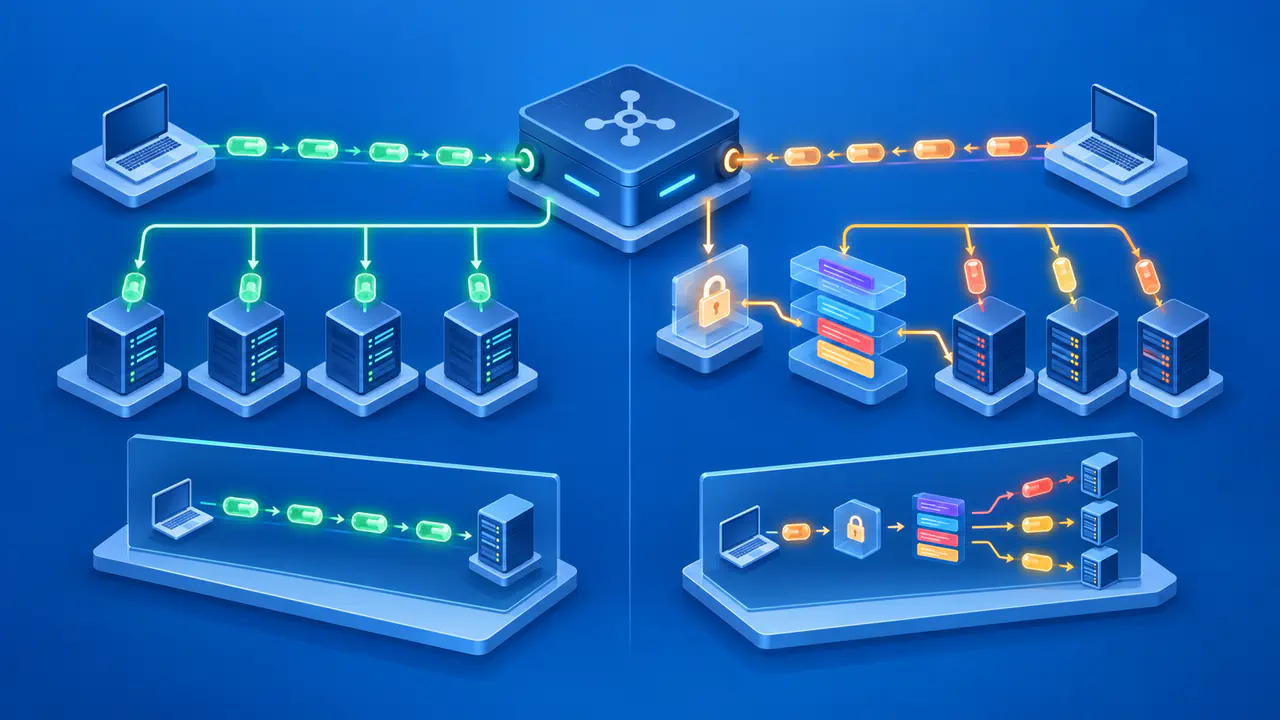
Name-based web hosting allows several domains to share an IP address. For unencrypted HTTP, a server can read the request hostname and select the intended site. A full certificate-based HTTPS handshake establishes the secure connection before ordinary HTTP routing. Without an early indication of the intended name, a shared endpoint may have to offer a default certificate before it knows which site's HTTP request will arrive.
Suppose shop.example.com and docs.example.com point to the same HTTPS endpoint. They may use separate certificates, or a certificate covering both names. The endpoint needs to choose an appropriate certificate for the connection. SNI allows the client to include the requested DNS hostname while negotiating TLS, so the server can make that choice.
This does not mean every shared site needs a distinct certificate. A certificate can cover multiple names if issued and configured accordingly. SNI is most important when one endpoint has different certificate choices for different names. The server still needs a certificate whose listed names and trust chain satisfy the client's checks.
The Hostname in ClientHello
A TLS client begins the handshake with a ClientHello message. The SNI server_name extension can contain the intended hostname. The value is a DNS hostname, not a URL path, and the defined hostname form does not permit a literal IPv4 or IPv6 address. The client sends it because it knows the host named in the connection request.
The server can use the indicated name to select a certificate and apply appropriate security policy. The client then checks the certificate against the hostname it intended to contact. SNI does not replace that verification. A server can also reject an unrecognized name or continue with a configured fallback, depending on policy and implementation.
The usual HTTPS sequence completes TLS setup before the HTTP request supplies its hostname and path. A resumed TLS 1.3 connection can instead send early application data and omit a new certificate exchange. The TLS SNI name and the HTTP host remain separate fields, even when both identify the same site. Server operators should avoid treating either field as proof that the other is trustworthy.
Certificate Selection and Errors
If the endpoint recognizes the SNI name and has a suitable certificate, it can present that certificate during the handshake. The client validates its trust chain and name coverage before treating the connection as secure. A valid certificate for docs.example.com cannot simply be used for shop.example.com unless its names cover the latter too.
A certificate mismatch can occur even when DNS directs the client to the intended server. The server may not have a matching certificate, may choose the wrong default, or may be behind a proxy where TLS terminates earlier than expected. Inspect the certificate presented for the exact hostname and endpoint rather than assuming a web virtual host rule controls it.
After TLS succeeds, HTTP routing can still be wrong. The server might present a correct certificate yet return content from a default virtual host. That separates two checks: certificate selection in the handshake and site selection for the HTTP request. An operator needs both configured for the name visitors use.
No-SNI and Default Behavior
If a client omits SNI, the endpoint has no requested DNS hostname from that extension at certificate selection time. It may present a default certificate or reject the handshake, depending on its configuration and protocol policy. Some older or specialized clients may behave differently from current browsers. A connection made to a literal IP address should not be assumed to send that address as valid SNI.
Default behavior matters on shared endpoints. A server can have a default HTTPS site and certificate for an address and port. That certificate may not cover an arbitrary hostname that happens to resolve there. A browser warning in this situation does not prove the requested site's content is missing; the secure connection may have failed before any HTTP request reached it.
For troubleshooting, compare the requested DNS hostname, resolved endpoint, SNI sent by the client where observable, and certificate actually presented. Then check HTTP routing only after certificate validation succeeds. This sequence keeps a TLS name problem from being confused with a missing web page or DNS record.
What SNI Reveals
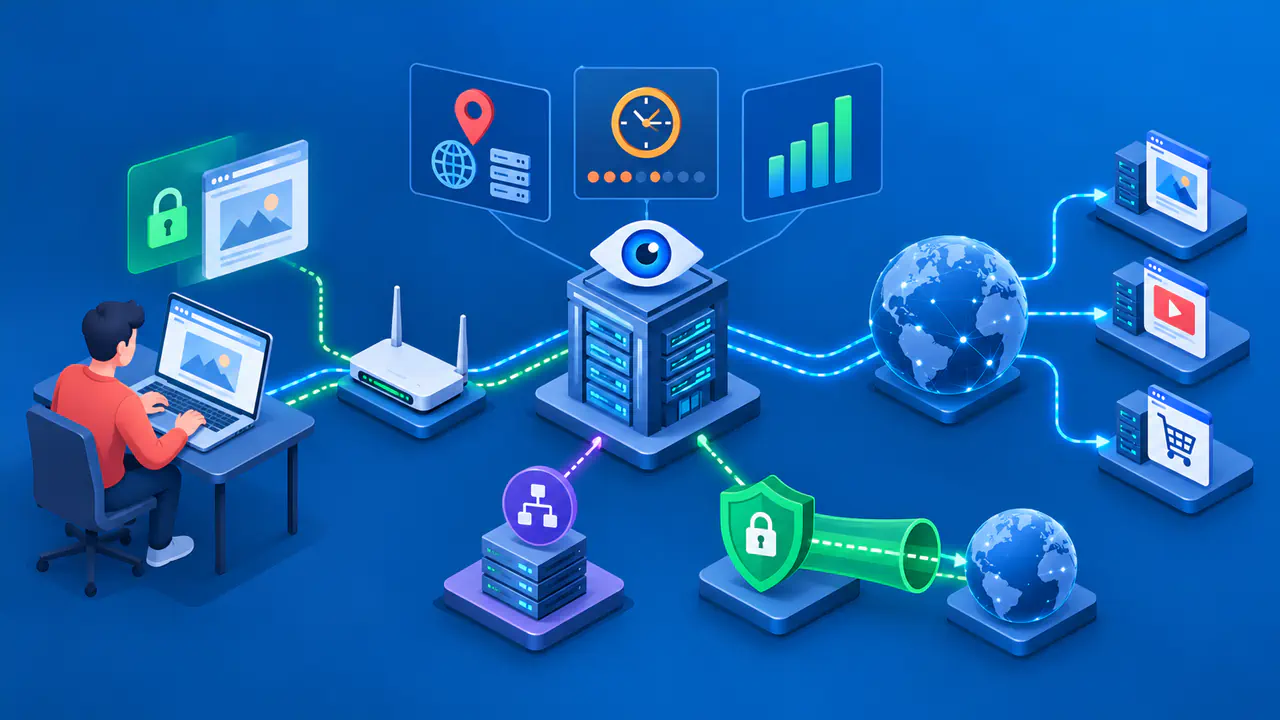
Ordinary SNI is sent in the initial handshake so the server can read it before selecting a certificate. That timing has a privacy consequence: the hostname may be visible to observers of the connection even though later application data is encrypted. TLS 1.3 encrypts substantial portions of the handshake and application traffic, but using TLS 1.3 alone does not make the initial SNI hostname private.
Encrypted Client Hello, or ECH, can protect the intended server name when the client and server successfully negotiate it. That is an additional mechanism, not a property of ordinary SNI or TLS 1.3 alone. It does not hide the destination IP address, and unencrypted DNS queries can still expose a lookup name.
If an observer sees shop.example.com in ordinary SNI, that identifies a hostname rather than a page such as /cart or /checkout. Those paths and the rest of the HTTP message are carried inside encrypted HTTPS application traffic. Seeing an SNI name also does not prove that TLS completed or that an HTTP request was sent.