How IPv6 Prefix Delegation Works
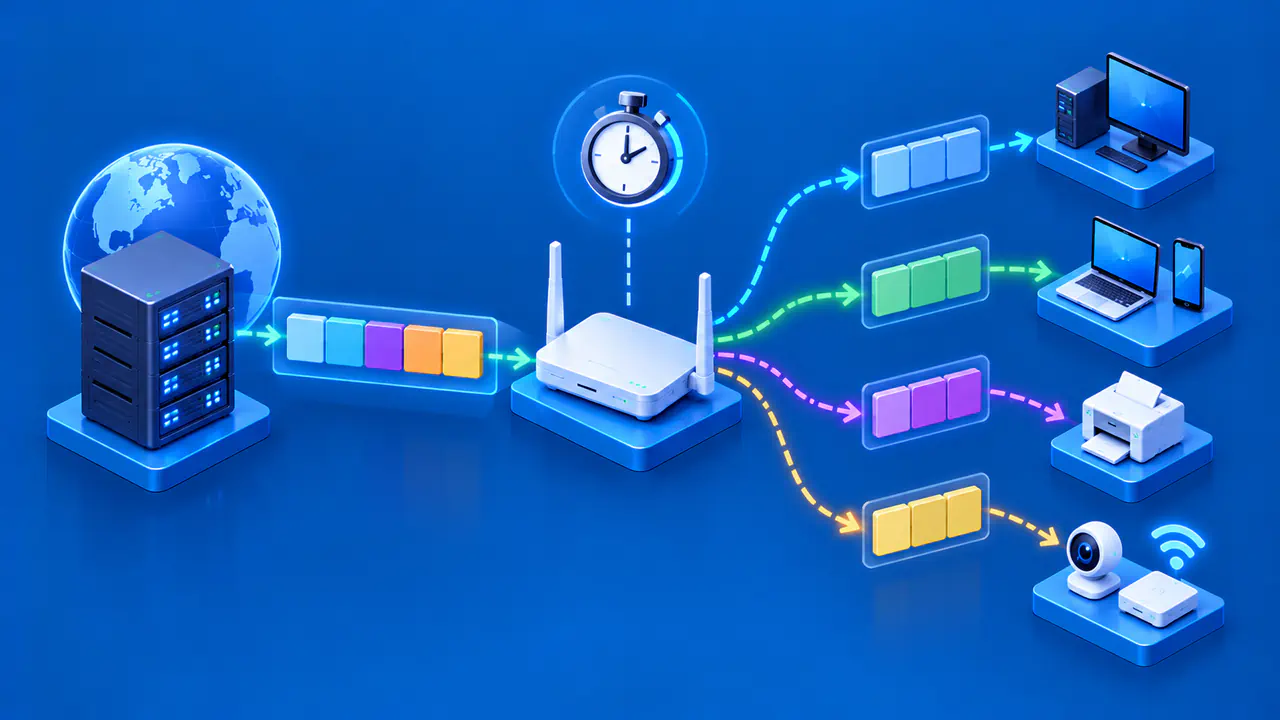
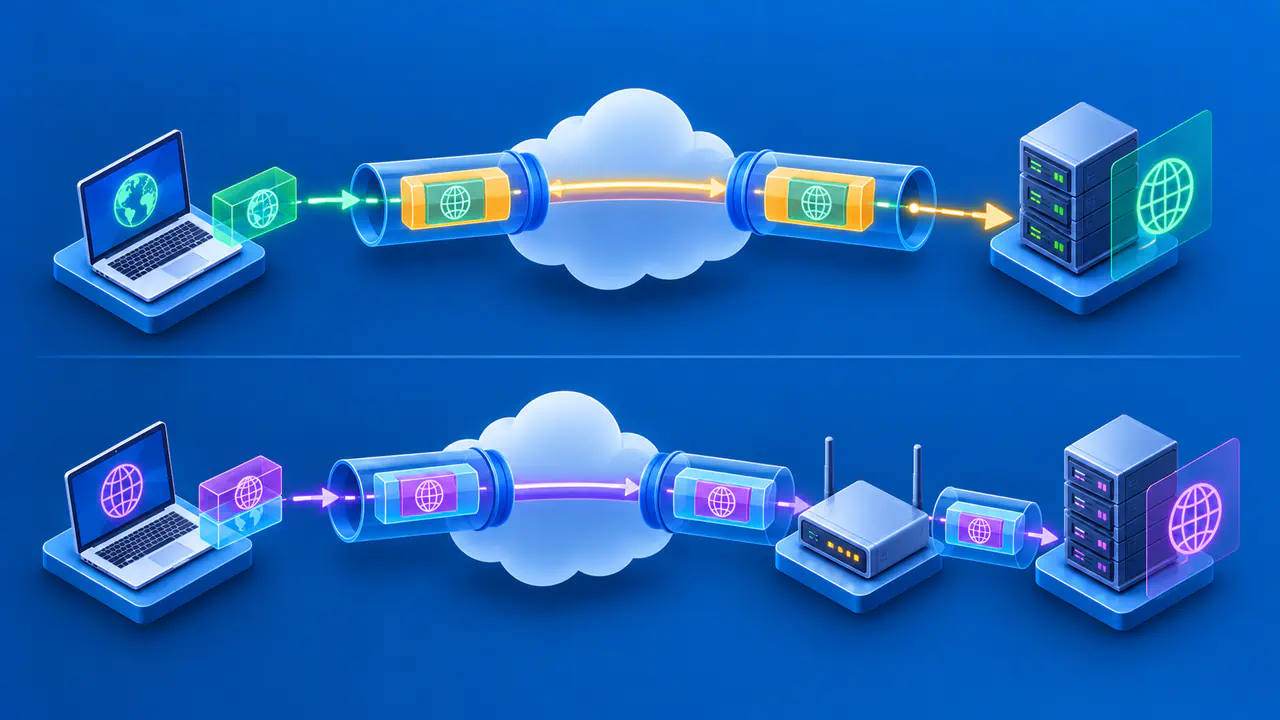
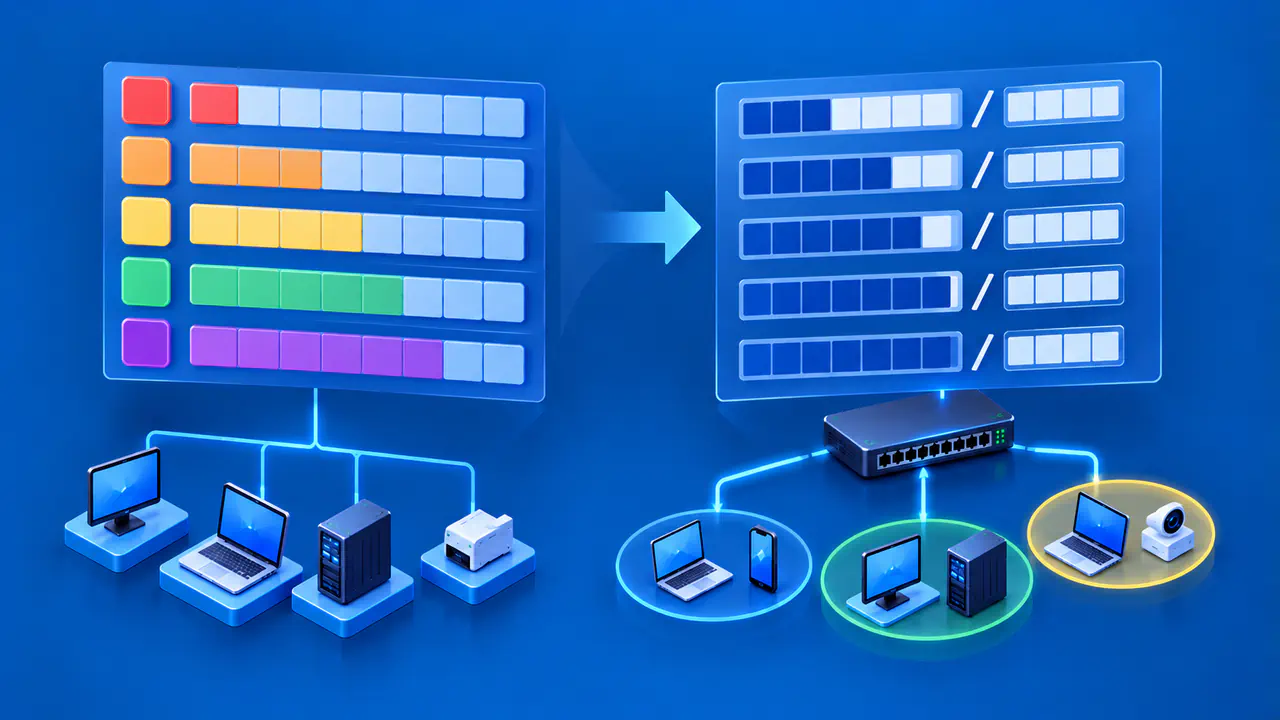
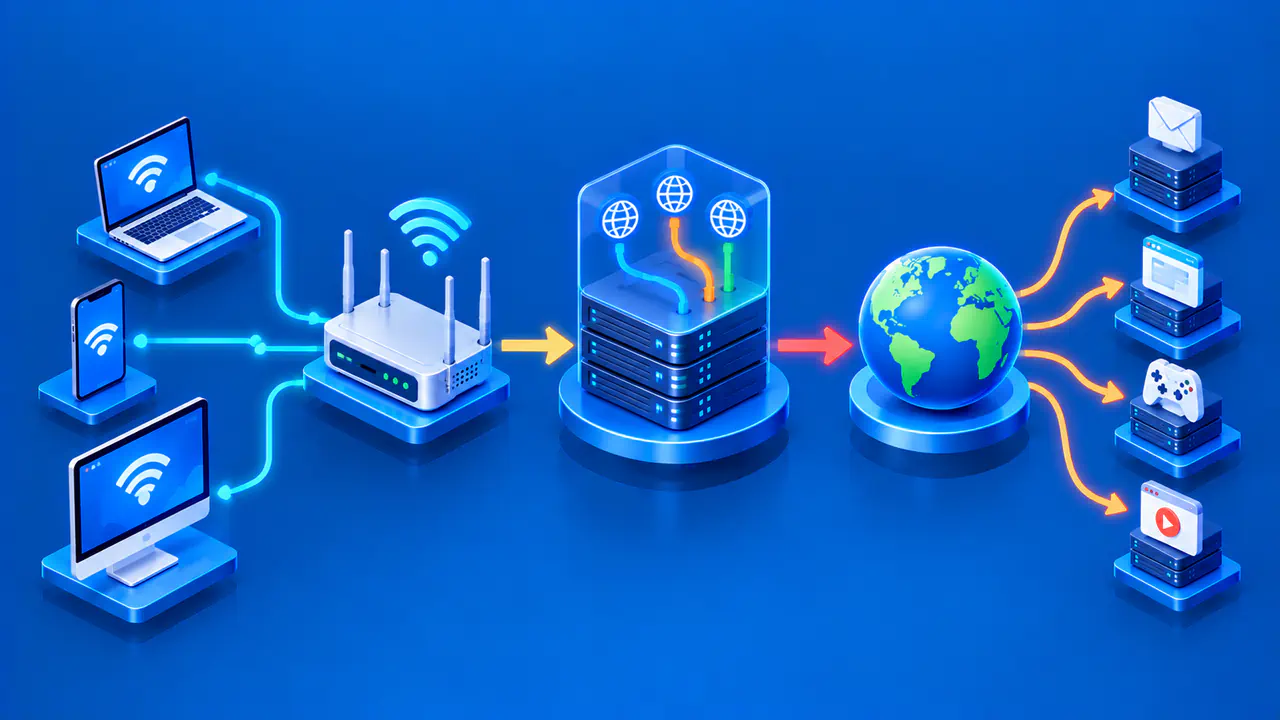
IPv6 prefix delegation lets a router obtain an address block for the networks behind it. The router can divide that block into separate local area network (LAN) prefixes, giving an office network, guest network, and device network their own IPv6 subnets.
A global IPv6 address on the wide area network (WAN) interface facing the upstream network does not tell you whether this delegation succeeded. That address identifies an interface; a delegated prefix supplies space for downstream networks. A router status page can therefore show working WAN addressing while still lacking the block needed for its LANs.
A delegated prefix comes with lifetimes that limit how long the router may use it. The Internet service provider may extend those lifetimes or replace the prefix. Receiving the same prefix several times does not mean the provider has promised a permanent allocation.
The Router Requests a Prefix Upstream
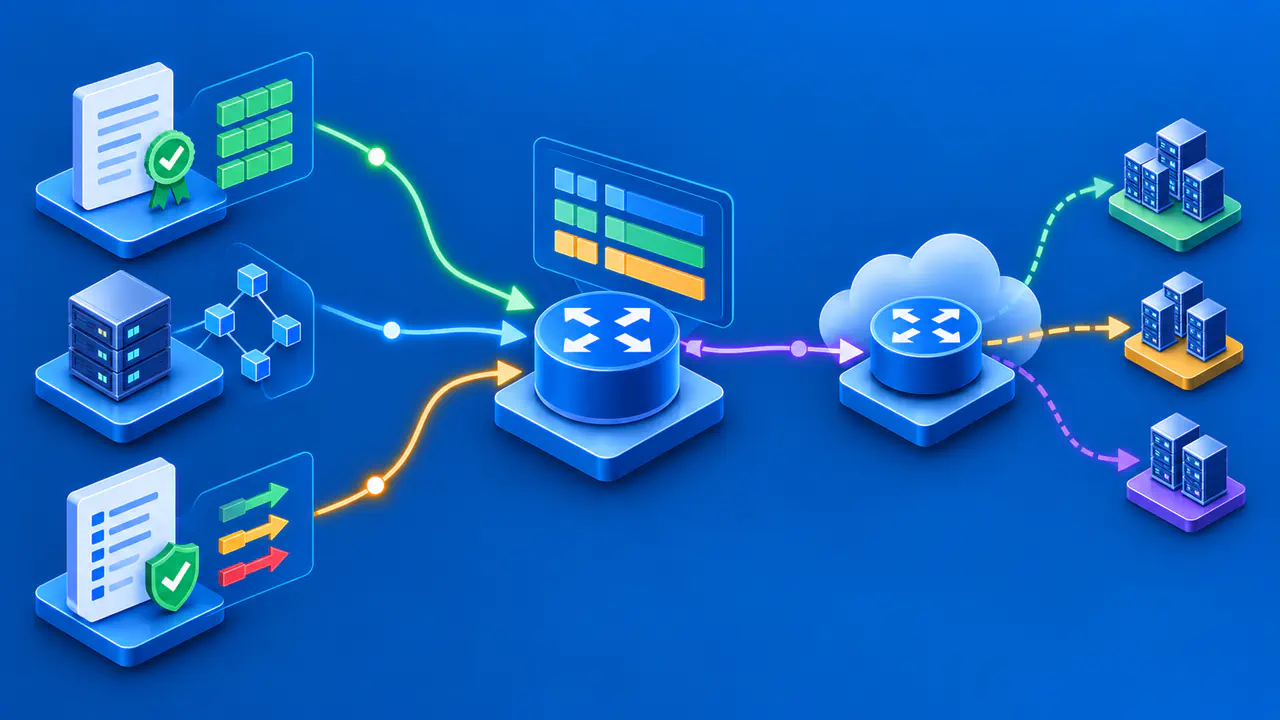
The usual Dynamic Host Configuration Protocol for IPv6 (DHCPv6) exchange starts with Solicit, followed by Advertise from an available server. The client selects a server and sends Request; the server returns Reply with the allocation. A router requesting a prefix uses the Identity Association for Prefix Delegation (IA_PD) option, while the Identity Association for Non-temporary Addresses (IA_NA) option handles interface addresses. These are separate options, even when carried in the same exchange.
A router may include a prefix-length hint describing how much space it wants. The server can return a different size according to its allocation policy. Requesting a /56 does not guarantee that the server will delegate one. Check the returned prefix length to see how much address space the router received.
Provider allocations do not have one universal size. Planning should start with the actual service offering and the number of downstream networks required. If the returned block cannot supply those networks, entering the desired length in the router again does not create the missing address space.
WAN Addressing and LAN Address Space
Receiving an IA_NA address does not assign the surrounding address block to the router's LANs. For example, a WAN address of 2001:db8:9:1::20 does not establish that the router controls 2001:db8:9:1::/64 for downstream use. The upstream link's addressing and the delegated LAN space have distinct roles.
A customer edge router can receive a delegated prefix without receiving an IA_NA address. If it requested both IA_NA and IA_PD, it must accept the delegated prefix even when no address is returned, unless it is configured to obtain its WAN address only through DHCPv6. A missing global WAN address alone therefore does not mean prefix delegation failed.
Packet delivery still needs routing. In an access network using a prefix-delegating relay, the relay maintains a route for each delegated prefix toward the requesting client and removes the route when the lease is released or expires. The route must point toward the router that received the prefix. A status page showing a delegated block does not, by itself, prove that traffic can reach the downstream LANs.
A /56 Can Supply Separate /64 LANs
Consider a hypothetical delegation of 2001:db8:48:5600::/56. These addresses come from documentation space and illustrate the arithmetic rather than a usable Internet allocation. For ordinary Ethernet LANs using Stateless Address Autoconfiguration (SLAAC), which lets hosts form addresses from an advertised prefix, use a /64 prefix for each LAN.
Moving from /56 to /64 leaves eight bits for selecting the child subnet. Eight bits provide 256 combinations: the fourth hexadecimal group runs from 5600 through 56ff. The first three groups remain 2001:db8:48 throughout this example.
- Staff LAN: 2001:db8:48:5600::/64.
- Guest LAN: 2001:db8:48:5601::/64.
- Device LAN: 2001:db8:48:5602::/64.
Those three allocations occupy three distinct child subnets, leaving 253 /64 subnets unassigned in the example. This is a count of subnet choices, not a limit of 256 devices across the site. Each LAN has its own address space within its /64.
The device LAN cannot be assigned 2001:db8:48:5700::/64 under this delegation: 5700 is beyond the parent block's final fourth-group value, 56ff. A child prefix must fit inside the received parent and must not overlap another LAN allocation.
How Prefix Length Changes the Number of LANs
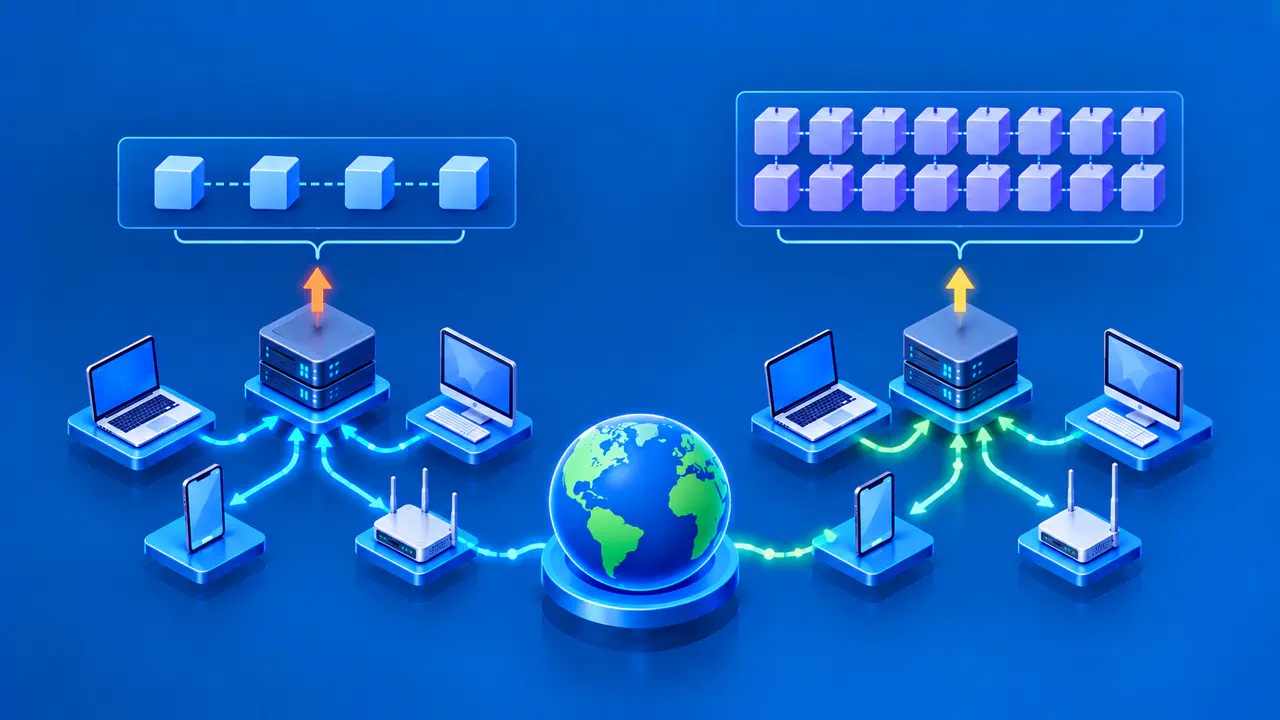
If the router instead receives 2001:db8:48:5600::/60, only four bits remain before /64. That block contains 16 /64s, from 2001:db8:48:5600::/64 through 2001:db8:48:560f::/64. After the same three LAN choices, 13 child subnets remain unassigned.
The earlier 2001:db8:48:56ff::/64 subnet falls outside this /60. Keeping a saved /56 layout after receiving a /60 can therefore leave LANs using space the router no longer has. The calculation must use the current prefix length as well as the current prefix value.
A received /64 supplies one conventional SLAAC LAN prefix. It cannot be divided into several smaller address blocks while preserving the /64 required for Ethernet SLAAC. If several separate LANs are needed, the service and router configuration must provide enough delegated space for them.
Hosts Learn Their Own LAN Configuration
After choosing a subnet for each LAN, the router advertises the corresponding prefix on that LAN. With SLAAC, a host forms its address from that advertised prefix and an interface identifier. The host on the guest network uses the guest prefix, not the entire /56 shown in the router's upstream delegation record.
Router Advertisements also let hosts discover default routers. That is a separate function from obtaining an address through DHCPv6. A LAN can have correctly formed addresses yet lack the default-router information needed for destinations beyond the link.
Each child prefix belongs to a particular LAN interface or virtual local area network (VLAN). The delegated block covers the downstream networks as a whole, a child prefix identifies one subnet, and a host address identifies an interface within that subnet.
Renewing the Delegated Prefix
When the renewal timer, T1, expires, the client sends Renew to the server that supplied the prefix. If no reply arrives before the rebinding timer, T2, expires, the client sends Rebind to seek an extension from any available server. These timers start requests; they do not guarantee an extension.
Preferred and valid lifetimes describe different stages of address use. When an address's preferred lifetime expires, it becomes deprecated: existing communication may continue while a suitable preferred address is favored for new communication. Once its valid lifetime expires, the address becomes invalid and cannot continue as an ordinary source or destination address.
LAN advertisements and downstream DHCPv6 assignments must not offer lifetimes beyond the remaining lifetimes of the delegated parent. For example, if a delegated prefix has only a few minutes of valid lifetime left, the router cannot advertise another full day of validity for a LAN prefix derived from it.
If the delegated prefix's valid lifetime expires without an extension, the router must stop using it. Retaining a remembered prefix in configuration is not a substitute for a current delegation.
When a New Prefix Replaces the Old One
When the delegated parent prefix changes, the LAN prefixes also change even if the router keeps the same subnet numbers. For example, retaining the guest subnet choice does not retain the old guest addresses when the provider replaces the parent block. The router must supply configuration derived from the new allocation.
If the old allocation remains valid during a planned transition, old and new addresses can coexist while the old ones are deprecated. If the old prefix is withdrawn immediately, that overlap may not be possible. The router must advertise stale LAN prefixes with both preferred and valid lifetimes set to zero. For downstream DHCPv6 clients, its replies must also set both lifetimes to zero for addresses or prefixes that are no longer valid.
This notification does not guarantee that every host instantly removes every old address. Hosts can miss advertisements, and SLAAC has rules protecting existing address validity against abrupt reductions from unauthenticated advertisements. Transition behavior depends on received information and remaining lifetimes, not merely on the router having obtained a new block.