How to Choose a DNS Server
Choose a DNS server by comparing its privacy policy, ability to resolve required names, filtering options, and performance on your own networks. Here, DNS server means the recursive resolver that answers your device's DNS questions, rather than an authoritative server that publishes a domain's records. Your internet service provider usually supplies a resolver automatically, but you may be able to choose a public service or one run by your organization.
No resolver is universally fastest: response time depends on the network route, cache state, and name being queried. A fast DNS answer also does not guarantee a fast website, because page loading includes connections and content transfers after name resolution. The best fit for a home connection may also be unsuitable for a workplace with private DNS names.
Start with ISP, Public and Managed Resolvers
Your router or network may supply the address of an ISP resolver automatically, or supply the router's own address so it can forward DNS queries. A public resolver is a service available over the internet, with its own privacy commitments and filtering options. A workplace or school may instead require a managed resolver that knows internal names and applies network policy.
Before choosing a replacement, identify any company domains or VPN services that depend on private DNS. A public resolver will not normally have access to an organization's internal DNS view. If a company hostname stops resolving after a change, that limitation can explain the failure even when public websites work.
Changing a recursive resolver does not edit a domain's authoritative records, change your internet subscription, or assign your device a new public IP address. It changes the DNS service used for queries handled by that setting. On a managed device or network, check whether policy permits that change before overriding the assigned resolver.
Compare Privacy and Encrypted DNS
A recursive resolver can observe the names sent to it and information associated with those queries, such as timing and the source IP address. Compare each provider's current policy for logging, retention, sharing, and the jurisdiction in which it operates. A broad “private DNS” label does not explain those practices. Policies vary among ISP resolvers and public services.
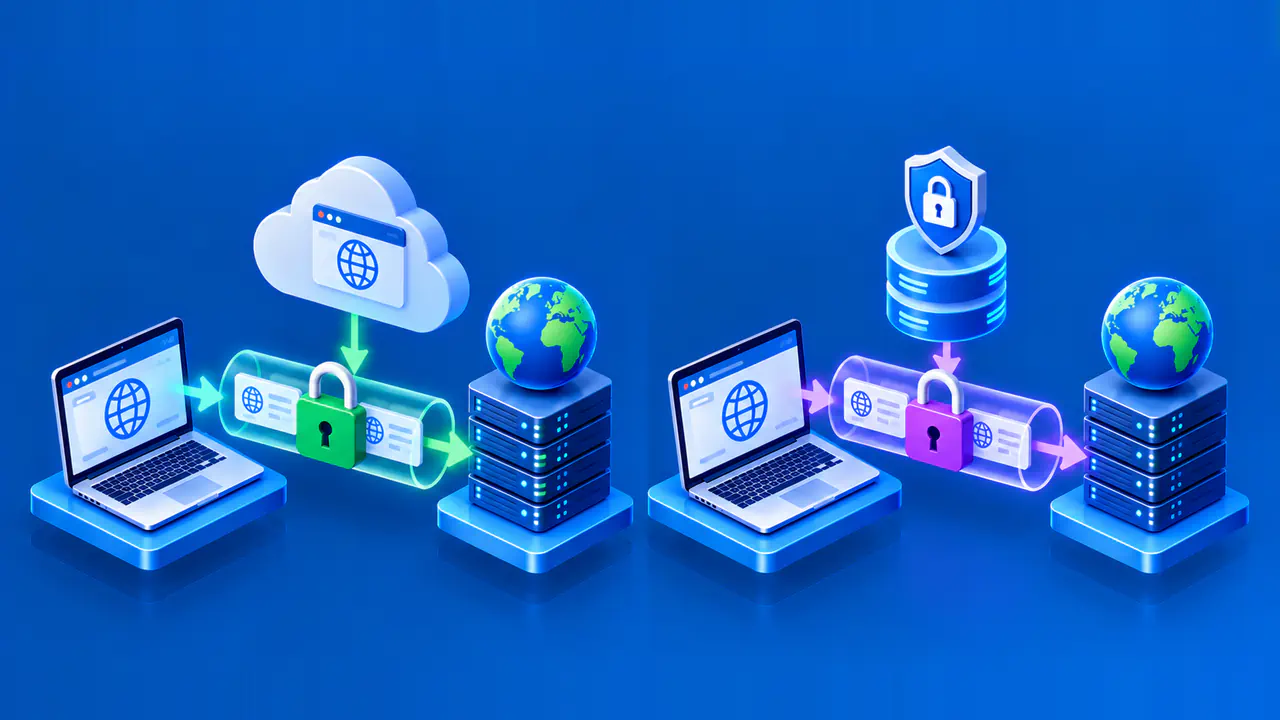
DNS over HTTPS and DNS over TLS encrypt queries between a client and its resolver. This protects the query contents against passive observation on that connection, but the resolver still receives the names being requested. Other network activity can also reveal destinations. Check that your device or application supports the provider's encrypted service, because entering an ordinary DNS server IP address alone does not necessarily enable encryption.
Check Filtering and DNSSEC Support
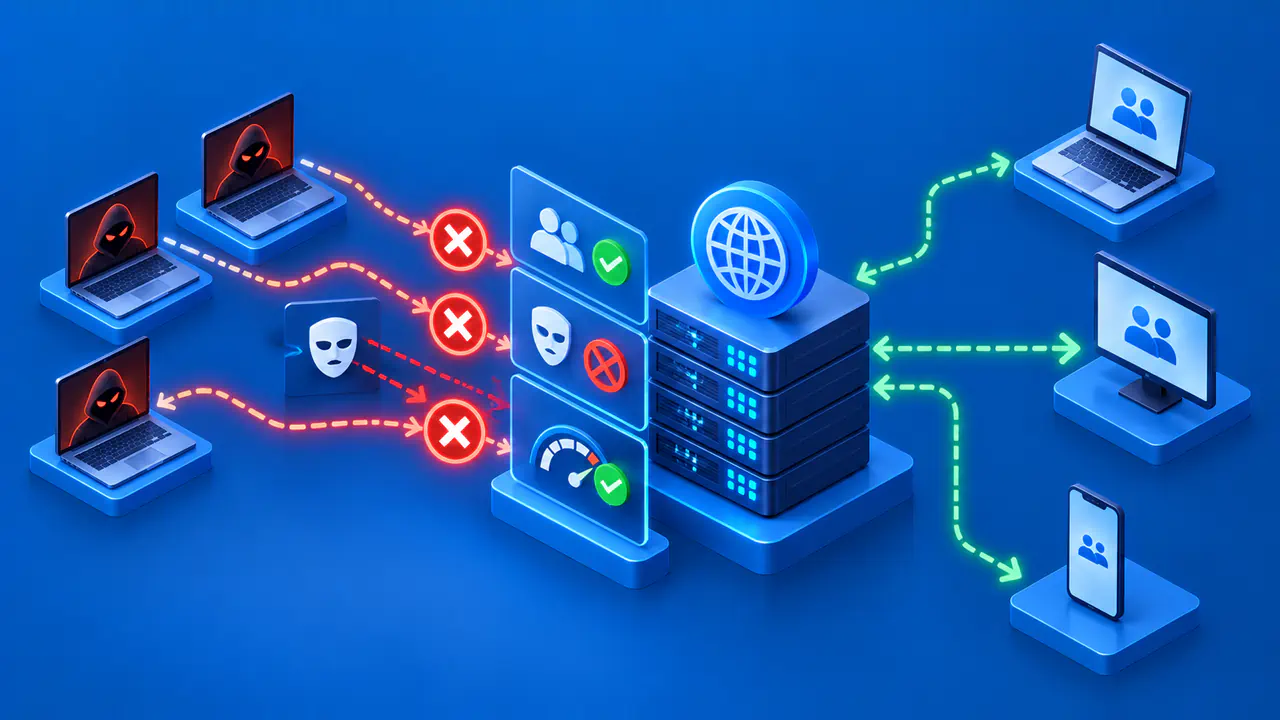
Decide whether you want domains blocked for malware, adult content, or other categories. Check how the provider classifies domains and handles an incorrectly blocked site. One provider can offer several endpoints or profiles with different filtering rules, so compare the specific service you intend to use. DNS filtering cannot guarantee that all harmful content is blocked, especially when an application uses another resolver or does not need a DNS lookup.
DNSSEC validation is a separate feature that checks DNS data using digital signatures and a chain of trust. A validating resolver rejects answers that fail those checks, but it can still answer for domains that are legitimately unsigned. DNSSEC does not encrypt queries or determine whether a website's content is safe. Confirm that a candidate supports validation instead of treating encrypted transport or malware filtering as proof that it does.
Check Reachability before Comparing Speed
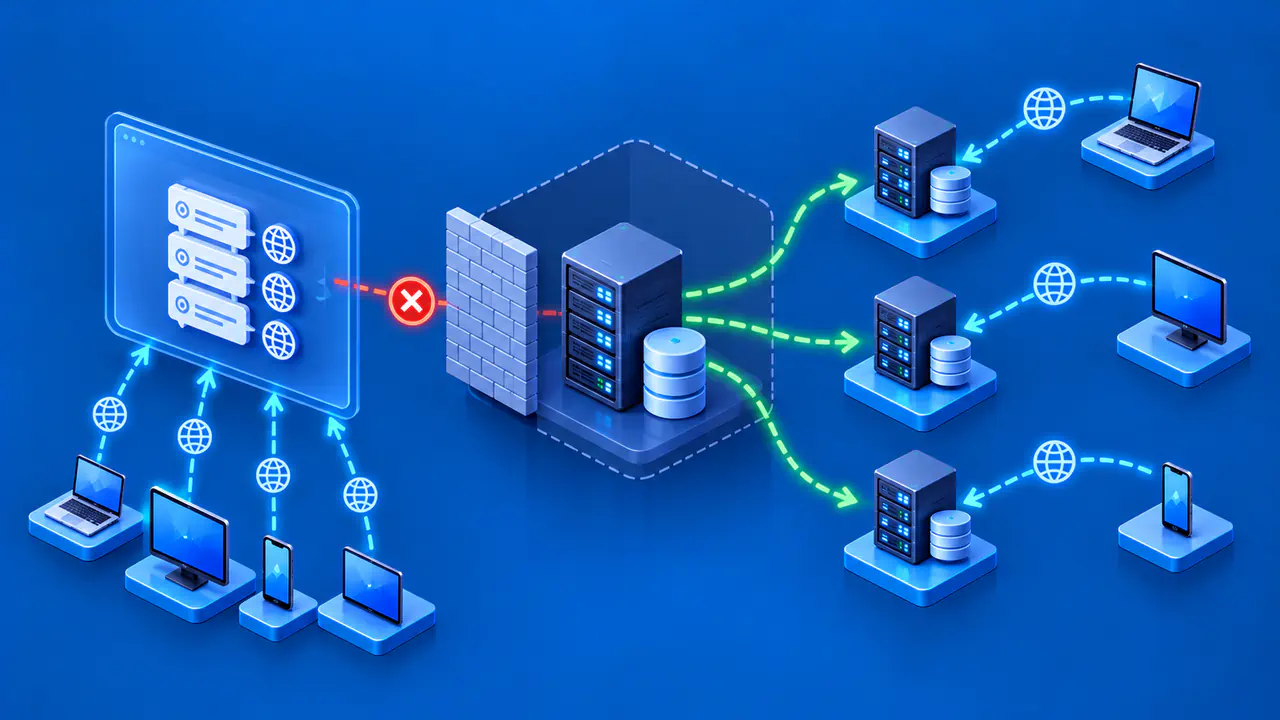
A candidate must be reachable on the networks where you plan to use it. Some networks block or redirect ordinary DNS traffic, and a captive portal may depend on the network's DNS service during sign-in. IPv4 and IPv6 connectivity to the resolver can also differ. A browser's own encrypted DNS setting may bypass the operating system's choice, while a VPN may route private DNS queries separately.
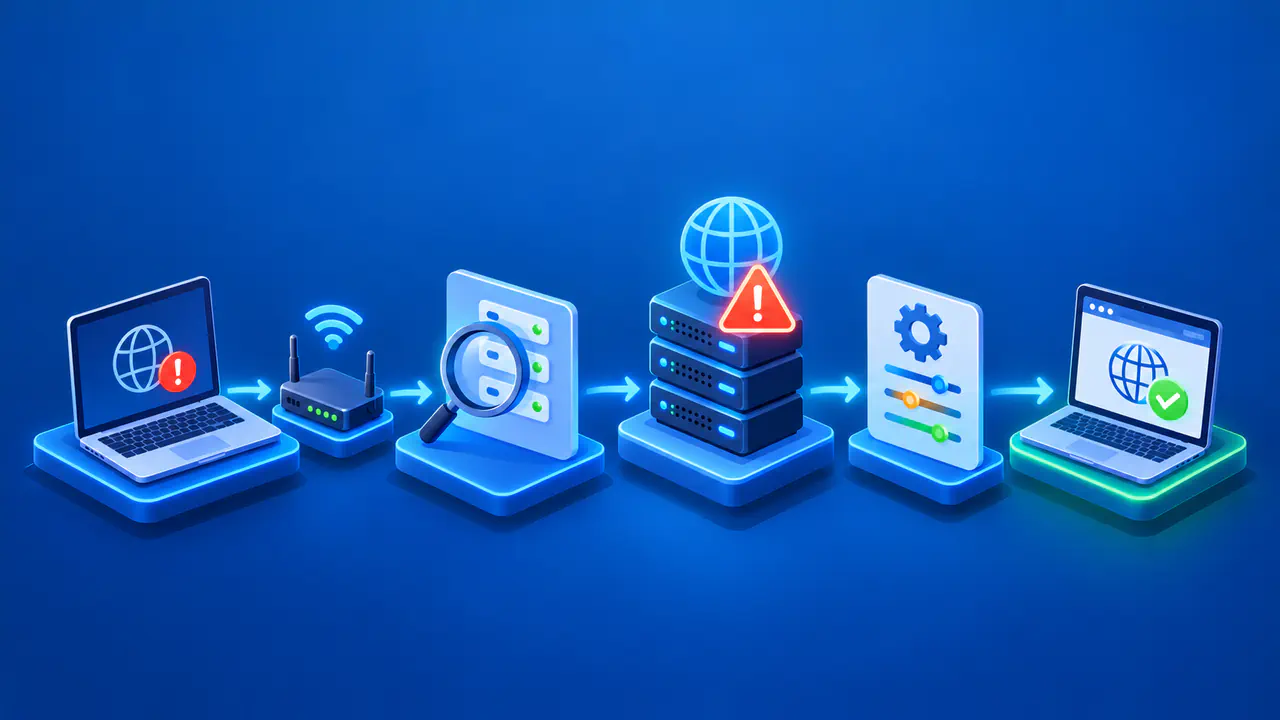
Test representative public names and required internal names on each relevant connection, such as home WiFi or a work VPN. Send DNS queries to the candidate using the transport you intend to use; success over ordinary DNS does not establish that its encrypted service is reachable. Record timeouts, failed lookups, and unexpected filtering before comparing response times.
A browser loading a page is not enough to confirm which resolver answered, because it may use cached data or another DNS service. Where a provider offers a connection check, use the check intended for the DNS transport being tested. If a custom setting prevents captive-portal sign-in, restore the network's approved DNS configuration before trying to sign in again.
Run Repeatable DNS Latency Tests
Use the same device, network, DNS transport, and set of names for each candidate. Query the same record types across multiple runs and at more than one time of day. Record the resolver address, query name, record type, response code, and elapsed time so that the results remain comparable.
Distinguish your first query for a name from later queries, but do not assume that the first one starts with an empty resolver cache. Other clients may already have requested the same name, and clearing your device's cache does not empty a public resolver's cache. Repeated queries can benefit from cached answers, but a public service may distribute them among servers with different cache contents. Call a test “cold cache” only when you can establish the relevant cache state.
Compare the median and range of successful query times, and count failed or unanswered queries separately. Otherwise, a candidate that answers quickly only when it works can look better than a more dependable service. Alternate the order in which you test candidates to reduce the effect of changes during the test period. For encrypted DNS, also distinguish a new connection from a reused connection, because connection setup can add delay.
If an application already has a usable cached answer, it may not query the chosen resolver at all. Treat these measurements as evidence about DNS responses from your connection, rather than a promise that every page will load faster.
Make the Change Reversible
Record the previous setting before replacing it, including whether DNS was assigned automatically or set to specific addresses. Change one layer at a time: a device setting affects that device, while a router setting can affect clients that obtain DNS settings from the router. An application or VPN can have its own configuration, so changing the router does not necessarily change every client's behavior.
Use the current documentation for your device or router to apply the setting, since menus vary by platform and version. After the change, repeat your checks for ordinary sites and any required private names through the applications you actually use. If the replacement prevents a required service from working, restore the recorded configuration and confirm that the service works again.