HTTP Security Headers Explained
HTTP security response headers tell a browser how to handle a page or resource after receiving a response. Different headers address different risks: unwanted script execution, framing by another site, disclosure of page addresses, misuse of browser features, insecure transport, and session cookie exposure. These browser controls supplement secure application code; they cannot correct flaws in authentication or access checks.
Choose headers according to the features and risks of the site. Identify which pages contain sensitive data, which outside scripts or frames are needed, how authentication cookies work, and which browser features the site uses. Introduce changes in stages and check whether the affected functions still work. Copying a universal set of headers can break legitimate behavior while leaving the actual risks unaddressed.
Match Each Header to a Browser Control
Security policies do not all have the same scope. HSTS applies to a host, CSP controls a document, and cookie attributes apply to individual cookies. Choose each policy for the part of the browser behavior it actually controls.
HTTPS Connections
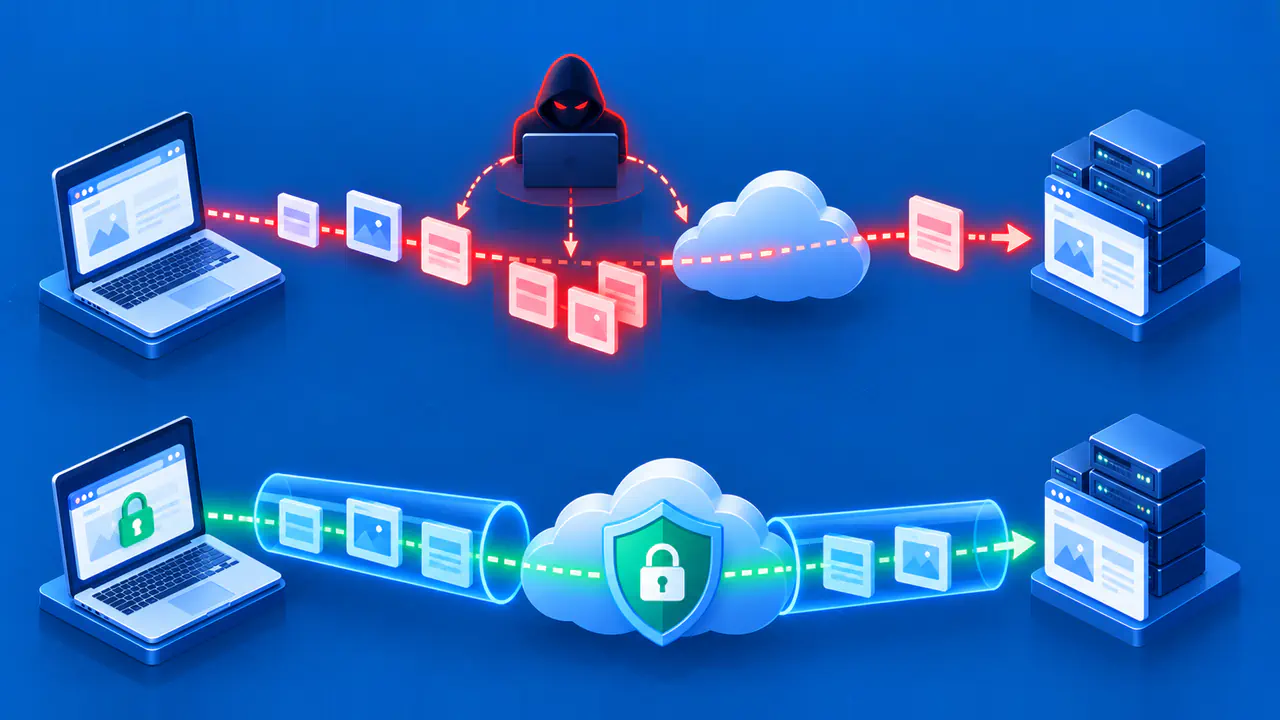
Strict-Transport-Security, or HSTS, tells a browser to use HTTPS for later requests after it receives the header over a valid HTTPS connection. It helps prevent a return to plaintext HTTP for a known host. The browser stores the policy for the duration set by max-age; includeSubDomains extends the rule to subdomains. If HTTPS fails or the certificate is invalid, the browser blocks the connection instead of allowing an insecure fallback. HSTS is distinct from a server redirect and should follow reliable HTTPS deployment.
Scripts and Page Embedding
Content-Security-Policy, or CSP, can restrict which scripts and other resources a document may load or execute. It can also restrict which sites may embed a page through frame-ancestors. These restrictions help counter cross-site scripting, which injects malicious scripts, and clickjacking, which uses embedded pages to trick visitors into unintended actions. The application must still handle untrusted input safely.
The right CSP depends on the site's scripts, styles, frames, and integrations. A broad allowance can make a policy ineffective, while an overly strict policy can block required functions. X-Frame-Options also restricts page embedding, but offers fewer choices than CSP for defining where embedding is allowed.
Referrer Information and Browser Features
Referrer-Policy controls how much page address information is included in the Referer request header when the browser follows a link or loads a resource. It can reduce disclosure of paths and query strings to other origins. It does not hide the visitor's network IP address, erase browsing history, or control every piece of information a request may contain. Choose a policy that fits the site's navigation and analytics needs.
Permissions-Policy can allow or deny selected browser features in a document and its embedded frames. A site that never uses a feature can restrict it, while a site using an embedded tool may need to allow that tool's origin explicitly. Allowing a feature through this policy does not grant any user or operating system permission it still requires. Browser support varies by directive, so test the specific feature in the browsers the site supports.
Content Types and Cookies
X-Content-Type-Options: nosniff tells supporting browsers to respect the declared content type, also called the MIME type. For scripts and stylesheets, a wrong Content-Type value can cause the browser to block loading. Set the correct type on the resource and use nosniff to prevent the browser from interpreting the response as a different type.
Set-Cookie attributes such as Secure, HttpOnly, and SameSite protect different aspects of a cookie. Secure restricts transmission to HTTPS, apart from the browser exception for localhost. HttpOnly prevents JavaScript from reading the cookie, and SameSite governs when it is sent with cross-site requests. None substitutes for the others or for server-side session controls. Cookie choices must reflect the login flow and any legitimate embedded or cross-site use.
Check Browser Support and Delivered Headers
Not every header or directive has identical support across browsers. Permissions Policy has uneven support across browsers and features. Older clients may ignore a newer directive; a browser may also enforce a default behavior that differs from another browser. Decide which browsers and application clients matter, then test the policy in representative versions rather than judging it from a header scanner alone.
Inspect the headers sent from the public endpoint, not only the origin configuration. A content delivery network (CDN), reverse proxy, or application framework may add, replace, or omit headers. Check HTML documents, redirects where relevant, and resources that need particular MIME or cache behavior. A header present on one page does not guarantee the same policy reaches another hostname or error response. Record where each policy is set so later changes do not create conflicting values.
Stage Changes and Observe Reports
Begin with working HTTPS and correct MIME types. Inventory session cookies and set their attributes according to the product's authentication flows. Choose a referrer policy after checking links and analytics, and restrict browser features that the site does not need. Set framing controls to permit the sites that genuinely need to embed your pages. These controls have different breakage risks, so a staged rollout makes causes easier to identify.
CSP needs particularly careful preparation. Content-Security-Policy-Report-Only lets a browser detect potential violations without blocking the affected actions. Configure a reporting destination if you want to collect those reports, then check which violations involve required scripts or frames. Test enforcement on a limited group of pages before expanding the policy. Reports can contain page addresses, so limit access to the reports and decide how long to retain them.
A CSP that allows scripts by nonce needs an unpredictable value generated separately for each response. The value in the policy must match the nonce attached to each approved script. Adding the same value indiscriminately to every script would also authorize an injected script, defeating that check.
For HSTS, check HTTPS on every hostname that the policy will cover. Start with a short policy lifetime and increase it only after checking those hosts. A long cached lifetime can delay rollback; inclusion in a browser's preload list creates a separate delay while list removals reach browsers. Submitting a preload request does not itself place the domain in every browser's list.
Test cookie and permissions changes against sign-in, embedded content, and feature prompts. Allow time to observe each stage, and record the policy actually sent to browsers. That record helps distinguish a configuration error from a browser that does not support a particular directive.
Recheck Behavior after Deployment
Verify the expected response headers on the public site and test the browser outcome, not just the syntax. Confirm that required scripts load, unauthorized frames are blocked, referrer data follows policy, browser features behave as intended, cookies support the login flow, and HTTPS remains reachable. Compare representative desktop and mobile clients when support differs.
Repeat the relevant checks when the application or the servers delivering it change. A new third-party script, an external sign-in service, or a CDN configuration change may affect a policy that previously worked. Include expected headers and required browser behavior in the review of those changes.