What Is a Subdomain, and When Should You Use One?
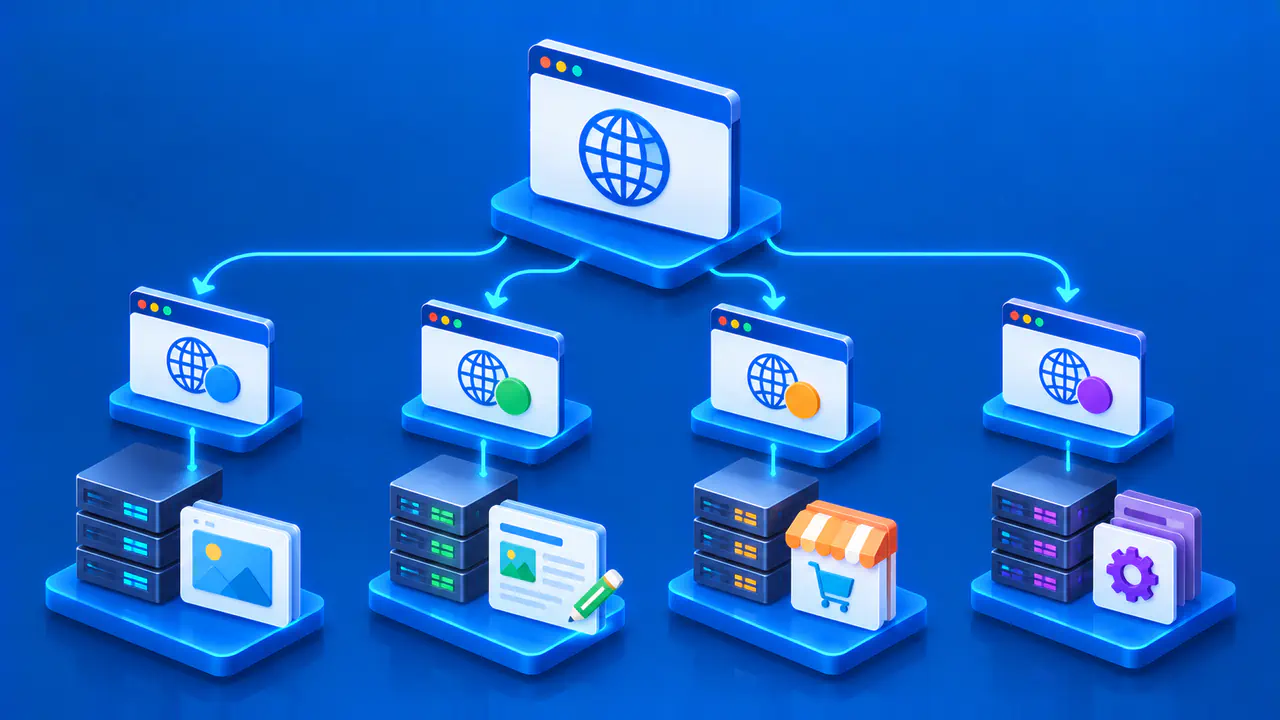
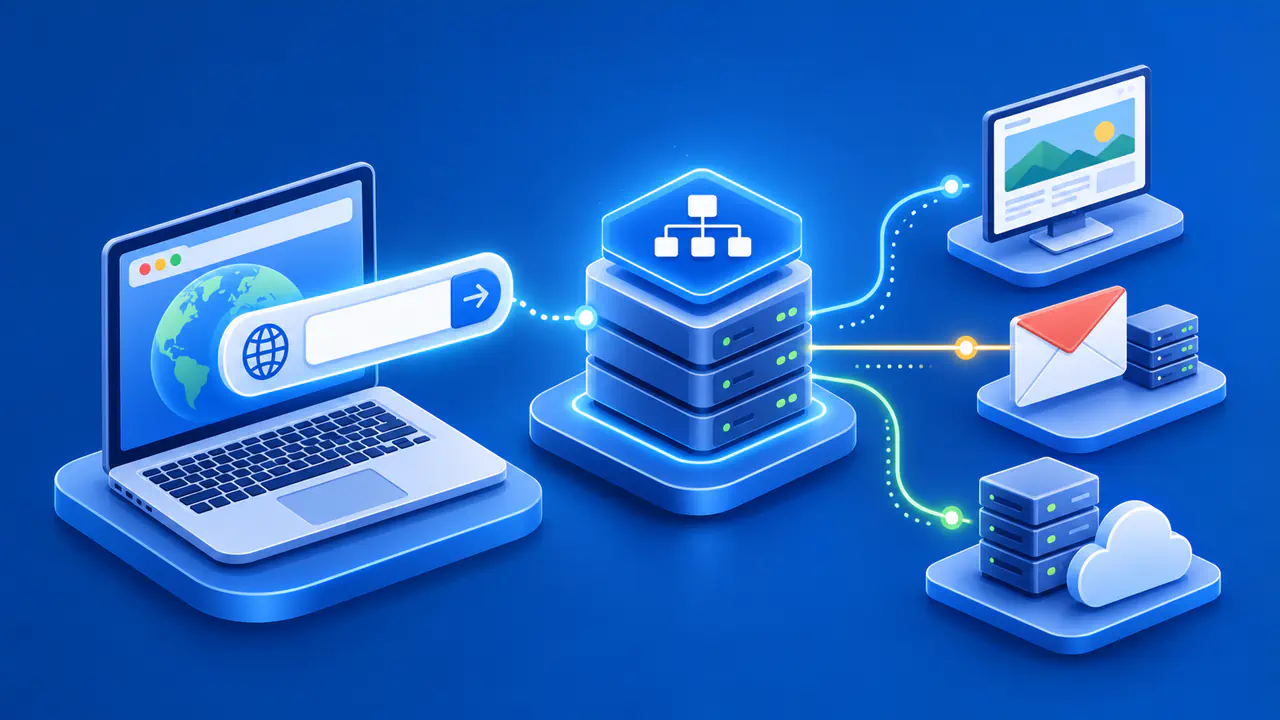
A subdomain is a name beneath another domain in the Domain Name System (DNS) hierarchy. In docs.example.com, docs is a label beneath example.com. The full name can identify a documentation site, an application, a mail service, or another resource. It does not, by itself, create a website or require a separate domain registration.
A separate hostname is useful when a service needs its own hosting destination or needs to be deployed or managed independently. It also adds DNS and application settings to manage. The right choice depends on what must be separated, not on an automatic search ranking benefit.
Parent Domains and Child Labels
DNS names form a tree of labels separated by dots. The name example.com is a parent of shop.example.com, and eu.shop.example.com sits one level deeper. In everyday site planning, the added label shop is often called a subdomain. Technically, shop.example.com and all names beneath it form a subdomain of example.com. The exact hostname is the full sequence of labels, not just the word shop.
A parent domain and a child hostname can resolve to the same destination or to different ones. For example, www.example.com may serve the main site while status.example.com serves a separately operated status page. They may even share an Internet Protocol (IP) address while the web server selects content using the requested hostname. Conversely, a name may exist in DNS solely for a nonweb service.
A subdomain is distinct from a URL path. In the URL https://example.com/docs/, /docs/ is the path on the example.com hostname, whereas docs.example.com is another hostname. Paths and hostnames can both organize content, but they have different DNS, browser origin, and deployment implications. Neither format is inherently superior for every site.
When a Separate Hostname Helps
Use a subdomain when a service needs to point to another platform or be managed by a different team. An application at app.example.com might use a managed application platform while the informational site at example.com stays on another host. A documentation service, support portal, or status page can follow the same pattern. Each hostname can have its own DNS destination and web configuration.
Development and staging environments are another possible use. A team may give an internal preview a distinct name so it is not confused with the public site. The hostname alone does not secure that environment: access controls, authentication, indexing decisions, and exposure of test data still need deliberate configuration. A public DNS record can make the name discoverable even if the team thinks of it as private.
A subdomain may be unnecessary when the content belongs naturally within the same application and shares its release process. A path can be simpler to manage if no separate DNS destination or browser origin is needed. Consider who operates the content, how deployments occur, whether users need a distinct address, and how the service will be secured. Base your choice on those needs rather than on broad claims about search rankings.
DNS Records and Delegation
A DNS zone is a managed part of the name tree whose records are published together. Adding a subdomain does not by itself require a separate zone. The operator of the parent zone can add records for the child hostname there.
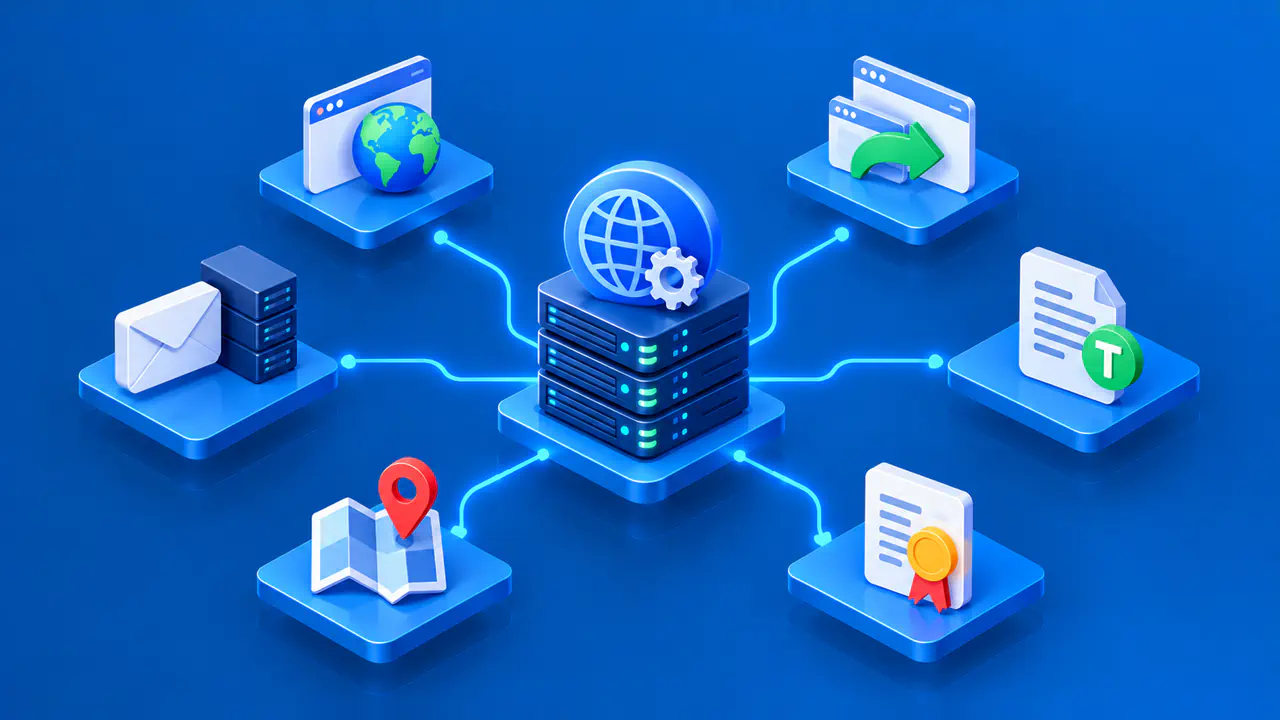
An A record supplies an Internet Protocol version 4 (IPv4) address, and an AAAA record supplies a version 6 (IPv6) address. A CNAME record makes one name an alias of another where that record type is permitted. The destination hosting provider may specify the exact record and value to use. Creating a DNS record provides connection information but does not deploy an application at that address.
Delegation is a separate option. The parent zone can publish nameserver (NS) records that assign authority for a child zone, such as team.example.com, to the nameservers responsible for that zone. These authoritative nameservers supply the child zone's DNS answers.
Delegation makes sense when another operator needs to manage many names beneath that child independently. The child zone must be configured on the servers named in the parent delegation. Delegation is not a routine requirement for a single app or docs hostname.
Check which zone is authoritative before editing. If the child is not delegated, create or update its record in the active parent zone. If it is delegated, the child hostname's address records and records for names below it belong in the child zone. Editing only an unused copy of the zone in another provider's panel will not change the active authoritative answers. Cached responses can also make a recent change appear at different times to different resolvers.
Hosting and Security Implications
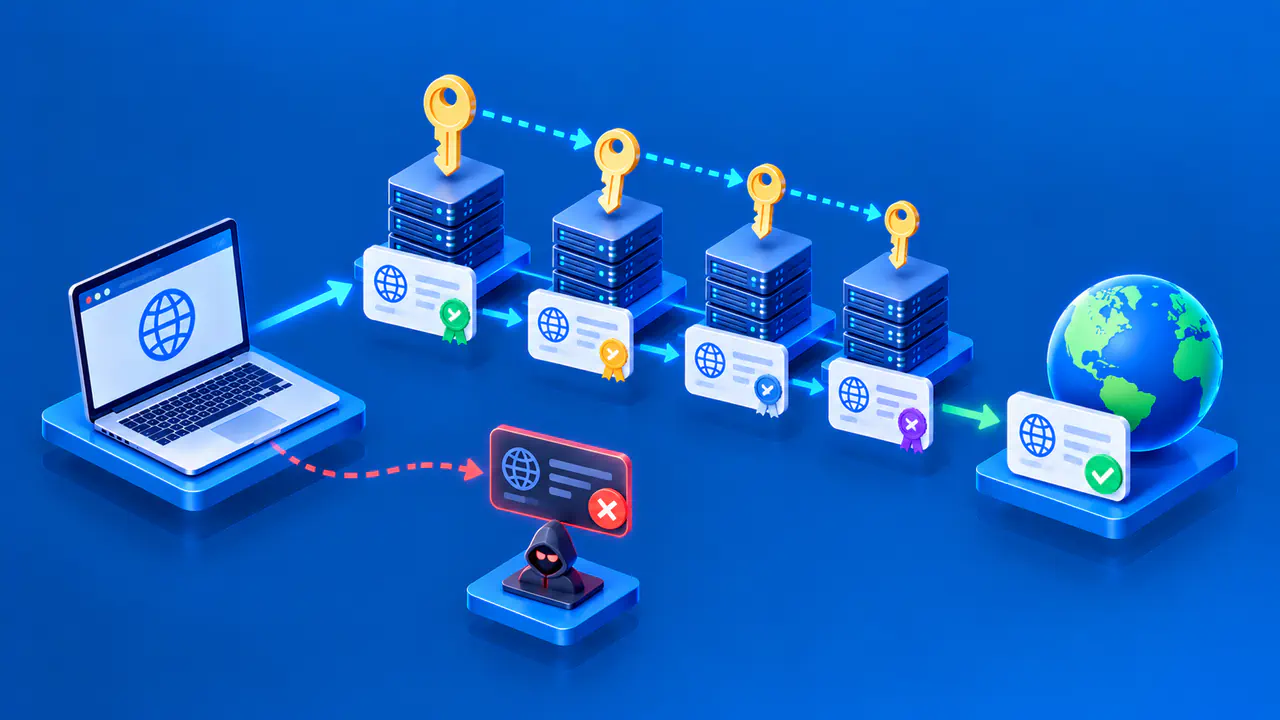
DNS gets clients to an endpoint, while hosting determines what that endpoint serves. Configure the web server or application to accept the new hostname and route requests to the intended content. For HTTPS, which protects web traffic with Transport Layer Security (TLS), the server must present a certificate valid for that hostname. A parent hostname's certificate does not automatically cover every child label. Coverage depends on the names in the certificate, and one certificate can cover several hostnames.
An origin combines the protocol scheme, such as HTTPS, the hostname, and the port number used for the connection. Even if example.com and app.example.com belong to the same organization, they are different browser origins. Requests between the applications, embedded resources, authentication flows, and browser storage may therefore need separate configuration. A subdomain can help separate applications, but it is not a complete security boundary: cookie settings, trusted scripts, access control, and hosting provider configuration still matter.
For a new subdomain, decide its purpose and identify the active DNS zone. Claim the destination hosting resource under your account before publishing a DNS record that directs traffic there. Configure the service to accept the hostname, then confirm HTTPS and access controls and test the intended address. A DNS answer alone does not prove that the website works.
When retiring a hosted service, remove or update its DNS records before releasing the hosting resource. If the old hosting resource can be claimed by another account, a leftover DNS record can let that account serve content under your hostname.