How to Find Out Which DNS Server Answered Your Query
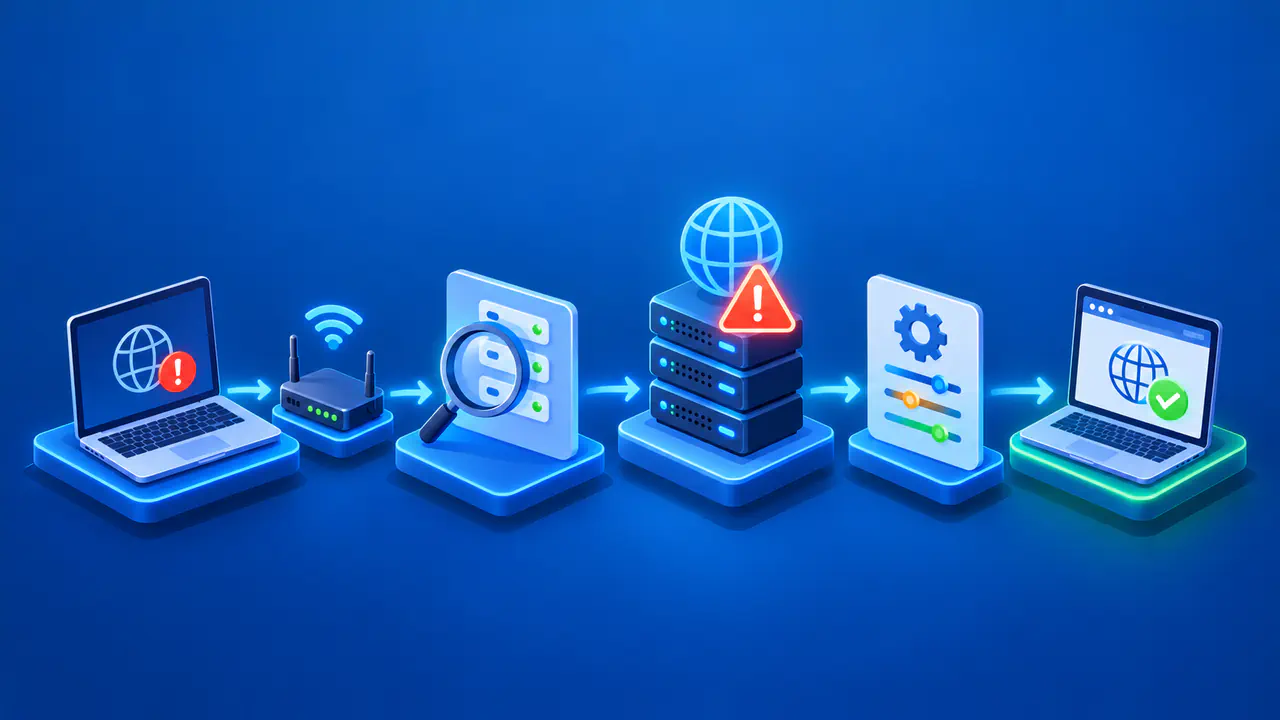
To find out which DNS server answered a query, check the server address in the lookup tool's output after it receives a DNS reply. In nslookup, look near the start of the result; in dig, look for the SERVER line near the end. The address may belong to a router, a local stub resolver, a corporate forwarder, or a public recursive resolver. It identifies the responding endpoint for that command, not every upstream server involved.
Use the same hostname and record type when comparing lookups, and run the comparisons close together. Record the time, active network connection, and VPN status for each result. Compare the configured system resolver with the endpoint shown by the command. If you are investigating a browser, check its DNS settings separately because the browser may use a different provider.
Start with System DNS Settings
Check the DNS servers assigned to the active network interface. On Windows, ipconfig /all displays the full configuration for each adapter, including its DNS servers. Find the adapter carrying the connection you are testing, rather than taking an address from an inactive adapter. The listed servers may come from automatic network configuration, a manual setting, or a VPN.
On Linux systems using systemd-resolved, resolvectl status shows global and per-link DNS settings. A local stub resolver receives requests from applications and passes them to the resolver service, which can select an upstream server. A loopback address therefore points to a service on your own device. Other Linux configurations may use a different resolver manager, so this command does not describe every distribution.
Configured servers are possible destinations, not proof of which server answered a particular lookup. A VPN can provide its own resolver or route selected domain names differently. If Wi-Fi and another interface are both active, their DNS settings may differ. Read the interface and domain rules together before comparing the settings with command output.
Find the Server in nslookup Output
For an IPv4 address record, run the following command on Windows. The name example.com is reserved for documentation; replace it with the hostname you are investigating when repeating your own lookup.
nslookup -type=A example.comWithout a server argument, nslookup uses its default DNS server. The Server and Address fields near the start identify the server being queried; the name and addresses in the answer describe the requested hostname. If the request times out, the displayed server address is only the attempted destination. A timeout alone does not establish that a DNS server replied.
To compare with a specific resolver, add its address after the hostname. For example, nslookup -type=A example.com 1.1.1.1 asks Cloudflare's public resolver if your network permits that connection. Use an approved resolver for internal names that should remain within your organization's DNS service. Supplying a server argument changes the destination of this command, without changing the device's DNS settings.
Find the Server in dig Output
Where dig is installed, dig example.com A requests the same record type. In its full response, the SERVER line identifies the endpoint that replied. Read this separately from the addresses in the ANSWER SECTION, which are DNS record data. Avoid using only +short output for this check because the default short display omits the server line.
A response from a recursive resolver may be non-authoritative because the resolver is answering on behalf of the domain's authoritative servers. The resolver can return a cached record without contacting those servers for this request. A non-authoritative answer is therefore not automatically wrong. The responding server's address and the identity of the server that originally published the record are different pieces of information.
Check the Browser's DNS Settings
A browser can send DNS queries to its own DNS over HTTPS provider instead of following the command-line tool's resolver path. On desktop Firefox, open Settings, then Privacy & Security, and locate DNS over HTTPS. Check both the protection level and the displayed status. Default Protection can fall back to the default resolver, and conditions such as a VPN or enterprise policy can cause Firefox to use local DNS.
On desktop Chrome, open Settings, then Privacy and security, then Security, and find Use secure DNS. Automatic mode can fall back to unencrypted DNS if a secure lookup fails. With a custom provider selected, Chrome does not fall back to unencrypted DNS by default. These settings can help explain differences between DNS lookups in a browser and a command-line tool.
Identical answers from a browser and a command-line tool do not establish that they contacted the same resolver. Several providers can return the same records, and a browser cache can avoid a new lookup. Browser settings explain the configured behavior; they are not a complete record of past queries. For a specific failure, compare the hostname, timing, and browser's current DNS status with the command result.
Check Upstream Forwarding and Caches
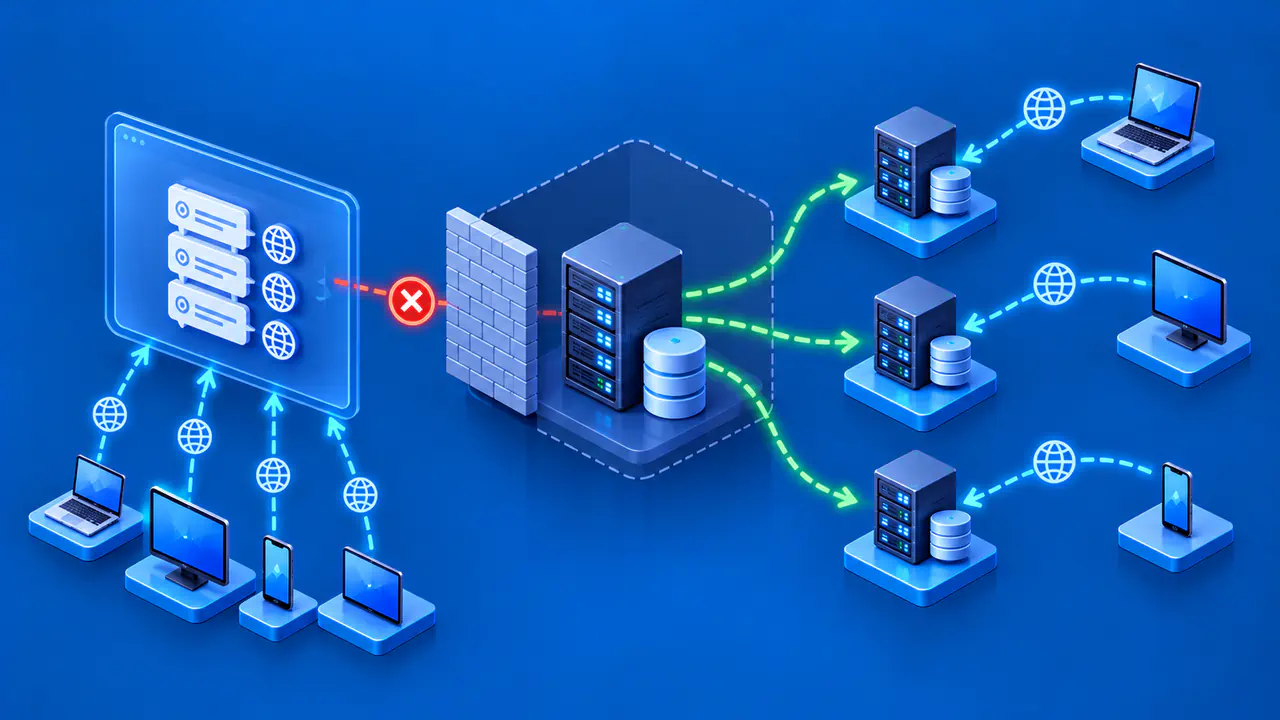
If the responding address belongs to your router, the router may forward requests to an ISP resolver, a public service, or another local server. A local stub can also select among several upstream servers. Inspect the router or resolver configuration to identify those candidates. The configuration alone does not establish which upstream server handled an earlier request.
A cache can answer a query without any new upstream request, so there may be no upstream contact to find for that lookup. Different answers on two devices can reflect cache state, network policy, domain-specific routing, or a change in the records. A difference in returned addresses does not by itself identify the cause. Keep the requested record type and query time with each result.
For a forwarding problem, give the administrator the exact command, complete response, timestamp, and active network details. Query logs on the router or local resolver may then show whether the request was forwarded and where it went, if suitable logging was enabled. Browser-specific logs may be needed for a browser lookup. Use evidence from the component handling that query to decide which resolver or setting needs attention.