What Is Anycast DNS?
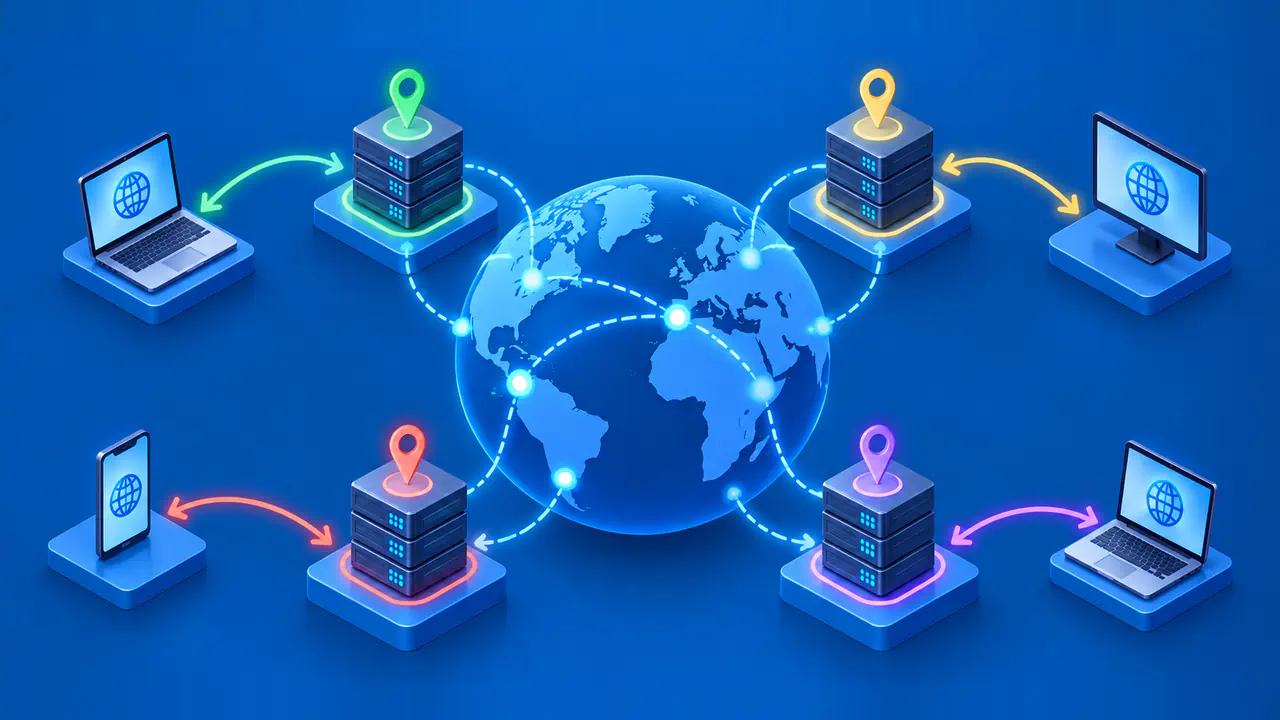
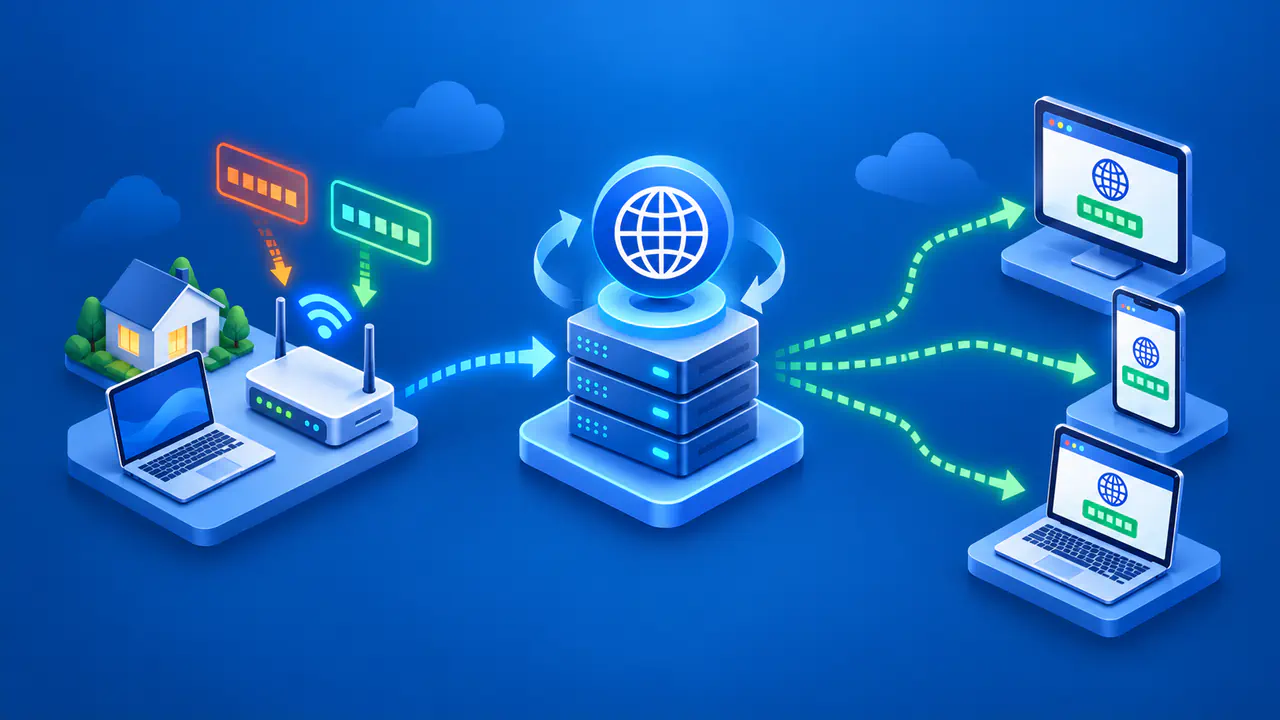
Anycast DNS makes the same DNS service IP address reachable from servers at multiple network locations. Each site announces a route to that shared address, and the routing system sends a query toward one of the available sites. To the DNS client, the service still appears at one address.
Network routes and routing policies determine which anycast site receives a query. When routes change, the same client can reach a different site without changing the DNS server address it uses.
This design can improve reachability and distribute query load, but the chosen site is not guaranteed to be the closest physical location or the lowest-latency server. Operators need stable routing, consistent service settings, and checks that remove routes to failed services when appropriate. They also need to monitor the service from several networks and keep authoritative zone data synchronized.
One Service Address at Several Sites
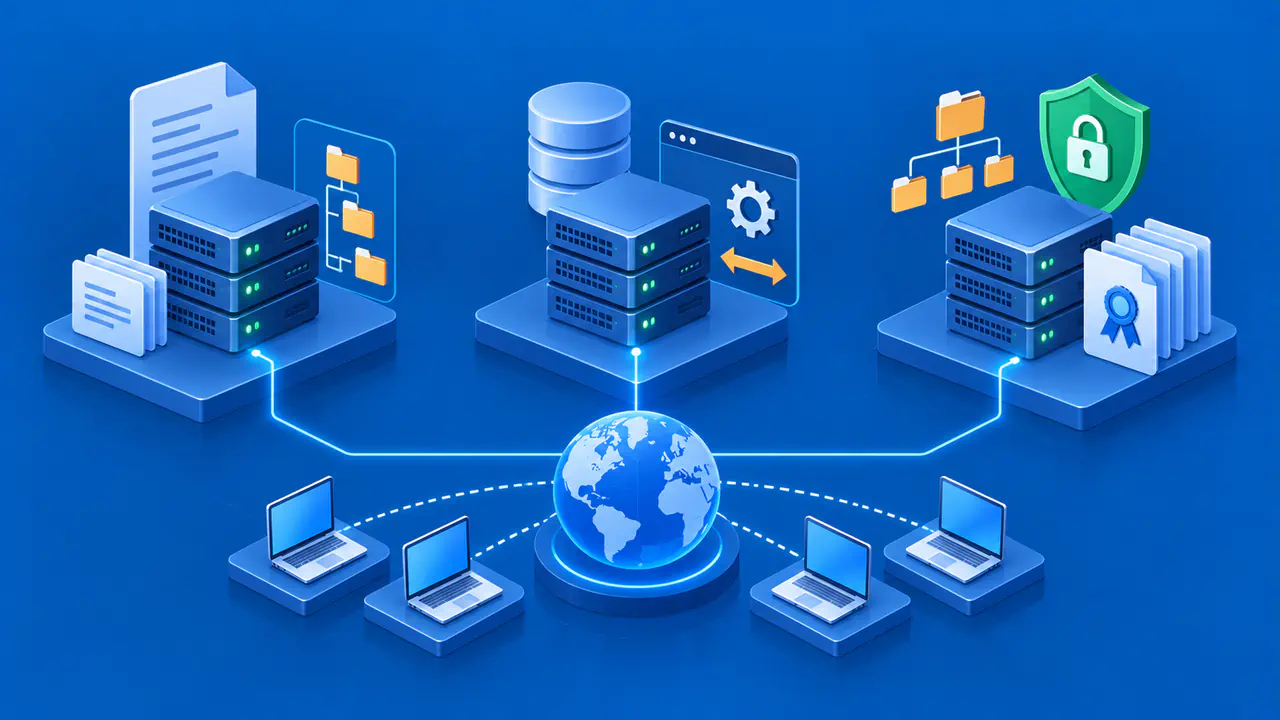
An anycast node is a server, or a group of servers and routers, that provides the shared DNS service at one location. A node may distribute incoming queries among several local servers. The anycast service has at least two independent nodes, each reachable through a route to the same service address.
For an authoritative DNS service, a zone's NS record can name a server whose A or AAAA record contains the anycast address. Resolvers across the internet query the same destination address, even though their packets may reach servers in different cities or networks. A recursive DNS service can use the same principle for the resolver address configured on client devices.
Operators normally use unique unicast addresses to manage individual nodes. These addresses let an operator reach a specific site to update or monitor its servers. The shared anycast address alone does not identify which site handles a client's query.
Every active node must be ready to provide the service before it advertises reachability. If a route becomes visible while the DNS process is unavailable or the zone data is incomplete, traffic can be attracted to a node that cannot answer correctly.
How Routing Chooses an Anycast Node
Within one managed network, an interior gateway protocol can carry routes to the service address from several sites. Across the global internet, operators commonly use BGP to announce a prefix, or address range, that contains the service address. Other networks receive those announcements and apply their own routing policies.
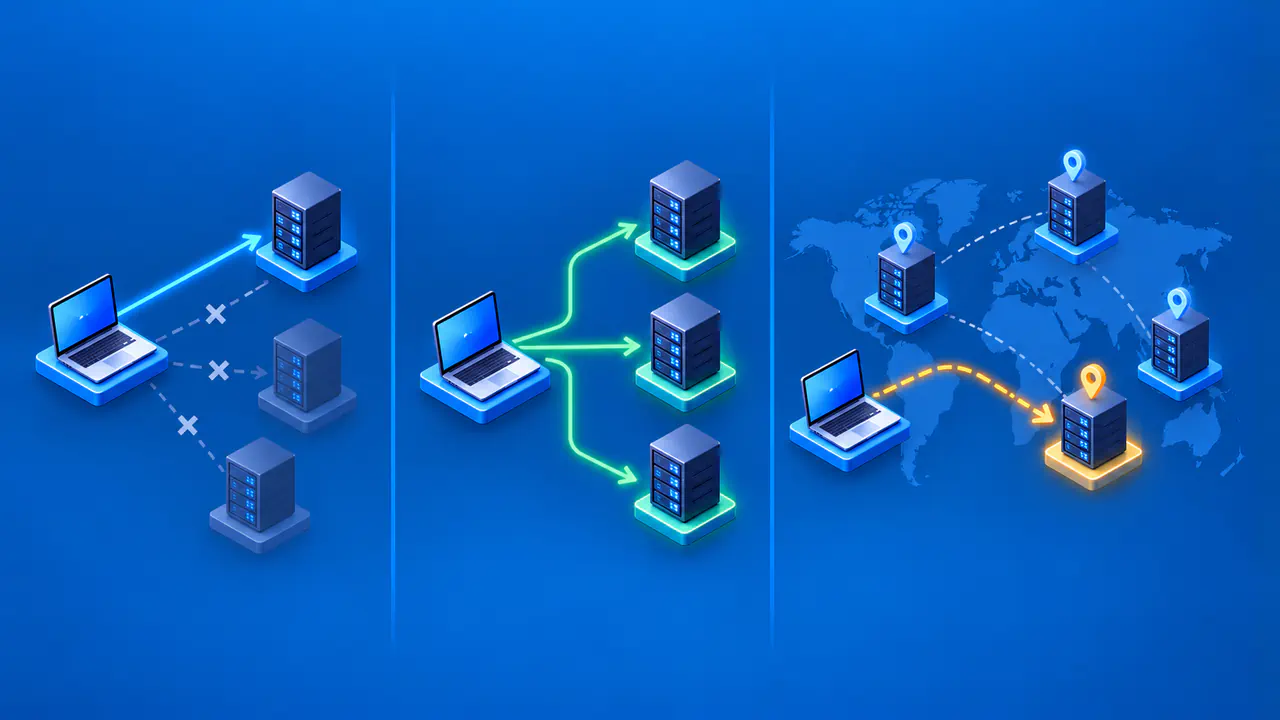
The selected route reflects factors such as local preference, path attributes, peering relationships, route availability, and internal metrics. Routers do not compare the physical distances between sites to choose a route. An internet provider's commercial agreements can favor a path through a farther city even when a nearer node exists.
The set of networks routed to one anycast node is called its catchment. Catchments can be large or small, and they do not need to follow national or regional borders. For example, two devices in the same building can reach different nodes if they use internet providers that select different paths.
Anycast does not divide queries evenly among nodes. An access network with many clients can send substantial traffic to one node while another node receives little. Operators can adjust route announcements to influence the distribution, but they cannot dictate the routing choices of every network on the internet.
Why DNS Works Well with Anycast
Many DNS exchanges are short: a resolver sends one UDP query and receives one response. Keeping traffic on the same path for a brief exchange is generally easier than maintaining it throughout a long connection. This makes those DNS transactions well suited to anycast.
DNS also uses TCP and encrypted transports such as DNS over TLS, which can keep connections open for multiple queries. These connections depend on packets reaching the node that holds their connection state, unless the deployment can share or otherwise preserve that state. If routing sends later packets to a different node that lacks the state, the connection can fail and the client may need to reconnect or retry.
Authoritative nodes should provide consistent answers for the zones they serve, except where the operator deliberately configures different responses. Zone transfers or another distribution mechanism keep the records synchronized. Operators also need to coordinate DNSSEC data and configuration changes, and check that the software running at different nodes behaves consistently.
DNS can list several authoritative server names for a zone, and each server name can have one or more addresses. Anycast adds redundancy behind each shared address by making it reachable at several sites. Keeping multiple authoritative server names and addresses provides another way for resolvers to retry when one destination fails.
How Anycast Improves Resilience
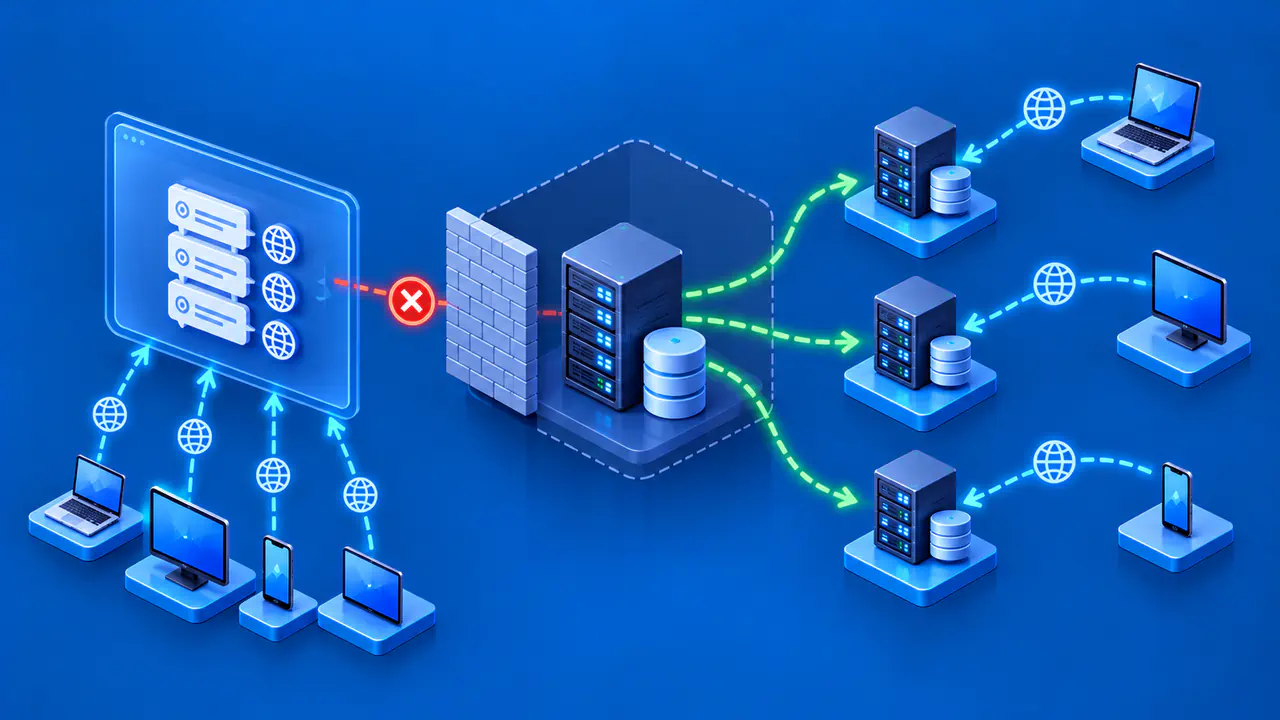
When a node or its network path fails, its route can be withdrawn. Routers can then select another available path, allowing queries to reach a surviving node at the same DNS server address. This failover changes the network route rather than a DNS record.
The decision to advertise or withdraw a route should account for whether the DNS service is working. A router can remain healthy while the DNS server software is stopped or returns errors. Health checks should trigger the configured failover without repeatedly withdrawing and restoring a route in response to brief or misleading failures.
A covering prefix may include several service addresses. Withdrawing that prefix for one failed service also changes routing for the others, so a deployment may instead forward requests for the failed service to another healthy node.
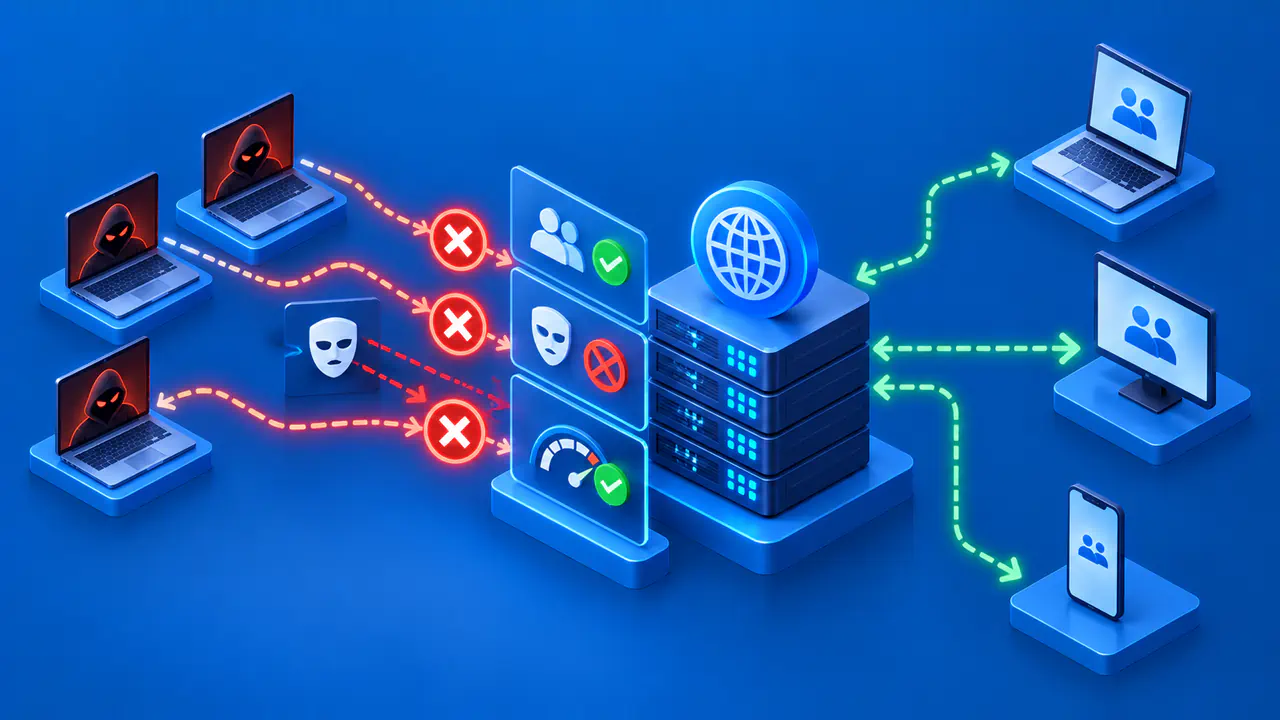
Anycast can limit the impact of congestion or an attack to part of the service, leaving other nodes available. However, withdrawing a route during an attack can send the attack traffic to other nodes and overload them in turn. Operators still need enough capacity, traffic filtering, and suitable DNS response limits; moving traffic alone does not stop an attack.
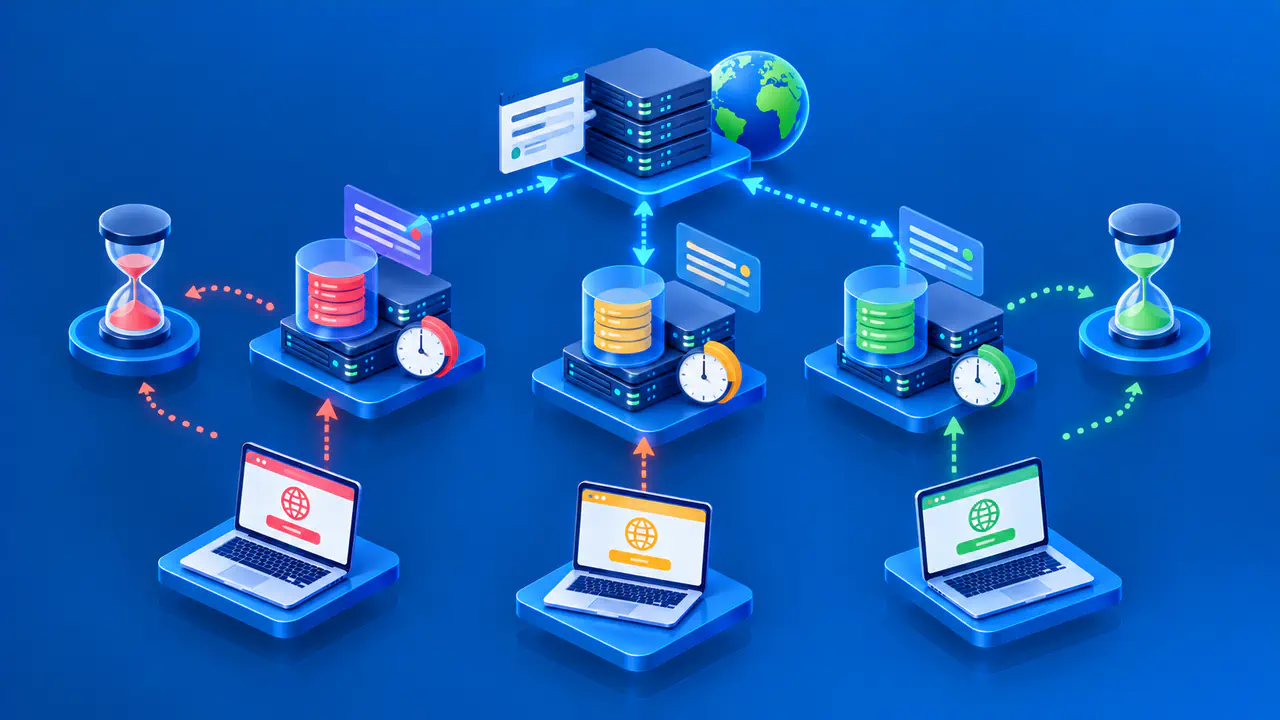
Networks take time to learn about route changes and select new paths. Some update sooner than others, and routing policies can delay or suppress changes. A quick switch observed from one test location does not show that clients everywhere have recovered.
Anycast DNS and GeoDNS Are Different
Anycast uses routing to deliver packets for one IP address to a node. GeoDNS returns different DNS records according to an estimated client or resolver location. Anycast determines where packets sent to an address arrive; GeoDNS determines which answer a DNS query receives.
The methods can be combined. A geographic DNS rule can return one of several regional addresses, and each regional address can be anycast from multiple sites. When troubleshooting that setup, check both the address returned by DNS and the site that receives packets sent to that address.
Monitoring from Different Networks
A successful check from one office shows only that the node reached from that network was responding at that time. Queries to the same address from another internet provider may reach a different node. Monitoring from just one location can therefore miss failures that affect clients on other networks.
An unexpected route can also indicate a security problem. An unauthorized or mistaken announcement may draw traffic away from legitimate nodes. Operators should authorize the expected BGP origin for their prefixes, filter inappropriate routes, and watch for unexpected changes in the originating network or path.
How to Verify an Anycast DNS Service
Begin by querying the shared address from multiple independent networks and checking the DNS replies. Where the service supports it, record the responding node's identifier, or match the query to the operator's logs. The destination address alone cannot tell you which node answered.
Measure response time and check the returned records from each test location, then inspect network paths and BGP announcements. Traceroute may help identify the answering site, but filtered replies, different return paths, and routers' response behavior can leave gaps or make the path hard to interpret. Compare those results with routing data and node logs.
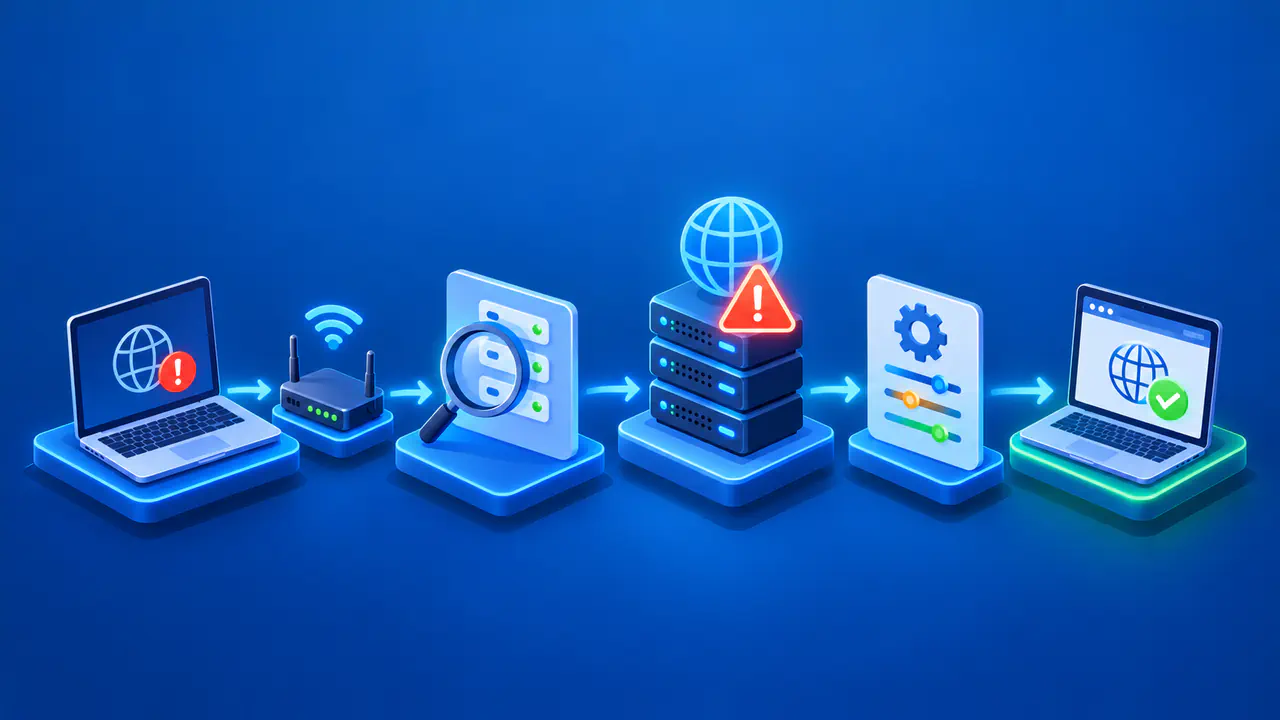
On infrastructure you control, test a DNS service failure separately from a network route failure. Under an agreed test plan, stop the DNS service or isolate a test node, then check that the configured route withdrawal or forwarding takes effect. Measure recovery from the relevant client networks and confirm that the surviving sites can handle the additional traffic.
For authoritative DNS, also compare zone serials, DNSSEC responses, and configuration across nodes. Allow for the expected time to distribute an update, and investigate missing records or failed signature validation.