How to Fix a 403 Forbidden Error
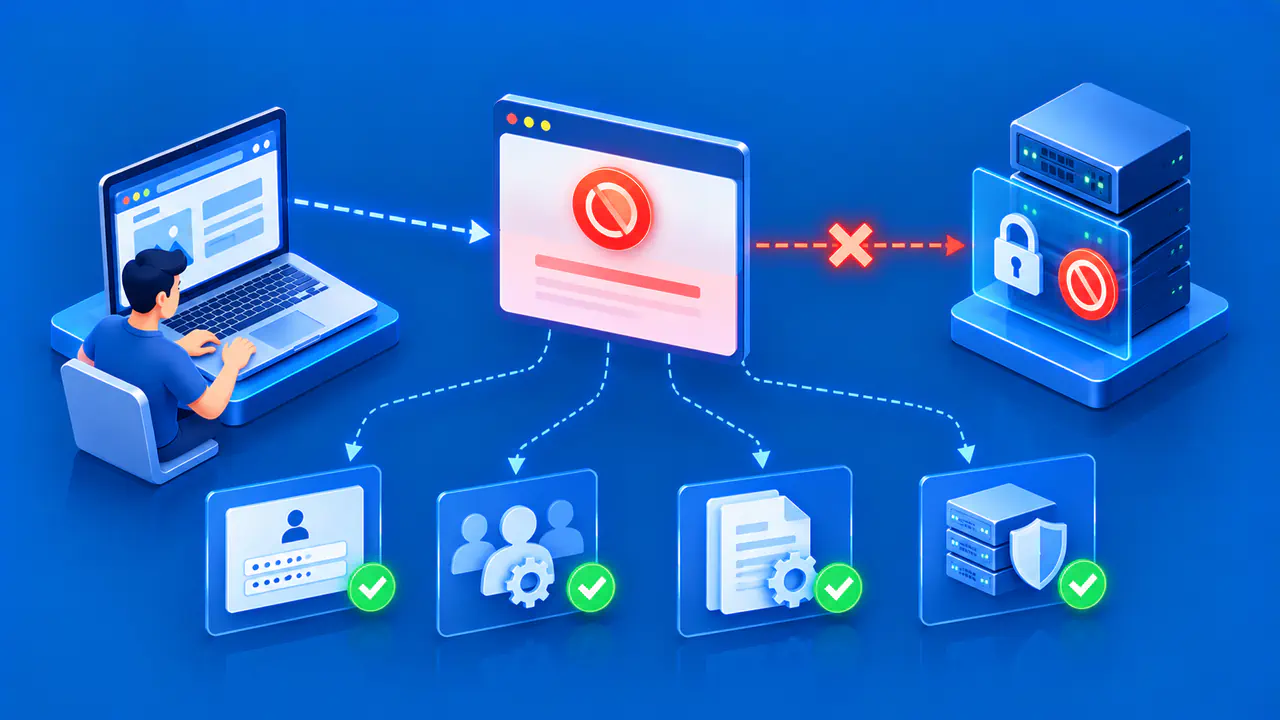
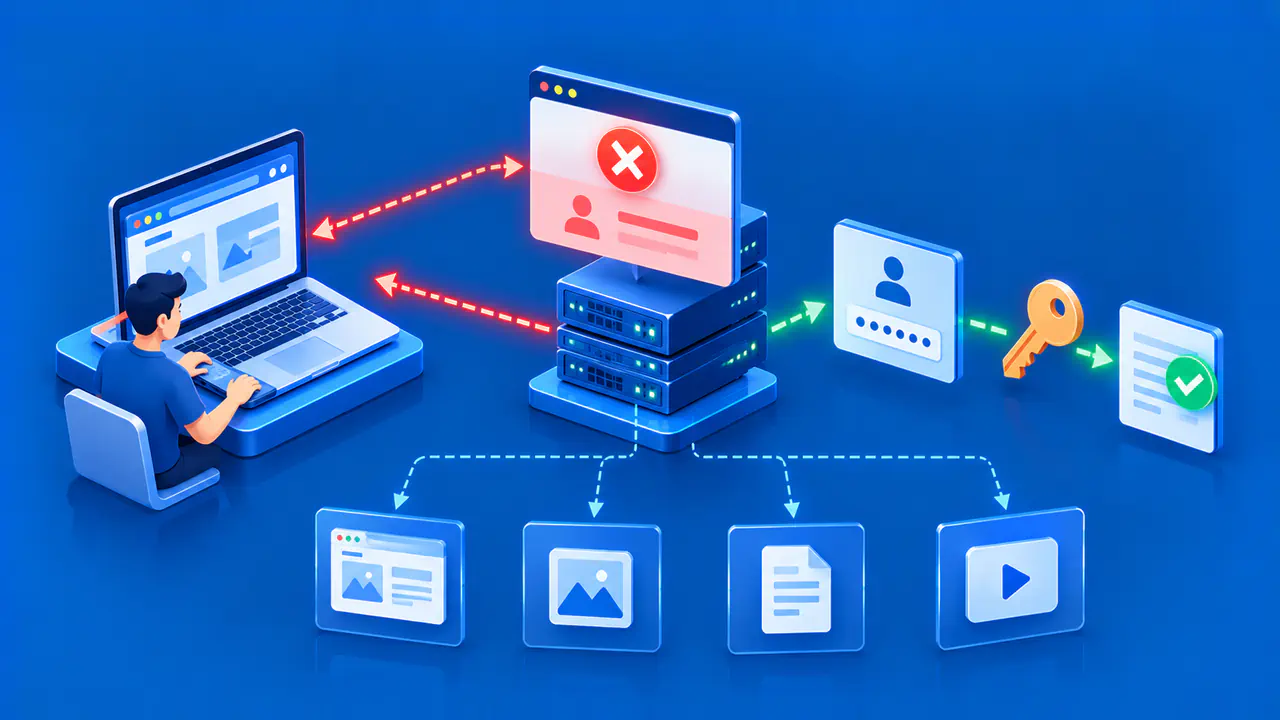
A 403 Forbidden response means the server understood the request but refuses to fulfill it. The practical fix depends on who controls access: a visitor can request the proper permission, while a site owner can examine the policy or configuration that denied the request. The status alone does not tell you which account, network, or rule caused the refusal.
The same status can appear for a private document, a public page affected by a bad rule, or an API action the account cannot perform. A denial may be intentional, so the aim is to restore the intended access without opening private content.
Confirm the Response and the Denied Resource
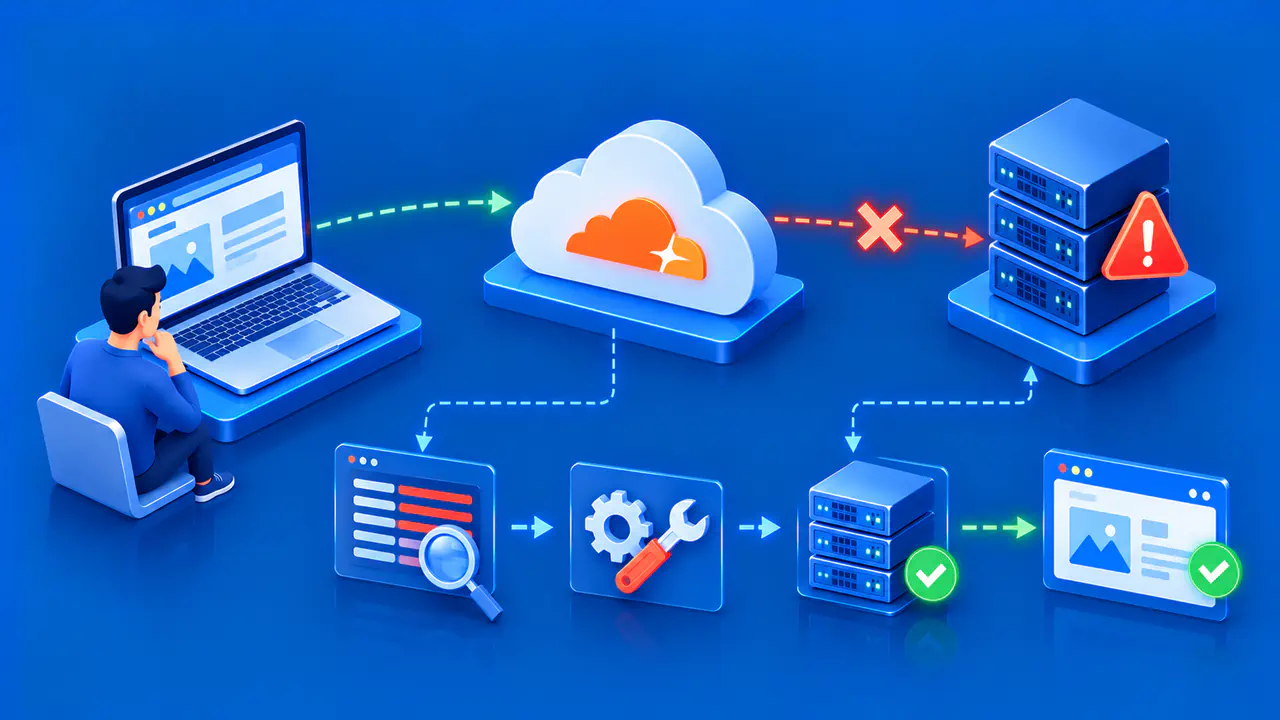
Use the browser's network tools or an API client to find the request that returned 403. Record its URL, method, and time with time zone. A page can contain several background requests, so identify whether the main document, an image, or an API endpoint was denied. Look for an explanation or request identifier in the response without assuming that an error page always names the responsible rule.
Compare the intended resource with the link that actually failed. An old bookmark may point to a private path, while a new public link may be available through the site's normal navigation.
Check the Account and Authorized Role
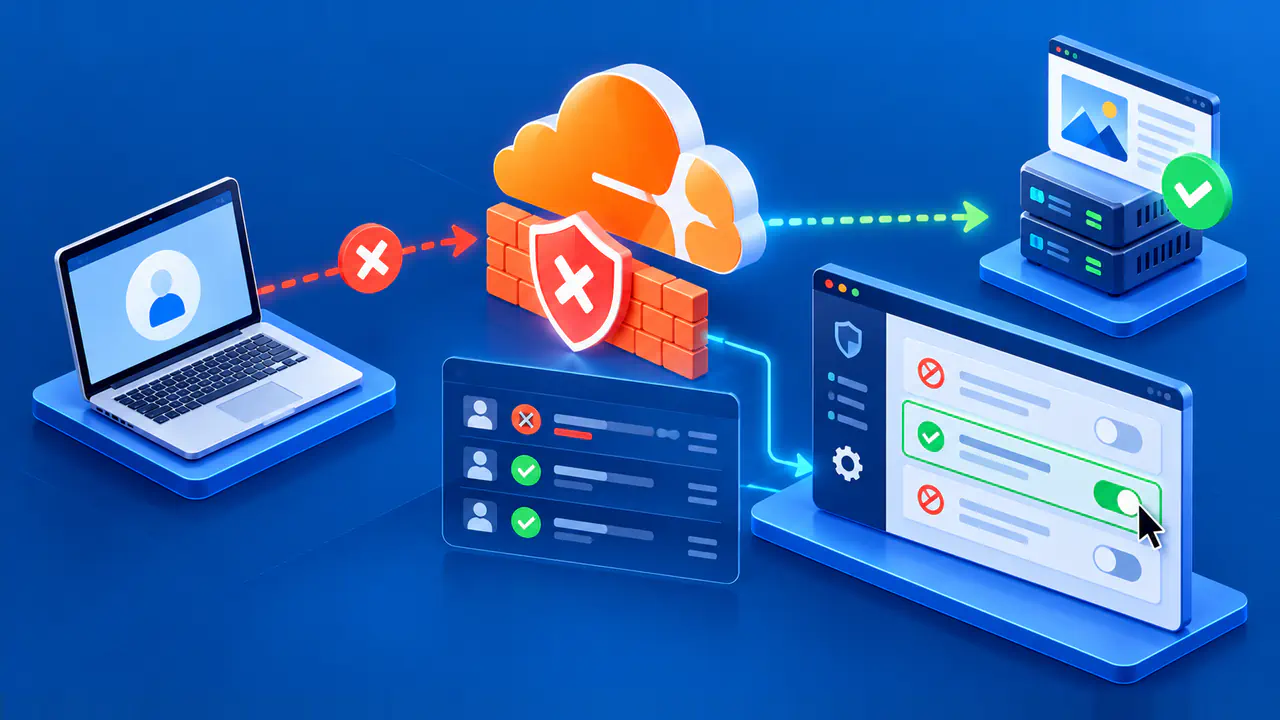
For a signed-in visitor, confirm that the account is the one meant to use the resource. An account used for personal work may lack permissions that belong to your organization's account. Sign in through the normal route and check whether the owner has granted the required role or subscription. If access is restricted to a group, request membership from the service administrator.
A successful login does not guarantee authorization for every action. A user may read a document but be denied an edit request, or view one project while another remains private. A 403 on one endpoint is not proof that an entire account was disabled.
For HTTP authentication, a 401 challenge asks the client for valid credentials. A 403 can instead reflect a policy that applies whether or not the visitor has signed in. Read the service's error details before assuming a password reset will help.
Find the Rule That Denied the Request
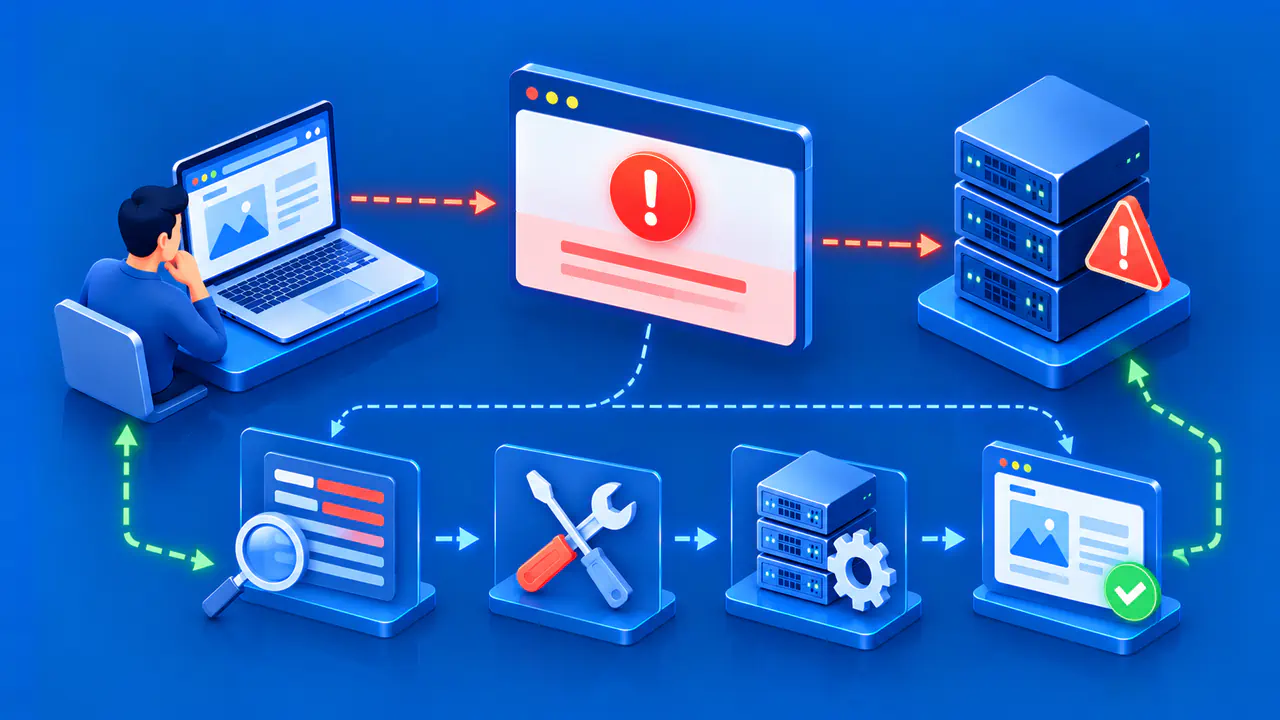
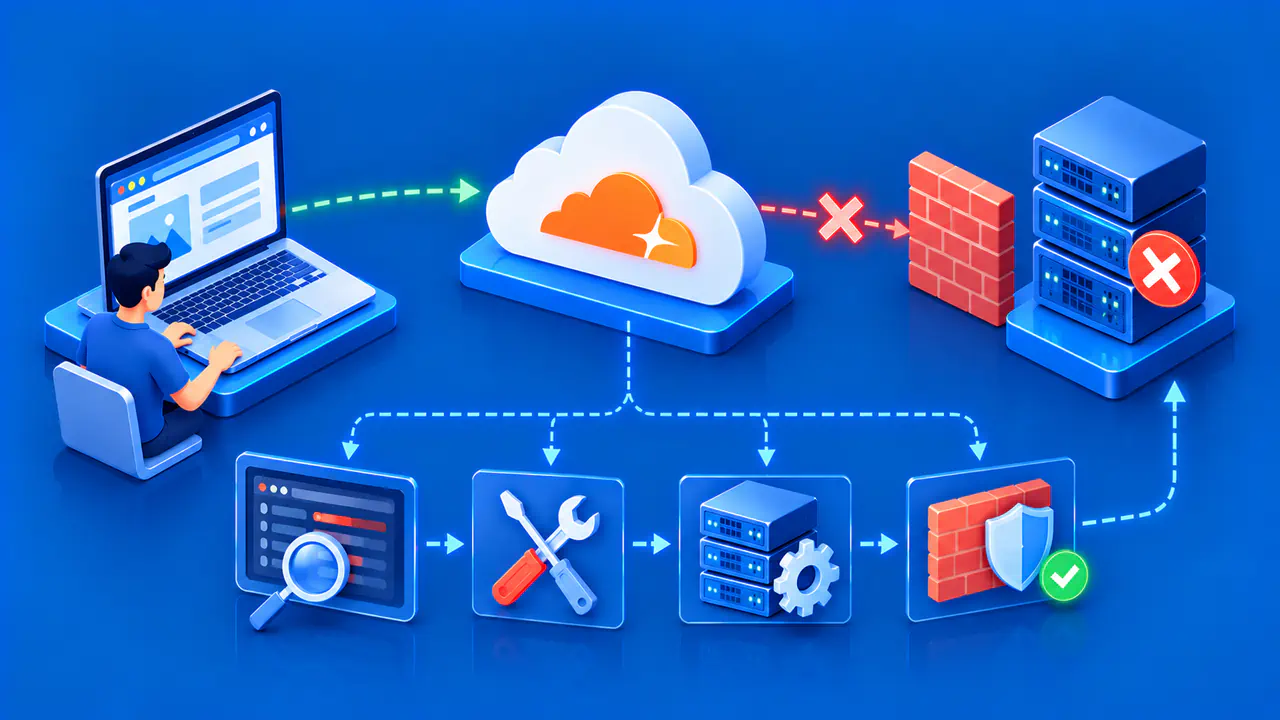
An application can deny a request because of resource ownership or an organization rule. A reverse proxy or security service can refuse it before the application receives it. Compare the logs from those components to identify which one returned 403; a 403 entry in a proxy log does not by itself show whether the proxy blocked the request or relayed the application's refusal.
Match the request identifier or timestamp with the relevant error or security event. If the logs identify a rule that blocked a permitted request, check the condition it matched, such as a route, HTTP method, or approved network. For example, if a proxy rule rejects traffic from an unapproved network, changing an application role will not satisfy that network rule.
If the failures began after a deployment, compare the relevant access settings with the previous configuration. Check whether the change affected the requested path or the account's assigned group. Correct the condition that conflicts with the intended policy, rather than disabling security checks across the site.
Check File Access on the Server
For content served from disk, check the server's error log before changing file permissions. An operating-system permission error and an access denial from a server configuration rule require different fixes. Find the actual file path used for the request, since the visible URL may be mapped to another directory.
On Linux, the web server's operating-system account needs permission to read a static file and search the directories leading to it. Check the file's owner, group, and applicable permissions, as well as the parent directories. Restore the intended access for that account; making every file writable by everyone is unnecessary and can expose the site to changes by other accounts.
Request Access or Correct the Specific Rule
If the resource is private by design, ask its owner for access using the site's normal process. Include the resource name, intended task, account identifier appropriate for support, and time of the refusal. The owner can confirm whether that account is eligible. A denial based on policy is not a browser defect, and clearing the cache will not grant an account a role it lacks.
When changing an application permission, grant the intended role access to the specific resource and action. For a server configuration change, save the previous setting and validate the updated settings using that server's documented procedure before applying them.
Verify the Intended Access
Retest with the authorized account and the exact resource after the owner confirms the change. Check that the expected content appears or that the intended action completes. The owner should also use a test account without that permission to confirm that private content remains unavailable.
If the visitor is still blocked, send the owner the time and identifier of the new request. The owner can compare the new and old events to see whether a second policy is involved. Use the service's support channel and remove passwords, session cookies, and private tokens from any shared example.