How to Fix Cloudflare Error 521
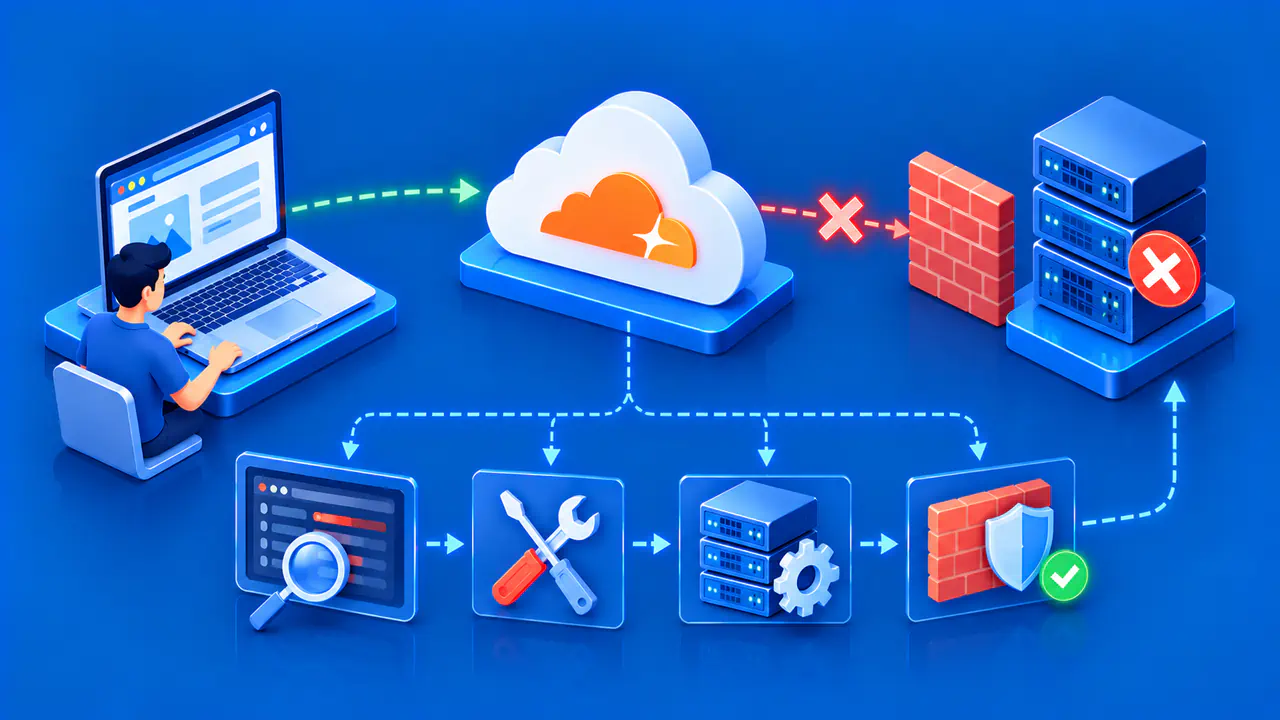
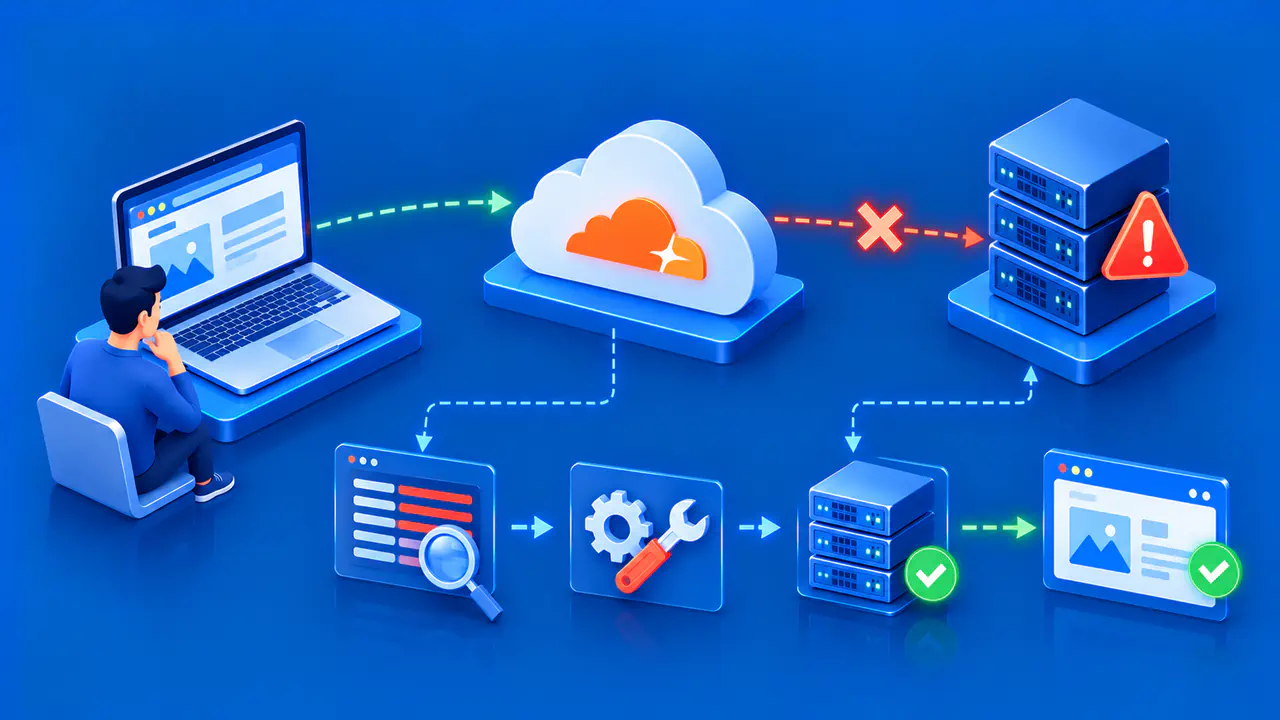
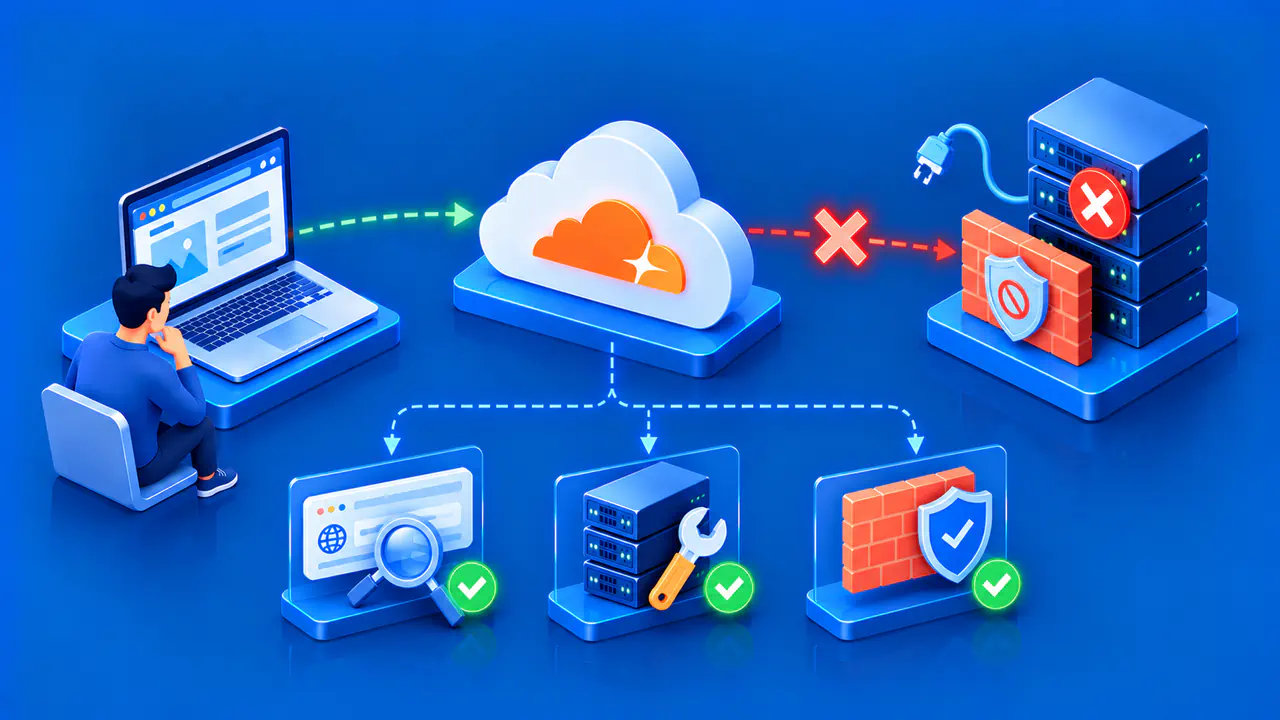
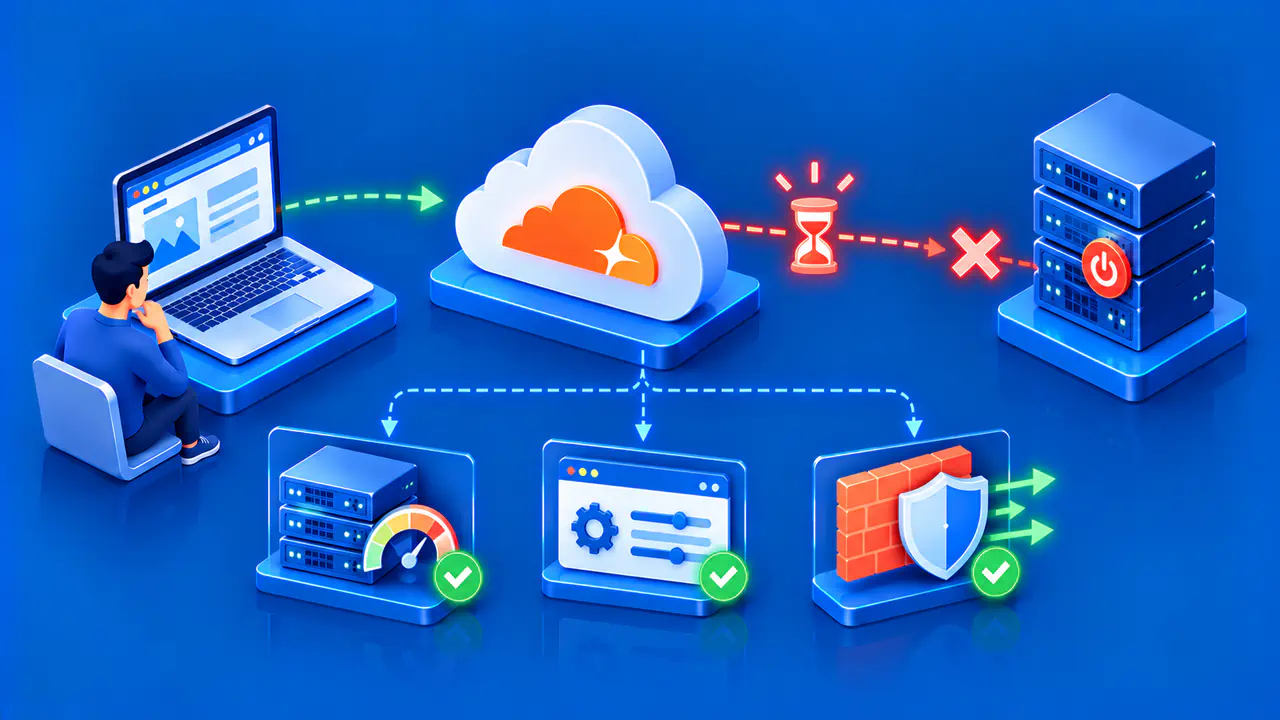
Cloudflare error 521 means the origin web server refused a connection from Cloudflare. The origin is the server hosting the website behind Cloudflare. The common causes are a stopped web service and security rules that reject Cloudflare connections.
Site owners can fix a 521 by restoring the web service on the correct port or correcting the rule that blocks Cloudflare. A visitor can report the affected URL and time to the site owner. Browser settings cannot restore a stopped service or change the origin's firewall.
Check Whether the Origin Is Listening
Record the URL, error code, time with time zone, and any Cloudflare Ray ID shown on the error page. The Ray ID helps the owner match a report to request records. Confirm that the origin address configured for the hostname matches the server assigned by the hosting provider. If the site moved recently, check for an old address still being used.
Check the web service in the hosting panel or the server's service manager. A running server does not necessarily have a working listener, which is the web service accepting connections on a particular address and port. Examine its error logs for a failed start, an address or port already in use, or a crash after a deployment.
Confirm that the listener is bound to an interface reachable from Cloudflare, rather than only accepting connections from inside the host. A successful local application check does not establish that Cloudflare can reach it. If the service stops intermittently, compare the failure times with restarts, configuration changes, and resource use.
If the hostname uses multiple origin instances, check each one that can receive its traffic. A successful response from one instance does not rule out an unavailable listener on another. Use the load balancer's health checks and connection logs to identify the affected instance before restarting services or changing access rules.
Confirm the Port for the Configured TLS Mode
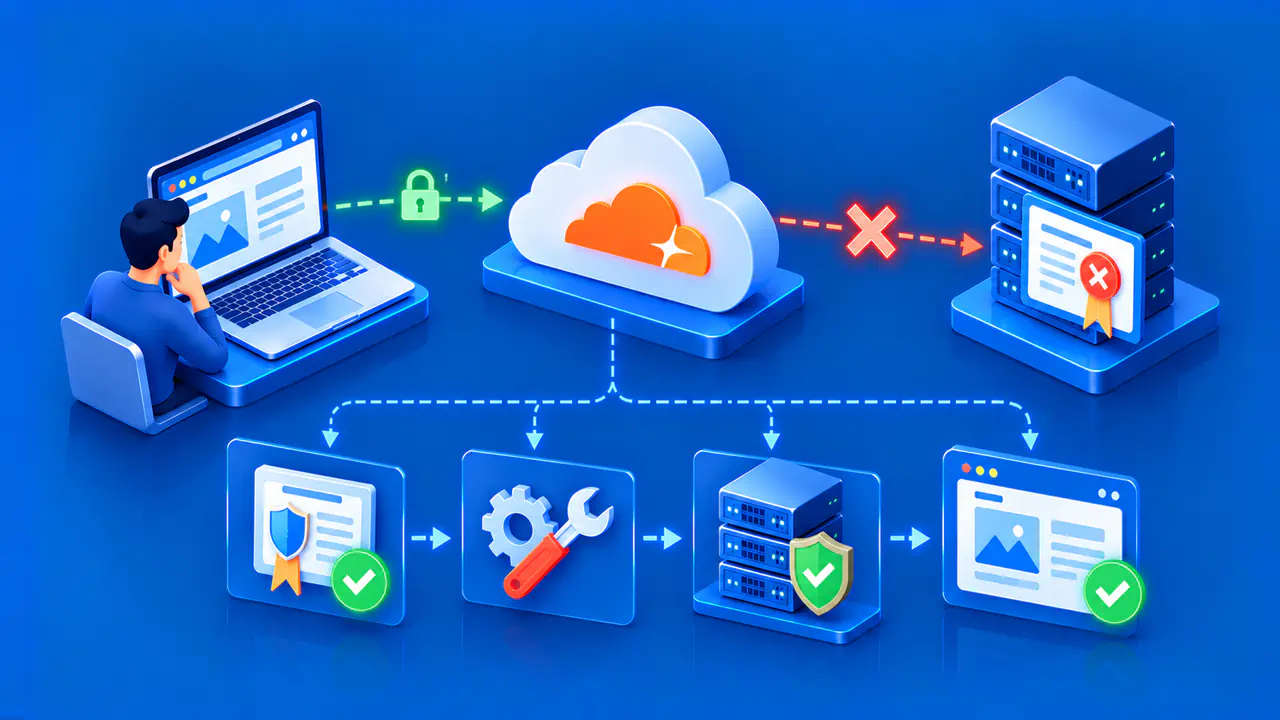
For an HTTPS request on the default port, Flexible mode normally connects to the origin over HTTP on port 80, while Full and Full (Strict) use HTTPS on port 443. These are default examples, not universal port assignments. Check the request's scheme and port, the active encryption mode, and any Origin Rule that overrides the destination port.
In Full mode, an HTTP request also uses HTTP to the origin unless another setting changes that behavior. Cloudflare supports several additional proxy ports, and Flexible falls back to Full for HTTPS on ports other than 443. The useful test is whether the origin accepts the connection Cloudflare actually attempts, not whether an unrelated port is open.
When the origin connection uses HTTPS, the server must support TLS and present a certificate appropriate for the selected mode. If the listener accepts connections but a handshake or certificate error appears, investigate that specific error. Lowering the encryption mode can hide a configuration mismatch while leaving the origin connection less protected.
If a load balancer accepts the public connection and forwards it to an application on another internal port, inspect both stages. Its external listener may be available while forwarding to the application fails. The resulting error depends on how that load balancer handles the failure, so use its logs rather than treating every backend problem as a 521.
Review Blocks and Rate Limits on Cloudflare Connections
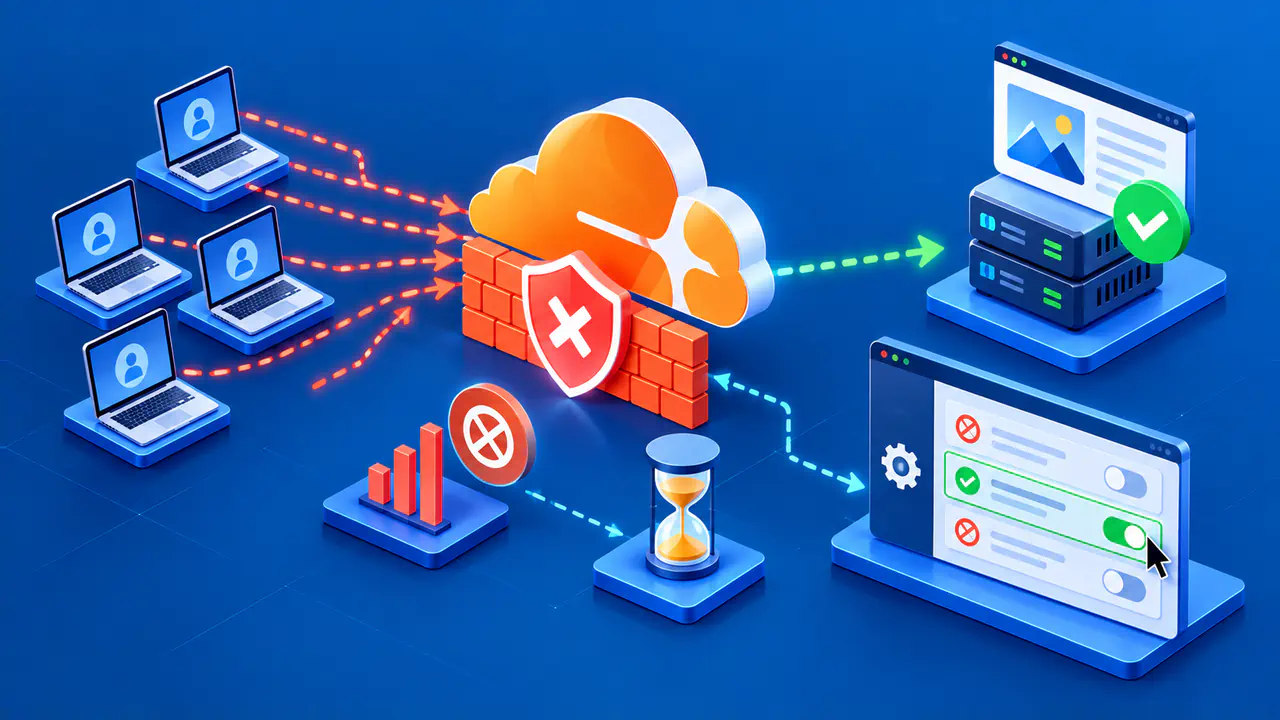
Inspect the origin firewall, hosting provider controls, and web server security software for rejected Cloudflare connections. Compare logged source addresses with Cloudflare's current published IP ranges. The connection reaching the origin comes from Cloudflare's network, even when the request carries the visitor's address in an HTTP header.
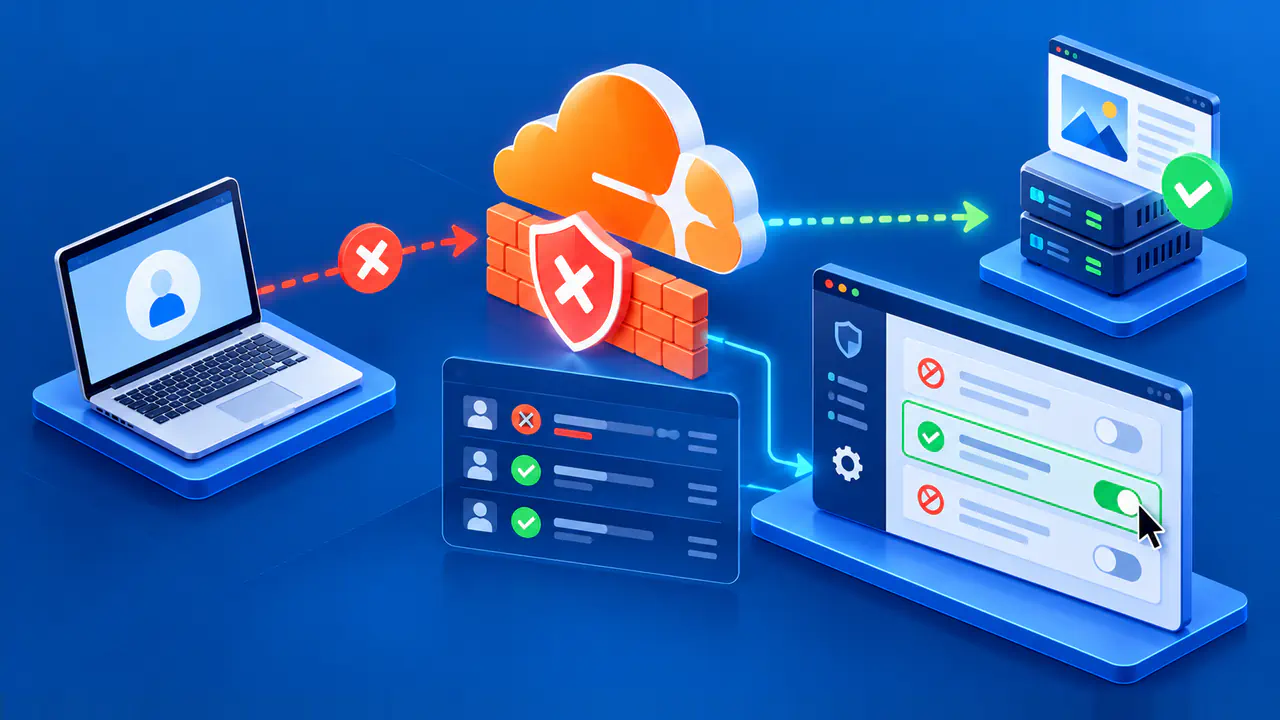
Check that the origin's allowlist includes all current Cloudflare ranges needed for the connection. A partial or outdated list can explain why some requests succeed while others fail. If a rate limit rejects legitimate connections, adjust that specific rule and retain the protections that apply to other traffic.
Provider-level filtering can reject a connection before the server's own firewall records it. If the listener is healthy and local controls show no matching denial, ask the host to inspect its network security records. Provide the time, destination address and port, and error details with private information removed. An absent application log entry does not identify the refusing component.
Restore the Failed Service or Correct the Blocking Rule
Apply the correction supported by the logs. Restore a stopped web service using the hosting panel or service manager, fix its address or port binding, or update the rule rejecting Cloudflare traffic. If a configuration deployment caused the failure, correct or roll back that change using the site's deployment process.
Record the previous setting and the time of the correction so another failure can be compared with the change. Restarting a service may restore access temporarily without resolving the reason it crashed. Check its startup messages and subsequent errors before concluding that the repair will hold.
Keep the origin's access restrictions in place after it responds again. If the site is designed to reject direct connections that bypass Cloudflare, verify that this restriction still works. Allowing connections from every source address or disabling the whole firewall unnecessarily exposes the origin to other traffic.
Verify a Request through Cloudflare
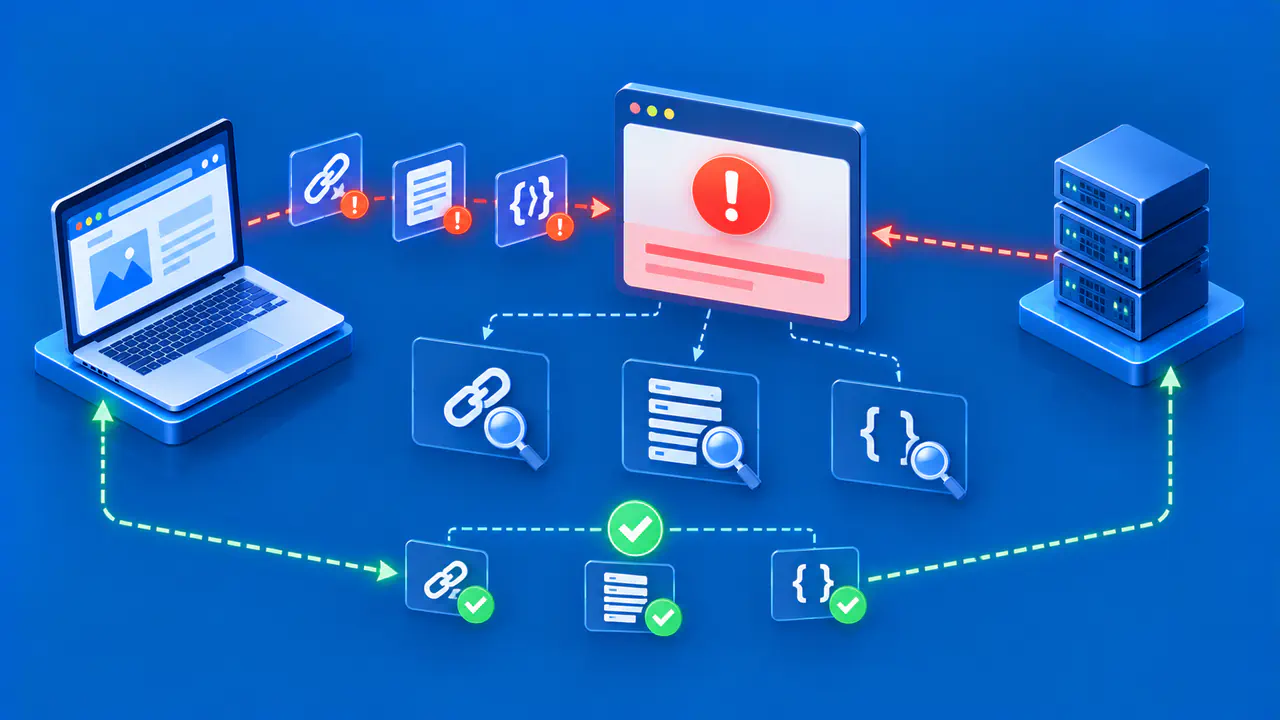
Request the affected URL through the normal Cloudflare-proxied hostname after the correction. Confirm that the expected content and status arrive, then match the successful request to the origin logs where available. Check the instances and conditions involved in an intermittent failure. For a form submission that changes data, confirm whether the original operation completed before repeating it.
Continue watching web server errors and security denial events for the same connection pattern. If a 521 returns, record the new time and Ray ID and compare them with the earlier event. Cloudflare 522 instead indicates a timeout while contacting the origin, so preserve the actual code when reporting a new failure to the host.