How to Fix a Domain Name Mismatch in TLS
A TLS domain name mismatch means the certificate presented by a server does not identify the name the client intended to reach. The warning can appear even when the certificate is current, signed by a trusted authority, and correctly installed for some other hostname. Start with the hostname in the URL, inspect the certificate the server sends, and check which server configuration selected it.
Do not weaken hostname verification to make a warning disappear. That removes a check that distinguishes the intended service from a different endpoint. The fix depends on whether the URL is wrong, the certificate lacks the required name, or the server is presenting the wrong certificate.
Capture the Exact Hostname in the URL
Record the hostname as it appears in the address bar, including whether it has a www prefix or another subdomain. For an HTTPS URL containing a domain name, the browser checks that name against the certificate. A redirect can move the browser to a new hostname; check the name where the warning occurs, not just the name originally typed. A certificate for www.example.com does not automatically cover example.com.
If the URL uses a literal IP address, the certificate needs a matching IP address identifier in its Subject Alternative Name extension. A DNS name that resolves to that address is not a substitute for an IP identifier. If a visitor accidentally used the wrong URL, correcting that input may resolve the warning. If the intended published URL is right, the site operator must repair the endpoint.
Inspect the Certificate Actually Served
Inspect the leaf certificate from the public TLS connection for the affected hostname. Read its Subject Alternative Name entries and compare them with the exact URL host. Modern HTTPS clients require a matching SAN entry. A Common Name field does not replace a missing or incorrect SAN. Confirm that the certificate observed is from the same CDN edge, load balancer, or server that affected users reach.
For a normal DNS name, a relevant DNS SAN must match the full name or a valid wildcard pattern. A wildcard such as *.example.com can match shop.example.com, but it does not match the apex example.com or a deeper name such as api.shop.example.com. The wildcard must occupy the entire leftmost label, with no other wildcard elsewhere in the name. If the served certificate already contains the intended name, investigate whether the client saw another endpoint, an old certificate, or a different warning category.
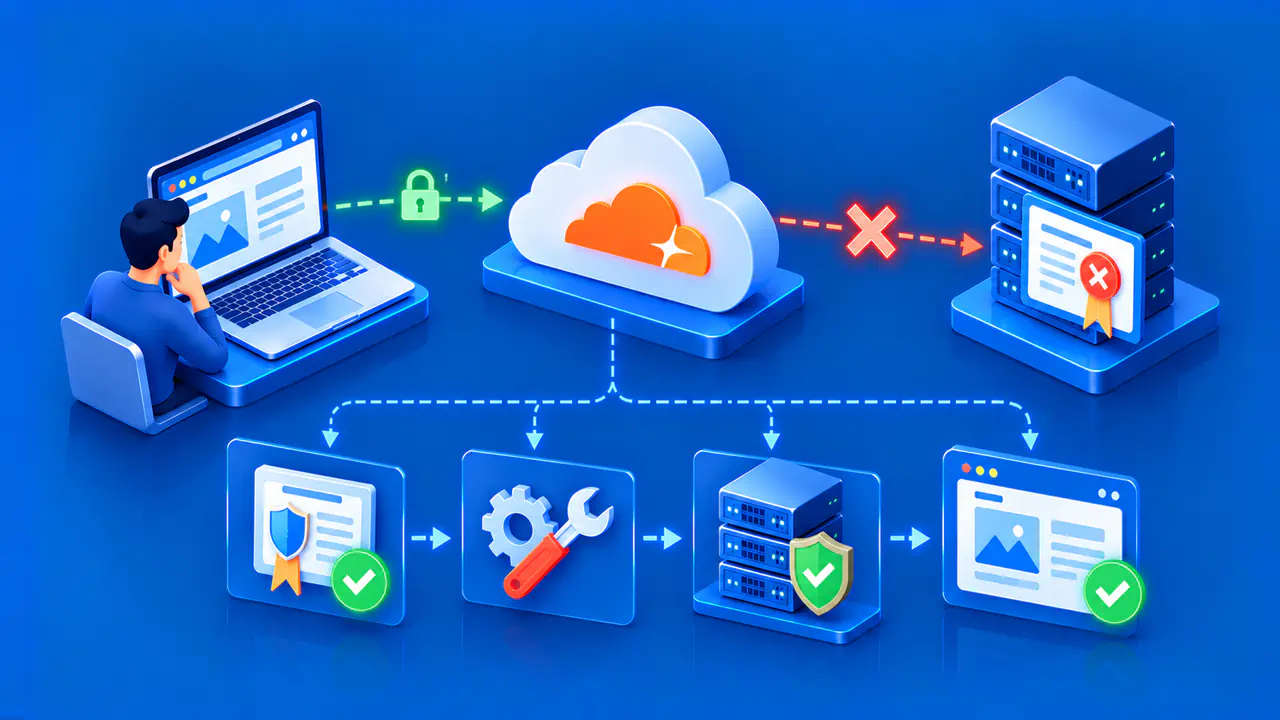
Do not compare only files on disk. A server may have a replacement certificate stored but still serve an older one because the process was not reloaded. A CDN may serve its own edge certificate while the origin has a correct certificate. Check the endpoint visible to the client, then work backward to its configuration.
Trace SNI and the Default Server
Server Name Indication, or SNI, lets a client signal the requested DNS hostname during the TLS handshake. A server hosting several HTTPS names on one address can use that signal to select a certificate. Without a usable SNI name or a matching TLS virtual host, it may present the default server's certificate. Because TLS begins before the HTTP request, changing only an HTTP routing rule may not change the certificate chosen during the handshake.
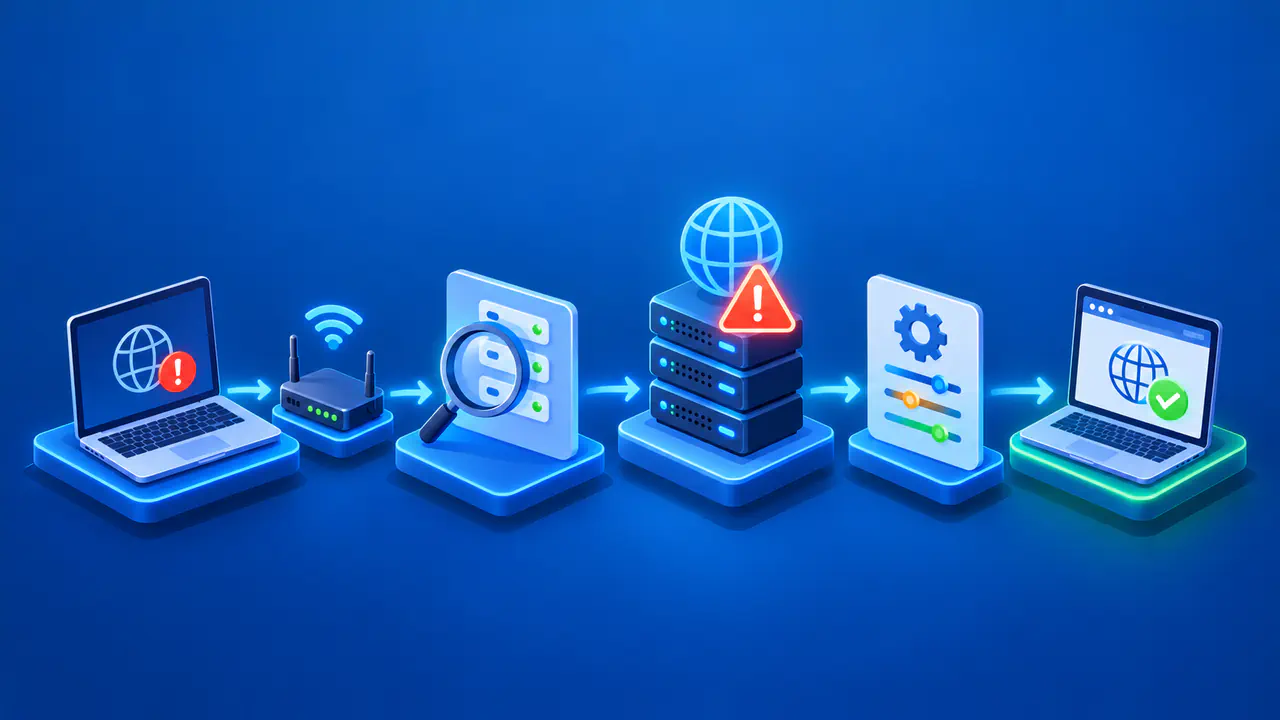
Check the public DNS records, port, CDN proxy status, listener, SNI hostname, and virtual host or certificate mapping in sequence. One possible cause is a hostname resolving to a shared endpoint whose default certificate belongs to another site. A newly added subdomain may be absent from the proxy's certificate map. The IPv4 and IPv6 addresses for the same hostname may lead to differently configured servers. A test without the intended SNI name can misleadingly show a default certificate even if normal browser connections receive the correct one.
For a URL containing a literal IP address, SNI is not the way to request a certificate for that address. The SNI HostName field permits DNS hostnames, not literal IPv4 or IPv6 addresses. The endpoint still needs a certificate with the matching IP SAN and a configuration that presents it for the relevant connection.
Correct the Certificate or Server Configuration
If the intended hostname is absent from the certificate at the right endpoint, request or deploy a certificate whose SAN set covers that exact name. Certificate issuance requires validation of control over the requested name, using a method accepted by the certificate authority. A certificate for a different hostname does not fix the mismatch, even if both hostnames are under the same domain. Include both apex and www names if both are intended public URLs, or configure a redirect only after the initial TLS connection can be authenticated.
If the correct certificate exists but the wrong one is served, update the SNI or default-server mapping on the server, proxy, or load balancer that handles the TLS connection, then reload or deploy through that product's supported process. Review each relevant edge or load balancer, not only the origin. Preserve key permissions and avoid copying a private key into logs or tickets. In a managed CDN setup, the provider may control certificate issuance and edge selection; use its documented configuration rather than changing an unrelated origin server.
Verify the Public Result
After the change, connect to the exact public hostname and inspect the certificate served with that name selected. Compare the SANs and check the other normal TLS validations, including chain and validity dates. Repeat the checks for the apex, www, and other affected hostnames. Test both IPv4 and IPv6 when the site supports them. A successful browser visit to one hostname is not proof that every route is fixed.
If the mismatch persists, record the connected IP address and the certificate fingerprint at the time of failure. Compare that fingerprint with the fingerprint of the certificate you intended to deploy. Do not ask visitors to click through the warning, install an unknown root, or disable identity checks.