How to Fix Cloudflare SSL Errors 525 and 526
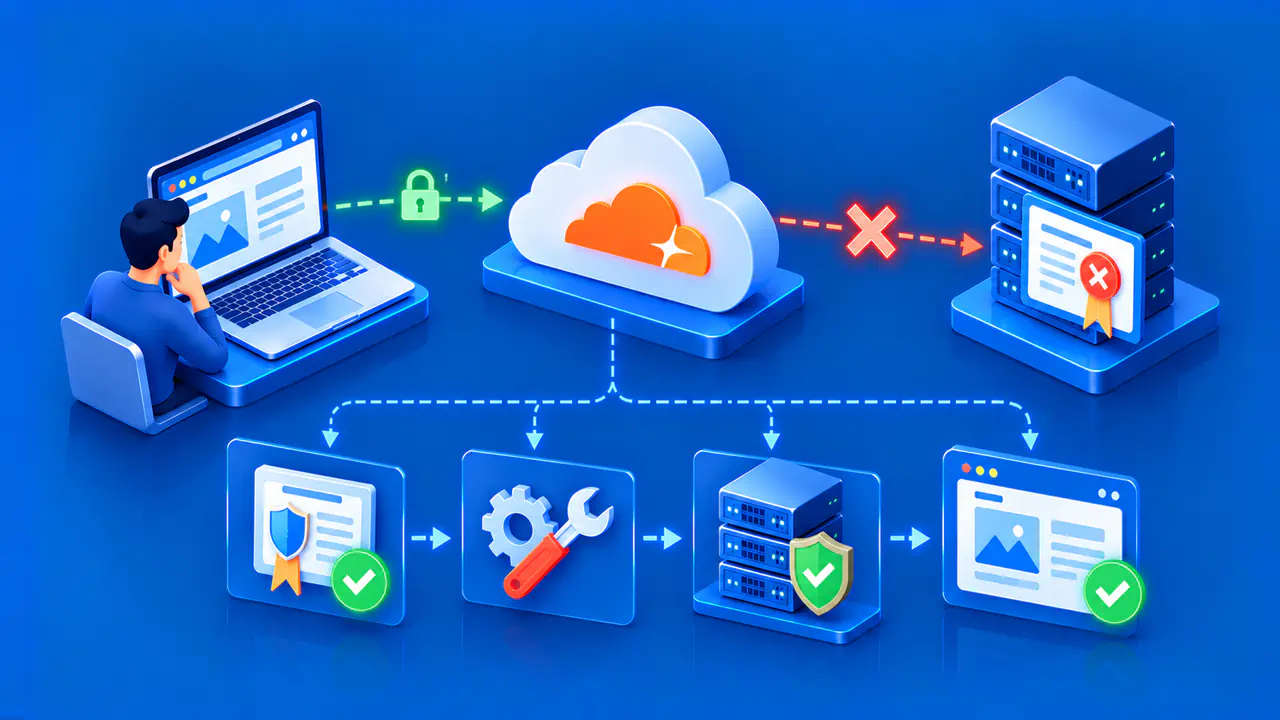
Cloudflare errors 525 and 526 both concern the secure connection between Cloudflare and the origin server hosting the site, but they identify different failures. Error 525 means the TLS handshake with the origin failed. Error 526 means Cloudflare could not validate the certificate presented by the origin under strict validation. Distinguishing the two errors helps you choose between investigating TLS negotiation and checking certificate validity.
Record the exact error, affected hostname, URL, and time with time zone. Check the zone's current SSL/TLS encryption mode and identify which origin service handles that hostname. These details matter when several servers, load balancers, or certificates sit behind one site. Work on the origin side of the connection; a browser certificate warning on the visitor side follows a different diagnostic path.
Read the Error and the Active TLS Mode
For a proxied website using Full or Full (strict), a failed TLS handshake with the origin can produce Error 525. Error 526 occurs when Cloudflare cannot validate the origin certificate with Full (strict). For HTTPS requests, Full (strict) encrypts the origin connection and verifies the certificate; Full encrypts without verifying the certificate's validity. Encryption alone does not establish that the server's certificate is trusted or valid for the requested hostname.
Confirm the mode that actually applies to the affected hostname, including any configuration rule that sets a different mode for a subset of requests. Note any recent origin move, certificate renewal, load balancer change, or TLS policy change near the first failure. Do not change the mode merely to make the error page disappear. A lower validation setting can conceal the certificate defect that needs repair.
For Error 525, Check the Origin Handshake
Start with the HTTPS listener at the origin. Verify that the intended server or load balancer accepts TLS on port 443 or on the custom secure port configured for that origin. Check that a certificate is installed on the service Cloudflare reaches. If the listener is absent or the connection is reset during negotiation, Cloudflare cannot complete the handshake regardless of whether a different service on the machine is healthy.
Inspect the origin's TLS error logs at the failure time. Look for rejected protocol versions, cipher-suite mismatch, connection resets, or an SNI-related virtual host mismatch. Server Name Indication (SNI) carries the requested server name during TLS negotiation, allowing a shared server to select the matching certificate and configuration. If there are several origins, compare a failing member with a working one; an intermittent 525 may come from only part of the pool.
A certificate being present in a control panel is not enough if the active listener serves a different configuration. Test the exact origin endpoint with the expected server name supplied for TLS, and record any negotiation error. A test that connects only by IP address may select a default virtual host and show a different certificate.
For Error 526, Validate the Certificate
For Error 526, check whether the certificate presented by the origin is valid at the time of the request. A certificate can fail this check if it has expired or its validity period has not yet begun. Confirm that its Common Name or Subject Alternative Name covers the requested or target hostname. A certificate for a neighboring subdomain does not automatically cover the affected name.
Next verify the issuer and the complete chain served by the origin. By default, Full (strict) accepts certificates from publicly trusted certificate authorities or Cloudflare Origin CA, provided the certificate meets the hostname and validity requirements. A public certificate may fail validation if the origin omits a required intermediate certificate, even when the server certificate looks correct in a local file. Also check any revocation or trust error reported by the service that validates the origin certificate.
Inspect the certificate actually presented by each origin endpoint. Renewal may have updated a file on disk while a load balancer or web server continues serving an older certificate, and different nodes may present different chains. Also confirm that SNI selects the intended certificate for the hostname. Record the presented subject, issuer, validity dates, and chain without exposing private key material.
Repair the Origin Configuration
For a handshake failure, fix the listener or TLS compatibility problem identified in the logs. Depending on the cause, you may need to enable HTTPS on the correct listener, install the certificate on the active virtual host, correct the SNI mapping, or restore a supported protocol and cipher configuration. Apply the fix to the affected origin or virtual host. Avoid weakening TLS settings across the whole site to work around a problem at one origin.
For a validation failure, install a certificate that covers the hostname and is trusted under the chosen strict mode. Serve the required intermediate certificates in the correct chain and remove stale certificates from active endpoints. A Cloudflare Origin CA certificate is an option when the origin is meant to be reached through Cloudflare; a publicly trusted certificate is appropriate when direct browser trust is also required. If Custom Origin Trust Store is configured, check its uploaded CAs: they replace the default publicly trusted CA list, so a public certificate is not automatically accepted. A self-signed certificate also needs an explicitly configured trust arrangement.
Coordinate with the hosting provider if they operate the listener, certificate deployment, or load balancer. Give them the exact error code, hostname, timestamp, current mode, and evidence from the relevant TLS endpoint. The endpoint evidence helps distinguish a negotiation failure from a failure to validate the certificate the server presents.
Retest with Validation Intact
After the repair, request the affected hostname through Cloudflare and confirm the expected site response. Keep Full (strict) where the origin is configured to meet its requirements, and check that the certificate presented by every applicable origin is valid for the hostname. If the failure was intermittent, sample requests long enough to cover the affected members or traffic pattern.
Review new TLS errors and confirm that neither 525 nor 526 reappears. Do not treat a successful page load after disabling certificate validation as proof that the original trust problem was fixed. Confirm both that the handshake succeeds and that the origin certificate passes the intended validation checks.