What Is CIDR Notation?
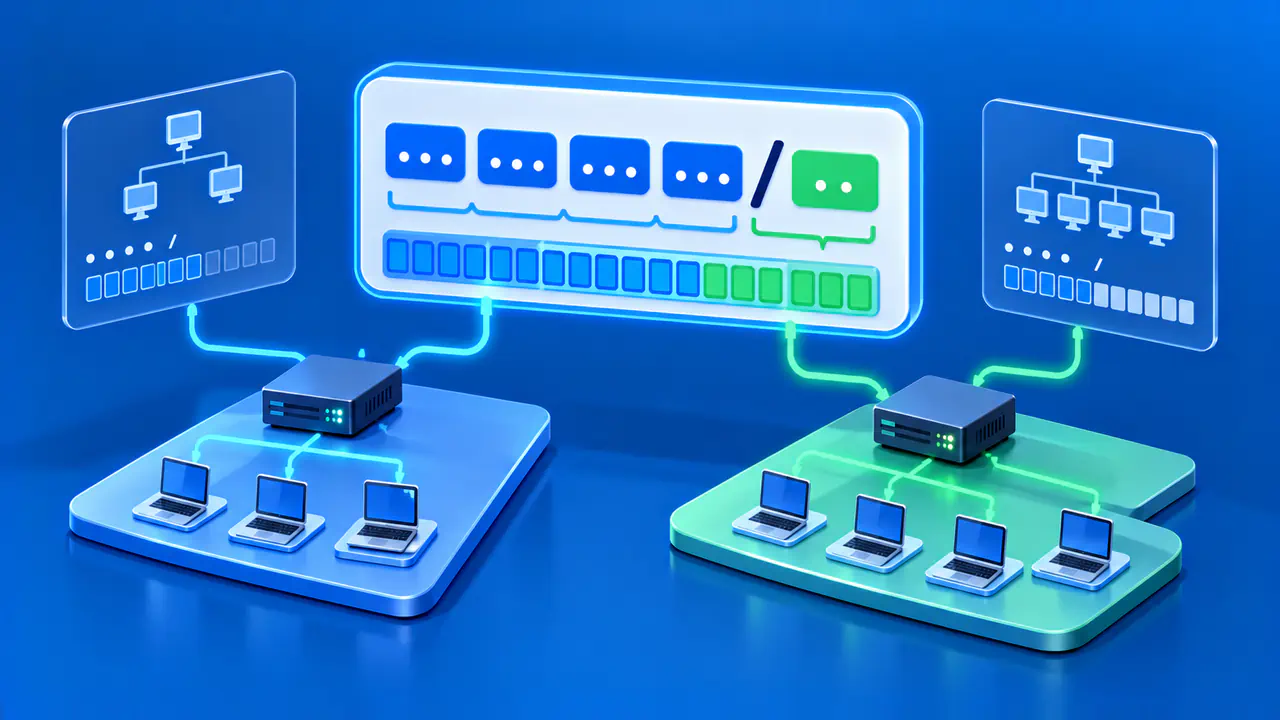
CIDR notation writes an IP address followed by a slash and a number, such as 192.0.2.0/24. The number tells you how many leading bits belong to the prefix. Those fixed bits define an address block; the remaining bits vary within that block. CIDR stands for Classless Inter-Domain Routing, a way to describe address ranges without relying on old fixed network classes.
The slash number is a length, not another address. Reading it correctly helps you understand network plans, route entries, firewall rules, and device settings. It does not by itself tell you whether a particular address is assigned, reachable, or publicly routed.
Read the Address and Prefix Length
Start with the address family. An IPv4 example has four dotted decimal parts, such as 192.0.2.0/24. The /24 means the first 24 of 32 IPv4 bits are fixed as the prefix. An IPv6 example uses colon-separated hexadecimal groups, such as 2001:db8:1:2::/64. Here the first 64 of 128 IPv6 bits are fixed.
In IPv4, the slash number ranges from 0 through 32. The same slash-length idea is used with IPv6, where valid lengths run from 0 through 128. A larger prefix number fixes more bits and therefore describes a smaller address block within the same address family. For example, an IPv4 /25 is a smaller block than the /24 that contains it.
Do not interpret the slash value as a count of devices. The possible address count follows from the bits left after the prefix, but assignment and usable endpoint rules depend on the network and address type. A route may describe a block even if no device currently uses a particular address in it. This distinction matters when reading a list of allocated ranges: the range is a planning or routing unit, not an inventory of active computers. A single device may also hold more than one address, so counting the written blocks will not reliably count devices.
Network Bits and Address Blocks
Think of a prefix as a test: addresses belong to the same block when their leading bits match the prefix for the specified length. In 192.0.2.0/24, the first three decimal octets stay the same and the last octet can vary from 0 through 255. That gives 256 IPv4 bit patterns in the block. The number of addresses assignable to ordinary hosts can differ because of network and broadcast conventions or special prefix rules, so do not equate 256 with 256 usable devices.
An address such as 192.0.2.37/24 combines a particular host address with its /24 prefix length. The containing block is 192.0.2.0/24. Some interfaces and tools accept the host-plus-prefix form, while route tables usually show the normalized network prefix. The first form identifies a host address within the /24, while the second names the block itself.
CIDR permits blocks of different sizes and supports route aggregation. A network operator can announce or manage a larger prefix instead of listing each smaller block separately when the routes actually share a path. This is one reason classless prefixes helped address allocation and routing scale. Aggregation is a routing decision, however, not a claim that all addresses in a block belong to one machine or one customer.
IPv4 and IPv6 Examples
The block 192.0.2.0/24 is reserved for documentation. It contains 192.0.2.37 because the first 24 bits match. An address beginning 192.0.3. is outside that /24. If the prefix were 192.0.2.0/25, only last-octet values 0 through 127 would belong to that particular /25; the other half belongs to the next /25 block.
The IPv6 example 2001:db8:1:2::/64 fixes the first four 16-bit groups. An address such as 2001:db8:1:2::5 shares that /64 prefix. An address whose fourth group is 3 would not. The broader 2001:db8::/32 range is reserved for documentation, so these examples are explanatory rather than claims about live systems.
IPv4 has only 32 bits, so /64 cannot be an IPv4 prefix length. Even a slash number that is valid for both families does not describe equally sized blocks: /24 leaves eight varying bits in IPv4 and 104 in IPv6. Identify the address family before comparing block sizes.
Prefix Notation versus Host Configuration
When a device setting asks for an IP address and prefix length, it needs an assigned address for that interface and the boundary of its local network. Entering only a network block such as 192.0.2.0/24 may not provide a valid individual device assignment. The gateway and DNS server are separate settings where required. Use values from the network plan rather than copying documentation examples.
A firewall rule or route entry uses a prefix differently: it may match or direct traffic for every address in a block. A /32 in IPv4 or /128 in IPv6 names one exact address as a prefix, while a shorter length may cover many addresses. That is why a misplaced slash number in a rule can affect a much broader scope than intended.
For example, replacing 192.0.2.0/25 with 192.0.2.0/24 in an IPv4 source-address rule expands the matched range to include 192.0.2.128 through 192.0.2.255. Whether that traffic is permitted depends on the rule's action and its other conditions. A valid prefix length can still describe the wrong range, so check the complete prefix rather than just the address before the slash.