How to Automate TLS Certificate Renewal
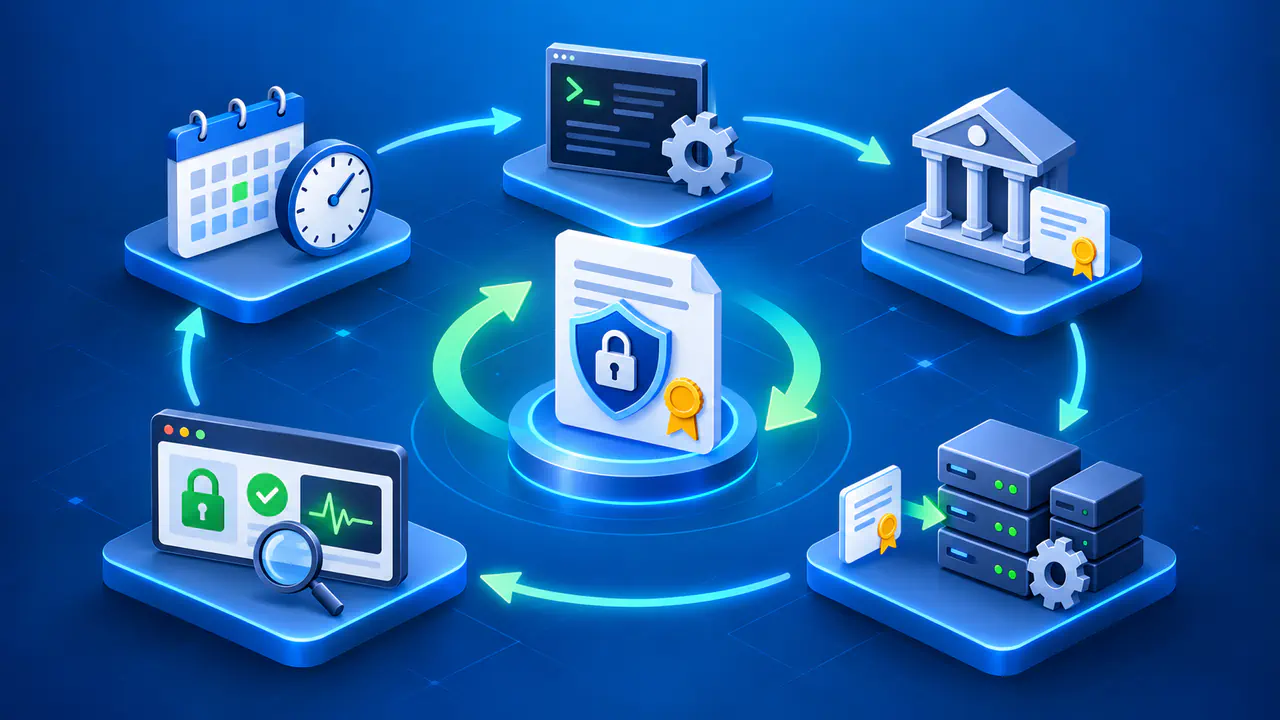
An ACME client can obtain a replacement TLS certificate when renewal is due, validating control of its identifiers when required. Automation also needs a way to deploy that certificate and check what visitors receive. Issuance can succeed while a proxy continues to serve the old certificate.
Choose an ACME client supported by the certificate authority and by the server or DNS provider used for validation. The Certbot examples below apply to version 5.8.0; commands, scheduling, and hooks differ for other clients. Check the installed client version and deployment environment before applying a procedure.
Configure the Renewal Client and Schedule
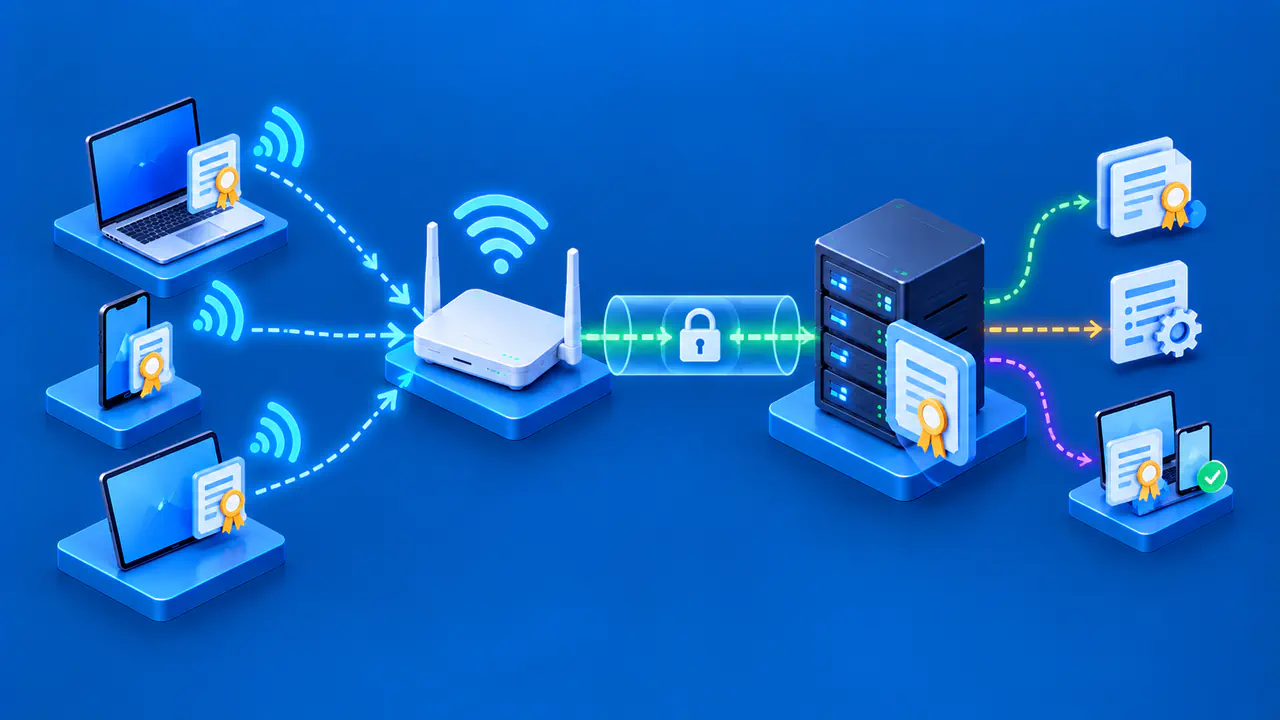
First identify every certificate and the identifiers it covers. Confirm that the client retains its account, renewal configuration, and authentication method. An HTTP challenge needs a reachable web path; a DNS challenge needs controlled DNS updates. Certbot's manual authenticator needs an authentication hook for unattended renewal. If a certificate is installed on multiple machines or at a CDN edge, document which systems need the replacement certificate and key.
The certbot renew command checks managed certificates and attempts renewal when they are due under the client's policy. Many installations already include a periodic system timer or task. Inspect the existing schedule before adding another one, including which client installation and configuration it uses.
If no suitable renewal task exists, configure a timer or scheduled task to run the renewal command periodically. Confirm that the command finishes without interactive prompts under an account with the permissions needed for renewal. Preserve the client's configuration across upgrades and server rebuilds so the scheduled task can continue to use it.
Do not hard-code a universal 90-day lifetime or a fixed 30-day renewal threshold. Certificate lifetimes and client policies can change. Certbot's renewal rules include thresholds based on the remaining fraction of a certificate's lifetime. ACME Renewal Information, or ARI, lets supporting clients use a certificate authority's suggested renewal window. Schedule the client often enough to act within its own policy, then monitor the actual expiry independently.
Test Renewal Behavior Safely
After configuring validation and the schedule, use the client's supported test mode to exercise the future renewal path. For a standard Certbot setup, certbot renew --dry-run uses the Let's Encrypt staging service and tests whether renewal can complete without saving a production replacement. Check the output for each certificate, the chosen authenticator, and the challenge path or DNS record. A successful dry run does not prove that the production service was reloaded or that the public endpoint now serves a new certificate.
A custom ACME server set through --server on the command line or in Certbot's global configuration can override the staging target for a dry run. Such a test may cause a real certificate to be issued and discarded. Review the effective server setting before testing.
A Certbot dry run can run pre and post hooks by default, and a web server plugin may temporarily change configuration and reload the server. Deploy hooks are skipped unless --run-deploy-hooks is enabled. With that option, deploy hooks run only after a successful dry run and use the current active certificate, not the temporary test certificate. Review the actions each hook performs before testing it.
Deploy and Reload the Correct Service
Plan the action that must happen after a successful renewal: copy the certificate and key to an approved location if needed, update a secret store or load balancer, and reload the exact service that terminates TLS. Do not assume that a fresh file on one host changes a CDN edge or a separate proxy. Map each hostname to its public TLS terminator and the certificate path it actually reads.
For Certbot, a deploy hook runs after a certificate is successfully issued or renewed. Use a deploy hook for a reload that depends on a new certificate. A post hook can run even if renewal fails. A zero exit status can also mean that no certificate needed renewal, so it does not prove that a new one was deployed. Write hooks so rerunning them leaves the intended deployment intact, inspect their results and logs, and keep credentials out of command output.
Keep private keys readable only by the services and administrators that require them. If a hook copies key material, use protected transport and destination permissions. A reload command should target the service using the renewed certificate, not every server on the machine. On a cluster, track renewal and deployment for every serving node so each presents a valid certificate for its hostnames before the previous certificate expires.
Check the Certificate Actually Served
After a production renewal, inspect the public TLS endpoint for each hostname, including its IPv4 and IPv6 endpoints where applicable. When connecting directly to a specific IP address, send the intended hostname as the TLS server name so the server can select the appropriate virtual host. Record the certificate identity, names, serial number or fingerprint, and expiration date shown by the endpoint. Compare each result with the replacement intended for that endpoint. A mismatch may indicate a missed copy, an unchanged proxy, an alternate virtual host, or another edge location still serving the previous certificate.
Use a monitor that connects to the visitor-facing endpoint and alerts before the served certificate expires. Monitor renewal job failures separately, since a successful job does not prove that each service has loaded the new certificate. Allow enough lead time for an operator to repair validation, deployment, or DNS before expiry. Provider reminder email is not a dependable primary signal: Let's Encrypt ended its expiration email service in 2025.
Review Failures and Access Regularly
Periodically confirm that the scheduled task still runs, its ACME account and DNS credentials remain valid, the validation route is reachable, and the deploy hook targets the correct service. Inspect logs without exposing private keys or API secrets. After changing a CDN, DNS provider, container image, or certificate authority, repeat the relevant validation and deployment checks and confirm the certificate served by each affected endpoint.