SSL vs TLS: What Is the Difference?
SSL and TLS are related generations of protocols for protecting a network connection. SSL is the older family and should no longer be used; TLS is its successor.
To understand a site's security, separate the protocol negotiated for the connection from the certificate used to authenticate the server. A setting labeled SSL may control a connection that actually uses TLS.
Why TLS Replaced SSL
Secure Sockets Layer, or SSL, preceded Transport Layer Security, or TLS. SSL 3.0 was followed by TLS 1.0, and later TLS versions continued to revise the protocol. Both SSL 2.0 and SSL 3.0 are deprecated: their security weaknesses make them unsuitable for protecting current connections.
SSL 3.0 has flaws in its encryption and key exchange mechanisms. Some attacks exploit the way it protects messages, allowing information to be recovered from traffic that was supposed to be confidential. SSL 3.0 also lacks the extension mechanism that enabled many later security improvements in TLS.
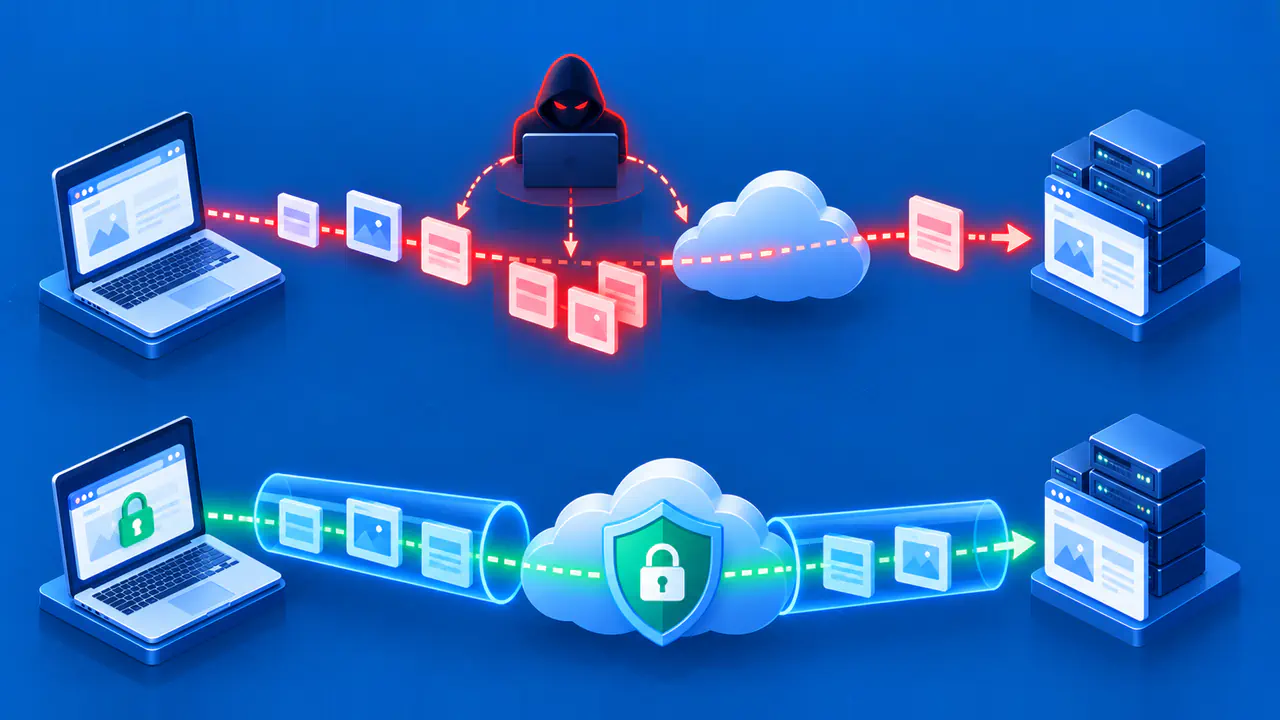
Modern TLS offers encryption methods that protect both message confidentiality and integrity, meaning that an observer cannot read protected content and an attacker cannot silently alter it in transit. TLS 1.3 permits only authenticated encryption algorithms, which provide those protections together. This is a change in the available cryptographic protections, not simply a different name for SSL.
Which TLS Versions Matter Today
TLS 1.0 and 1.1 are also deprecated, so a setting labeled TLS is not enough to establish that a service uses a suitable version. Current configurations use TLS 1.2 or TLS 1.3. TLS 1.3 is preferred where both endpoints support it; TLS 1.2 remains usable with appropriate security settings. Support for a version and the decision to enable it are separate configuration choices.
During a TLS handshake, the client and server agree on a protocol version and compatible cryptographic parameters. The connection uses that negotiated version, not every version listed in an administrator's interface. During a typical initial HTTPS handshake, the browser also validates the server's certificate before sending its HTTP request. The certificate supports authentication but does not itself choose the TLS version.
Protocol versions and cryptographic algorithms may have separate controls. Enabling TLS 1.2 while leaving weak algorithms available does not produce the same configuration as limiting it to suitable modern choices. TLS 1.3 removes many older options, but the software, certificate setup, and other enabled versions still need attention. A broad “secure” switch cannot show all of these settings.
Why the Name “SSL Certificate” Persists
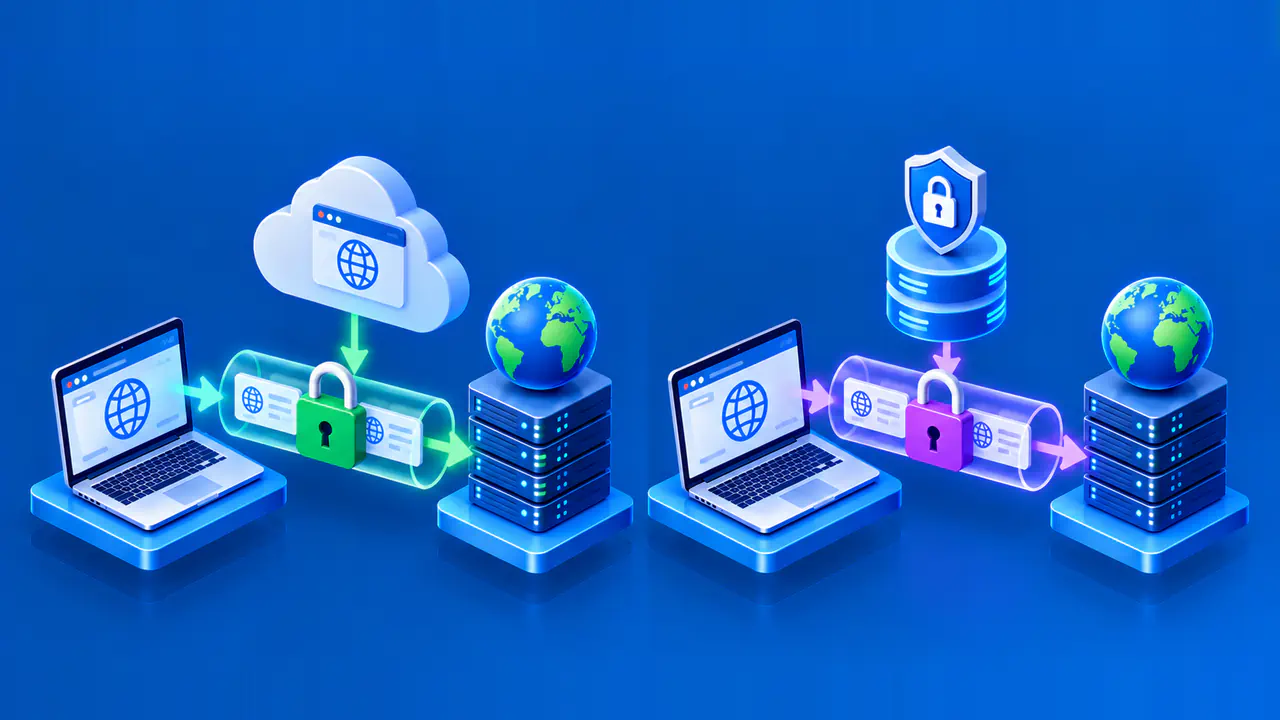
A server certificate contains a public key and names for which it is valid. Many vendors still call this an SSL certificate because the label became familiar before TLS replaced SSL. A certificate sold under that name can be used with TLS when its key type, names, validity, and trust meet the client's requirements.
A browser showing a valid certificate does not prove that every older protocol option on the server is disabled. Disabling an obsolete protocol requires a configuration change, not a different certificate.
How to Read a Legacy SSL Label
The letters SSL remain visible in product menus, hosting plans, documentation, and certificate sales pages. A screen labeled “SSL settings” might control TLS versions, certificates, or both. An option explicitly labeled “SSL 3.0,” however, names the obsolete protocol and should remain disabled. The label on the surrounding menu does not change what that specific option enables.
Older instructions can also use “SSL” as a broad label for secure transport. If an instruction says to “turn on SSL,” find out whether it means assign a certificate, permit a TLS version, or change how a service starts its protected connection. Those actions affect different parts of a deployment. A certificate file alone does not make a service listen for TLS connections.
Sometimes SSL appears in a software library's name or in a configuration key that remains unchanged for compatibility. Consult the documentation for the installed version to determine what the setting controls. The label alone does not show whether the setting is enabled, which service it applies to, or whether a proxy handles the visitor's connection first.
Distinguishing TLS Failures from HTTP Errors
TLS protects HTTPS connections, while HTTP defines the requests and responses exchanged through them. TLS does not decide whether an account has access to a page or whether a site's content is accurate. Calling every problem an “SSL error” can obscure whether the failure concerns the protected connection or the application using it.
For example, a browser can successfully negotiate TLS and then receive an HTTP error page. The application returned an error through a working protected connection. By contrast, a failed TLS handshake prevents the browser from exchanging ordinary HTTP messages through that connection. The exact error helps distinguish a connection problem from a website response.
Checking the Service behind the Label
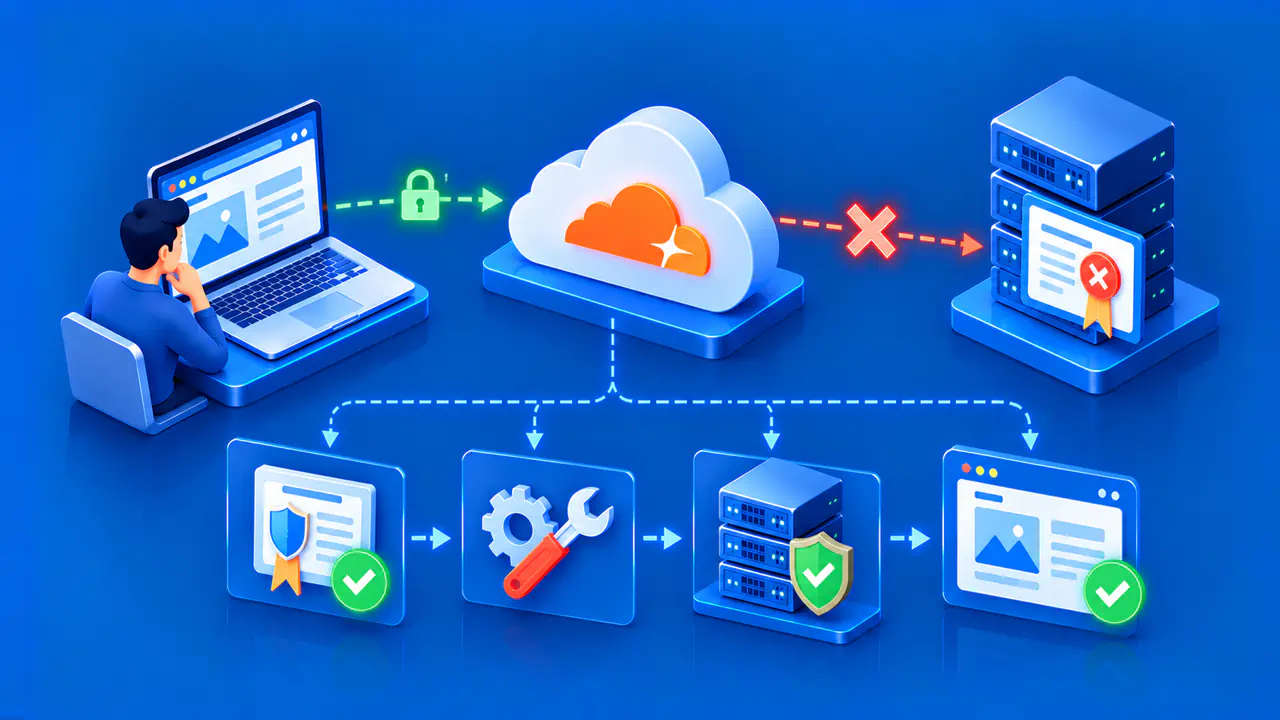
Start with the precise connection under discussion: a browser to a website, an application to its service, or a proxy to an origin server. Identify where TLS begins and ends. If a proxy makes a separate connection to the origin server, check the protection on that connection as well. The browser's negotiated protocol describes its connection to the proxy, not that second connection.
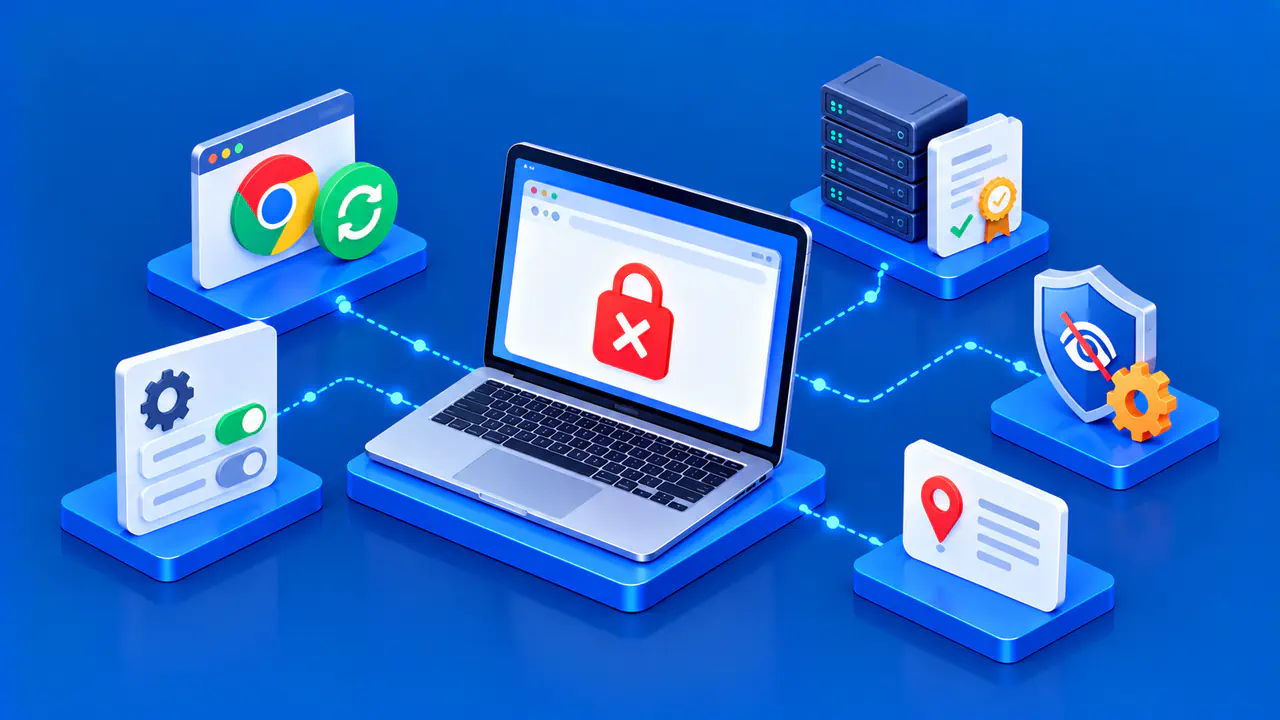
Check which protocol versions the endpoint allows and which certificate it uses. Verify that the certificate covers the name clients use and is trusted under the intended client's rules. If the connection fails, note the client, the server it contacted, and their TLS settings. A version mismatch requires a different correction from an expired certificate or an incorrect hostname.
Do not enable SSL or deprecated TLS versions simply because an older client fails to connect. Compare the client's supported versions with the server's allowed versions, then check their other handshake requirements. Updating an unsupported client or correcting the server's configuration may resolve the incompatibility. If the client cannot support a suitable configuration, replacing it is preferable to reopening obsolete protocol support.