How to Find a Domain's Nameservers
A domain's authoritative name servers answer queries for its Domain Name System (DNS) zone. An NS query asks for name-server records. The answer can come from a recursive resolver's cache, the parent zone's delegation, or the domain's own authoritative zone. Those views can briefly differ after a change, or remain mismatched because the configuration is wrong.
To identify the name servers in use, begin with a normal NS query and note which server supplied the answer. If a migration or outage makes the result doubtful, check the parent delegation and the child zone separately. The name servers identify DNS authority, but they do not necessarily reveal the website host or a hidden origin server.
Start with an NS Lookup
Enter the exact domain in a trusted DNS lookup tool and select the NS record type. With BIND's dig tool, dig example.com NS requests NS records for the reserved example domain. Replace example.com with the domain you want to check.
Read the record owner name, which is the DNS name the record applies to, along with the NS hostnames, response status, answer section, and responding server. A and AAAA records contain IPv4 and IPv6 addresses, respectively, and answer a different question from NS records.
Query the zone apex, the name at the top of the DNS zone you care about. A website hostname such as www.example.com may not have its own NS records because it is commonly inside the example.com zone. A subdomain gets a separate delegated set only when the parent publishes a delegation for it. An empty NS answer for www does not prove that the main domain has no name servers.
Copy the complete hostnames, including their suffixes, and avoid replacing them with IP addresses in your notes. The NS record names servers by hostname. Address records can help a resolver reach those servers, but an address is not the same thing as the delegation name.
Identify the Resolver That Answered
By default, dig uses the name servers in its resolver configuration unless you supply a server argument. With the default resolver, the result usually reflects what a recursive resolver currently knows. The SERVER line identifies the server that answered the query, but does not establish whether the answer was authoritative. A web-based tool may use its own resolver, so note the tool and location when comparing results from several services.
Recursive answers can be cached. A recent name-server change may appear in one resolver and not another until cached records expire or the resolver refreshes them. A differing answer is therefore a reason to inspect the delegation path, not immediate proof that one tool is broken. Compare query timestamps and the TTL values where the tool shows them, but remember that a displayed TTL is not a universal deadline for every cache.
You can choose a particular server with dig's @server form. For a direct query, use dig @server example.com NS +norecurse, replacing server with the verified server's address or hostname and example.com with the domain being checked. The +norecurse option requests an answer without recursive processing. Keep the server choice with the result so another person can reproduce the same query.
Check the Parent Delegation When Needed
The parent zone directs resolvers toward the delegated child zone. For example, the relevant top-level domain publishes delegation data for a registered second-level domain. A registrar's name-server setting normally affects this parent-side delegation through the registration system, while reading DNS data does not change it.
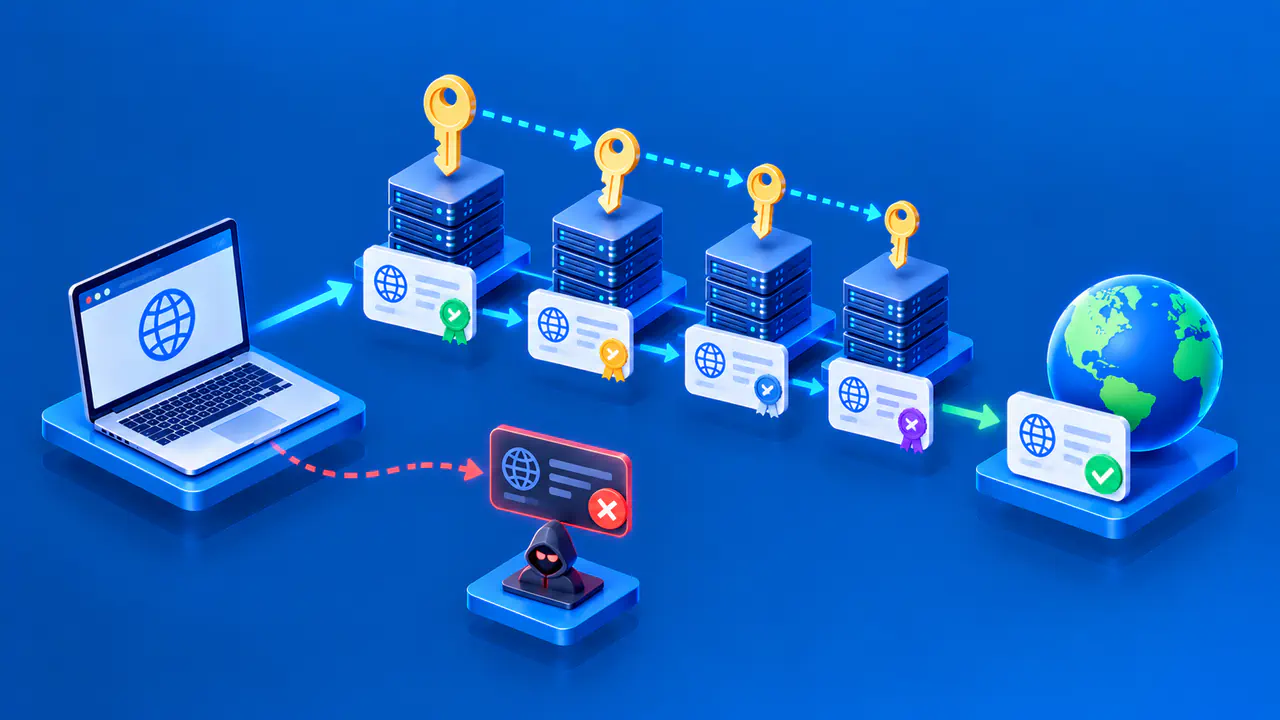
Use a trace when you need to see how resolution moves from root to the relevant parent and child. The command dig example.com NS +trace follows the delegation path iteratively and shows replies from servers along the way. Read which response came from the parent and which came from the child. A trace is a diagnostic view, not a promise that all recursive resolvers already have the newest data.
You can also ask a verified parent-zone authoritative server directly for the domain's NS delegation. Read the referral in its authority section and record the server queried. Do not pick an arbitrary public resolver and label its answer parent delegation. The relevant parent may be a subdomain zone rather than a top-level domain when the name itself is delegated below another domain.
Compare Parent and Child Records
After identifying a delegated name server, query it for the child zone's NS records and compare the returned hostnames with the parent's delegation. The parent tells resolvers where to begin, while the child's own zone normally publishes its apex NS set. When those sets differ, some tools may display different names depending on which side they asked. Record both sets and avoid silently merging them into one answer.
Check whether each listed server returns NS records for the intended child zone in the answer section and includes aa in dig's response flags. The aa flag means the responding server says it is authoritative for the queried name. A hostname that resolves to an address but does not serve the zone is not a healthy name server just because it appears in the delegation. Conversely, a server can host a copy of a zone without being listed at the parent, so ordinary resolvers may never be directed to it.
Address records stored at the parent to reach a name server inside the delegated zone are called glue. They let resolvers reach that server without first asking it for its own address. Compare each glue address with the current A or AAAA record for that name server, because a stale address can break access even when the NS names look plausible. Do not infer the website's origin IP from a name-server address, because DNS and web hosting can be on different systems.
Report Discrepancies Clearly
When asking a registrar or DNS provider for help, provide the domain, query time, resolver used, parent server checked, child server checked, and the NS sets each returned. Mention whether a server answered authoritatively and whether the discrepancy followed a planned change. Redact any private account information from screenshots. This evidence lets the provider distinguish propagation through caches from a persistent mismatch or a server that is not serving the zone.
For a basic list of name servers, the NS lookup and the name-server settings in your registrar account may be enough. For a suspected delegation fault, compare parent and child evidence before changing anything. Name-server changes can affect the entire DNS zone, including website and mail records, so the finding should be specific about which layer is wrong and who can update it.