How to Redirect HTTP to HTTPS
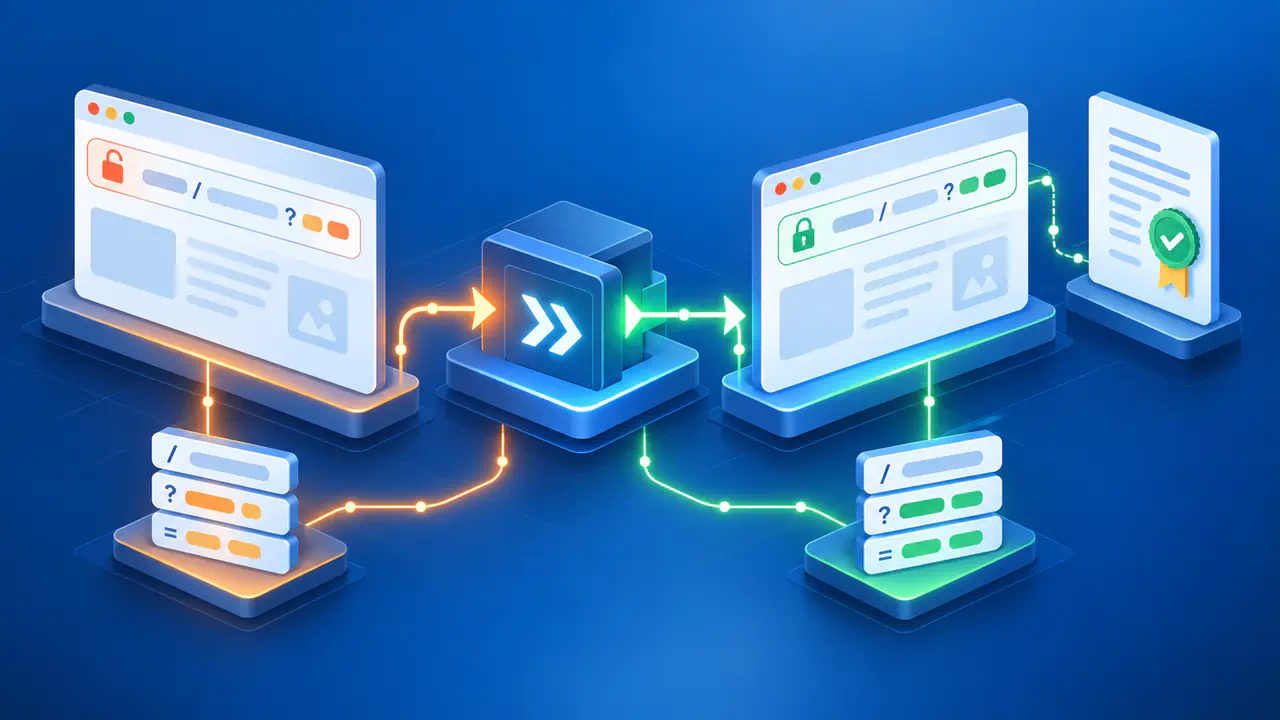
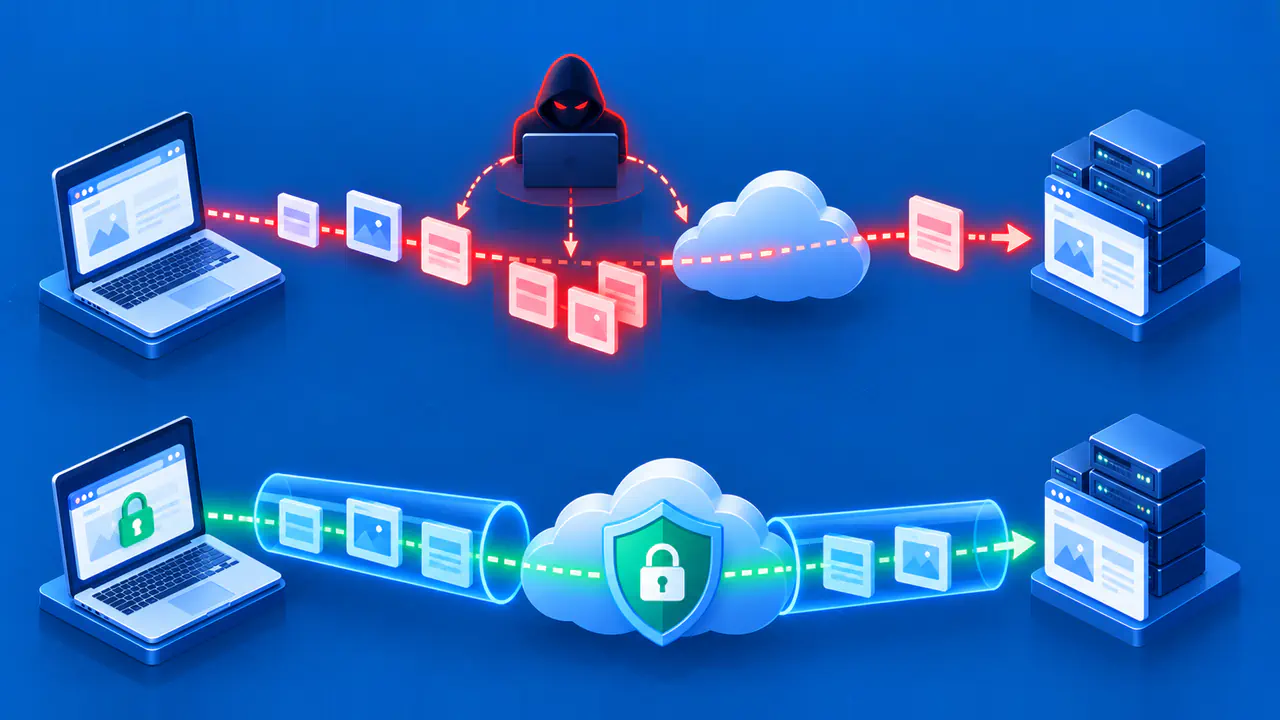
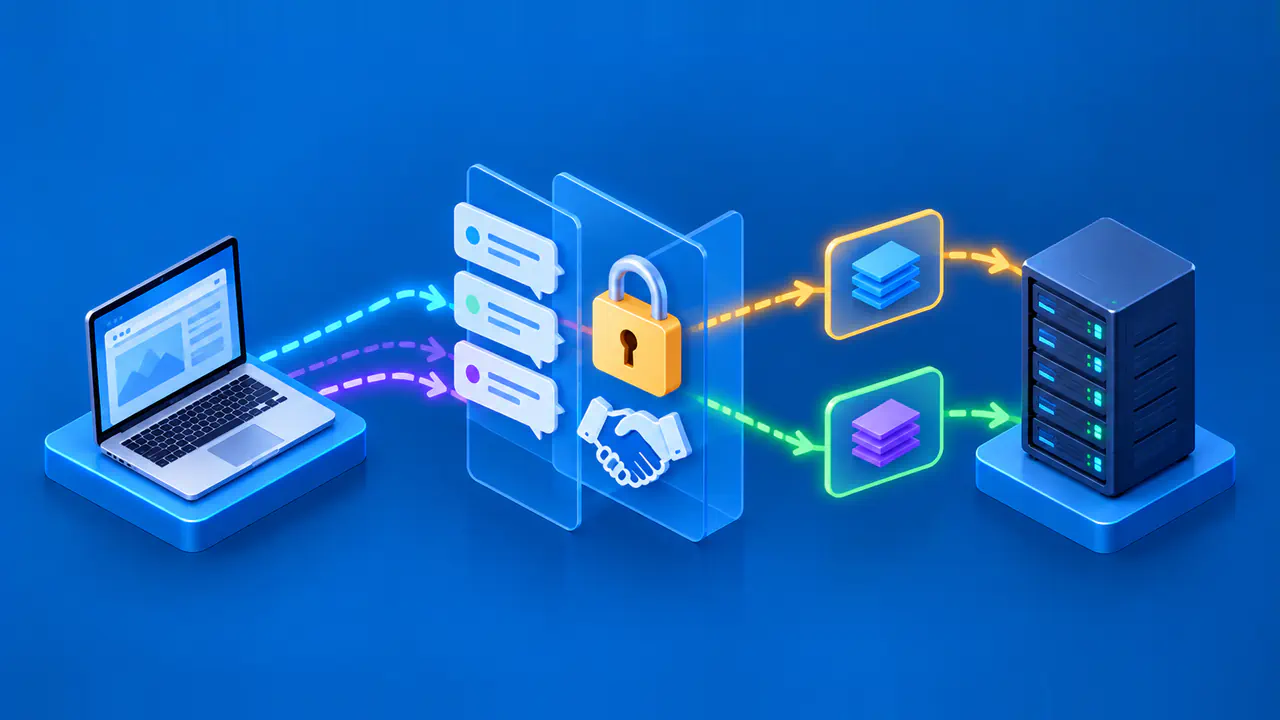
To move a website you manage from HTTP to HTTPS, first make the HTTPS address work, then redirect requests from the HTTP address. A redirect is an HTTP response with a status and a Location header pointing to the secure URL. A redirect cannot repair a missing certificate or a broken HTTPS service. Test the destination before sending every visitor there.
The redirect should use a known, trusted hostname, preserve the intended page path and query information, and avoid loops between a content delivery network (CDN), reverse proxy, and application. Form submissions and API calls need separate checks because a redirect can affect how the request is sent. Verify that pages load over HTTPS and that login, forms, and other important functions still work.
Validate HTTPS before Redirecting Traffic
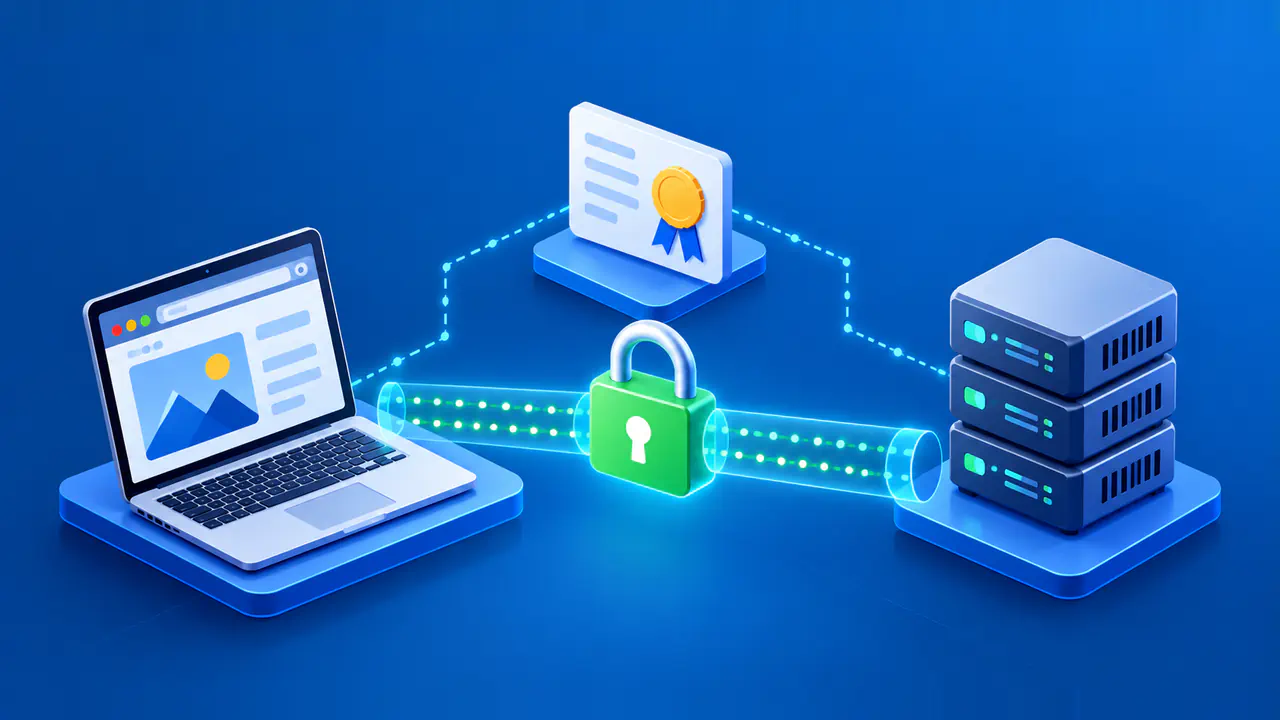
Confirm that the preferred HTTPS hostname resolves to the right service, presents a trusted certificate covering that exact hostname, and returns the correct page for representative paths. Test the apex and www names if both accept requests. A browser checks the certificate before it can receive any redirect from an HTTPS hostname, so all served host variants need valid TLS coverage even when one immediately redirects.
Inspect the certificate chain, validity dates, and renewal process. Then check application behavior under HTTPS: assets, API endpoints, forms, login callbacks, and downloads should not fall back to insecure URLs. A page loaded over HTTPS can fail to load scripts or other resources requested over HTTP because browsers block some types of mixed content. Fix those references before treating the migration as finished.
Test the HTTPS setup in a staging environment or with a limited rollout before changing the whole site. Do not enable a broad permanent redirect to a destination that has not been tested. If the preferred host changes as part of the migration, test both the scheme and host transition together.
Use a Fixed Trusted Destination
Configure the HTTP listener, CDN, or application to return a redirect with an absolute HTTPS URL on your chosen host in the Location header. For example, an HTTP request for http://example.com/guide can be sent to https://example.com/guide once that destination is live. The configuration depends on which service receives the public HTTP request. Set the redirect there, and check whether a proxy or application already has a rule for the same URLs.
If NGINX receives visitors' HTTP requests directly, its HTTP server block for the known site names can use return 301 https://example.com$request_uri; for a permanent move of ordinary web pages. The destination host is fixed, and $request_uri keeps the original path and query string. Replace example.com with the preferred hostname, and use this rule only in the HTTP block, after confirming that the corresponding HTTPS pages work.
Do not build the target by copying an unchecked Host request header. A request can carry an unexpected host value, and a permissive redirect handler can then become an open redirect or send visitors to an attacker-controlled domain. Match known source hostnames and construct the destination from an explicit trusted host. Reject or handle unrelated hostnames separately.
A 301 redirect allows a client to change a POST request to GET, whereas 308 preserves the method and body. Test form submissions and API calls separately from ordinary GET requests. For requests containing passwords or other credentials, change clients to use HTTPS directly: a redirect cannot protect data already sent over HTTP.
Preserve Paths and Queries Deliberately
Map each old URL to its corresponding secure URL where the content still exists. Preserve the path so visitors to an old article reach that article rather than a generic home page. Preserve a query string when its parameters are meaningful to the application, but review sensitive or obsolete parameters before carrying them to a new host. If a parameter no longer applies, decide whether to remove it or map it to a supported value rather than carrying it over unchanged.
Test encoded characters, trailing slashes, and unusual but valid paths against the actual redirect implementation. An incorrect rule can double-encode a URL, drop parameters, or create duplicate slashes. When old and new site structures differ, use an explicit mapping for changed paths. Do not send missing pages to a single unrelated destination merely to avoid an error response.
Update internal links to use HTTPS so they do not depend on redirects or browser upgrades. This also avoids an extra network request when the browser would otherwise contact the HTTP address. Update canonical tags and sitemaps to the preferred HTTPS URLs as well.
Check Proxy Scheme Handling and Loops
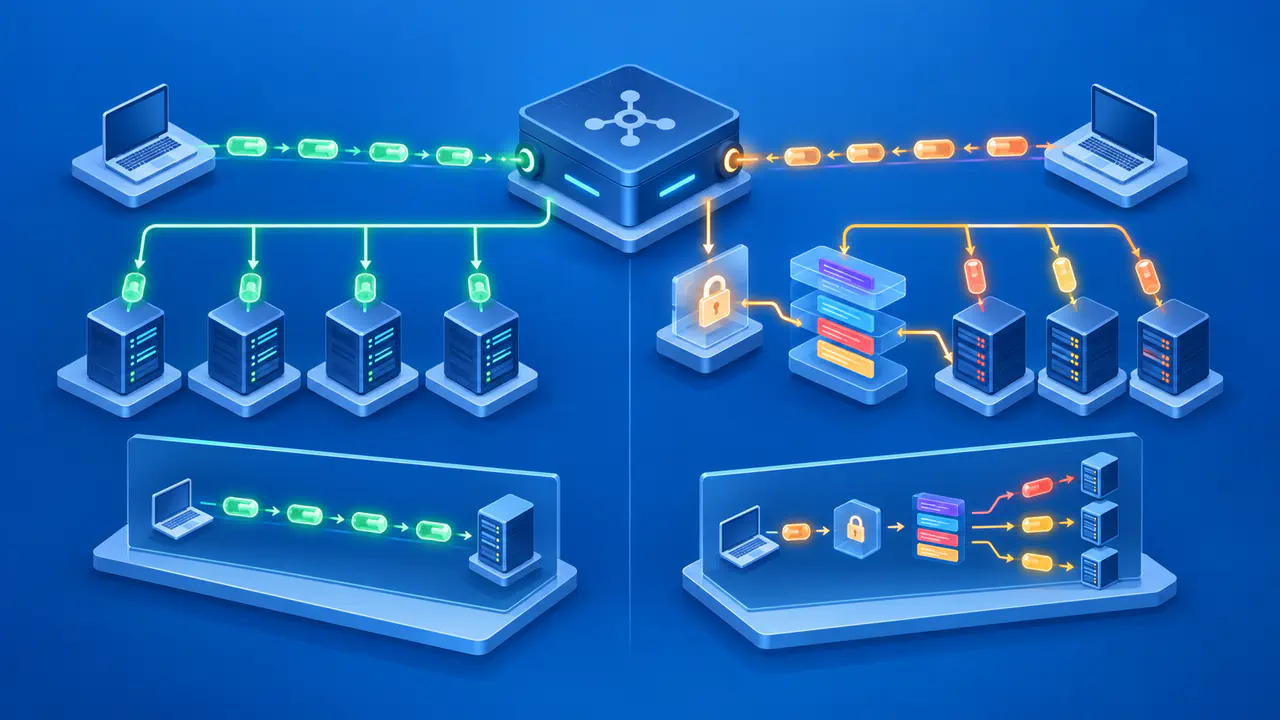
A common loop appears when a TLS-terminating proxy receives HTTPS from the browser but forwards HTTP to the application. If the application checks only its local connection scheme, it may incorrectly think the visitor used HTTP and redirect back to the same HTTPS URL. The browser repeats the request, and the loop continues.
Configure the application to recognize the original request scheme only from a trusted proxy. A header such as Forwarded or X-Forwarded-Proto can identify the original scheme, but the proxy must remove or replace untrusted incoming values. Alternatively, keep the redirect at the edge and avoid a second conflicting rule at the origin. Check the browser-to-proxy connection and the proxy-to-application connection separately.
Inspect the complete chain from all public HTTP variants, including www and apex. Watch for an HTTP-to-HTTPS hop followed by a host redirect, then another scheme redirect. Collapse unnecessary hops where possible and ensure the final page is correct. Check the server with an HTTP client that does not automatically upgrade the request, as well as with a browser. A cached redirect or an HTTP Strict Transport Security (HSTS) policy can otherwise prevent the browser from contacting the HTTP endpoint you need to test.
Check the Site after the Switch
After rollout, sample important pages, form submissions, assets, and error routes. For a failed request, inspect the starting URL, redirect status, Location header, and final response to find where the failure occurs. Check certificate details and mixed-content warnings when the failure involves HTTPS. Monitor certificate renewal and redirect failures because a correct rule today can break after a certificate or proxy change.
HSTS tells a browser to use HTTPS for future requests after receiving the Strict-Transport-Security header over HTTPS. It complements an HTTP redirect but does not replace a valid HTTPS service or protect an HTTP request sent before the browser knows the policy. Review scope and duration before enabling it, especially if subdomains are included. Send HSTS from HTTPS responses, not from HTTP redirect responses.
Keep a copy of the previous configuration so you can correct a faulty redirect without losing the working HTTPS setup. After a change, repeat the request that failed and check that the browser reaches the intended page without a redirect loop.