How to Set Up www and Non-www Website Addresses
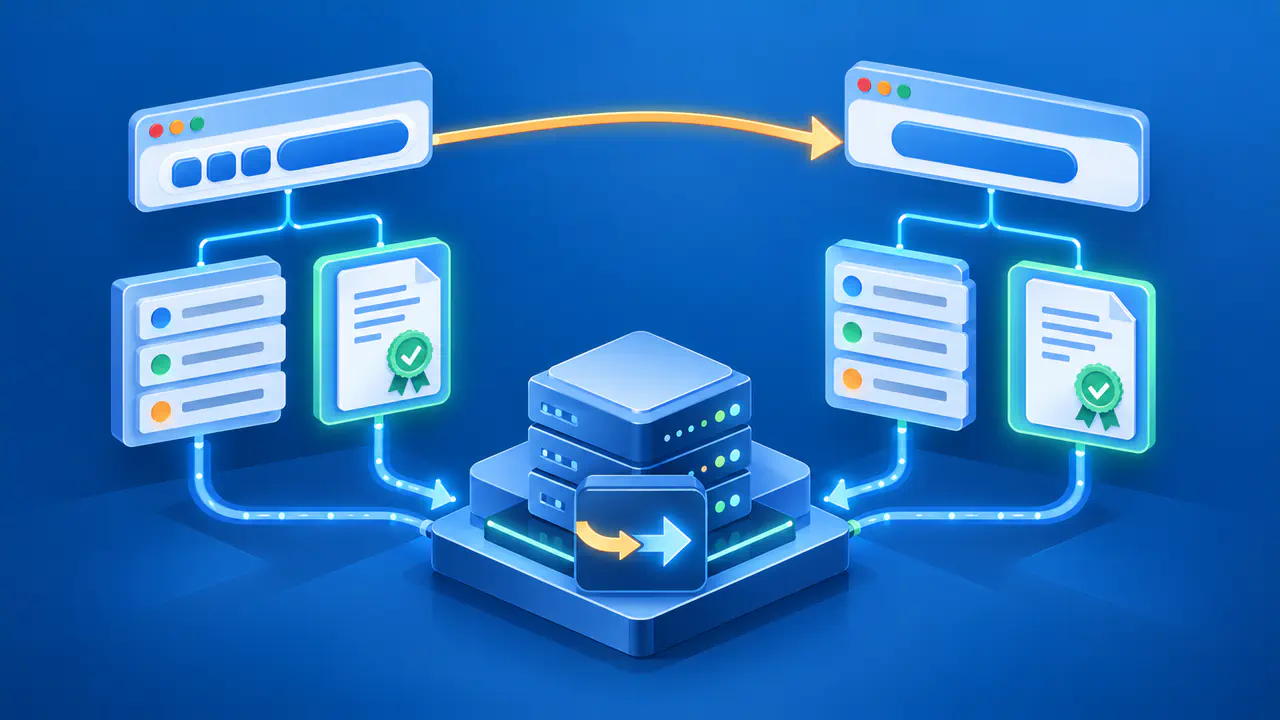
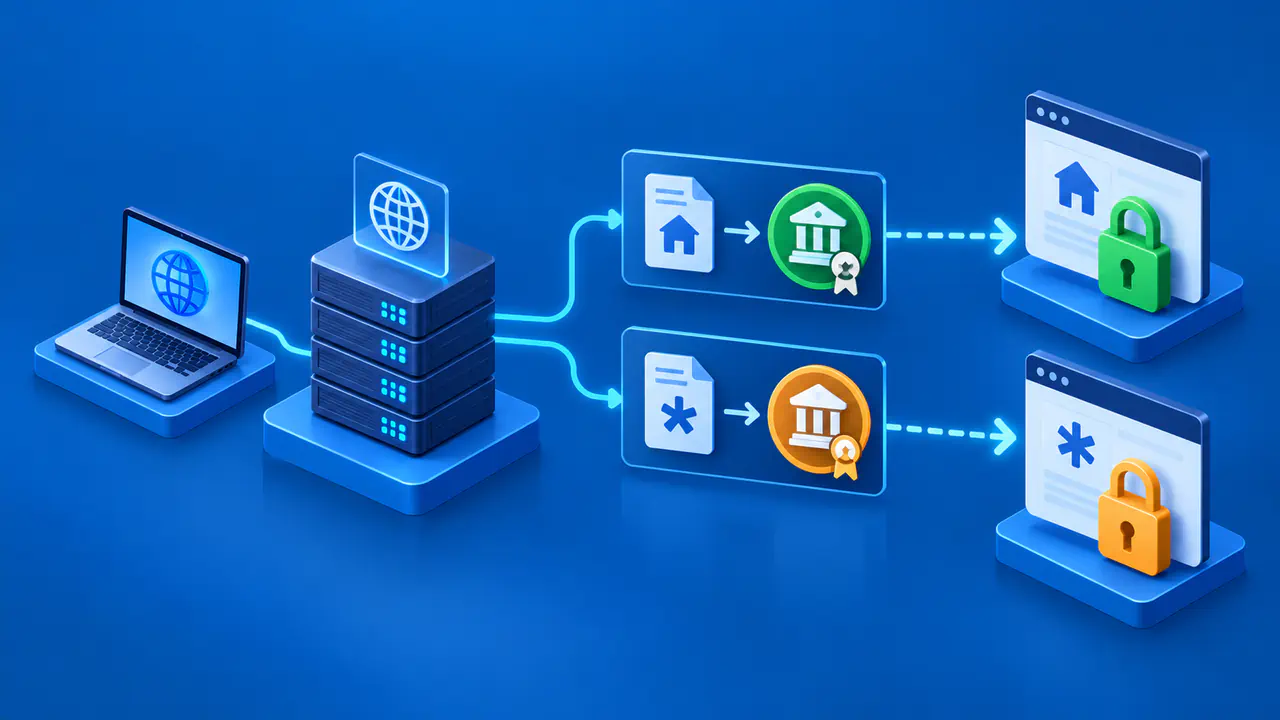
A website can be reached at an apex hostname such as example.com and a www hostname such as www.example.com. These are distinct DNS names, and their HTTPS pages have different origins because the hostnames differ. To make both addresses work, configure DNS, add both hostnames to the web server or content delivery network (CDN), and provide valid HTTPS certificates for each. Then choose one public address and redirect the other to it consistently.
A DNS alias can help a hostname reach the right service, but DNS does not tell a browser to change its visible URL. The redirect happens at the HTTP layer after a connection is made. That is why a redirecting HTTPS hostname still needs a valid certificate: the browser checks TLS before it can read the redirect response.
Configure DNS and the Web Server
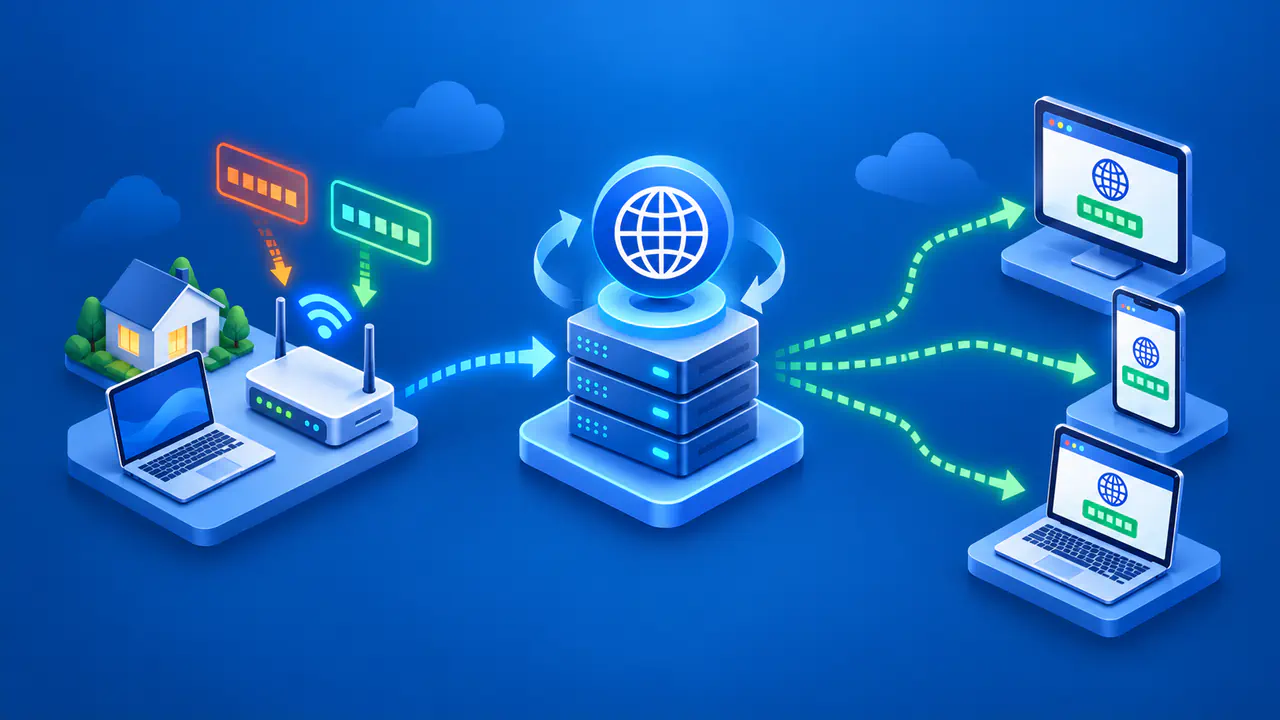
Check authoritative DNS for both the apex name and the www name. The apex may use A or AAAA address records, or an alias feature supported by the DNS provider. The www name may use address records or a CNAME that points to another hostname. Use the IP addresses or target hostname supplied by your hosting service. The exact record type depends on the hosting and DNS provider, so follow that provider's documented setup rather than copying a record from another site.
DNS resolution alone is only the first step. The server, reverse proxy, or CDN must recognize both hostnames and route requests to the correct site or redirect handler. A name can resolve successfully yet display the wrong virtual host, a default page, or an error. Once your test resolver returns the updated records, check each hostname independently with HTTP and HTTPS. Cached DNS answers can keep directing clients to an old address until those answers expire.
Adding www to example.com creates the subdomain www.example.com, but that name does not require a separately delegated DNS zone. You can add its record in the existing example.com zone. In that zone, example.com is the apex, the name at the top of the zone; www.example.com is a name below it.
Cover Both Names with HTTPS
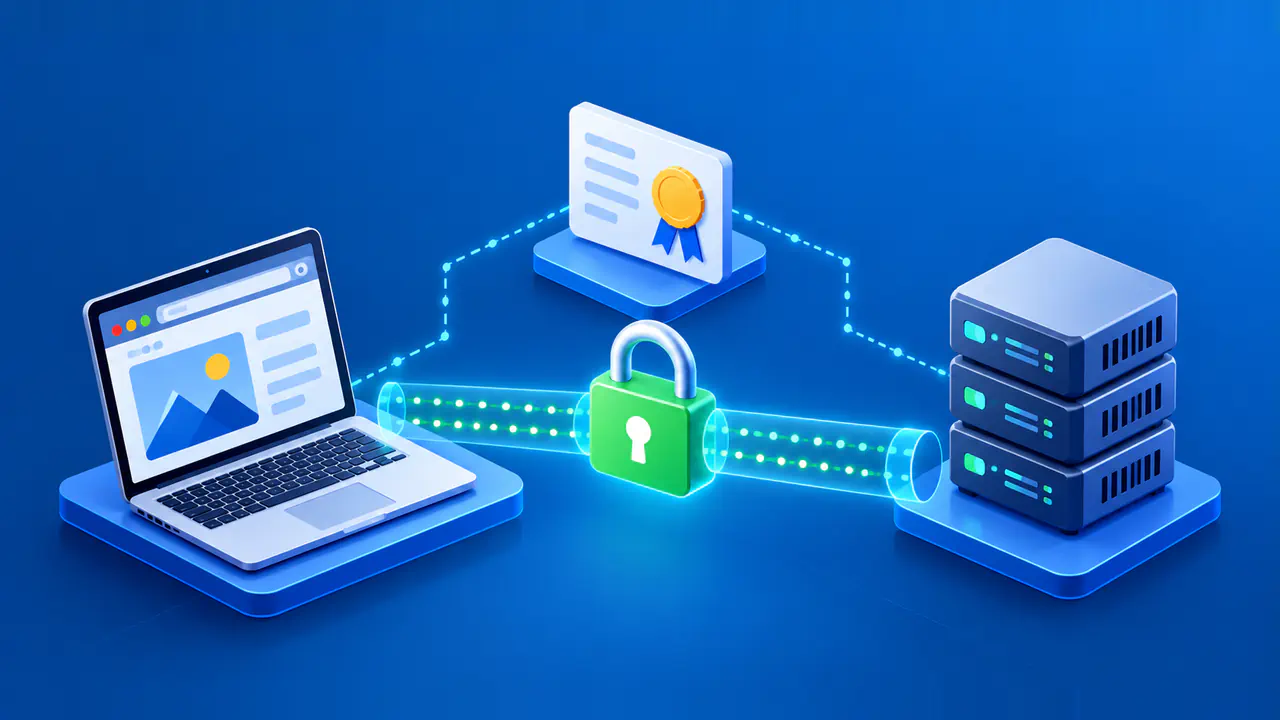
Before enabling an HTTPS redirect to the preferred host, ensure that each hostname presents a trusted certificate that covers that name. A certificate for example.com does not automatically cover www.example.com. A certificate can list both names, or the service can present suitable certificates for each name, depending on the platform. Make sure certificate renewal covers both hostnames, including the one that only redirects visitors.
When several HTTPS sites share an IP address, the browser can send the requested hostname through Server Name Indication (SNI) during the TLS handshake. The server uses that name to select a suitable certificate before reading the HTTP request. The later HTTP request still has to reach the correct site or redirect handler, whether TLS ends at your server or at a CDN. A browser cannot safely follow a redirect from a hostname whose TLS connection fails first.
Also verify that the redirect target itself uses HTTPS and has a valid certificate. Avoid an HTTPS-to-HTTP hop or a chain that visits multiple host variants. The preferred destination should be one stable, secure URL for each resource.
Choose the Preferred Host
Either www or the apex can be the preferred public address. Choose based on existing links, brand use, operational setup, and the URL pattern already established for the site. There is no universal SEO rule that makes one spelling inherently superior. Use the chosen hostname consistently in navigation and published links.
Inventory the site's current URLs before changing the host. Look for hard-coded absolute links, login callbacks, API allowlists, cookie scope, asset hosts, sitemap entries, and canonical tags. A host migration can affect integrations even when ordinary pages still load. Keep a mapping from each old URL to the corresponding path on the preferred host, rather than sending every path to a home page.
For example, if https://www.example.com/guide is preferred, a request for https://example.com/guide should normally arrive at the same guide on www. The redirect status must suit both the duration of the move and the requests the site handles. A permanent 301 can change a POST submission to GET, while 308 preserves the method and body. Check forms and API requests before applying the same rule to every path.
Redirect the Alternate Address Safely
At the web server, CDN, or application layer, configure a redirect for the alternate hostname with a fixed destination on the preferred host. Preserve the path and query string only when doing so is intended and safe for that route. Do not build the destination from an unchecked Host request header. Limit the redirect handler to the known alternate name and use an explicit target host.
Use a permanent redirect when the move is settled and the old host is no longer the preferred address. A temporary redirect can be useful during testing, but its handling of request methods must also match the application. Avoid loops caused by conflicting rules at the CDN and origin. A redirect from apex to www at one layer and from www to apex at another can make the site inaccessible.
Keep HTTP-to-HTTPS behavior coordinated with host preference. Ideally, each entered variant reaches the secure preferred URL through as few hops as practical. Inspect the actual chain from http:// and https:// for both hostnames, including path and query handling. A working destination can hide an unnecessary extra redirect or a hop back to unencrypted HTTP.
Align Canonical Tags and Site Links
On each preferred page, a self-referencing canonical annotation identifies that same page URL as the preferred version. Update the sitemap to list preferred HTTPS URLs and change internal navigation to link directly to them. For Google Search, redirects and canonical annotations are stronger signals than sitemap inclusion. Aligned signals support your preference, but Google can still choose a different canonical URL.
Check a sample of equivalent pages, not only the home page. Check the certificate and redirect response on the alternate host, then inspect the final page and its canonical annotation on the preferred host. Confirm that the sitemap and internal links use the preferred URLs. Confirm that redirects do not erase meaningful paths or parameters and that login and forms still work. If a page fails, keep the requested URL and the response from each step so you can locate the failing rule. Check the configuration at the layer that returns that response, then repeat the affected request.