RDAP Lookup vs WHOIS Lookup Differences
Registration Data Access Protocol (RDAP) and WHOIS both answer questions about registration data, such as which registrar serves a domain and what status or name servers appear in the public record. They differ in how a client finds the service, sends the query, and reads the answer. RDAP uses web transport and JSON, a text format with named fields and structured lists. Traditional WHOIS sends a text query to a server and receives plain text whose labels and layout can vary.
For a quick lookup, either interface may show useful information when the operator offers it. For software that must interpret many results consistently, RDAP's structured fields and discovery mechanism are usually the more suitable starting point. Neither protocol automatically reveals private contact details or proves who operates a website.
Compare the Query and Response Formats
Traditional WHOIS uses TCP port 43: a client sends a line of text and the server replies with text. The protocol does not define one standard set of domain fields or a machine-readable response schema. A program may need provider-specific parsing rules for labels, dates, and notices. A web page branded as a WHOIS lookup can add its own presentation layer, so distinguish the old protocol from the site's user interface.
RDAP clients send web requests, normally over HTTPS, and receive JSON. Registration objects such as domains, contacts, and name servers have defined structures, with fields for statuses, events, and other information. A client can read those named members rather than guess where a field sits in free-form text. Standardization helps interoperability, although providers may still expose different optional data and policy notices.
For example, a registration event in an RDAP domain result is labeled as an event and has a date. That is easier to identify than a loosely formatted WHOIS line, but it still represents a registration-system event. It is not evidence of when the website went live or a complete history of every person who used the domain.
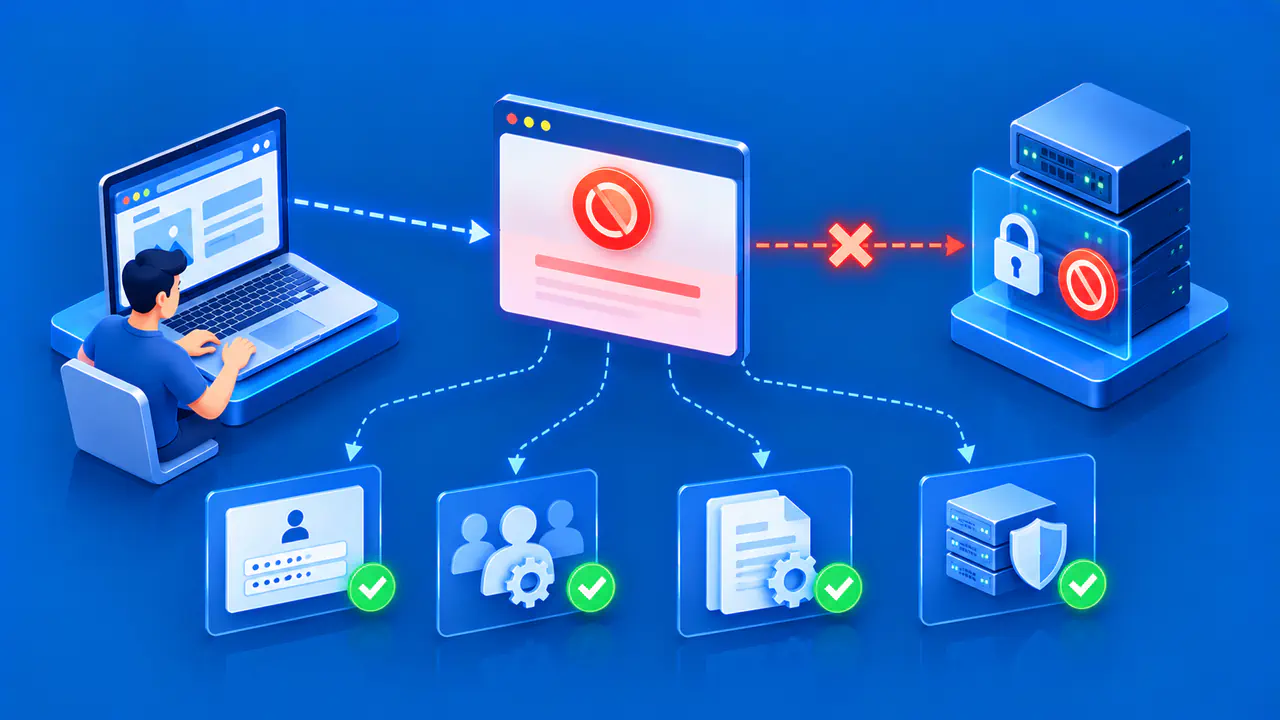
RDAP responses also have HTTP status codes that distinguish a successful query from a request the server cannot fulfill. With WHOIS, a client has to interpret the service's chosen text to recognize errors or unavailable data. A blank result on a lookup page is therefore insufficient to tell whether the record is absent, access was refused, or the query failed.
Find the Correct Service and Understand Access
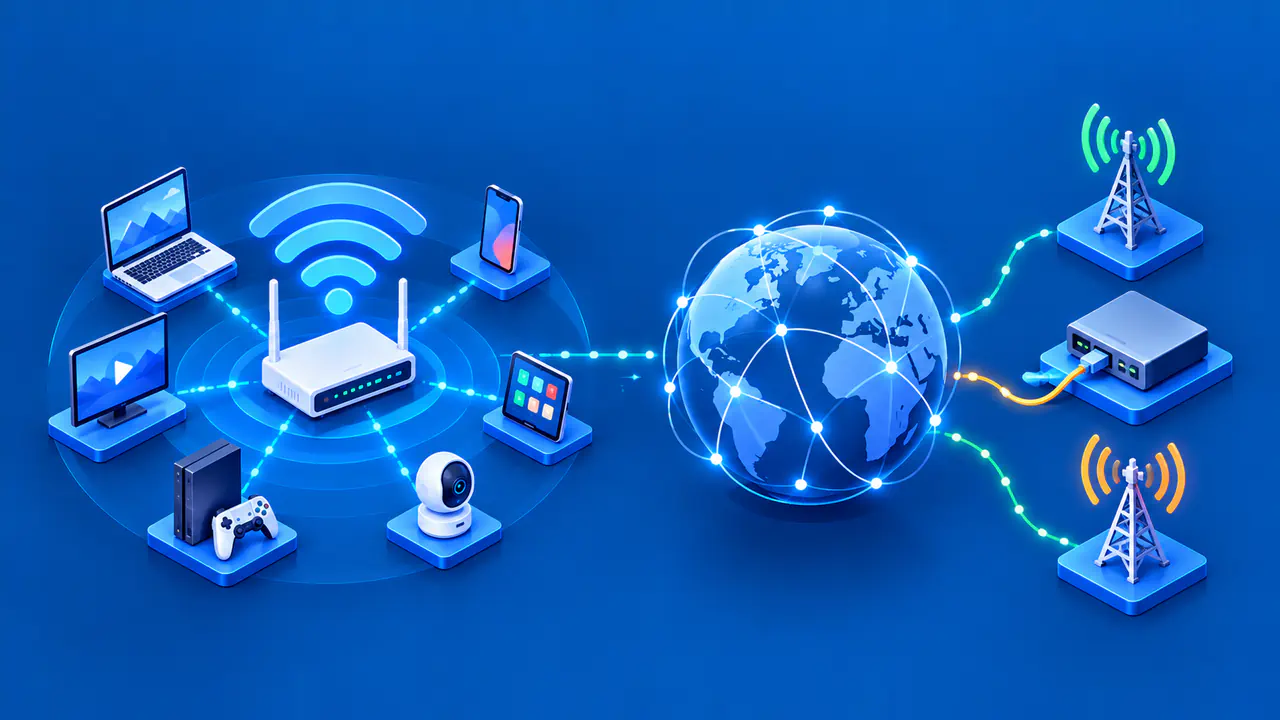
With WHOIS, a user or client may need to know which server to ask or follow a referral in a response. For domains, RDAP clients can use a directory of service addresses to find the relevant registry. Separate directories cover IP networks and autonomous system numbers, which identify independently operated networks. This bootstrap step matches the queried resource to the appropriate service, rather than trying an arbitrary server. A lookup interface may perform this discovery for you.
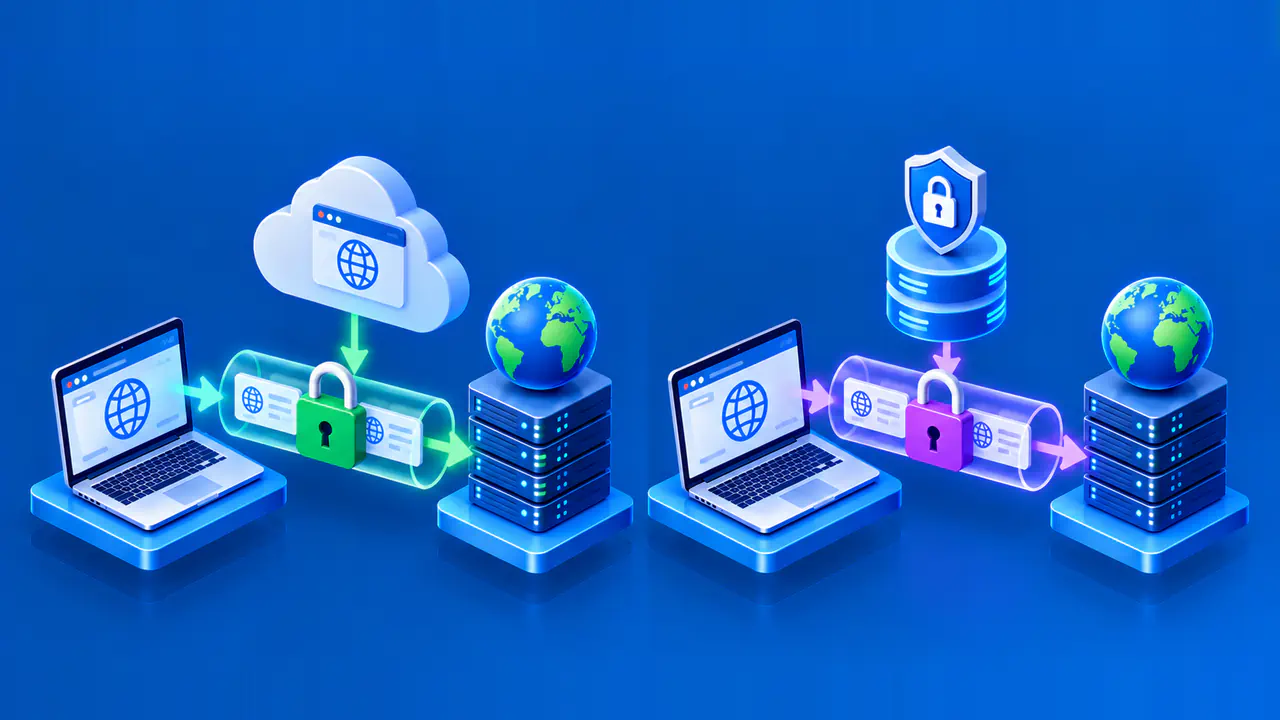
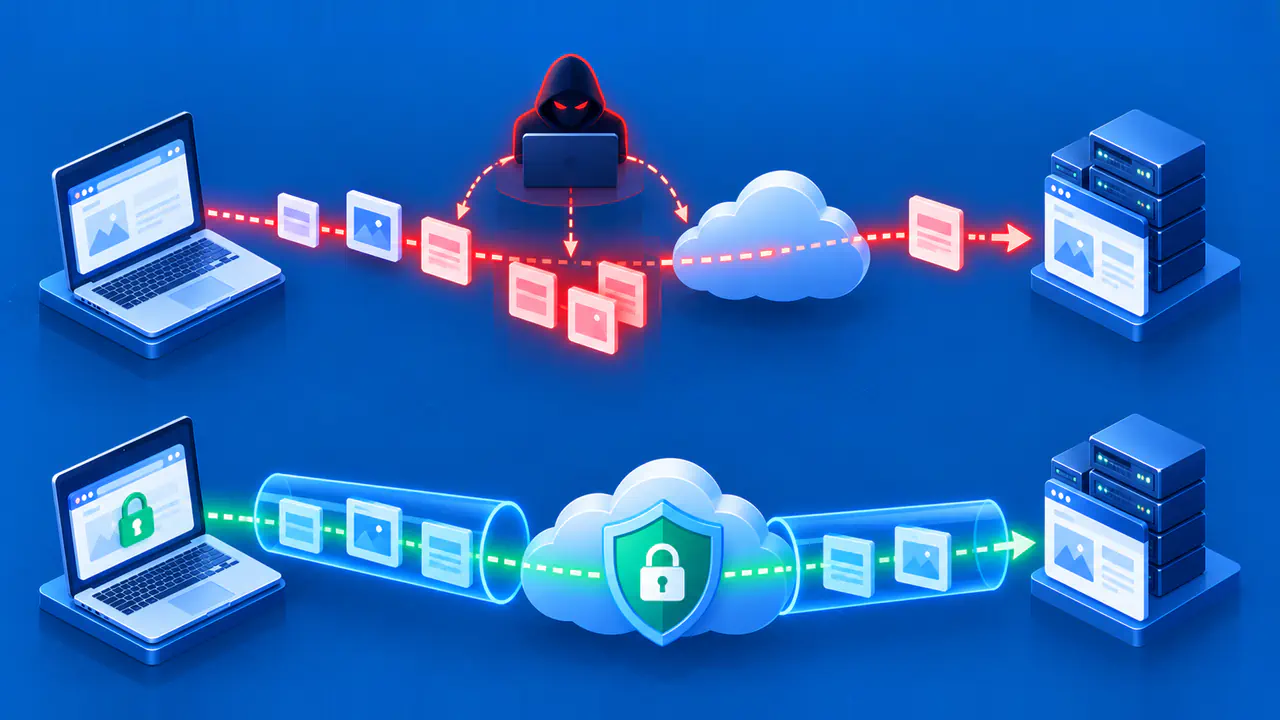
Traditional WHOIS has no built-in mechanism for strong access control, integrity, or confidentiality. RDAP uses HTTP features that can support secure transport and differentiated access. That capability does not mean an anonymous public lookup will show all registration data. The server applies its publication and access policy, and contact values may be redacted or omitted.
RDAP also supports internationalized data more deliberately than the old WHOIS protocol, whose specification has no way to indicate the character encoding of a response. A modern interface may normalize either output for display, but the underlying protocol capabilities remain different.
Understand the Current gTLD Transition
Registries and registrars for generic top-level domains (gTLDs) must provide RDAP services under the applicable profile. As of January 28, 2025, WHOIS services are no longer required for most gTLD contracted parties, with exceptions for .com, .name, and .post under their applicable contracts. This change concerns a particular set of registration services. It does not mean that every WHOIS server on the Internet has shut down.
Some providers may continue to offer WHOIS voluntarily or for other reasons, and country-code registries and regional Internet registries have their own service arrangements. Do not apply the gTLD transition date to every extension or IP-address registry. Check the relevant operator when one lookup method does not return a result.
The public fields can also differ because publication rules and service policy apply separately from transport. Moving from WHOIS text to RDAP JSON does not make redacted personal data public. A difference between two lookup pages may reflect the source, caching, redaction, or a display choice rather than a protocol error.
Recognize the Limits of Either Lookup
Registration data can identify a registrar, registry statuses, dates, and delegation information, but it does not tell you whether the website is online, whether an email account works, or whether the listed party owns a trademark. Public contact information may be hidden. A privacy or proxy service can affect what name appears in a public record. Treat a missing value as unknown until the service explains whether it is absent, redacted, or not returned to your access level.
Status codes also need context. A transfer-prohibited value indicates an operation restriction, not necessarily a dispute. An expiration date does not predict the exact public release date of a name. If you manage the domain and need to act, the authenticated registrar account is the place to confirm transaction details that a public lookup cannot settle.
Automated clients should also respect server notices, rate limits, and response errors. RDAP's structured data makes parsing easier, but it does not remove the need to handle incomplete results or policy-based restrictions. A one-off browser lookup should still be checked against the registrar if a consequential decision depends on it.
Choose the Lookup Method for the Task
Use a trusted RDAP lookup when you want structured current registration data, clear field labels, and a service-discovery path. Use an available WHOIS service when you need to compare its output with an RDAP result or an operator provides useful text output. For gTLD names, begin with the RDAP service that follows the current ICANN profile; for other namespaces, check the responsible operator's offering.
When results disagree, record the queried domain, service, time, and relevant fields. Check whether one page is cached, whether the contact field is redacted, and whether the same registrar or registry source supplied both answers. Contact the registrar for authoritative account-level facts.