What Is a Virtual Host on a Web Server?
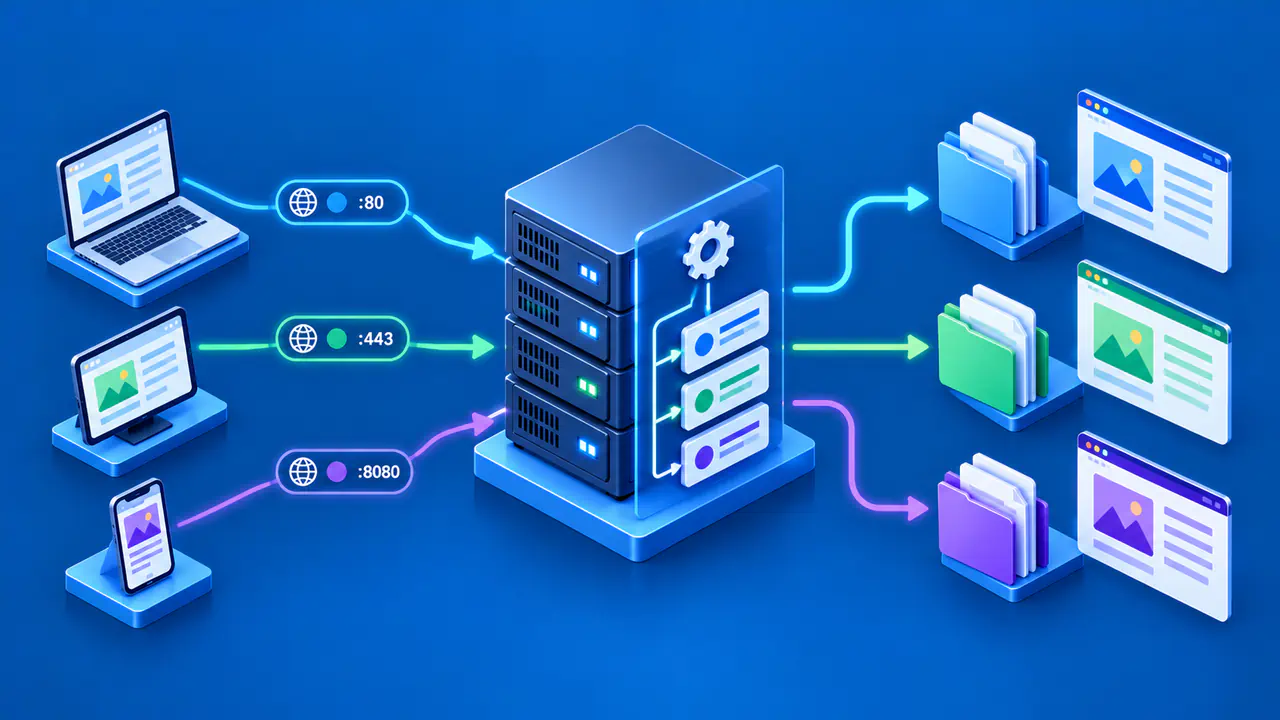
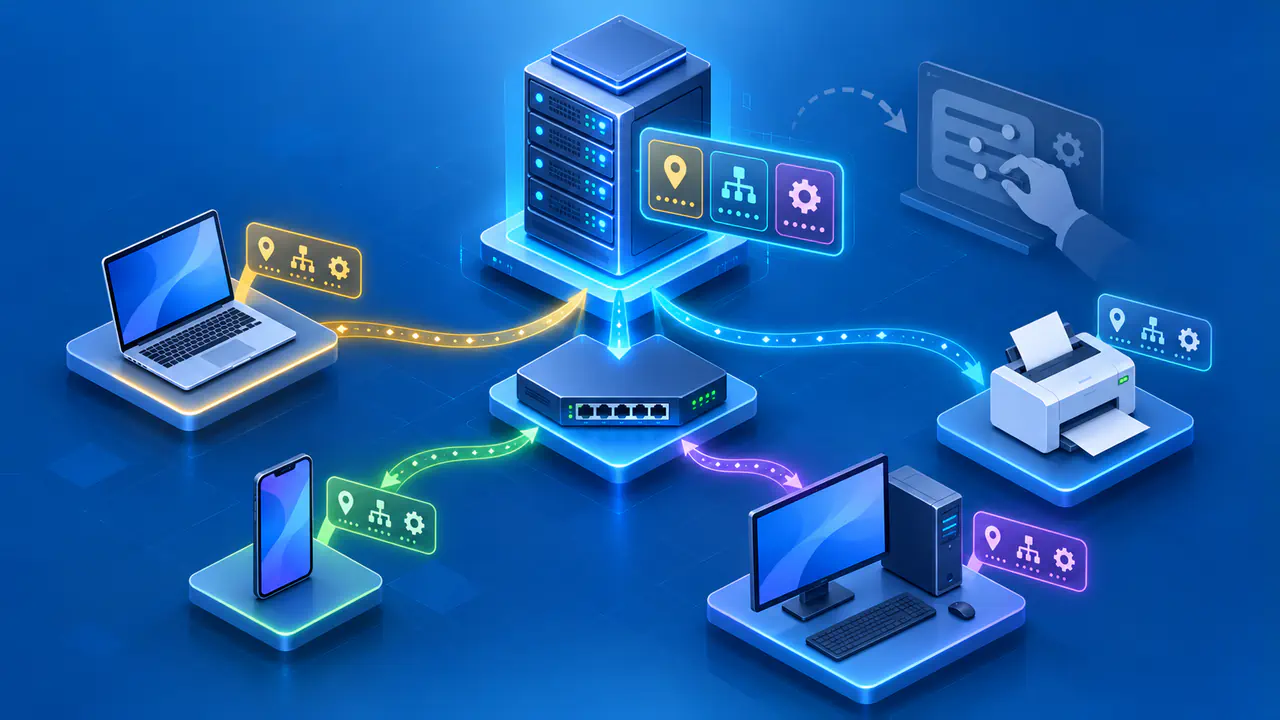
A virtual host provides the settings a web server uses for a particular website. With multiple virtual hosts, the server can choose the appropriate site using the connection's destination address and port, the requested hostname, or both. Each virtual host is a set of configuration rules, not a virtual machine or a separate physical server.
This arrangement is common when several domains point to one endpoint. It also explains a familiar surprise: a domain resolves to the right address but shows the wrong site. DNS has completed its job, while the web server has selected a default or unintended virtual host.
The Listening Address Comes First
A web server accepts connections on configured network addresses and ports. A request arriving at one address and port may be eligible for a different set of site configurations than a request arriving elsewhere. Apache and Nginx both use the listening endpoint as an important part of site selection, although their configuration syntax differs.
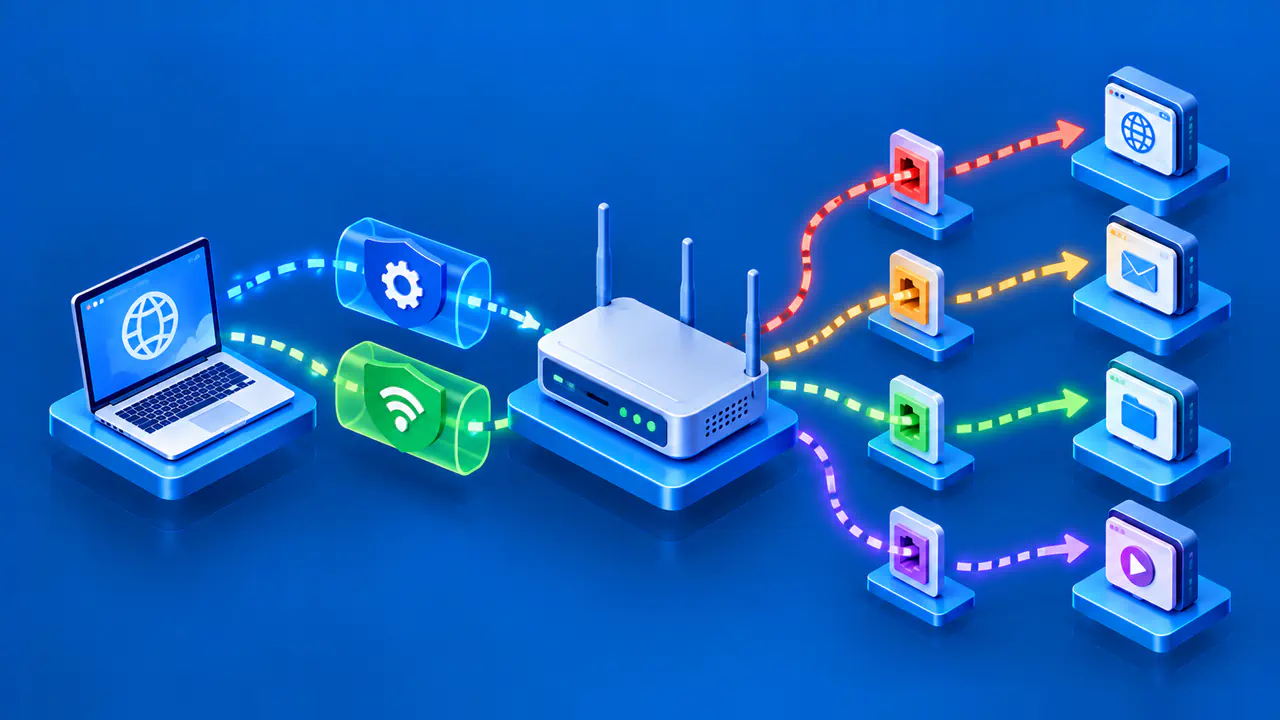
In IP-based virtual hosting, separate sites are associated with distinct address and port combinations. The server can select a site using the destination of the connection. A machine may have multiple addresses or interfaces, and a port can also distinguish services. This arrangement does not require one physical machine per site.
With name-based virtual hosting, multiple hostnames can share the same address and port. The server first has a connection on a listening endpoint, then uses the hostname supplied by the web request to decide which site configuration should handle it. This conserves addresses and allows many ordinary websites to share one endpoint. DNS must still direct each name to that endpoint.
When diagnosing a mismatch, record the actual destination address and port. Testing an alternate address or a different port may select another configuration even with the same hostname. A server can also listen on a wildcard address, accepting connections on several local interface addresses. The virtual-host configuration still determines which site answers.
Hostname Matching
A browser sends the intended hostname as part of its HTTP request. Web server rules compare that name with configured site names or aliases. Apache uses directives such as ServerName and ServerAlias within virtual host definitions. Nginx uses server_name within server blocks. The server then applies that site's document root, routing rules, logs, or application proxy settings.
For example, www.example.com and shop.example.com can both point to one address while receiving different content. The server may map www to an informational site and shop to an application. It can also configure both names as aliases of one site. The DNS records only help clients arrive; the server configuration decides which content is returned.
Hostname matching happens within the candidates associated with the request's destination address and port. Apache's name-based virtual host rules first narrow the candidates by address and port, then compare configured names. Nginx similarly checks the listening address and port and then the host name. The exact precedence among aliases and wildcard patterns is product-specific, so inspect the active configuration when names overlap.
When the Default Host Answers
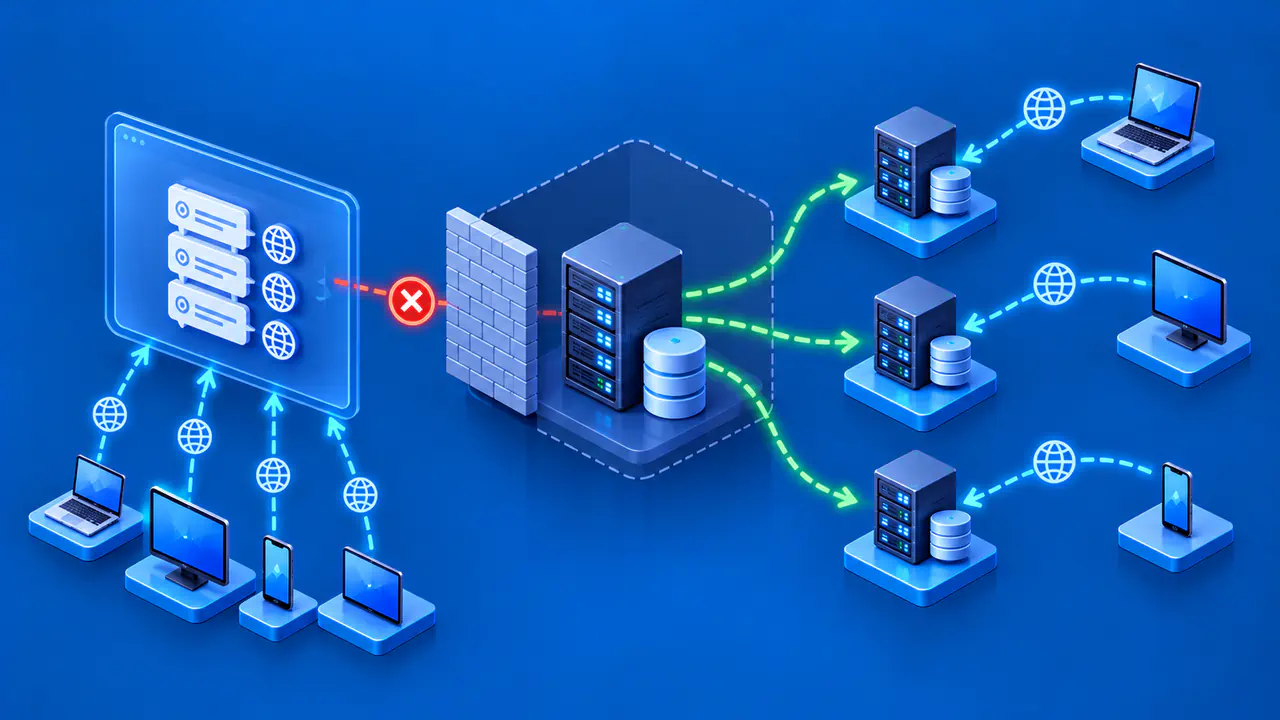
If a request does not match an expected hostname, a default site can answer for that address and port. In Apache name-based hosting, the fallback is the first listed virtual host in the best matching address-and-port group. Nginx can designate a default server for each listening address and port; without an explicit default, the first server block for that pair is used. A mistyped hostname or missing site definition can therefore return an unrelated default page.
A default host is not automatically an error. It is a deliberate or implicit fallback that the operator should review. It may serve a neutral page, reject the request, or redirect according to local policy. The important point is to know which configuration receives unmatched names. Otherwise, pointing a new domain at an existing IP address might unexpectedly display the first configured site.
If an Apache virtual host omits ServerName, it inherits a name from the main server configuration. If no global name is set, Apache detects one at startup through reverse DNS for the first listening address. Those names can cause unintended matches, so compare the configured names with the exact public hostnames, including the www name and other aliases.
Two Sites on One Web Server
Imagine two sites, docs.example.com and store.example.com, both resolving to the same web endpoint. The server has two name-based configurations on the same port. A request for docs.example.com/guide selects the documentation configuration; a request for store.example.com/cart selects the store configuration. The path is then handled within the selected site.
Now imagine preview.example.com also resolves to that endpoint, but no site configuration names it. The request may fall through to the default host and show one of the existing sites or another default response. The DNS record was valid; the web routing was incomplete. Adding the intended virtual host or correcting the name mapping addresses the mismatch.
The same named sites could instead use different addresses. The address and port would narrow selection before name matching. Neither pattern alone guarantees isolation of application data or user permissions. Separate site configurations can share operating system resources, and their security depends on the actual server and application setup.
HTTPS Certificates and Site Routing
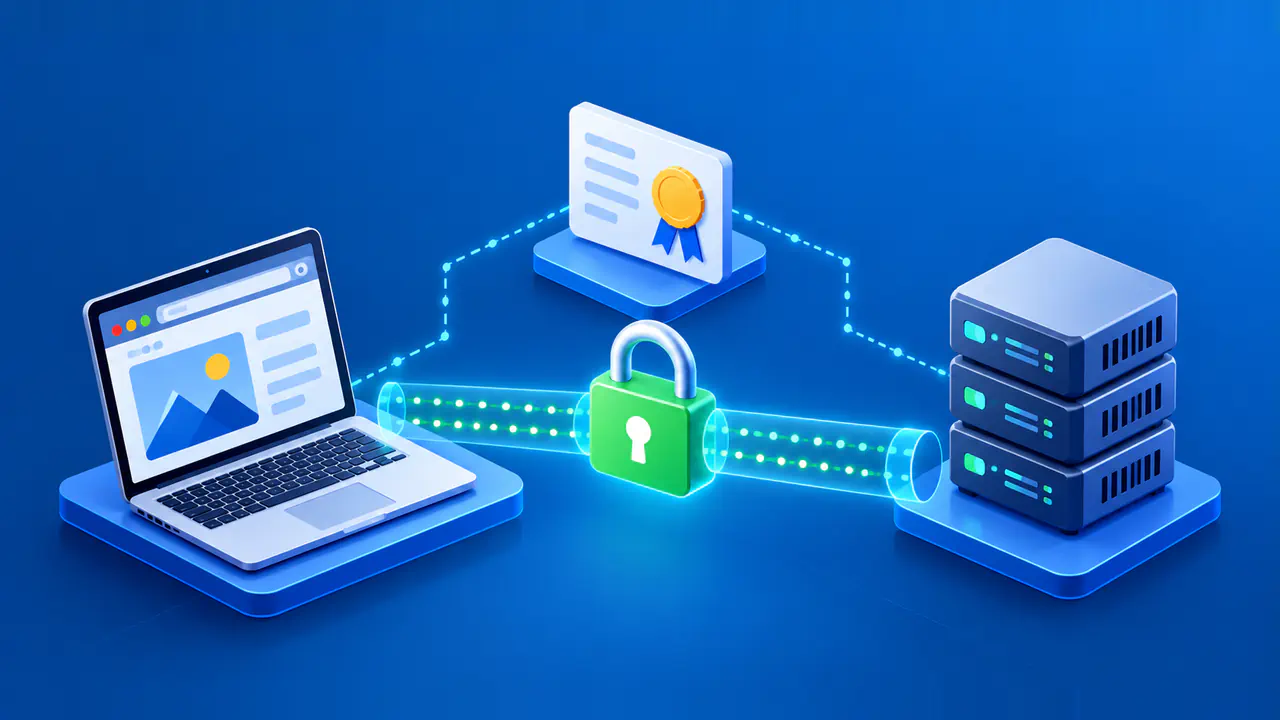
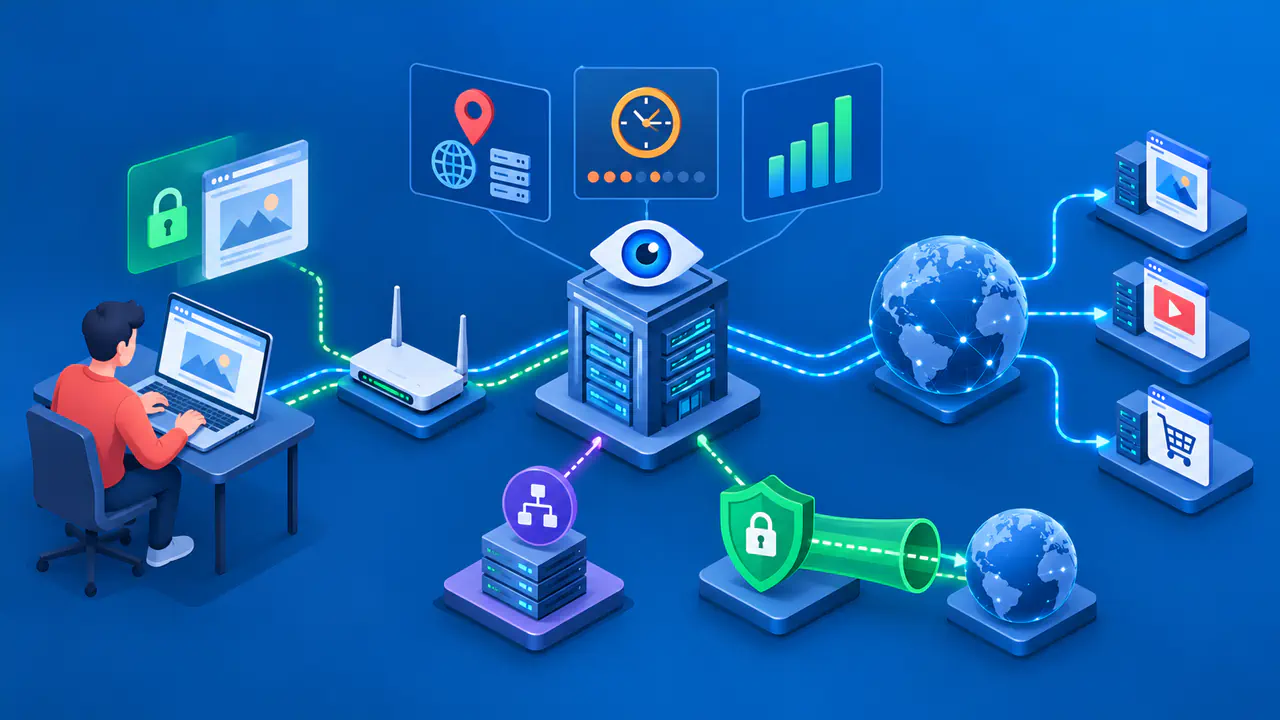
For HTTPS, certificate selection takes place during the TLS handshake, before ordinary HTTP hostname routing. The client can indicate the intended server name during that handshake, allowing the endpoint to choose a suitable certificate. A matching HTTP virtual host cannot repair a certificate mismatch that stops the secure request from proceeding.
When checking a site, test the exact HTTPS hostname as well as the HTTP routing result. Confirm the certificate covers the name, then inspect which virtual host answers the request and what content it serves. Keep the two stages separate: secure connection setup happens first, and HTTP site routing follows.
If HTTPS stops at a certificate error, the server may have no HTTP request to record in the site's access log. After TLS succeeds, Apache can include the selected virtual-host name in an access-log entry, helping distinguish default-site routing from an error in the intended application. Use the selected host recorded in the log rather than guessing from the page's appearance.