How to Check if an IP Address Is Used by a VPN
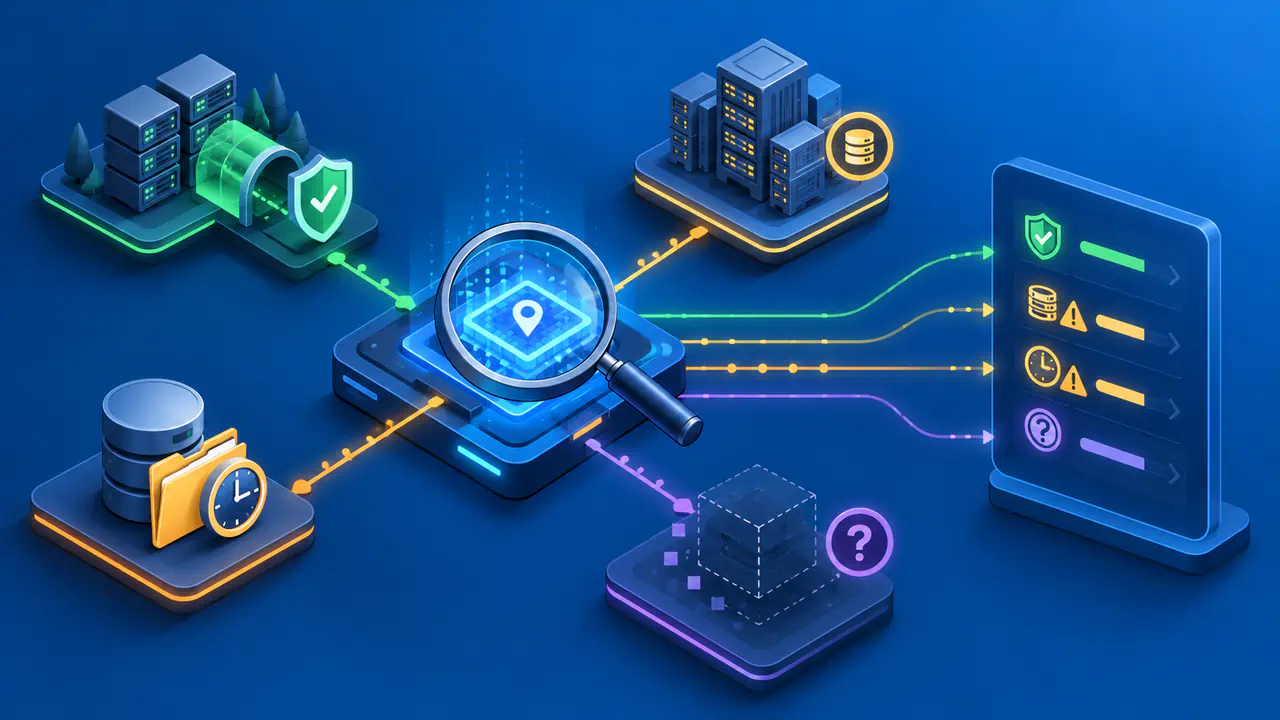
To check whether an IP address is used by a VPN, look it up with a service that reports VPN detection data, then check the meaning and age of the result. A VPN label means the provider associates the address or its network with a VPN under that provider's rules. The label does not establish who used the address or whether a particular connection passed through a VPN.
A VPN can use addresses that it owns or leases from another company, so ownership records alone cannot answer the question. Detection services may also disagree about the same address. You can make a more useful assessment by comparing their VPN and hosting fields, checking dates, and keeping unresolved differences in your notes.
Understand VPN and Hosting Flags
Start with the exact public IP address you want to check. If you are checking your own connection, use the address reported by an external IP lookup rather than a private address shown in your device's network settings. Choose a detection service that separates VPNs from other categories, such as proxies, Tor exits, relays, and hosting providers. A broad label such as "anonymous" may cover several of these categories, so it should not automatically be read as "VPN."
Read the provider's definition of its VPN field before interpreting the value. One provider may identify addresses registered to known VPN services, while another uses observations of VPN exits. A hosting flag usually identifies cloud or data-center infrastructure, which can support websites and business applications as well as VPNs. If only hosting is flagged, the result has not established which service uses that address.
A false VPN value means the provider has not classified the address as a VPN under its detection rules; it does not rule out VPN use. Missing fields need care too: some formats omit false values, while others may omit data that is unavailable or outside the product's coverage. Follow the documentation for the product and format you are using instead of treating every blank field as either false or unknown.
Check the organization and autonomous system listed beside the result for context. A VPN service that leases addresses may appear under its hosting company's name rather than its own brand. Registration records describe the organization holding the address space, and the autonomous system identifies a routing network; neither necessarily names the application using the address. A location estimate does not resolve that distinction.
Check Dates and Compare Providers
Record when you ran the lookup and, if available, the date or version of the underlying database. An online result can still rely on older observations, and a downloaded database stays unchanged until you replace it. The time you received a result is therefore different from the time its supporting data was collected.
Some products include a last-seen date or a confidence value. A network last-seen field may describe when the provider last observed that network in its anonymizer analysis, rather than the last time someone used the individual address. Read the definition before relying on the date. Confidence values also depend on the provider's method, so a score from one service should not be treated as directly comparable to a score from another.
When two services disagree, compare the same complete IP address and note the exact category each service returned. Check whether each classification applies to an individual address or a wider network range. A range-level finding may be based partly on observations of other addresses in that range. Comparing the coverage and dates helps explain the disagreement, even when the available records do not resolve it.
Recognize False Positives and False Negatives
A VPN label can remain after a service stops using an address or a hosting company assigns the address to a different customer. A broad network label can also include servers with different purposes. These cases can produce a false positive: an address is flagged even though its current use does not match the category. An older lookup can document a past classification, but it cannot establish how the address is used today.
A false negative occurs when a VPN exit is not recognized. New exits may not appear in a database yet, and a private VPN on a home or business connection may fall outside the provider's detection criteria. Several unflagged results can still share the same coverage gap. Agreement between services is useful context, but the number of matching results alone does not measure detection accuracy.
For your own connection, check the VPN client's connection status and compare the external IP with the exit address expected by the VPN service. If you compare results before and after connecting, keep the underlying network the same so a switch from Wi-Fi to mobile data does not confuse the comparison. Check whether the browser is included in the VPN: split tunneling can send selected traffic outside the tunnel. A browser lookup describes that request, so a matching exit address does not verify every app on the device.
Describe What the Lookup Supports
Keep a short record of the IP address, provider, lookup date, returned categories, and any relevant data date. If the provider reports VPN use, describe the address as classified as a VPN by that provider at the time of the lookup. If the result only identifies hosting, record hosting without adding a VPN claim. When providers disagree, retain both findings rather than turning them into an unsupported yes-or-no answer.
If you use the result to manage access to a website, consider the request's behavior and your access policy as well. Many users can share a VPN exit, and people may use VPNs for routine privacy or work. The classification alone does not identify a visitor or show that a request is abusive. A decision that affects an account needs more context than an IP category.