VPN vs Proxy: Which Do You Need?
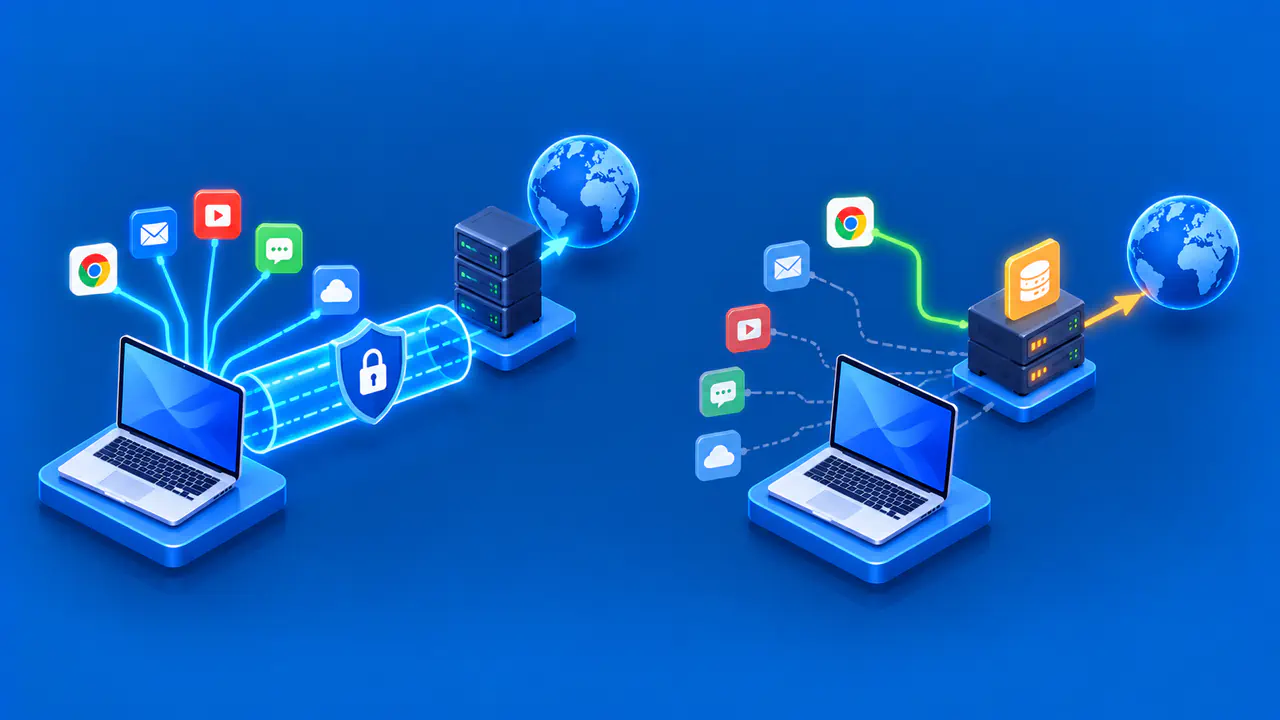
A VPN and a forward proxy can both send your traffic through another server, but they usually differ in which apps they cover and how they protect the connection. A VPN encrypts traffic routed through its tunnel between your device and the VPN server. A proxy forwards requests from apps configured to use it, often a browser or a single application. A proxy can use encryption, too, but encryption is not a built-in feature of every proxy connection.
The choice depends on what you need to route. A proxy may be enough for one application that needs access through a particular server. A VPN is generally a better fit when several apps need an encrypted connection across a network you do not trust. Neither option automatically covers every app or makes you anonymous.
Which Traffic Each Service Handles
A forward proxy accepts requests from a client and sends them to the destination. A website may therefore see the proxy's IP address as the source of a connection. Some proxies also pass the client's original address to the website in request headers, so a proxy does not necessarily hide your IP. A reverse proxy has a different job: it receives requests on behalf of a website and passes them to that website's servers.
An HTTP proxy handles web traffic. It may also support the CONNECT method, which lets a browser establish a tunnel through the proxy for an HTTPS connection. A SOCKS proxy can relay connections for compatible apps beyond a web browser. SOCKS5 supports TCP connections and UDP traffic, but support in the protocol does not guarantee support in your app or proxy service. For example, an app that needs UDP cannot rely on a proxy that only supports TCP.
A VPN usually changes routing on your device or router. Traffic selected by the VPN configuration goes through the tunnel before continuing from the VPN server to its destination. Many consumer VPN apps route traffic from multiple applications, while split tunneling lets selected traffic use a different route. A browser extension advertised as a VPN may cover only browser traffic, so check the product's actual scope.
Compare Encryption and App Coverage
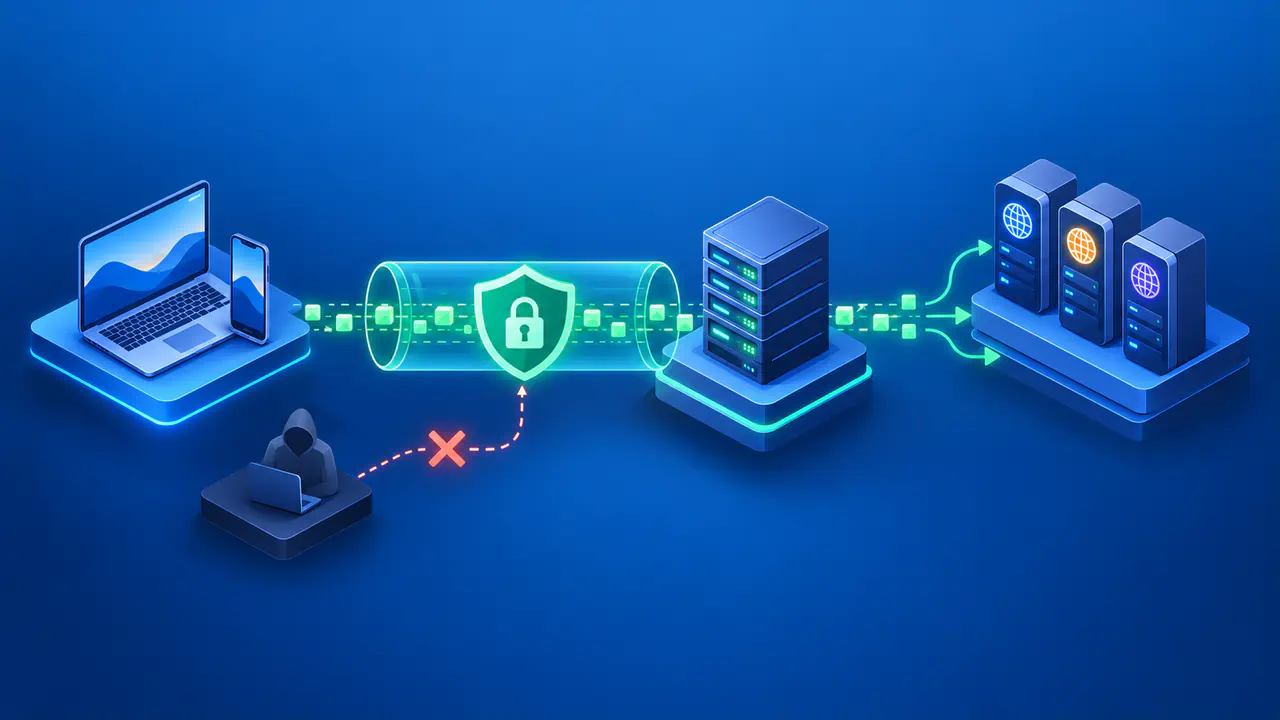
A properly configured VPN encrypts the connection between your device and the VPN server. Your local network operator or ISP can still see a connection to that server, but cannot directly read the contents or final destination addresses of traffic inside the tunnel. A proxy connection does not necessarily provide the same protection. Some proxies accept encrypted connections from clients; others receive traffic over an unencrypted connection. The proxy type and settings determine which arrangement you have.
HTTPS protects a separate connection: the one between your browser and the website. When that connection remains encrypted all the way to the website, neither an ordinary forwarding proxy nor a VPN server can read the page content. A VPN's own encryption ends at the VPN server, however. If an app sends unencrypted data to its destination, a VPN does not automatically protect that data after it leaves the tunnel.
Consider a browser set to use a proxy while a messaging app connects directly. The browser's requests can pass through the proxy without changing the messaging app's route. A device VPN can cover both applications, provided its routing settings include both. DNS requests may follow a different path from other traffic, depending on the client. To understand the protection you are getting, check the relevant application and service settings rather than relying on a connection icon.
When a Proxy or VPN Makes Sense
A proxy may suit a workplace that requires a browser to access websites through an organizational gateway. The organization can use the proxy to control web access or record requests, while other applications keep their existing connections. In this situation, the purpose may be access management rather than personal privacy. Follow the organization's requirements and read its policy on what the proxy can inspect and log.
A VPN is useful when you need an encrypted path across an untrusted local network for several supported applications. A work VPN may instead provide access to private company resources while leaving ordinary internet traffic outside the tunnel. These are different routing choices, even though both use a VPN. Confirm which destinations your VPN includes before assuming that a connection to a public website passes through the VPN server.
If you only need a browser request to reach a website from another IP address, either a suitable proxy or a VPN can do that. The deciding factors are the applications you need to cover and whether you need encryption between your device and the intermediary. The operator also matters: either service may observe connection details, and encryption does not tell you whether those details are logged. A website can still recognize a signed-in account or read the data you submit.
Check the Connection You Will Use
After configuring the service, check the public IP from the application you intend to use. Compare the result with the service connected and disconnected. If you want another app to connect directly, check that app separately where an equivalent test is available. A browser showing a different IP confirms a change for that request; it does not establish how every app connects or whether the connection is encrypted.
Review the proxy or VPN settings for excluded apps and destinations, and confirm that sensitive websites still use HTTPS. On a managed work device, an organization may install a trusted certificate that allows an inspection service to decrypt and examine web traffic. Ask the administrator how that arrangement works; the usual assumption that only your browser and the website can read the content may not apply.
Choose a proxy when you need its specific application support or organizational access. Choose a VPN when you need its encrypted tunnel and routing across the relevant apps. In either case, the useful test is whether the service covers the connections you actually use, with the encryption and operator practices you require.