What Does It Mean When a VPN Keeps No Logs?
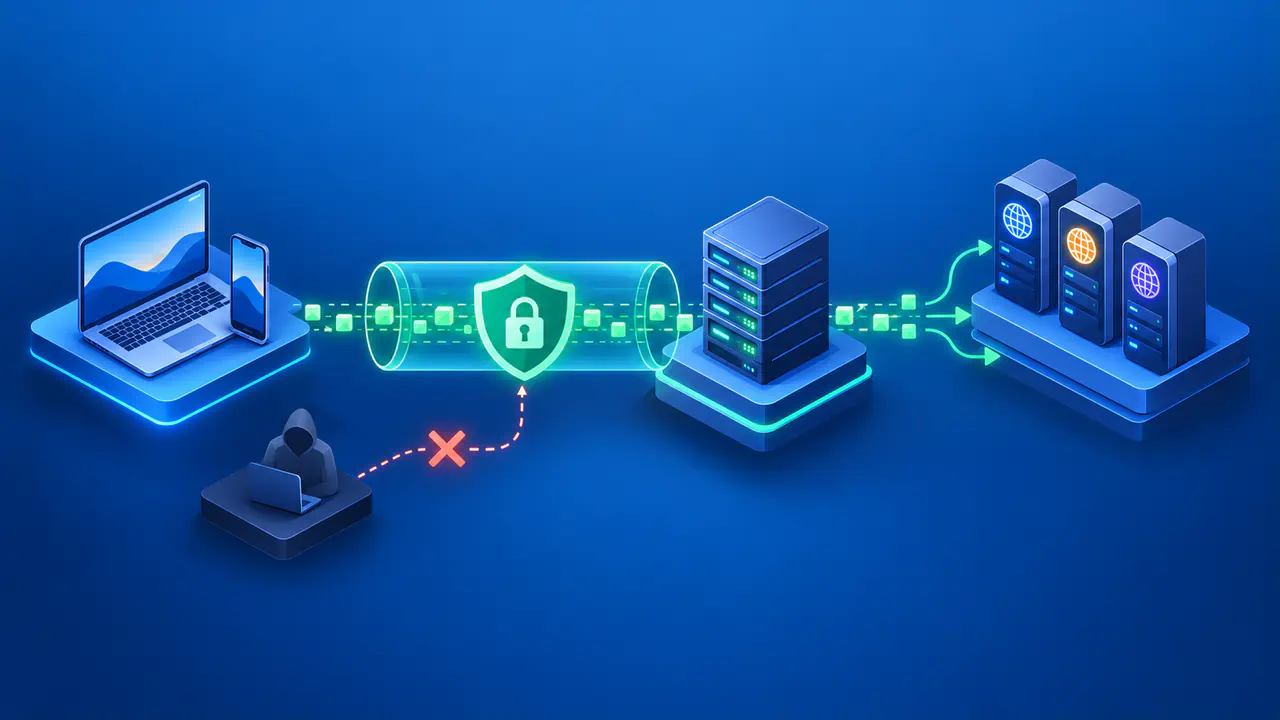
When a VPN says it keeps no logs, it is promising not to retain records of your activity through the VPN. The details matter: one provider may exclude both browsing activity and connection records, while another may retain information about when you connected. The phrase does not mean the company has no information about you. Your account, payments, and support requests can be covered by separate retention rules.
A VPN must process some information while a connection is active so that traffic reaches the right device. Processing an address to deliver a packet is different from saving that address in a record that can be examined later. To understand a no-logs claim, check which data the provider handles, whether any records identify you, and how long those records remain.
Traffic Logs and Connection Logs
Traffic or activity logs describe what someone does through the VPN. Possible entries include destination addresses and DNS queries, which ask for the addresses associated with domain names. Unencrypted traffic may also expose the content being transferred. HTTPS separately encrypts the communication between your browser and the website, so routing that traffic does not normally let the VPN provider read page contents or passwords.
Connection logs describe the VPN session rather than the pages you open. A record might contain your source IP address, the VPN server you used, connection times, session length, or the amount of data transferred. Even without a list of websites, a precise IP address and timestamp can help connect activity to a particular subscriber when combined with other records. A statement that excludes browsing logs alone does not tell you whether connection records are kept.
Server statistics are another category. A total showing that a server currently has 800 connections is not a list of which accounts made those connections. The same distinction applies to overall processor load and total traffic handled by a server. However, the label “aggregate” is not enough to explain how statistics are produced: check whether the provider first stores individual records or creates totals without retaining those records.
Account, Payment, and Diagnostic Data
An account can have an identifier, subscription status, login credentials, support history, and billing information. Those records may be necessary to provide the service even if browsing activity is not stored. A provider that uses numbered accounts may still keep the account number and its expiration date. An account identifier is therefore not, by itself, evidence of a browsing log; the question is whether the provider links that identifier to records of VPN use.
Check payment records separately from VPN activity. A VPN company may retain transaction details to credit a subscription or handle refunds, while a bank or payment processor keeps its own records. Paying for access and using that access are different events. A provider can avoid recording your VPN activity without making your payment anonymous, and its retention choices do not automatically apply to the processor.
Support requests contain whatever you choose to send. An email address, screenshot, or description of a connection problem can reveal details that the VPN server does not otherwise retain. Before sending a diagnostic file, look for a preview or an explanation of its contents. Remove passwords and unrelated personal information, and check whether the support service uses another company to receive or store messages.
App telemetry is information sent by the app about its operation, such as failures or feature use. Crash reporting and usage statistics may have separate controls, and the defaults can differ between platforms or versions. Check the settings in the app you use, together with the description of the data being sent. A diagnostic setting should make clear whether reports are optional and whether the provider can associate a report with your account or device.
What RAM-Only Servers Can and Cannot Prevent
A RAM-only VPN server runs without using a local disk for persistent storage. Data held only in ordinary working memory does not remain as a disk record after the server is powered off. This can reduce the information left on a seized server, but seizure alone does not guarantee that the machine has stopped running or that its memory cannot be examined.
A diskless server still processes active connections. Software running on that server could also send information to a remote logging system, so the absence of a local disk does not establish that no records exist elsewhere. Account databases, payment services, and support systems may use separate infrastructure. Their storage practices need to be evaluated independently of the VPN server's design.
An independent audit can help check whether the deployed service matches its stated logging policy. Useful details include the systems inspected, the dates of the work, and whether reviewers examined running configurations and how configuration changes are controlled. A review covering selected servers during a particular period supports conclusions about that scope; it cannot certify every future deployment. A report about security generally may not answer the specific question of what the service logs.
How to Read a VPN's Logging Policy
Start with the exact product and the policy's revision date. Read the statements about traffic content, DNS queries, IP addresses, timestamps, and bandwidth together, rather than relying on a single sentence about browsing history. Pay attention to the verbs: never collecting a field is different from keeping the field temporarily and deleting it later. If retention is temporary, look for a stated period or a clear event that triggers deletion.
Next, follow references to the company's account, payment, and support policies. For each category, identify who receives the data, why the data is needed, and when the data is removed. Check for exceptions attached to a particular plan, app, or feature. If a policy uses a broad phrase such as “service improvement,” look for the actual fields collected instead of assuming the purpose explains the amount of data involved.
Finally, compare any audit with the particular promises you want to verify. Record gaps as unanswered questions: a policy that omits connection timestamps has not established that none are retained. If the provider offers only an audit badge, look for a report that identifies what was checked and when. Save the policy version you relied on so that a later change in wording can be compared with the original commitment.