What Is VPN Split Tunneling?
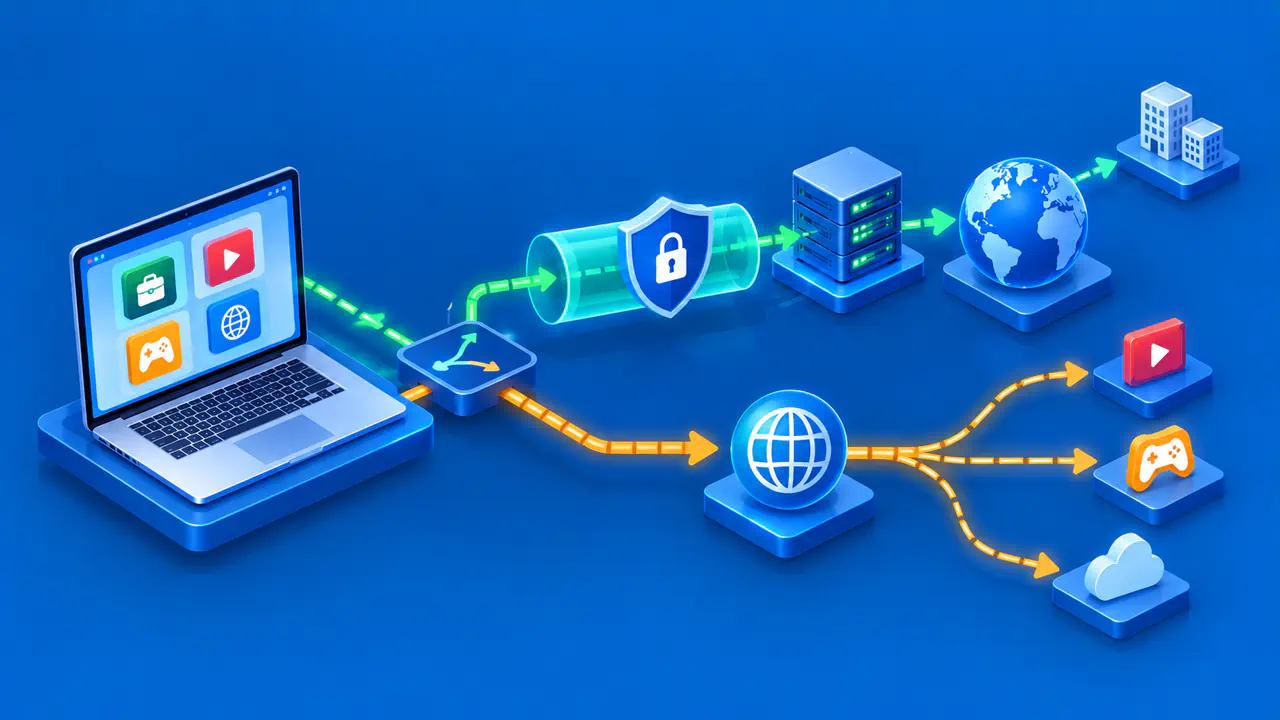
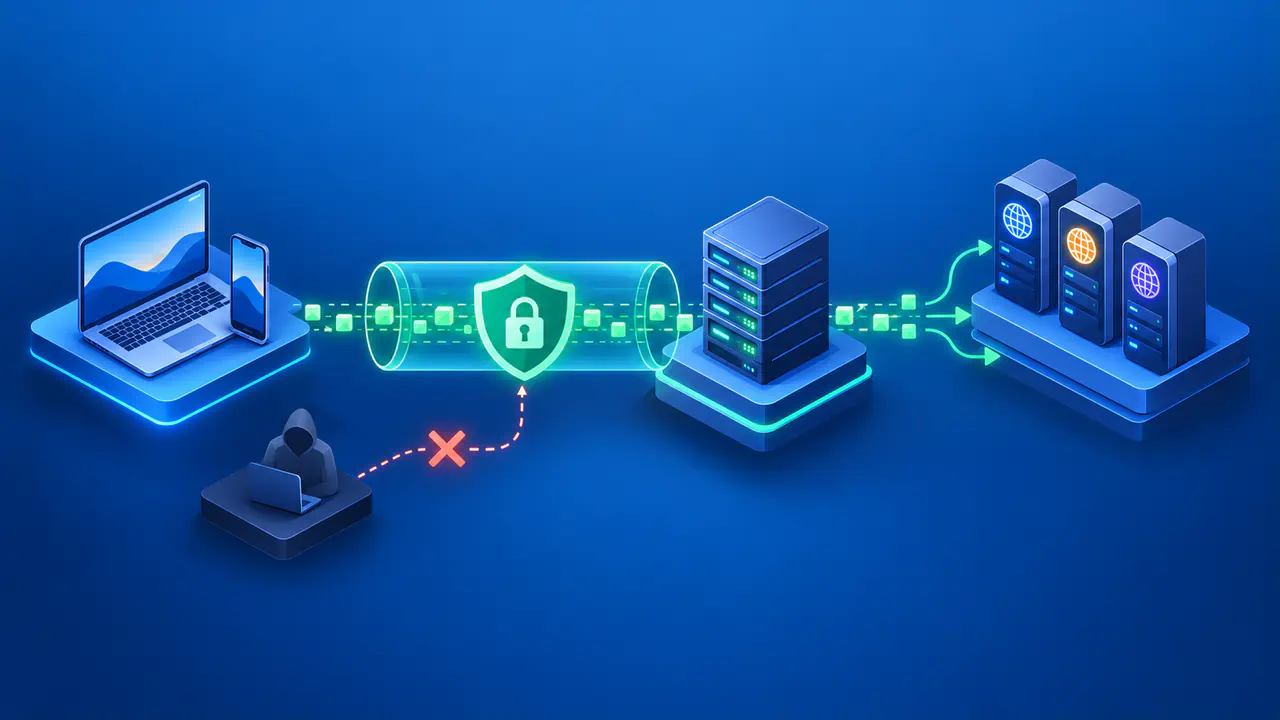
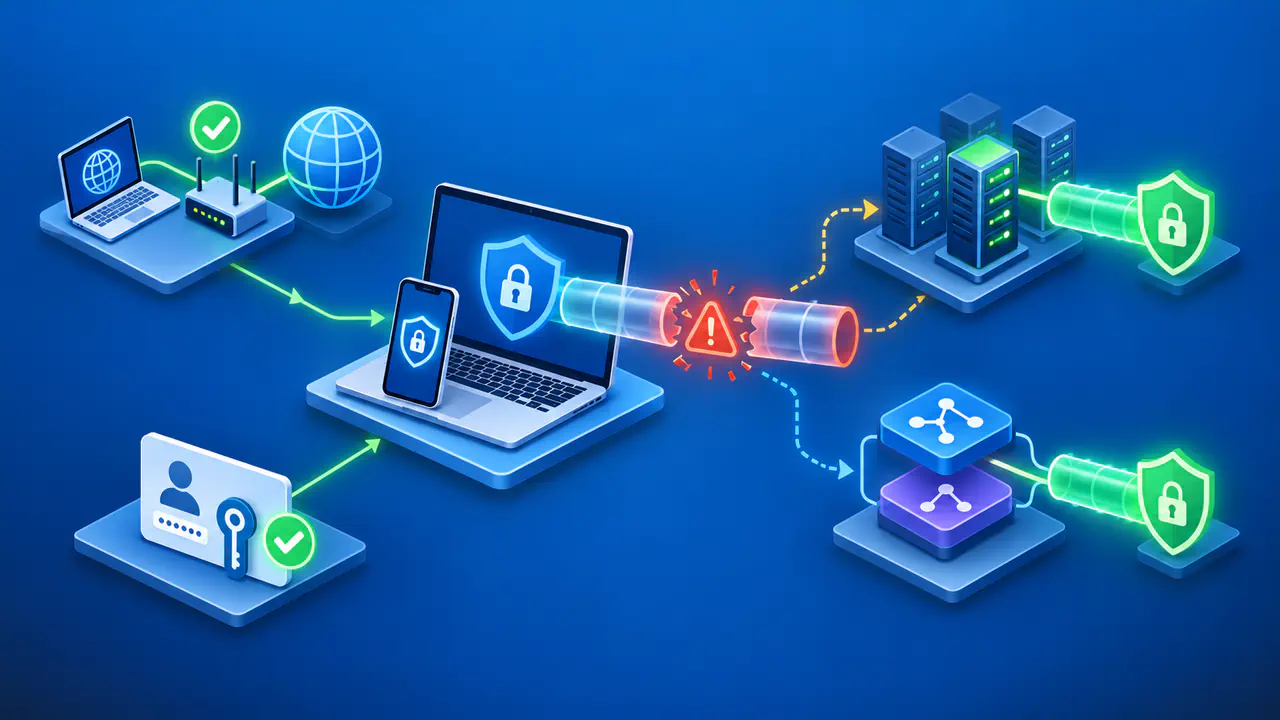
VPN split tunneling lets you choose which traffic uses a VPN and which traffic bypasses it. Depending on the product, you can select applications, destination IP addresses, or domain names. This lets one connection use the VPN while another uses the device's ordinary network connection. Traffic outside the tunnel does not receive that tunnel's protection.
The first decision is what you need the VPN to carry. You might need access to a company's private network while keeping ordinary web browsing outside the VPN, or you might want most applications to use the VPN with one exception. These choices require different defaults. A connected VPN icon alone does not tell you which applications or destinations are included.
Include and Exclude Rules
In exclude mode, the VPN handles traffic by default, with exceptions for the apps or destinations you select. For example, you could exclude a particular application while keeping other supported traffic in the tunnel. The exception changes that application's route; it does not disconnect the VPN for everything else. Check what the product excludes before adding an entire program.
Include mode reverses that choice: the selected apps or destinations use the VPN, and other traffic stays outside it. With an app include list, a newly installed application is not automatically selected. A destination rule works differently because any supported application connecting to the matching address may use the VPN. Check both the rule type and the treatment of unlisted traffic.
Names and available controls vary between products and operating systems. Proton VPN calls its Android include mode Inverse mode, while its experimental macOS feature currently supports app exclusions only. Do not copy a mode name from another platform without checking what the setting does. On a managed work device, the administrator may choose the rules for you.
App Rules and Destination Rules
An app rule is useful when an entire program needs a particular connection. Select the application that actually opens the network connection, not just a shortcut or launcher with a similar name. Some programs use helper processes or open a separate browser for sign-in. Check how the VPN handles those components before assuming one app entry covers them all.
A destination rule applies to traffic addressed to a specified IP address or range. It can suit a company network that several applications need to reach. Use the addresses supplied for that network and check the range carefully. A broad rule can affect unrelated destinations, while a rule for one address can miss a service that uses several addresses.
Some clients also accept domain names. A browser extension may apply those rules only within its browser, while a device VPN client may turn matching names into IP routes. A website can depend on additional domains for sign-in, images, or other services. An exception for its main name may therefore cover only part of what the application needs.
On Android, VPN apps can select applications through an allowed list or a disallowed list. The VPN app decides which controls to expose in its interface. Android can also block traffic that does not use the VPN, so an exclusion does not necessarily leave the excluded app with working internet access. Check the blocking setting as well as the app list.
Split tunneling and split DNS answer different questions. Split tunneling selects the route for traffic; split DNS selects which resolver handles particular names. A company service may need both the correct VPN route and the correct DNS server. A successful DNS lookup does not, by itself, prove that the application connection used the VPN.
Decide Which Connections Can Bypass the VPN
A local printer or file share may become unreachable if the VPN captures its destination range or blocks local connections. Some VPN apps offer a separate setting for local network access; others require a suitable route exception. Identify the affected device and use the narrowest supported change that solves the problem. Allowing local access on a trusted home network is a different decision from allowing it on public WiFi.
For a direct internet connection, the destination normally sees the public IP address of your internet connection rather than the VPN exit address. The excluded traffic also travels over the local network without that VPN tunnel's protection. HTTPS can still encrypt the connection's content, but it does not conceal the source and destination IP addresses.
At work, an exception can also bypass inspection or filtering performed at the VPN gateway. Confirm the organization's requirements before changing a work application's route. A program failing to connect is not enough reason to exclude it: the cause might be authentication, DNS, or another setting. Find the cause before removing protection from more traffic.
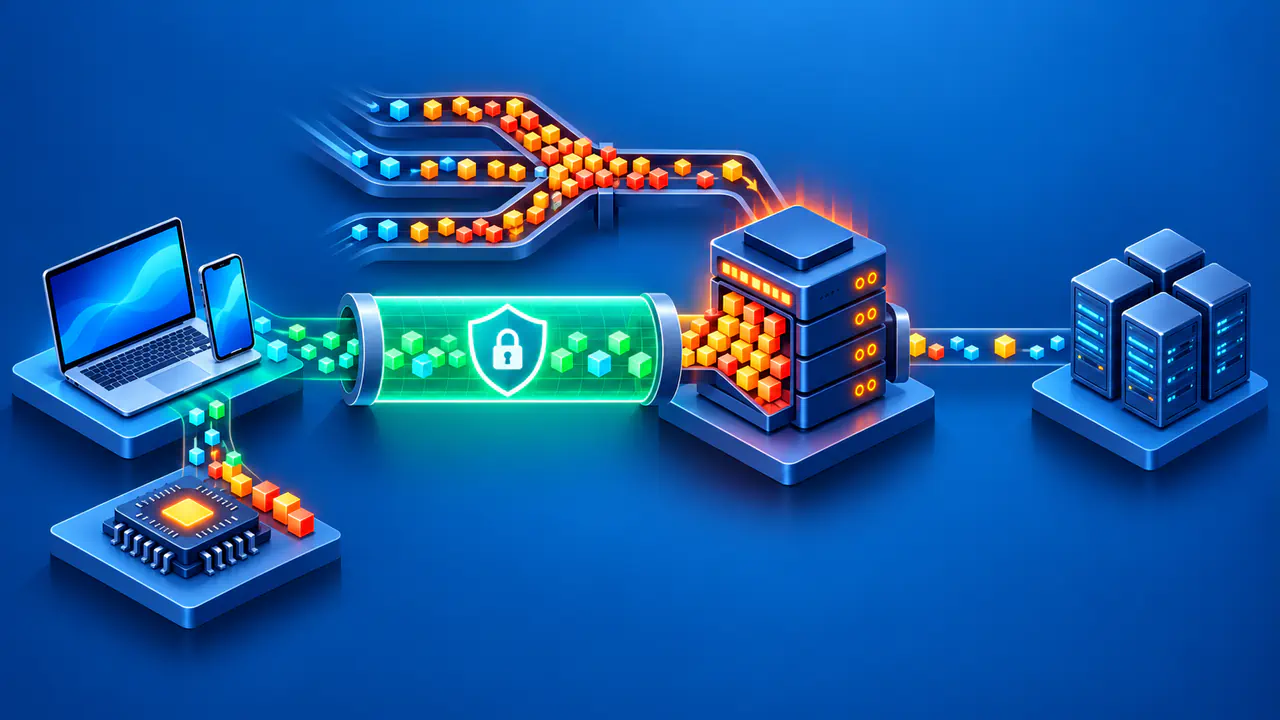
Sending selected traffic directly can reduce the amount carried by the VPN gateway, but it does not guarantee a faster connection. The direct route can have its own congestion or other limits. Choose an exception for a specific requirement and compare the affected application's behavior. Do not add unrelated exceptions merely because another application works better without the VPN.
Check the Connections after a Change
Save or apply the rule and reconnect if the VPN client requires it. In Proton VPN's Linux app, restart affected applications after connecting when split tunneling is enabled. Record the active mode, selected app or destination, and expected connection before checking the result. Keep the original settings available so you can restore a change made only for diagnosis.
Check an application expected to use the VPN and one deliberately left outside it. Use the client's connection information, an authorized connection log, or an appropriate public IP check for the actual application. A browser result describes that browser's request; it cannot establish what a separate messenger did. A page loading successfully also does not identify which route carried the request.
Check the interaction with the kill switch before relying on the configuration during a disconnection. Products differ in whether they can combine split tunneling with connection blocking. Proton VPN supports that combination on Windows, while most of its other platforms currently do not. Follow the rules for the exact client and platform, and use a controlled check that does not expose sensitive activity.
A result from one connection does not prove that every IPv4 or IPv6 connection follows the same rule. Split tunneling does not inherently disable or break IPv6; support depends on the client and configuration. Keep a short private record of the settings and observed result, and recheck affected connections after updates or network changes. Remove an obsolete exception only when you are authorized to change it.